When you realise that the lack of maintenance culture means some .gov.my websites are on antiquated versions of PHP that can't be patched or upgraded.
And perpetually susceptible to both the CVE exploits.
If you're not monitoring network connections your TV is making for at least 360 minutes, are you even debloating and removing bloatware crud, bruh?
Remove and disable all apps with "ET phone home" pings or vendor ad server connects. Exceptions only for OTA firmware upgrades.
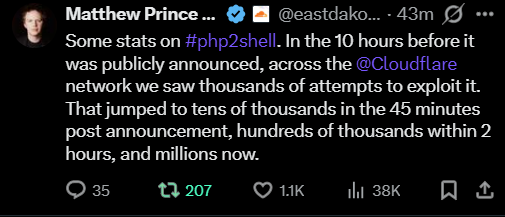
@waneizhanafeef More than 12 hours later, in which time Cloudflare has detected millions of zero day exploit attempts against websites with unpatched PHP.
It's practically useless by this point.
How many .gov.my websites have already been breached?
UPDATE: MyCERT issues an advisory, more than 12 hours after cybersecurity guardians of other nations, let alone the Japanese PM, issued their advisories, warnings and guidance.
In the interim period, Cloudflare reports millions of attempts to exploit the vulnerability.
MyCERT issuing an advisory still leaves gov websites using PHP at risk until they are patched or upgraded.
https://t.co/PzdylxRoJZ
In case you missed it, there's exploits for 2 PHP RCEs out in the wild. This allows an attacker to remotely run code on your PHP installation.
PHP powers a lot of popular websites, including those in the Malaysian government.
Has the Malaysian cybersecurity apparatus, NACSA, MKN, CyberSecurity Malaysia or anyone, issued a warning, let alone doing anything about it ? Or are they more worried about Waze ?
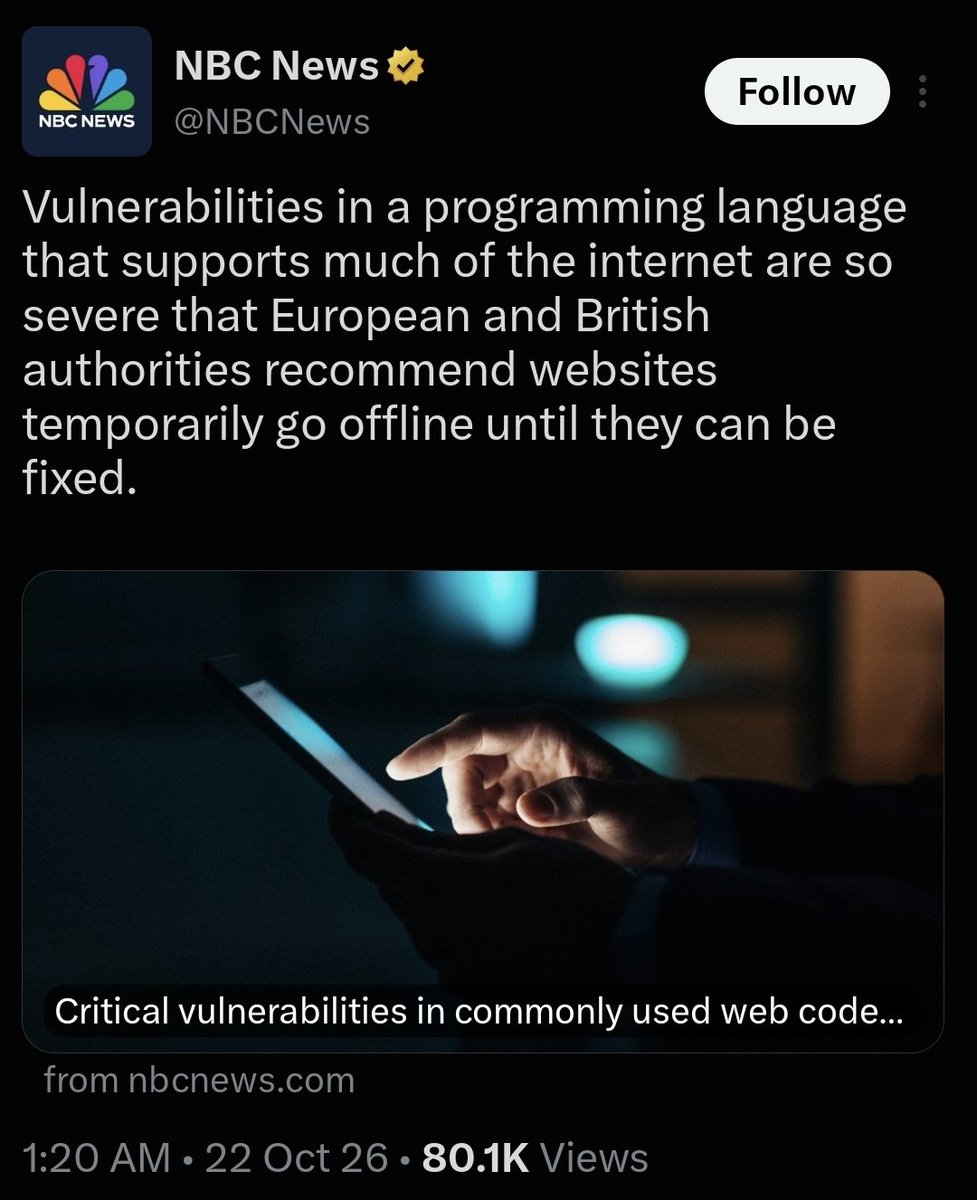
‼️ PHP UPDATE: The Dutch parliament, the Dutch national cyber agency and Finland's central government have pulled websites offline ahead of the PHP patch.
Finland's state IT centre Valtori is shutting down public-facing central government web services. The National Land Survey of Finland is already down.
In the Netherlands, the Tweede Kamer, the NCSC and the Dutch Data Protection Authority are offline. So are tech site Tweakers and NotuBiz, which runs council information for 100+ local governments.
The University of Vienna switched off its websites, webmail and Moodle. The University of Freiburg and Finland's Haaga-Helia have taken services down too.
Fur Affinity, Pinboard, explain xkcd and every wiki on Miraheze are dark as well.
Valtori says its shutdown is a precaution, not the result of an attack or breach.
PHP was created by Rasmus Lerdorf in 1994, it initially stood for Personal Home Page
PHP's fix is due at 14:00 UTC today.
The quintessential story of technology under Anwar Ibrahim's government.
Announce and promote an app one day, and the next day it's forced to be taken down for embarrassing bugfixes because it's unusable.
This is half baked software development and deployment.
The dunces in the Digital Ministry are still poring over a glossary looking up terms like PHP, RCE, CVE, and responsible disclosure.
All these acronyms fly way above their heads.
To be fair, this cybersecurity snafu doesn't land on them. It's with the national cybersecurity apparatus.
Hmmm.. It'd be interesting to see how Kementerian Digital handles these vulnerabilities. Almost (if not all) government digital services are exposed at the moment.
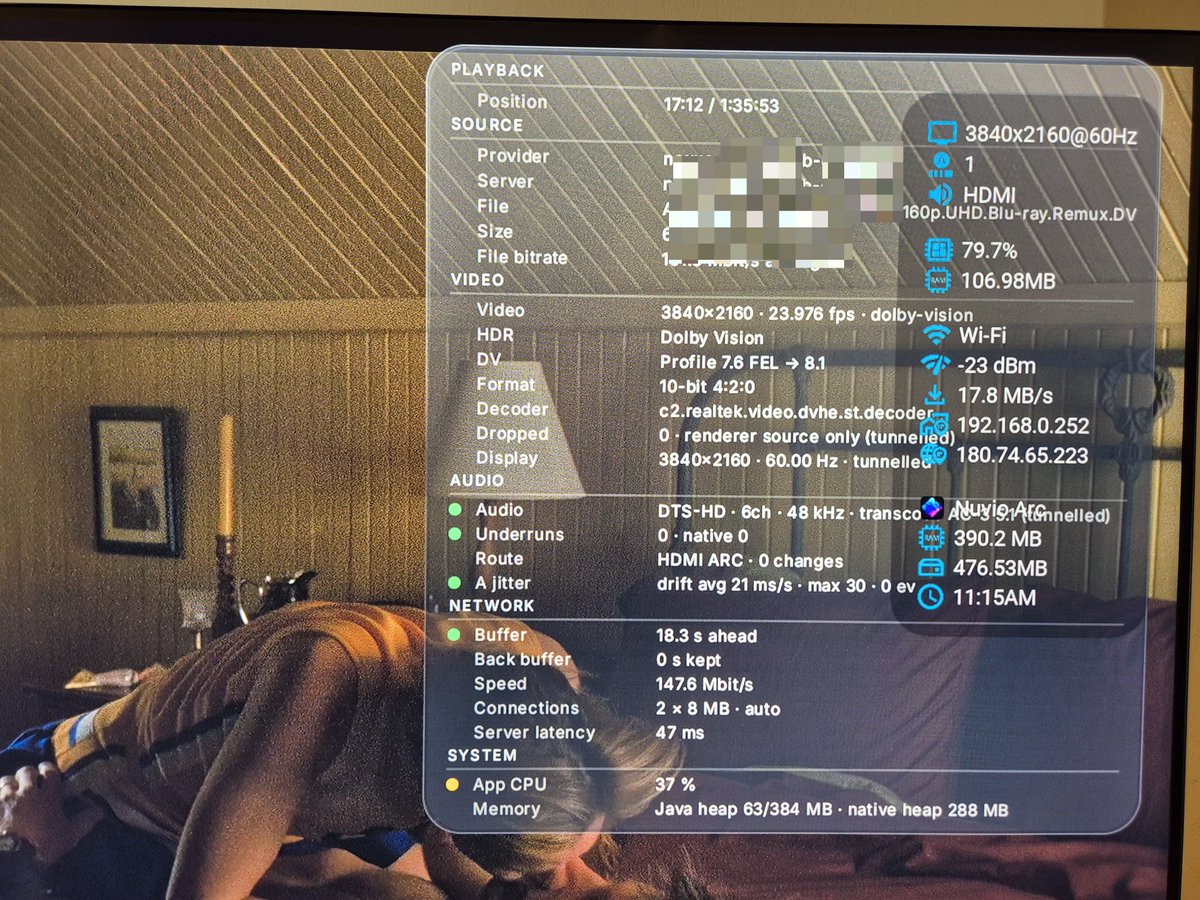
It takes a special kind of crazy to run two telemetry HUD overlays on top of each other.
Android TV performance tuning and app development in low memory environments requires it.
And BTW, that's the delectable Maria Bello doing the nookie with Viggo Mortensen.
@yayamnh48 Wrote about it earlier. The bigger concern is when are they going to start the arduous task of patching/upgrading all gov websites with PHP.
https://t.co/Y9ilNV6waX
UPDATE: MyCERT issues an advisory, more than 12 hours after cybersecurity guardians of other nations, let alone the Japanese PM, issued their advisories, warnings and guidance.
In the interim period, Cloudflare reports millions of attempts to exploit the vulnerability.
MyCERT issuing an advisory still leaves gov websites using PHP at risk until they are patched or upgraded.
https://t.co/PzdylxRoJZ
Cloudflare is already detecting early attacks from the zero day RCEs for PHP, which powers many Malaysian websites.
MKN, NACSA, National Cybersecurity Committee, MCMC have not issued any warnings nor are they doing anything about it.
They're more worried about the Waze juice.
PHP sites behind Cloudflare already have an initial set of WAF rules deployed for the known exploit vectors in these vulnerabilities. The rules are available to all customers, including free.
We are seeing early attacks emerging and are updating mitigations as new vectors show up.
This is a STOPGAP only. Patch as soon as @ThePHPF releases the update at 14:00 UTC today.
UPDATE: MyCERT issues an advisory, more than 12 hours after cybersecurity guardians of other nations, let alone the Japanese PM, issued their advisories, warnings and guidance.
In the interim period, Cloudflare reports millions of attempts to exploit the vulnerability.
MyCERT issuing an advisory still leaves gov websites using PHP at risk until they are patched or upgraded.
https://t.co/PzdylxRoJZ
The Japanese Prime Minister warns her nation about the PHP RCE cybersecurity incident affecting 70% websites globally and asks them to patch immediately.
In Malaysia, PM Anwar is busy fear mongering Waze and Israel to promote a crappy local replacement app.
Cybersecurity guardians all over the world also issued advisories and urged patching or upgrading PHP to latest version.
Locally, not a peep or any advisory from MKN, NACSA, CSM or JKSN.
Yet, they loudly classified a common crowdsourced GPS navigation app as a natsec threat.
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
PMX fearmongers using Waze and Israel as a natsec threat, while both he and the nation's cybersecurity guardians (MKN, NACSA, CSM, JKSN) haven't bothered to issue an advisory or guidance about an unfolding global cybersecurity threat and incident affecting government websites.
Actual natsec threat, depa buat dunno aje.
https://t.co/BqA1bCdw1H
The Japanese Prime Minister warns her nation about the PHP RCE cybersecurity incident affecting 70% websites globally and asks them to patch immediately.
In Malaysia, PM Anwar is busy fear mongering Waze and Israel to promote a crappy local replacement app.
UPDATE: Specific mitigation guidance for the recently identified PHP critical vulnerabilities is now available. Secure your servers today. Guidance and technical steps here: https://t.co/nuXgQ10Fzc
@azwan_ Malaysia's cybersecurity guardians baru bangun pagi, tengah minum kopi la. Gov websites using PHP being openly vulnerable isn't a high priority, let alone a natsec threat.
https://t.co/0HE23WYq4Q
Cybersecurity guardians all over the world also issued advisories and urged patching or upgrading PHP to latest version.
Locally, not a peep or any advisory from MKN, NACSA, CSM or JKSN.
Yet, they loudly classified a common crowdsourced GPS navigation app as a natsec threat.
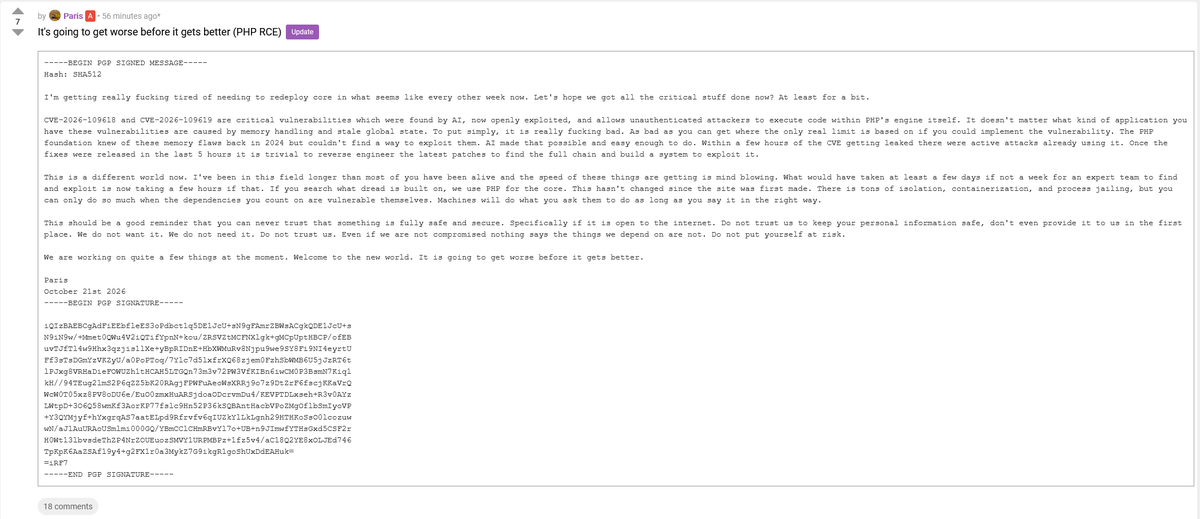
A look at critical PHP vulnerabilities from a darknet forum operator's perspective, revealing just how quickly new exploits are turning into real-world threats.
Dread Thread: https://dreadohblesmagfagqup24vw7catlvmqhhce5itz7wxr4vffgemjzaad[.]onion/post/14d9b2557ae62186394e
@sureshdr@VikkneshwaranR 7 years ago, Como declared bankruptcy and was playing in the amateur league. Then Fabregas joined, first as player and then manager, and today they're slamming 4 goals past Manure.