The Kaseya sideloaded DLL, a thread:
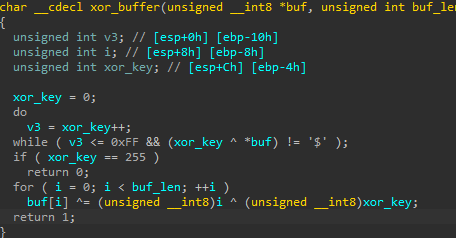
* If launched as a service, sleeps for 1000ms indefinitely
* If ServiceCrtMain is called, main malicious logic is unwrapped
* Initial payload is unpacked, XOR'd using a calculated key and execution continues
1/?
In malware analysis, the focus is on binaries and their details (C2, persistence, injections/hooking, anti-forensics techniques). On the other hand, maldocs are trivially simple to solve and most of them take 5 minutes or less to collect information. Don't waste time.
#malware
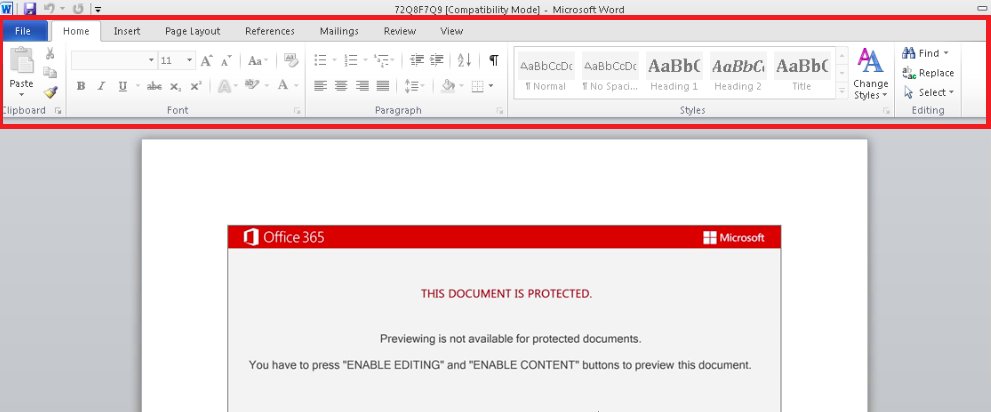
#Emotet is back and ...
+ Documents are protected: "Restrict Editing"
+ They use in the macro: ParagraphStyle
+ And dll are signed by: FRVFMPRLNIMAMSUIMT
We’ve been named an Academic Centre of Excellence in Cyber Security Education by the National Cyber Security Centre @NCSC, receiving a Gold Award. 💻🏆
We are one of eight "pioneering" universities who received this recognition by this new government programme.
#CyberSecurity
They aced it!
Eight UK universities have become the first in the country to gain recognition for their commitment to cyber security education in the new ACE-CSE programme https://t.co/7US8Vf3BHv
@DCMS
Researchers are warning of a phishing campaign that pretends to be an automated message from Microsoft Teams. In reality, the attack aims to steal Office 365 recipients’ login credentials.