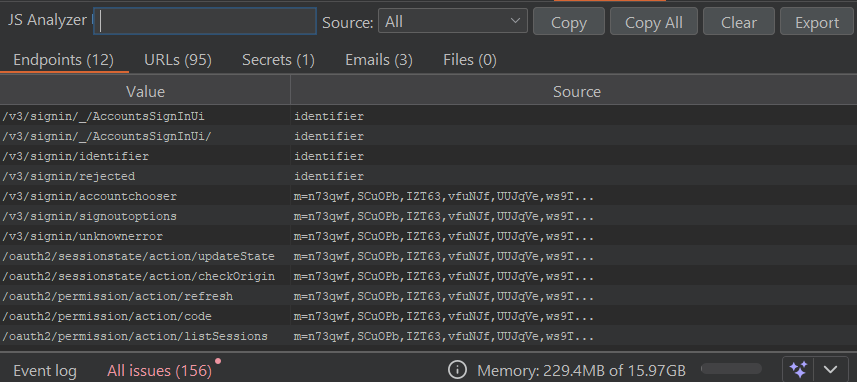
Sharing my Burp Extension that earned me $200k in 2025 while API testing heavy JS-rich targets.
https://t.co/2ttRurgoPh
The tool helps find endpoints, files, internal emails, and some secrets from minified JS.
Its goal is to achieve maximum efficiency with reduced noise in results. Contributions and feedbacks are welcome.
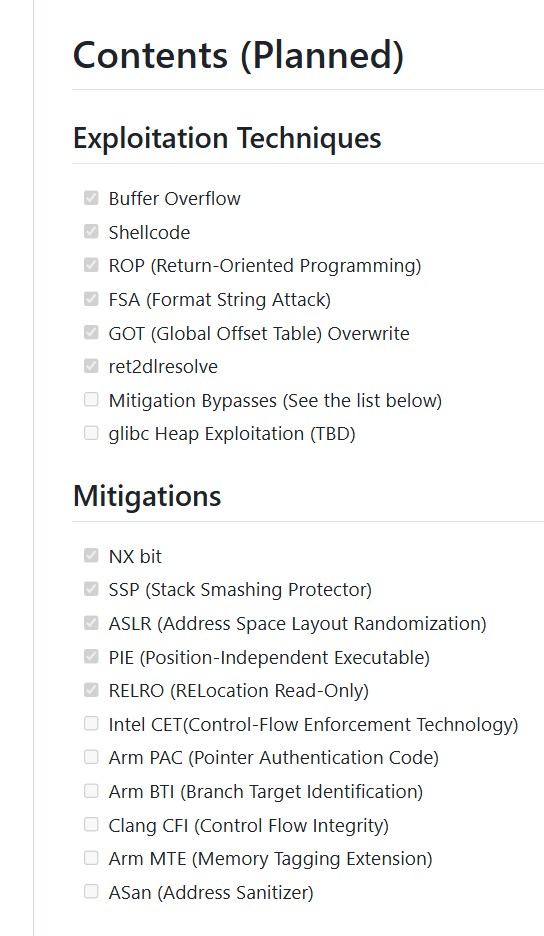
I have released the first half of "Binary Exploitation 101", a beginner-friendly guide to binary exploitation. You can learn from classic buffer overflow to ret2dlresolve through CTF-like challenges. I am working on the second half now. Stay tuned🔥
https://t.co/Oy4P8l4plk
Today our Cloud Vulnerability Research (CVR) team shared this research into LLM security, which is broadly applicable to AI domain security practitioners working in this rapidly evolving space.
Learn more: https://t.co/QtcOoDKgez
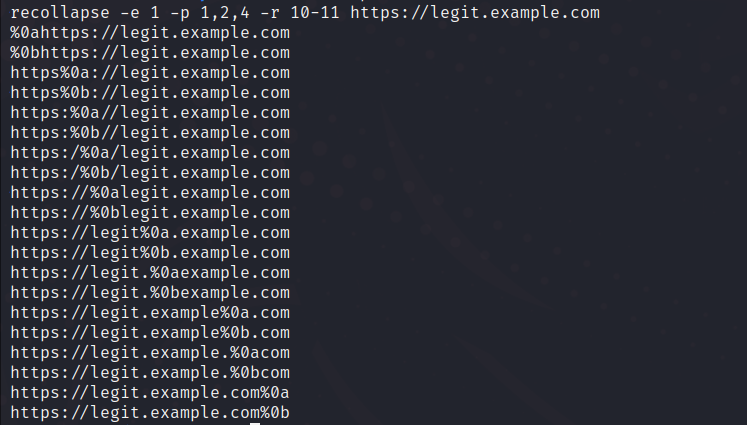
Bypass WAF / Restrictions with REcollapse
-
This tool assists in blackbox regex fuzzing to bypass validations and discover normalizations in web apps.
-
Repo: https://t.co/iHdzytjeVC
-
Creator: @0xacb (Also thanks to @Hacker0x01)
-
-
#infosec#cybersecurity#CTF#bugbountytips
New writeup:
Between March, 2023 and May, 2023 we found multiple critical vulnerabilities in points[.]com the global provider for major airline and hotel rewards programs.
Full post is available here:
https://t.co/inEYiYAwRQ
Work from:
@infosec_au@iangcarroll
Giveaway Alert 🎉🎉🎉
HackTheBox 1 Year VIP x1
- Follow, Like, and Retweet to join
- Winners will be randomly selected on July 12th.
#giveaway#hacktebox#ctf
🧶Free Resources To Learn Code Review 👇
Code review is an essential process for ensuring the quality and security of code in software development. If you're interested in learning more about code review for security, there are plenty of free resources available online.
I'm excited to start my journey in #Web3Security! After researching and learning about different attacks in Smart Contracts.
☑️Here is the list of Common Web3 Security Vulnerabilities:🧵
👇
BadSecrets - a library and command line tool for finding secrets!
Works on files, as a lib, and on URLs. OS and language agnostic.
By @BlackLanternLLC 👏👏
https://t.co/3xBL8ncK65
@actuallyclover I wrote an ugly script to detect every query parameter being reflected in the body or headers, then I ran it using a vast URLs file as input and found some good stuff
Anyway, I am slowly rewriting the tool to make it reliable https://t.co/4PFuErX7d8
Using 𝐕𝐢𝐥𝐥𝐚𝐢𝐧, the evolution of 𝐇𝐨𝐚𝐱𝐒𝐡𝐞𝐥𝐥 to generate an auto-obfuscated PowerShell backdoor payload, bypass Defender and gain access to a Windows 11 Enterprise machine.
#pentesting#redteam#cybersecurity#hackingtools#offsec
Time-based SQLi with two payloads injected in the following headers:
1. User-Agent: "XOR(if(now()=sysdate(),sleep(5),0))XOR"
2. X-Forwarded-For: 0'XOR(if(now()=sysdate(),sleep(10),0))XOR'Z
Both payloads were executed and the server responded after 15s. Very interesting.
One place for all the default credentials to assist the Blue/Red teamers activities on finding devices with default password 🛡️
https://t.co/rybxbTUzEW
#bugbounty#infosecurity#Redteame#cybersecuritytips