Hey Anthropic! I reported these encryption issues to you in May and you told me there was no relevance because replay attacks were not in your threat model. And now apparently you’ve been watching people exploit them for months. I’m actually kind of annoyed!
Attacks always get better. Here's a new nginx RCE that bypasses ASLR, tested on the latest nginx 1.30 and 1.31.
This still requires a non-default config, but unlike some previous bugs, it does not depend on any additional vulnerabilities or external helpers to get to RCE.
We reported the bug on May 15. F5 has confirmed it, and hopefully a patch will land soon.
This is getting ridiculous 😅. We have enough nginx bugs to do an entire week of MAD Bugs on it. Who could have thought nginx is starting to feel like the new Linux kernel?
This is the funniest time in computer hacking. And yet the world is completely unprepared for this new reality.
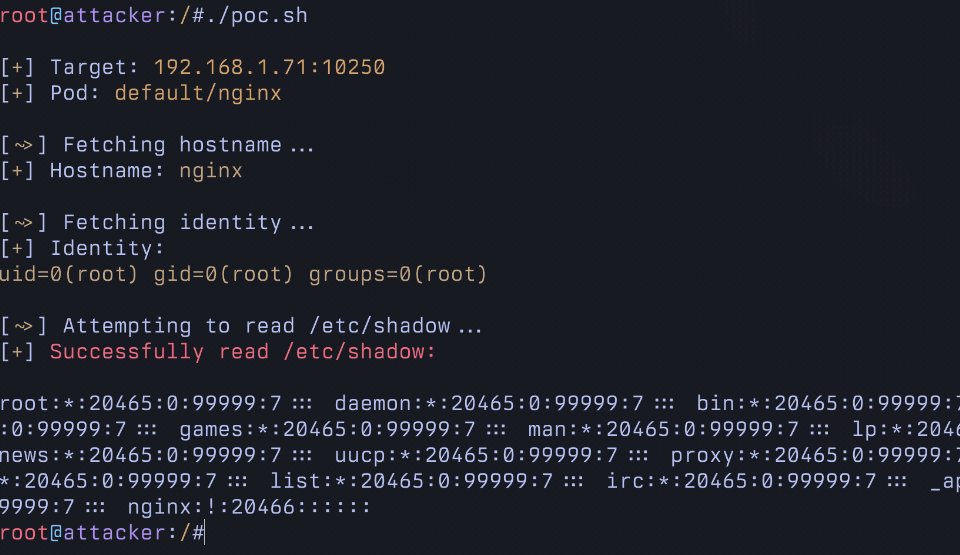
Excited to disclose my research allowing RCE in Kubernetes
It allows running arbitrary commands in EVERY pod in a cluster using a commonly granted "read only" RBAC permission. This is not logged and and allows for trivial Pod breakout.
Unfortunately, this will NOT be patched.
Last week I hacked @openclaw 3 separate times (I was the first to do this publicly).
Fast forward.
This week, I worked side by side with @steipete and @bquintero (founder @virustotal) to lead by example and ensure all AI skills moving forward, undergo strict security vetting to better protect openclaw users.