600 developers publishing containers. 1 small security team. 90 release programs to cover.
How ServiceNow scans every containerized product without growing security headcount at the same rate: https://t.co/cRDutAZNQe #SBOM
A container can run unchanged for 2 months while its base image picks up new CVEs. Catching that takes an agent that polls the cluster and reports every running image for analysis.
Runtime SBOM drift, explained: https://t.co/Mk0LAnMp6s
Neil Levine of Anchore speaks Nov 18 at 11:35 AM ET at the Government Security Summit: "Modernizing Legacy Without Breaking Mission: Practical Zero Trust for Government Environments." https://t.co/s9GELFSF0c
👀 CISOs, take note! @dfsoftwareinc uses automated #SBOM generation to build trust fast. See how it's opening doors in data warehousing. 🔗 https://t.co/zxKuOslI8h #SoftwareSupplyChain
Audit fatigue is real when engineering teams spend weeks manually reconstructing deployment histories. Stop manual CVE correlation. Real-time Kubernetes inventory tracking solves this problem. https://t.co/GS2veDtCK4
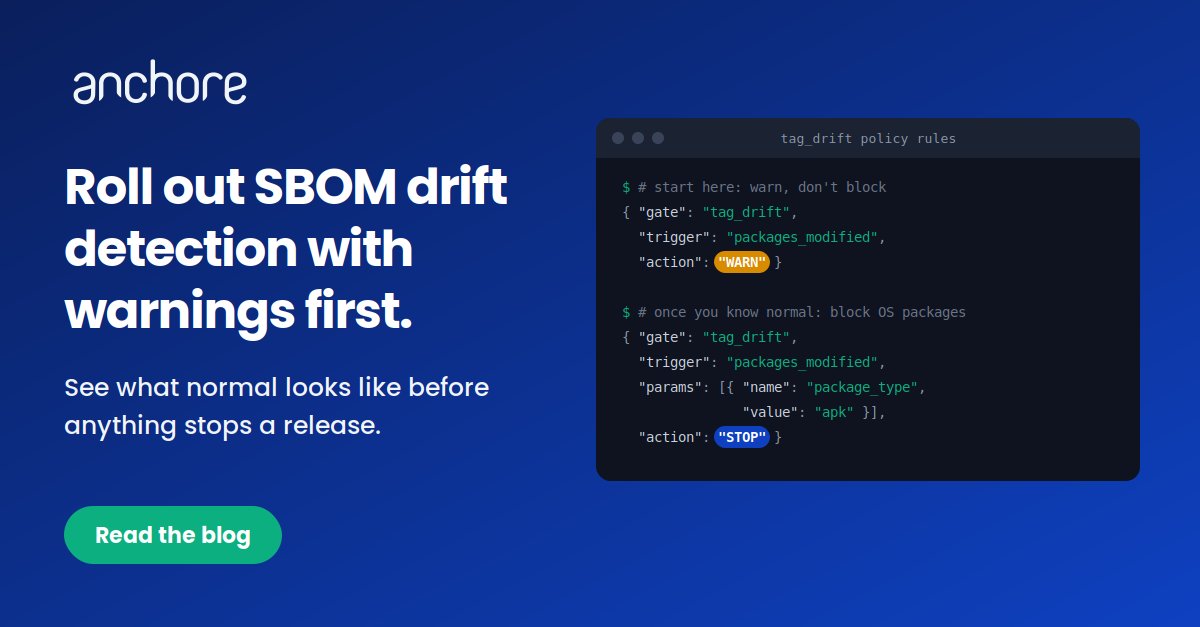
Turned on SBOM drift detection and it never fires? If every build gets a unique tag, there's no previous build of that tag to compare.
Keep a stable tag (latest, nightly, staging) in the pipeline too.
https://t.co/Mk0LAnMp6s
Revolutionizing #DevSecOps in DoD Software Factories with #AnchoreFederal. Secure & compliant software for warfighters. Learn more: https://t.co/flsHxsU5zE #CyberSecurity
Nightly rebuild, untouched Dockerfile. The SBOM diff still shows 14 modified packages and 2 removed.
That's SBOM drift, and your scanner is now checking a component list that doesn't match what's deployed.
https://t.co/Mk0LAnMp6s
#SBOM
New in Anchore Enterprise v6.3: policy gates for AI models. Fail stops the pipeline. Warn lets it continue and flags the model for vetting. https://t.co/nhSJ0t0bN9
🔍 Two tools scanning the same Debian package can return different results. If your scanner misses transitive dependencies, you miss critical CVEs.
Learn to evaluate data accuracy in our new eBook, SBOM 102 👇
https://t.co/mTvbj888r5
Anchore is a Gold sponsor of the Government Security Cybersecurity Summit, virtual, Nov 18. Neil Levine, our SVP of Product, speaks at 11:35 AM ET on zero trust for legacy government systems. Register: https://t.co/s9GELFSF0c
✨ Complete your SBOM journey with Part 2 of our blog series! Learn about Analyzed, Deployed, and Runtime SBOMs. Check it out 👉 https://t.co/60Sxty8B1l #SBOM#DevSecOps#Compliance
Case 31/31: Ivanti Connect Secure. Status: CASE REOPENED. Thousands of organizations affected. New flaws keep surfacing.
That's a wrap on The Anchore Case Files: 31 incidents, one a day. No ghosts here, just 4 cases that won't stay buried. Happy Halloween 🎃👻
New in Anchore Enterprise v6.3: Quick Package Search. Axios 1.14.1 and 0.30.4 were live on npm for about 3 hours with no CVE ever published. Now you can find where you run them. https://t.co/nhSJ0t0bN9
Case 30/31: TeamPCP: GitHub breach. Status: CASE CLOSED. 3,800 internal repos exfiltrated via an 18-minute trojanized extension.
Part of The Anchore Case Files: a real breach or vulnerability, opened daily all October for Cybersecurity Awareness Month.
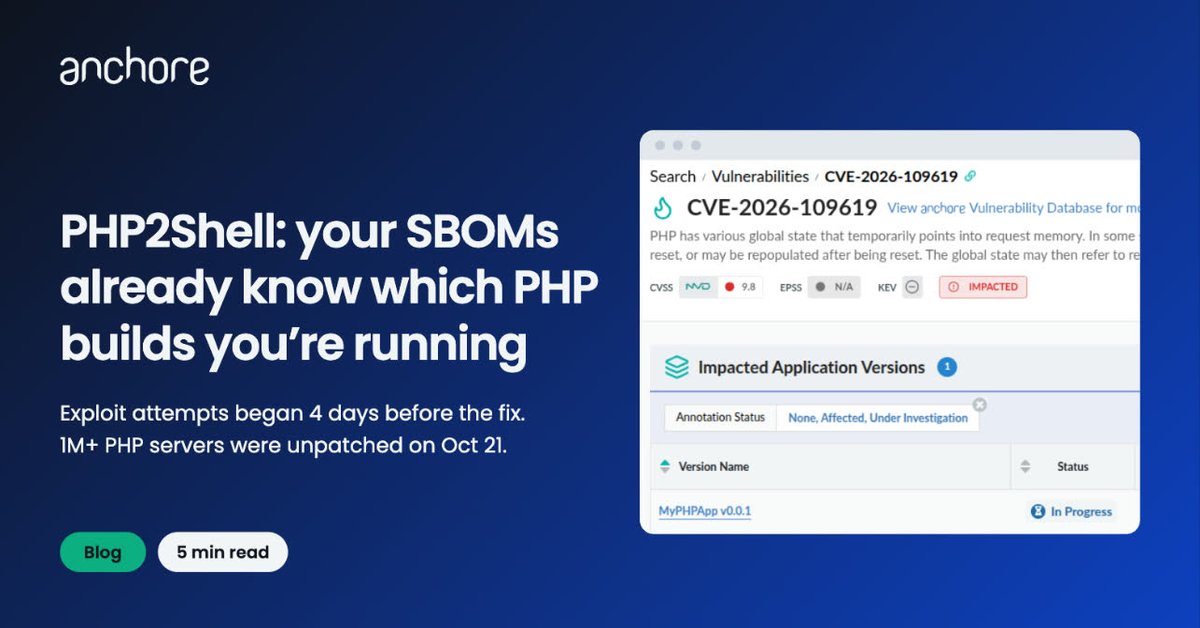
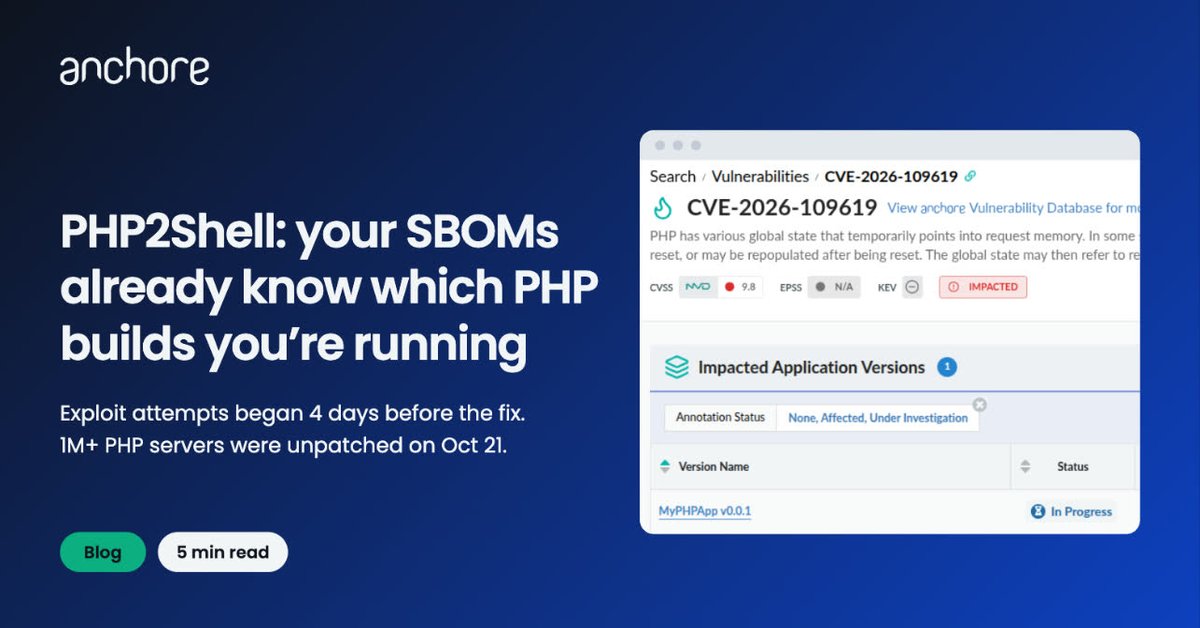
PHP2Shell patching gap: a registry says php:8.3-fpm is fixed, but pods started before the rebuild still run the old digest. How to find them, in our latest blog: https://t.co/dEZ0kyjvl5