The headline doesn't state this was from an Anthropic Bug Bounty program.
It's also unusual that this was released precisely when Anthropic announced today they filed for an IPO to trade as ANT.
Id be interested in reading the write-up from these "ex-DOGE cyber researchers". Until then I am concerned this is a hit piece.
EXCLUSIVE: In less than 12 hours, a group of ex-DOGE cyber researchers were able to penetrate Anthropic’s systems using AI agents — including Slack channels where the most sensitive models are discussed.
This is just weeks after
Anthropic whistleblower Joseph Coxon charged the company w/launching “a hubristic gamble” from a “private company’s Slack.”
Read our story here (gift link):
https://t.co/x6F8Dg6SLR
Chat, I don't wanna sound like a hater, but this guy fucking STINKS at being a criminal
- caught in a few weeks
- only made $210
- ???
We've got Threat Actors on Roblox making more money than him
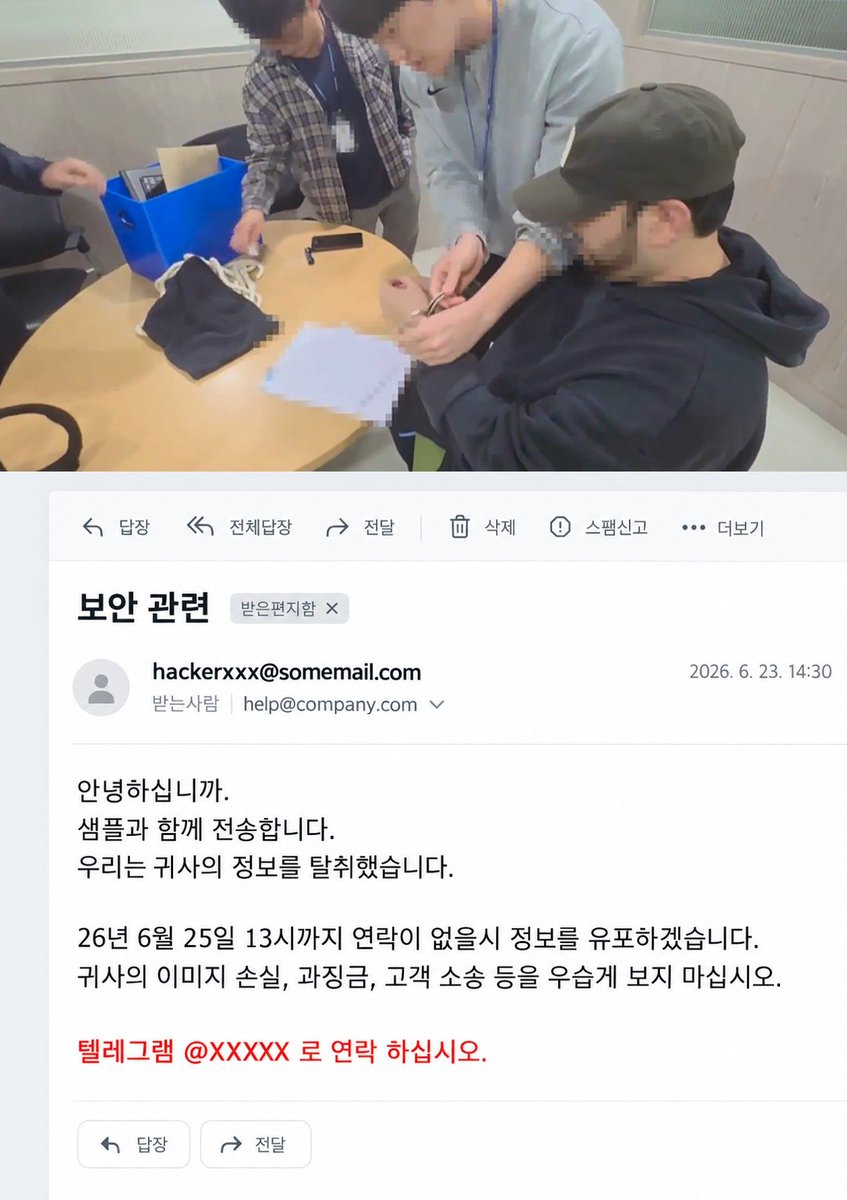
🚨 BREAKING: South Korean police arrested a self-taught hacker accused of using AI to breach 60 firms in six weeks.
Police say his seven-person ring stole 8.2M records from 90+ targets, hospitals among them, and demanded 360M won.
Only one paid. It sent 300,000 won, about $210.
I’m speaking directly to the source who leaked this information to Matthew Cole: Your life as you know it is as good as over.
Take it from me, or any of us who spent years in prison because of him (Reality Winner, Terry Albury, the list goes on).
The White House is smart. They know Matthew Cole is sloppy with sources, and they know he is a coward who folds like a wet blanket. Barack Obama had his way with him. And Trump is about to do the same thing. To all Cole’s sources, best of luck when his book releases this week.
Just spent the last 7 days on the front lines of the vulnpocalypse fending off an active cyber attack on one of our products.
Some thoughts:
- Software factories are going to be required equipment for everyone. There’s just no way to keep up with the pace of highly automated adversaries without one.
- We were lucky because we had spent the last few months getting our software factory running well. It is nice to have for product development but proved to be absolutely essential this week.
- At the minimum you need to have a coding server in the cloud pre-provisioned with read only access to all your logs and all the services you depend on for observability. With that in place you are a prompt away from reasonably good situational awareness, ongoing monitoring with loops, and ability for coding agents to validate fixes against your actual, observed attack patterns.
- Shared coding server also unlocks multiplayer incident response where everyone can see every session and jump in as needed. Sharing session links that can be forked is much higher bandwidth than re-explaining things.
- You don’t need to be Ramp/Stripe/Uber scale to have a working software factory in the cloud. We are a team of 3. Ours is built with an @opencode server (thanks @thdxr!), a forked version of compound engineering optimized for automated workflows (thanks @kieranklaassen!) and a multiplayer agent in slack that handles crons (we have our own harness but pick your favorite here).
- To get our software factory up and running well, we had to stop all new product development for ~6 weeks and just focus on getting the validation systems working that enabled us to reliably shipping PR without human code review. This felt very painful in the moment but was totally worth the eventual speedup in velocity.
- KYC for @AnthropicAI & @OpenAI cyber programs is now easy and quick (at least for defensive access), but a day felt like a lifetime this week. Submit your app now before you really need it.
- Getting Mythos access unlocked a deeper level of analysis that helped us shift from reactive mitigation to proactive patching. Wish we had done this a few weeks earlier. Get started now!
Just found a zero day
If you right click on an executable on Windows, select run as administrator, it will run as administrator
I'm calling it Program2Shell
I'm syncing a bunch of stuff to vx-underground, got lots of stuff working on, and my son has mastered the art of opening doors. He will now open the door when you're pooping.
More silly stuff coming next week. Please keep me in your prayers
Yeah, so pretty much I've scrapped a bunch of YouTube ideas because sometimes I can be a perfectionist about stuff.
I ended up telling myself, "nah, don't be a sissy, just choose a random goop and release the video".
Anyway, the random goop I selected, by what I believe may be divine intervention, is UNC6910 CURLYGATE
Lots of arguments online surrounding who truly discovered PHP2Shell, who gets the clout, etc.
I am the person who found. I found it in like 2013, or something, whatever. Trust me, bro. I'm hardcore and 1337.
Now give me lots of monies and clout. Don't be a hater