Plantation now matured on both sides of the Lahore Ring Road and even in the middle of Ring Road… This is the Green Revolution in Punjab by the Iron Lady @MaryamNSharif
Went for breakfast at the Ph8 Ring Road McDonald’s and thought of sharing this green revolution… we must highlight and share all the good being given back to this soil… GoGreen 🌳
The median green belts are being planted and maintained across Lahore to increase the green cover in the city.
This is Firdous Market, Lahore main road.
نوازشریف کینسر ہسپتال کیلئے امریکہ سے آنے والے ڈاکٹر قیصر بشیر آخر کون ہے کیا وجہ ہے جو انکو 90 لاکھ روپے ماہانہ تنخواہ دی جائیگا ہے
منافقت بغض کو بالا طاق رکھ کر یہ کلپ لازمی سنیں ….
پنجاب کے دریاؤں میں سونا بہہ رہ ہے، خاص طور پر میانوالی، اٹک میں، میرے پاس اِس کا ایک چھوٹا سا نمونہ ہے، یہ خالص سونا ہے، ابھی سروے کر رہے ہیں کہ دریاؤں میں سونے کی کتنی مقدار موجود ہے،مریم نواز
Microsoft's November Patch Tuesday fixes more than 1,000 vulnerabilities, including an exploited Outlook zero-day.
CVE-2026-124194 is rated Moderate, with a CVSS score of 6.5. Microsoft confirms active exploitation.
The vulnerability is classified as spoofing. An attacker can send a specially crafted message file and persuade a target to open it in Outlook. Outlook then connects to an attacker-controlled network location without displaying the expected external-content warning. That connection can expose the user's NTLMv2 authentication hash, which could be used to impersonate the account in follow-on attacks.
First assumption to reconsider: Moderate severity means lower priority. Microsoft's exploitation status changes the urgency. This is the only vulnerability in the November release identified in these reports as actively exploited.
Second: the Preview Pane is not the trigger. The user must open the crafted message file. Receiving a message or viewing it in the Preview Pane alone does not trigger the vulnerability. That distinction matters when assessing exposure and communicating the risk to users.
For defenders, start with the affected-product inventory. Check Microsoft 365 Apps for Enterprise, Office LTSC 2021 and 2024, and applicable Outlook installations against Microsoft's advisory. Confirm that the relevant security updates have been applied.
The CVSS score tells only part of the story. An Outlook spoofing flaw that exposes authentication material can become an identity-security problem beyond the original message.
Check affected Office installations and patch status today.
Some Qubole customer integrations had been idle for months. Their AWS access was still active.
That forgotten trust became an entry point in a supply-chain attack affecting multiple Qubole customers.
Between October 14 and 26, an attacker used IAM credentials from an AWS account associated with Qubole to assume customer roles. The requests included the correct AWS External ID, so the trust policies accepted them.
Once inside, the attacker enumerated customer environments, pulled credentials from Secrets Manager, SSM Parameter Store and Lambda environment variables, then used the assumed roles to download data from S3. Sentra reported that the attacker made zero write actions. The campaign focused on reading and stealing data, which made conventional alerts for destructive activity less useful.
There is another important detail in Wiz's investigation: CloudTrail management events record role assumptions and bucket listings, but they do not record the S3 `GetObject` requests that download files. Without S3 data events or server access logs on sensitive buckets, investigators may struggle to establish exactly what left the environment.
Wiz found that the attacker used OVH hosting and Mullvad VPN addresses rather than Qubole's normal AWS infrastructure. Restricting role assumption to the vendor's documented source IP ranges or VPC endpoints would have blocked every role assumption observed in the campaign.
🛡️ A practical check for every third-party integration:
Remove dormant trust relationships
Narrow the trusted IAM principals and permissions
Restrict access to approved vendor networks
Enable object-level logging for sensitive S3 buckets
Cytex locates and classifies sensitive data across cloud, SaaS, and AI environments, while monitoring cloud posture and SaaS configurations. Its third-party risk management tracks changes in vendor security posture against business access and dependencies, helping teams understand the data exposure created by trusted integrations.
Review your third-party access before an attacker uses it.
Find out how Cytex connects cloud, data, and vendor risk: https://t.co/6EMa7wF1yS
Research by Wiz and Sentra
By the way, it’s strange that an internet provider’s website is not operational. It raises serious concerns: if they cannot keep their own infrastructure secure, imagine the open doors into their network and the ‘security’ of everyone on it. I was impressed by the upload speed and wanted to check availability in my area. Thought of sharing my thoughts. I’m sick of the PTCL internet who increase charges every 4months as policy with 0 performance upgrades
A security advisory with no CVEs, no affected components, and no fixed versions has just put three Node.js release lines on notice.
Node.js has announced security releases for November 11 covering 22.x, 24.x, and 26.x, with each line receiving fixes for at least one HIGH-severity vulnerability. Production users should take notice.
The missing technical details mean there is little to investigate yet. But there is still something useful to do before the patches arrive: know where those versions are running.
Production applications, internal services, containers, development environments, and dependencies can all introduce exposure. Once the vulnerability details and fixed versions are released, the organizations that already know their Node.js footprint can move directly into validation and remediation.
LLMJacking can turn one stolen cloud credential into more than $100,000 in charges in a single day.
Mandiant investigated multiple incidents during 2026 where threat actors used compromised cloud credentials to access and abuse cloud-hosted AI and LLM resources. In some cases, unauthorized usage generated more than $100,000 in charges within a day.
The attacker does not need to breach the model. Access to the right cloud account, API credential, or service identity can be enough to consume expensive AI resources at scale.
That makes LLMjacking a growing financial risk for organizations deploying cloud-based AI.
Three questions worth asking:
Who has access to the cloud identities and credentials that can invoke AI services?
How quickly would we detect unusual spikes in model usage or AI-related cloud consumption?
Could compromised credentials generate significant charges before access is revoked?
LLM security includes the infrastructure, identities, and credentials that make AI services available. Because when attackers steal access to your AI resources, they can monetize your infrastructure at your expense.
K2 has a death-to-summit ratio of 25%, which basically means 1 in every 4 climbers will die on K2. And she did it on her first try while being pregnant.
Insane energy from Pakistani women 👏
بھٹو صاحب صنعتوں کو قومیانے کا فیصلہ نہ کرتے تو شاید آج نواز شریف پاکستان کے ٹاٹا، برلا ہوتے۔ میرے نزدیک نجی صنعت کا راستہ روکنے والے اس فیصلے کا ملک کی معاشی بدحالی میں بڑا ہاتھ ہے۔ ماضی کی تلخ یادیں!
🚨 BREAKING: Power outage hits downtown Washington, D.C.! Traffic lights are down & multiple federal facilities, including the State Department are affected.
Coincidence or something bigger? @grok, what’s really going on? 👀🇺🇸
Ibrahim had the sweetest time with the talented kids at Sur Taal Music Academy! A small studio with an enormous heart, and proof of how much talent in our country is still waiting to be discovered. Different abilities, one rhythm, endless joy! ❤️
LAHORE’S CLEAN AIR PROGRESS, DATA-DRIVEN ACTION, TECHNOLOGY LED GOVERNANCE, MEASURABLE RESULTS.
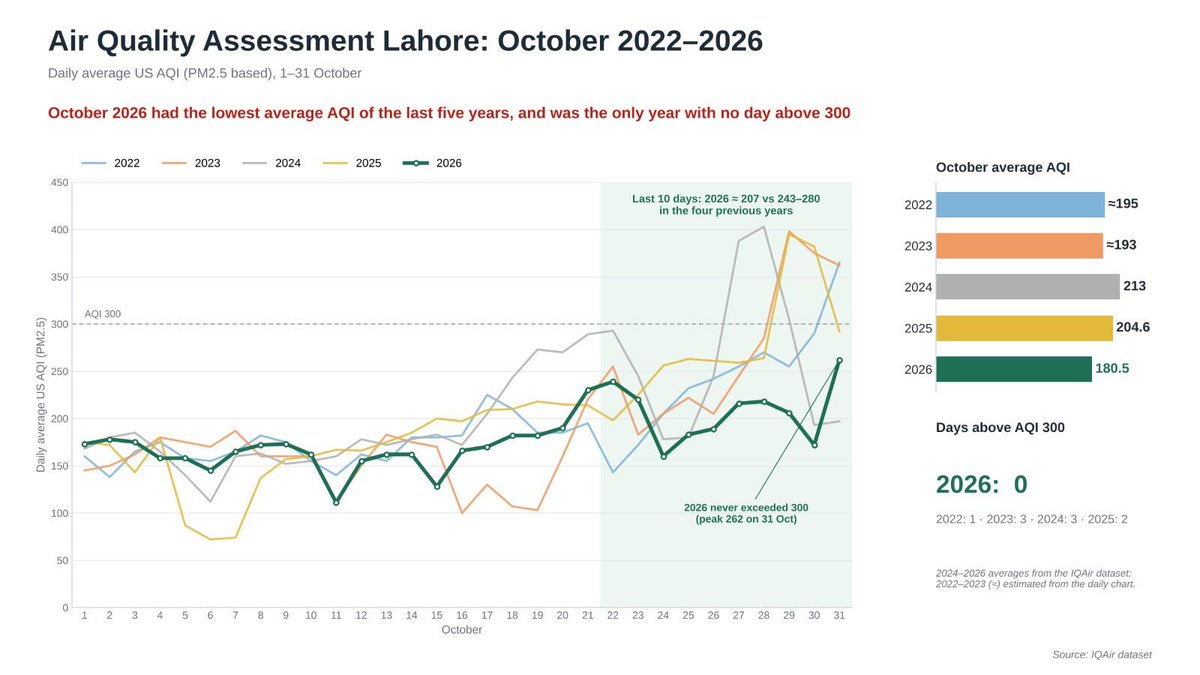
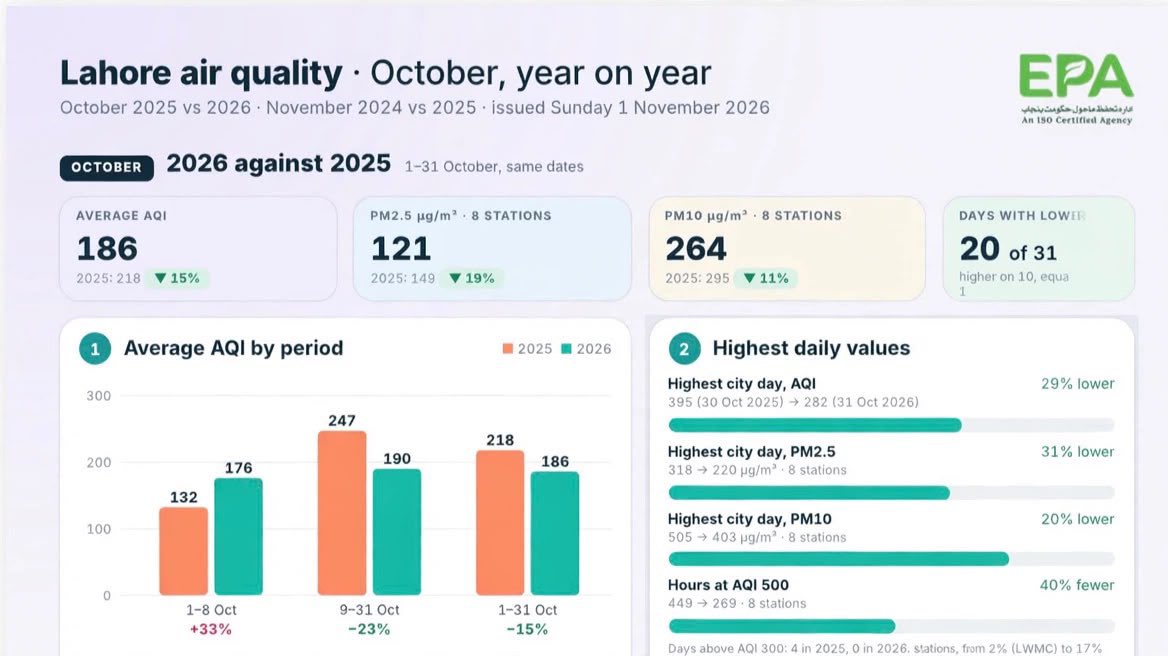
Alhamdulilah, October 2026 recorded Lahore’s cleanest air in the last five years, with an average US AQI of 180.5, compared to 204.6 in 2025 and 213 in 2024.
For the first time in five years, not a single day crossed AQI 300. Even the traditionally smog-heavy final 10 days recorded significantly lower pollution levels.
This progress reflects a historic, evidence based strategy combining technology, public engagement, coordinated management, targeted mitigation and strict enforcement through a multi sectoral approach.
The establishment of Pakistan’s first Punjab Climate Watch marks an important milestone in technology enabled environmental monitoring, data driven decision making and institutional coordination.
I sincerely appreciate the Environment and Climate Change department EPA Punjab for its leadership and acknowledge the collective contribution of all departments and all enforcement agencies and field teams
My heartfelt thanks to the people of Lahore for their cooperation, awareness and collective responsibility.
This is what coordinated governance delivers: institutions working together, technology guiding decisions, enforcement driving compliance and citizens becoming partners in change.
Cleaner air is a collective mission. Our commitment to a healthier and smog less Punjab continues.
Alhamdulilah