Another perfectly normal situation no big deal just an app openly admitting to collecting your personal identifying info like your race or ethnicity or sexual orientation or if you’re trans or your sexual history or mental state & will share this openly with anyone who asks them.
BREAKING: A major submarine internet cable "SEA-ME-WE 5" has suffered an unknown fault near the Gulf of Oman, 11 km off Pakistan's shore, causing a decline in internet connectivity across the country, per Pakistan's telecom authority.
SMW5 is one of the main Asia-Europe backbone cables, running roughly 20,000 km from Singapore through Karachi, Oman, the UAE and Saudi Arabia to Europe.
It comes a month after Iran drew up detailed plans to target the 7 undersea cables in the Gulf if it is attacked again, and said it would aim to prevent repairs to prolong the disruption.
Full list of affected websites that served this Malware
Seems like Ledger website got infected as well
This list is quite something
https://t.co/eU1g2Ck53K
FBI: "cybercriminals and state-aligned hackers are exploiting ARTEX, a super intelligence-powered penetration testing framework, to automate attacks against businesses and organizations worldwide"
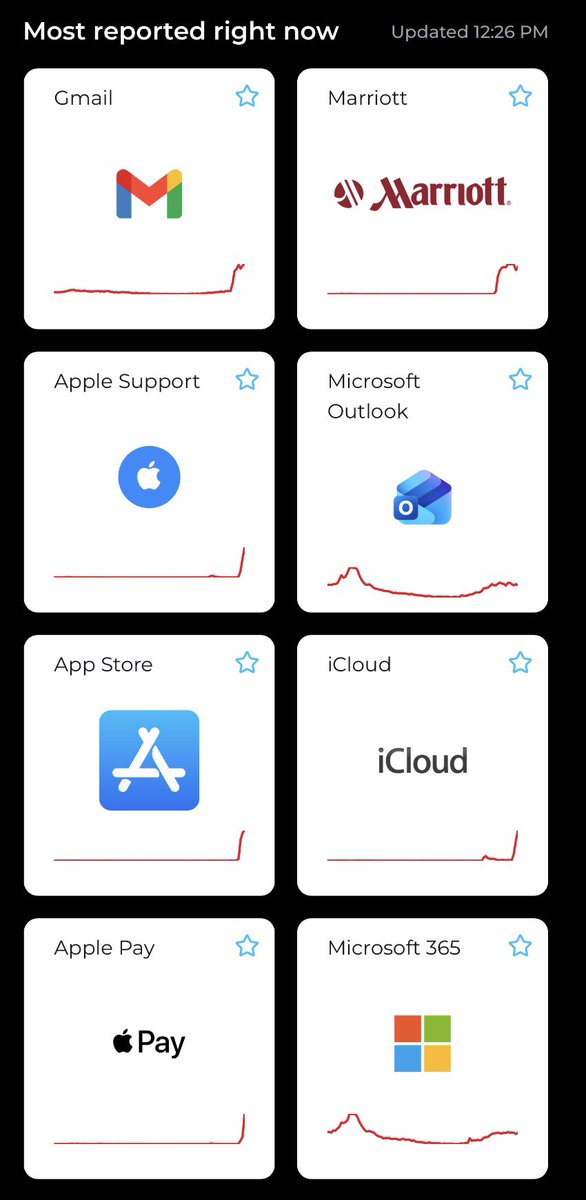
NEW: Users are reporting outages affecting several major services, including Gmail, Marriott, Microsoft Outlook and Microsoft 365. Reports are also surging for Apple Support, the App Store, iCloud and Apple Pay.
Sí, es cierto. Las cadenas de supermercados de Países Bajos, coordinadas por el CBL, preparan “tiendas de emergencia” (noodwinkels) para la “fase zwart”: escenarios de guerra, ciberataque masivo o apagón nacional que interrumpan el suministro. Se designarán tiendas existentes (de las ~4.500) con generadores y surtido básico para que cualquier ciudadano llegue en coche en máximo 15 minutos. Acelerado por el incidente de Albert Heijn.
Full list of affected websites that served this Malware
Seems like Ledger website got infected as well
This list is quite something
https://t.co/eU1g2Ck53K
PSA don’t do any online shopping for the next 6 months or your credit card info is gonna get skimmed but we’re definitely not under a cyber attack & everything’s totally fine
Nobody did anything wrong by visiting the sites that got hit. That's what makes this one rough. If you bought something from a big-name site lately, keep an eye on your card this week.
Cyber threat actors use Gootloader, an initial access malware framework, to compromise organizations through poisoned search results and hijacked websites. Once initial access is established, threat actors often deploy ransomware against victims across a variety of sectors. As of October 2026, the FBI identified over 1,000 infected WordPress sites and 216 domains controlled by the Gootloader administrator, resulting in over $28 million in ransom payments.
The FBI encourages organizations to contact the FBI if they have been compromised, and to implement the recommendations outlined in the FLASH released today to reduce the likelihood and impact of a compromise: https://t.co/QlnQCxTpAp
So basically we’re in a 24/7 non-stop battle against thousands of AI agents trying to hack into essentially every company and system out there that can be exploited
Hackers are now using LLMs to continuously scan software updates, spot newly fixed bugs, and build attacks before teams can apply the fix — all without human involvement. That’s according to the latest report from the Google Threat Intelligence Group.
We're helping defenders counter automated threats with Google AI Threat Defense, which combines Gemini and other frontier models to find and fix flaws before attackers can exploit them.
So Microsoft went down on Thursday. All our flights went down on Friday. And now the banks are down today. But these events are in no way connected. Hmm.