Excited to share that Intigriti has been named the new provider for Adobe's Bug Bounty Program, effective September 1, 2026! 🪲
As our Founder and CEO, Stijn Jans, shared, “At Intigriti, we believe the strongest security comes from working alongside the hacking community. Our focus is on giving Adobe researchers an outstanding experience and supporting that community's continued growth. We are honored that they have chosen us as the new home for their Bug Bounty Program, and we see this as the start of a long and rewarding partnership.”
To researchers: Create your Intigriti account ahead of September 1 to be ready when the program goes live. More details available on Adobe's Security blog.
https://t.co/jgPLs8BdjQ
#Cybersecurity #BugBounty #InfoSec #Intigriti #Adobe
We are at Security BSides Las Vegas handing out our exclusive CTF-style challlenge coin! Come grab yours at the PortSwigger both and try solving it to win swag!
#HackWithIntigriti#DEFCON#DC34
New Armadin research is live! @0xc0ffee_ and I chained four weaknesses in ERPNext (Frappe) to go from a heavily restricted customer role all the way to Remote Code Execution.
Full write-up: https://t.co/GxQVpaG0V3
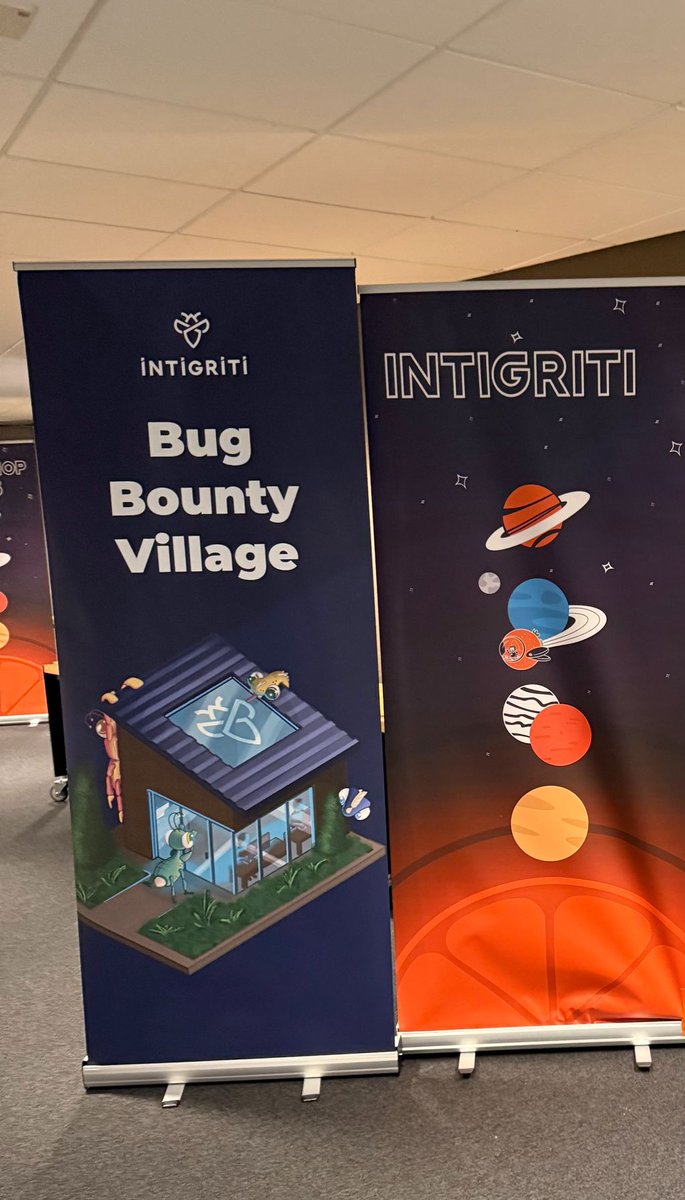
We're live at OrangeCon! 🤠
Come find us at the Bug Bounty Village (room 5) for a live CTF challenge, bug bounty talks, community, and of course, some cool swag! 😎