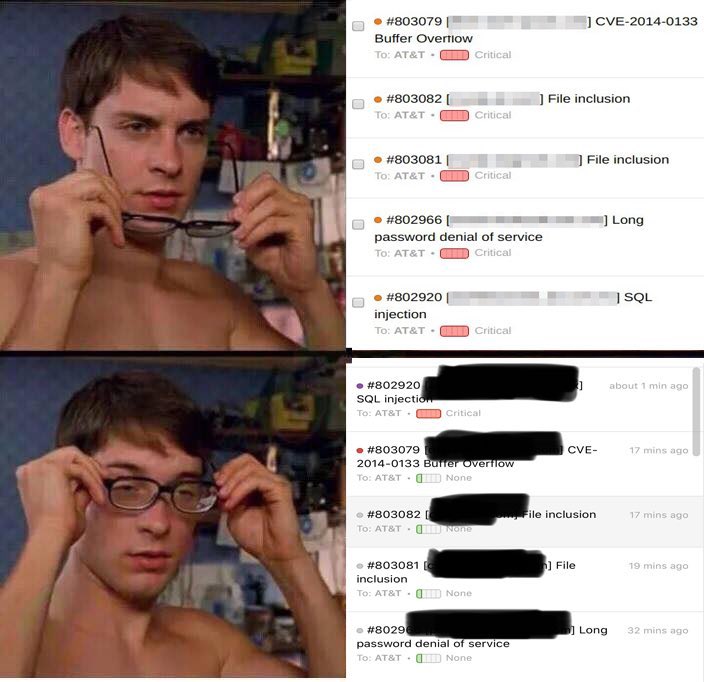
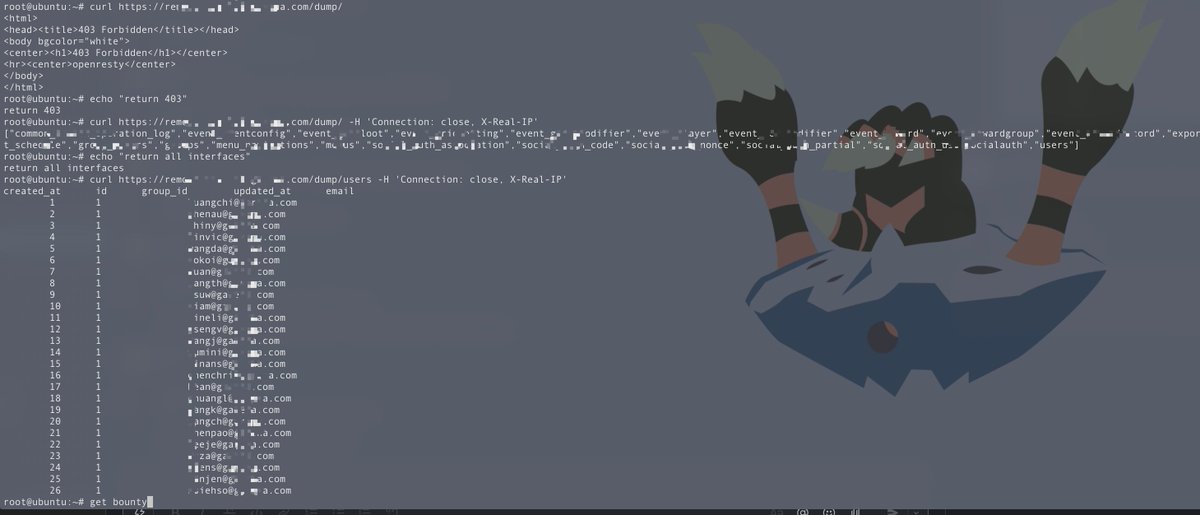
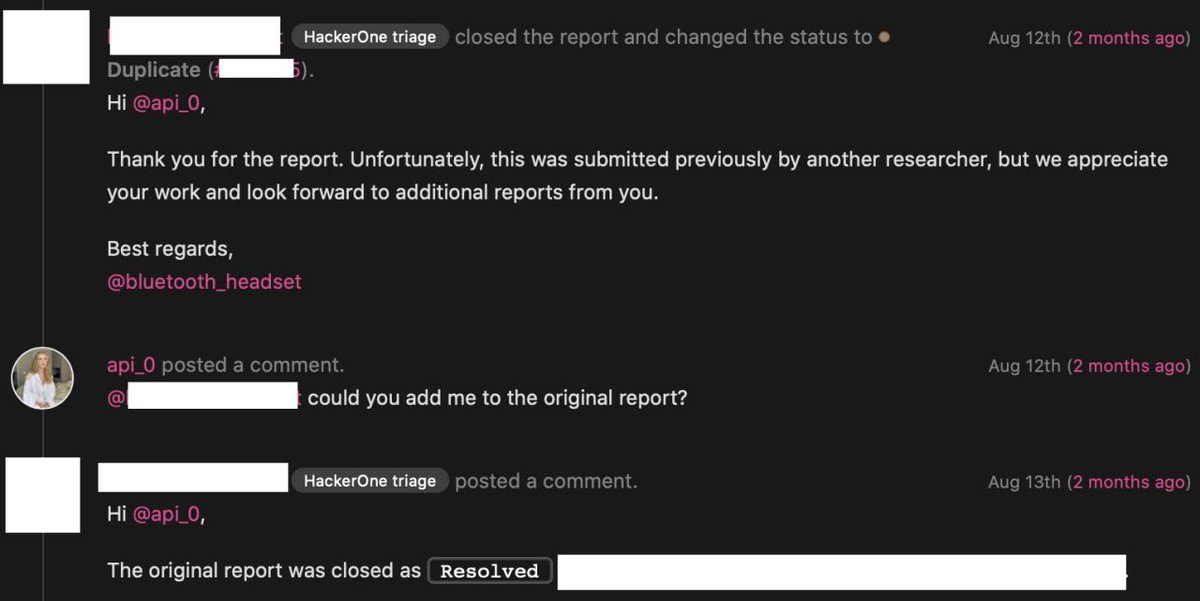
@damian_89_ 1. It seems cancel culture should exist in the bug bounty community as well.
2. My good friend created this: <https://t.co/IdHEMzet2c>
3. @Bugcrowd , seriously? So much time has passed since the publication. Where’s the response?!
Bout to do something that will change the entire landscape of Bug Bounty, at least within the USA. No more hunters getting effed over. Case is basically 99.9% my favor. My lawyer is fucking awesome & the BBP ain’t small. When we win, I hope it changes the industry for the better.
2/2 Also everyone knows the waybackurls utility, which allows you to find a large number of js endpoints. So I have thrown a script that allows you to open each link from the received in waybackurls and check for the presence of keys with trufflehog.
1/2 https://t.co/GTIVwo7Igh
I haven't posted anything here in a while, but I guess I should fix that.
Everyone knows the extension and utility like trufflehog for searching various tokens and keys in the site sources and git repositories.
🔒 Question of the day: How to hunt on restricted web applications protected behind a login page? 🤔 Well, guess what? While most folks tend to overlook these targets, I've pocketed over 5 figures $$$$$💰 from such apps. Bounties for findings on these assets often result in generous High/Crit payouts, ranging from $2,000 to $10,000. 💸
Here's a rundown of what you can do to uncover issues with such targets:
1️⃣Response Manipulation: Create a "match and replace" rule in Burp Suite to swap "false" with "true" and 403/401 status codes with 200. After this, try accessing the app and log in with an incorrect password while keeping Burp Suite active. 🛡️ This trick can often reveal whether the app relies on client-side validation for such apps, potentially granting unauthorized access due to lack of server-side authorization checks.
2️⃣Brute Force: Test common username/password combinations. Many such apps use predictable credentials, like admin:admin, admin:password, etc.
3️⃣SQL Injection: Perform SQL Injection on the login for these targets using tools like SQLMAP or Ghauri. It may take some time, but since it's just a single request, it's definitely worth a shot. Prepare to be amazed by the results! 😲
4️⃣JS endpoints: Review all exposed JS files on the page and extract endpoints using JSBeautify/LinkFinder. Often, you'll discover APIs that are vulnerable to IDOR/Information disclosure, even without authentication, potentially leading to nice bounties.
5️⃣Directory Fuzzing: Utilize FFUF or equivalent tools to fuzz for directories. You can find excellent wordlists at https://t.co/fMUQxJWmA5, tailored to the web application's underlying technology.
6️⃣Breached Credentials Services: Many people employ these services to search for org employees or other credentials linked to the target. If found, they often test them to access the admin page and report the findings (Note - not all programs accept this).
7️⃣Wayback: Always check for archived URLs related to the target, as they may reveal accessible paths without authentication, providing direct access to the dashboard.
There are many more tricks to get around such target apps. We'll talk more in detail with specific examples in future tweets.
🚀Lesson: Do not ignore these types of apps, as they are often a goldmine! 🕵️♂️🌐 #Cybersecurity #BugBounty #WebSecurity #hackerone #bugcrowd #securitytips #questionoftheday #bugbountytips #earn #bounties
🕵️♂️Here's another secret no one will tell you about: A Simple WAF Bypass for Stored XSS that has earned me $$$$💰 so far!
Stored XSS issues can fetch you rewards ranging from $500 to $7500, depending on the program.
WAFs can pose significant challenges when hunting for Stored XSS vulnerabilities, but this simple trick can help you bypass them. By adding 'Content-Encoding: any_random_text' to the request header, you can deceive some WAFs, allowing your payload to slip through undetected. Enjoy the hunt! #bugbounty #securityTips #ethicalhacking #WAFBypass #hackerOne #bugcrowd #bugbountytips
1/🧵When I report an XSS vulnerability I always try to escalate its impact, especially when I know that the Security Team is mature about those subjects.
However, what happens when I find an XSS on a WordPress site that is used only for branding ?
Here is how I do it ;)
Program employees did some mistakes in evaluating my critical reports.When I asked through the email that I took in the program policy to reopen the old report because it wasn't fixed and reproduced again - I was kicked out of the program. I was in the top 10 of that program.1/2
@Geox Hey guys! I have found many vulnerabilities on your site that put your users and your business at risk. Can you give me a contact where you can send these finds?
I want to say huge thanks to @Jhaddix for sharing your stories, techniques, and experience! Also, I want to say thanks to @infosec_au. And of course thanks @pdiscoveryio 🙌🏻 https://t.co/gVge3LUnDz
Since it's 2021 I'd like to go ahead and disclose some bugs I wasn't able to talk about in 2020. These were issues that either got NDA'd or had long remediation timelines.
The following are quick summaries and proof of concepts for some of the simpler bugs:
Want to get more credits for SecurityTrails API™?
Just retweet this tweet and you will get 100 RECURRING API CREDITS 🎉
Ends 28 Nov 2020, 3pm EST. Make sure we can PM you to ask for the email address you signed up with.