@edwardzpeng I like ur takes on AI and cybersecurity, and I also think it will make things tougher for entry level jobs, since junior level work is now fully replaceable by AI, and training AI can be cheaper than hiring and training interns
@S1r1u5_ I was expecting more of the technical side, like building a harness at least or MCP server, tool communication, and handling failures
I expected cases where AI gets stuck, how do you collect, filter, and organize context to get it unstuck? ;)
@S1r1u5_ As I know, Hacktone uses Opus, Codex, or another frontier model.
Suppose a client requests a white-box and provides you with the source code, but at the same time doesn't allow the use of any third-party LLMs due to privacy concerns, what your company do in this situation?
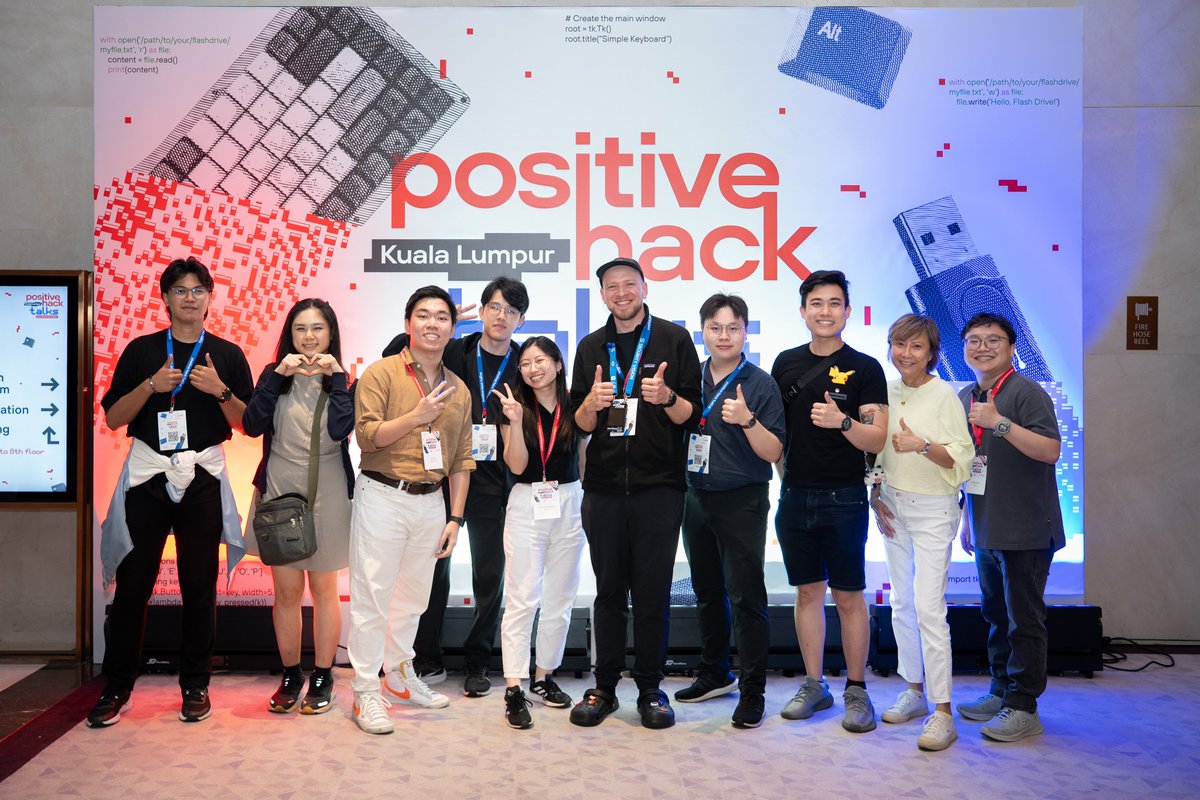
It’s been quite a while after we wrapped up #PHtalks in Kuala Lumpur 🇲🇾 Time to say a few words:
Damn amazing everything went over there! Thank you, community ❤️
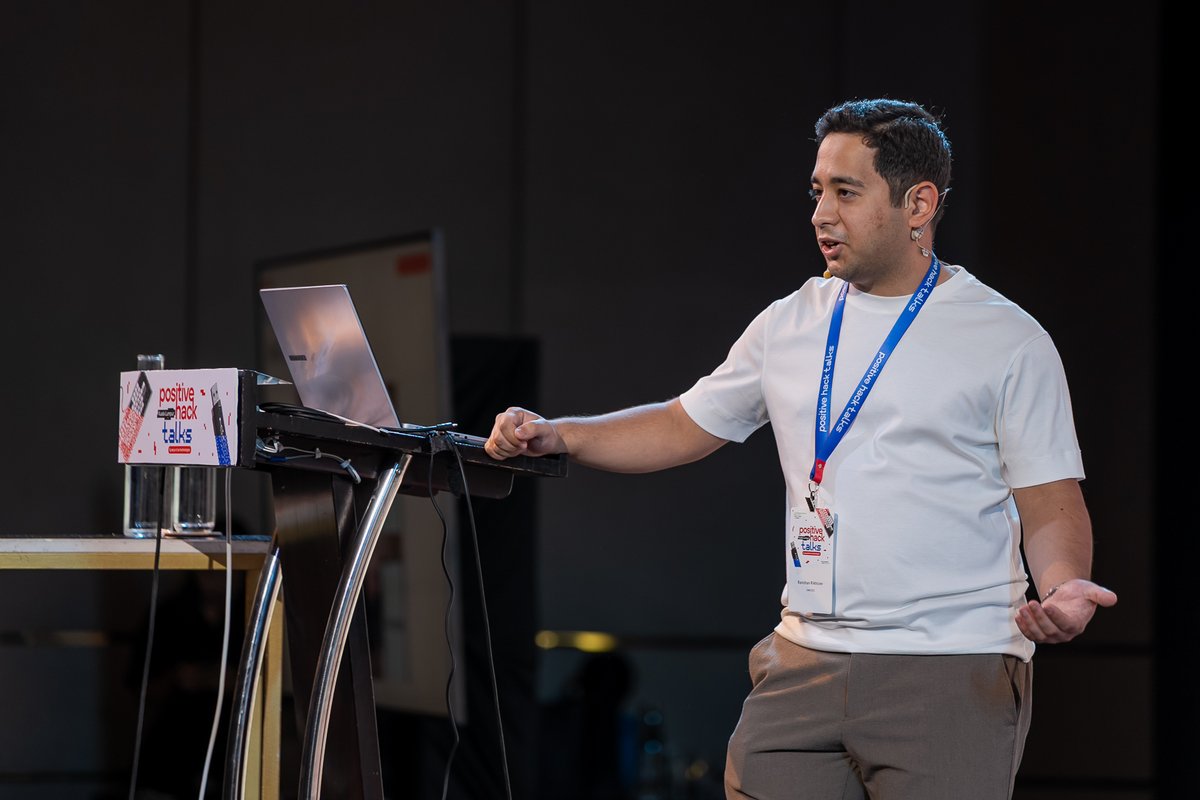
Great to have @arzedlab at #PHTalks Kuala Lumpur with Kernel Wars: Anti-Cheat Reversing, BYOVD Exploitation and Mitigations. An insightful session on kernel-level tradecraft, anti-cheat internals, and what defenders can realistically rely on.
... building the future of Vulnerability Research!
Captain Obvious here: vulnerability research isn't gonna look the same in 5 years than how it looked 5 years ago.
We are in the middle of a transition that is helping us scale vulnerability research in new ways!
2/🧵
Anti-cheats live in the kernel. So do we. Kernel Wars covers anti-cheat reversing, BYOVD abuse, and what actually helps against it. Hear @arzedlab at #PHTalks Kuala Lumpur 🇲🇾: https://t.co/4UZX2BQXI0
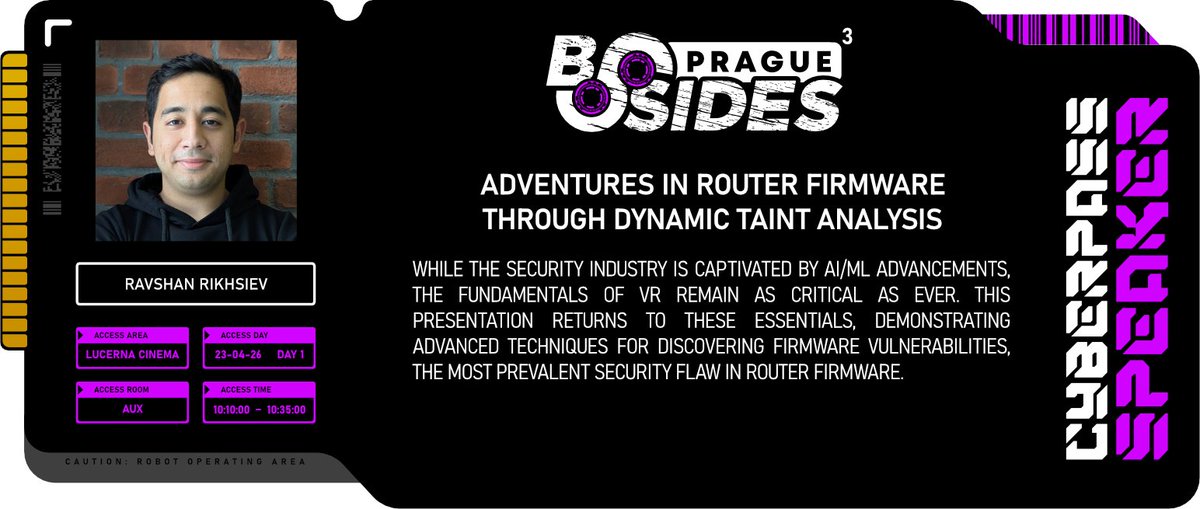
🚨 Speaker Announcement – #BSidesPrague2026
🎤 Ravshan Rikhsiev
Adventures in Router Firmware Through Dynamic Taint Analysis
A deep dive into router firmware vulnerabilities using dynamic taint analysis and advanced VR techniques.
#BSides
@HaifeiLi Probably will be more like "probably there is a zero day but not exploitable"
Folks prompting, but no idea how does AI give results, and most interesting moment, they verify result by asking AI.
I think due to over abstraction, it is hard to find deep bugs with AI.