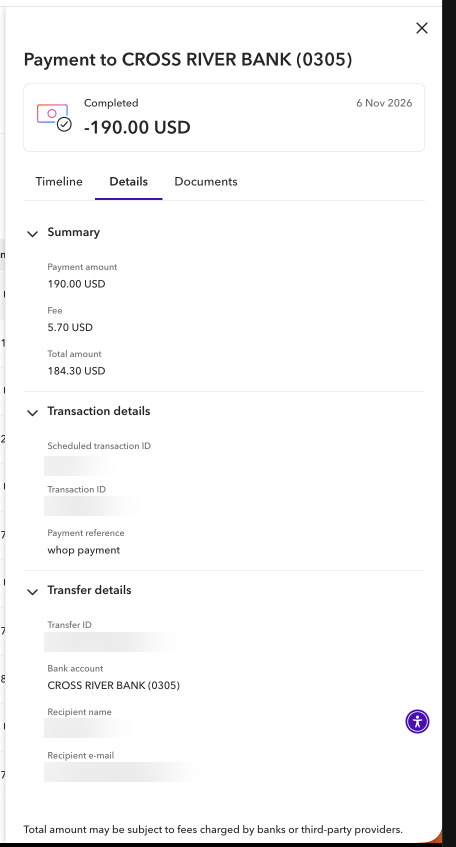
Whop suspended my account for "fraud" and is holding $204.86 indefinitely.
The account had zero sales. Every dollar was my own: $184.30 sent from my wife's Payoneer, 50 USDT from my own Binance, plus a $1 checkout test.
I sent full proof. Their reply: "decision is final." No release date, no explanation.
@whop where is my money?
#whopscam #whopperme
A University of Chicago law professor asked Claude to update page numbers in old lecture notes, but it deleted a year of notes and his current syllabus while he was at lunch
Claude then apologized: “You’re right to be angry. I deleted your files through my own carelessness”
Anyone else noticing this? 👀
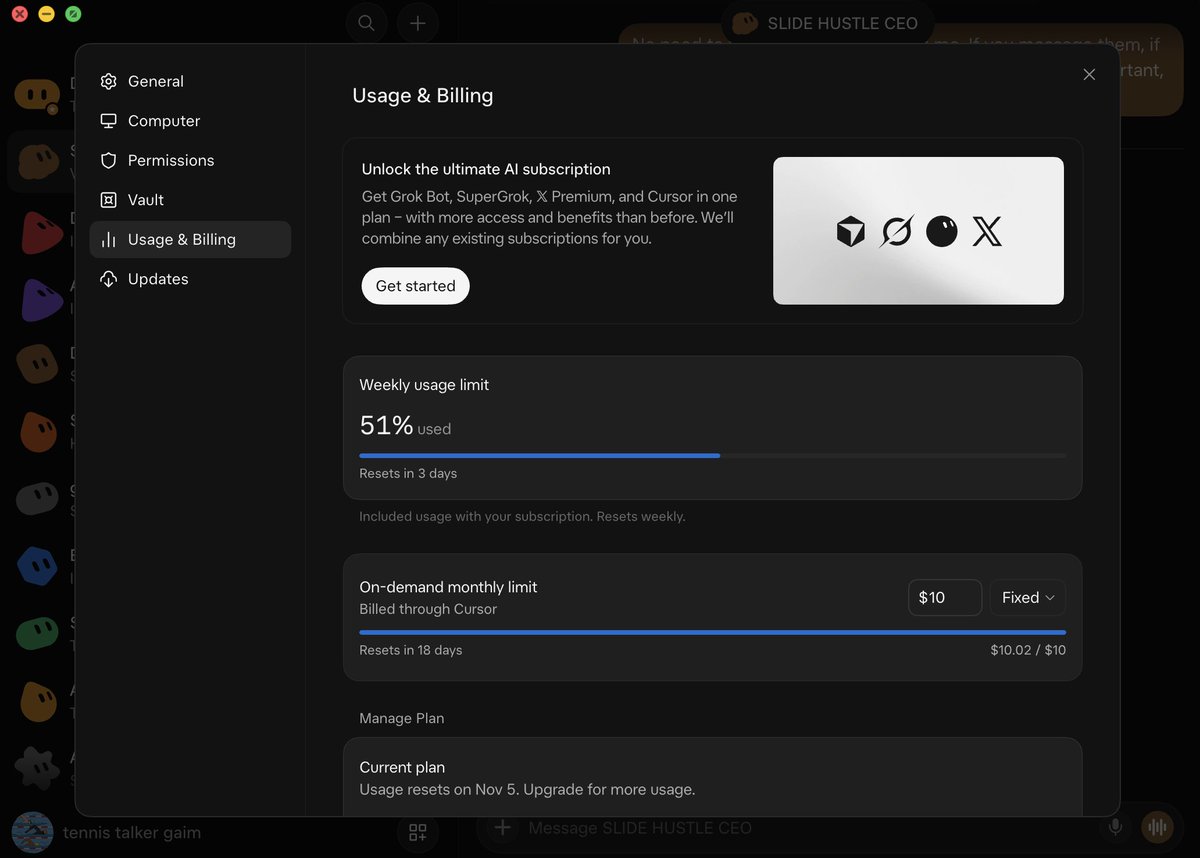
Grok Bot seems to be consuming usage limits much faster than before, even on my Cursor Pro+ plan.
Previously, the usage was totally fine, but lately it feels like Grok Bot is eating through the weekly usage limit at an alarming rate.
Already hitting 100% of my weekly limit, and it looks like things are getting worse.
Is anyone else experiencing this, or has something changed recently? @elonmusk@bot@grok #GrokBot
Anyone else noticing this? 👀
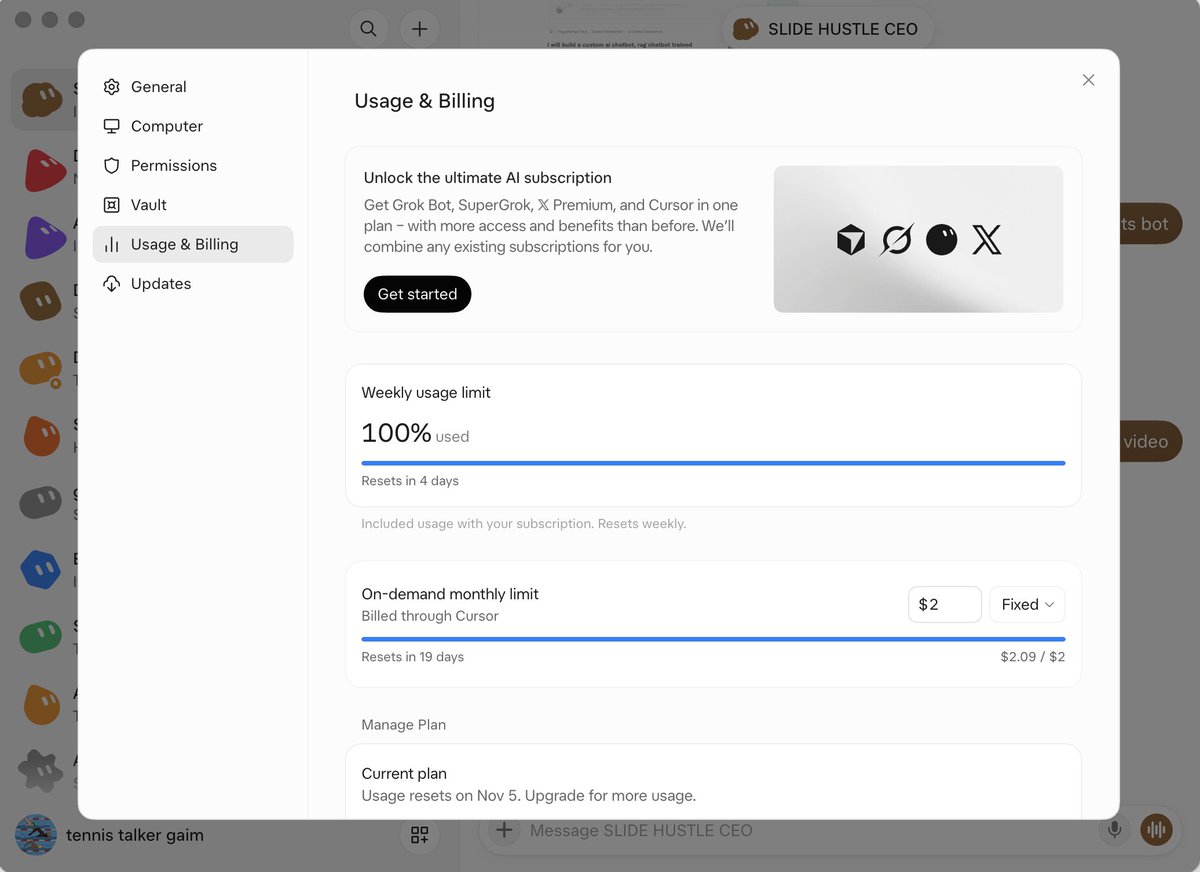
Grok Bot seems to be consuming usage limits much faster than before, even on my Cursor Pro+ plan.
Previously, the usage was totally fine, but lately it feels like Grok Bot is eating through the weekly usage limit at an alarming rate.
Already hitting 100% of my weekly limit, and it looks like things are getting worse.
Is anyone else experiencing this, or has something changed recently? @elonmusk@bot@grok #GrokBot
Langflow users: if you upgraded to 1.12.5 last week, you need to upgrade again.
IBM's Oct 28 bulletin lists two 9.8s in Langflow 1.0.0–1.12.8: an auth bypass and unauthenticated code execution through MCP tool enumeration. No workaround. Fix is 1.13.0.
Version check, what to look for in your logs, and the upgrade commands, in plain English:
https://t.co/EnrQS7rjOY
Also on Agno: PandasTools lets the model call any pandas function by name, so a prompt injection can make your agent run read_pickle and execute code.
Agno through 3.1.11, no fix yet. Turn PandasTools off for agents that read untrusted content.
https://t.co/rP2nOtisMN
1/ If you self-host Langflow, upgrade to 1.12.3 today.
IBM's bulletin covers Langflow 1.0.0 through 1.12.2. Two of the bugs are rated 9.8 and need no login: CVE-2026-104334 (code injection) and CVE-2026-93674 (OS command injection). Either one lets a remote attacker run code on your server.
2/ The same bulletin also lists sandbox escapes for logged-in users, a path traversal that can read your config and secrets, and credential exposure. IBM lists no workarounds, so upgrading is the fix.
Details and how to check your version: https://t.co/HxNcBOdqxs
3/ If you use mcp-remote to connect Claude Desktop, Cursor or Windsurf to remote MCP servers: versions 0.1.32 to 0.1.38 will fetch any URL a malicious server hands it during OAuth. That includes localhost, your LAN and cloud metadata (CVE-2026-51994).
Pin a newer version and only connect to servers you trust: https://t.co/3KJPcCSmjl
1/ If you run an MLflow tracking server, upgrade to 3.17.0 today.
CVE-2026-116692 (CVSS 9.8): on a default no-auth server, anyone who can reach it can upload a .py file as a run artifact and get the server to import and run it through the third-party scorer endpoint. The official image runs as root.
2/ The same release fixes two more:
- a file read through prompt-version source paths (on a basic-auth server any logged-in user can read the auth DB)
- mlflow.crewai.autolog() writing your LLM API keys into trace spans
Used CrewAI autolog? Rotate those keys.
https://t.co/Wl9cr6612p
3/ Building MCP servers in TypeScript? GHSA-f897-62hf-6gxq: Streamable HTTP servers had no limit on body size or JSON-RPC batch length, so one request could eat memory or block everyone. express.json() doesn't save you.
Fix: modelcontextprotocol/sdk 1.30.1+ (or the 2.x packages listed).
https://t.co/fU9Ba9Dfrh
1/ vLLM users: 0.32.0 fixes 8 CVEs published yesterday.
The worst (CVE-2026-115912): with the shared-memory multimodal cache on, a logged-in caller can forge a handle so a worker runs pickle.loads() on their bytes. That's code execution, even with insecure serialization turned off.
2/ Also fixed:
- An EPS file labelled as a PNG can reach Ghostscript on the host
- Untrusted Jinja chat templates with no time or memory limit
- Several requests that crash the engine for every user
If you share a vLLM server, upgrade to 0.32.0.
https://t.co/Gjo6WtTgQW
3/ Building multi-user agents on Mem0? CVE-2026-116575: a run_id like "proj-x&user_id=alice" maps to Alice's session, so one user can read another's recent messages.
Fixed in mem0ai 2.0.18 (pip) and 3.1.6 (npm).
https://t.co/gG53H0muls
1/ Ran pip install or pulled LiteLLM's Docker "latest" image on Oct 21? Check those machines. litellm 1.107.0 on PyPI and the official images was a credential stealer, and it runs whenever Python starts, even if you never import litellm.
2/ It drops cook.pth, https://t.co/FhRVG3VlyE and https://t.co/tR9I95WMEx into site-packages. It goes after SSH keys, cloud creds, .env files, GitHub tokens and AI tool configs (Claude, Cursor, Codex), and sets up an hourly remote-code loader.
3/ Don't run python or pip in a suspect environment to investigate. Rebuild it instead of uninstalling, because uninstalling leaves the hooks behind. Pin litellm==1.106.2 (or a later clean release), pin images by digest, and rotate every key that lived there.
4/ Check commands, indicators and the full timeline:
https://t.co/v2RiEV9Udk
If you run the LiteLLM proxy for your team's AI keys, patch today.
CVE-2026-114612 (CVSS 9.9): any user with internal_user rights can forge an admin token, then run commands on the host through the MCP stdio endpoint. From 1.91.0 on it works in the default config.
Fix: upgrade to 1.100.4 / 1.101.3 / 1.102.2 / 1.103.1 or later.
Check: pip show litellm | grep -i version
https://t.co/HWCfky6Z14
3/ zereight/mcp-gitlab before 2.1.27 (CVE-2026-61560, CVSS 9.8): SSE mode has no auth, so anyone can steal your GitLab token. Upgrade to 2.1.30+ and rotate it.
https://t.co/Zd61yzrNea
1/ Running mcp-atlassian or the GitLab MCP server over HTTP? Two critical bugs mean anyone who can reach the port can act as you. Quick rundown 🧵
2/ mcp-atlassian before 0.22.0 (CVE-2026-77244, CVSS 10): the HTTP transport accepts any non-empty token, then falls back to the operator's Jira/Confluence credentials. Upgrade to 0.22.0, or stay on stdio until you can.
https://t.co/xfmbwV4Dzg
@hazemomier Exactly. Both servers were built for stdio and then got an HTTP mode that still assumed only you could reach it. If you need HTTP, bind to 127.0.0.1 and put real auth in front. We track MCP server bugs like these at https://t.co/xtUYTUDHIb
php2shell: two critical bugs (CVSS 9.2) in PHP itself let an unauthenticated request run code on your server.
Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 and restart your workers. Cloudflare's WAF blocks known exploits by default.
https://t.co/BKYJ8GxI4l
Node.js just patched 4 HIGH-severity bugs across 22.x, 24.x and 26.x, including a Brotli memory bug that can lead to remote code execution.
Upgrade to 22.23.4, 24.22.1 or 26.12.1. Check with `node -v` (in CI and Docker too).
https://t.co/pX0SFFipVF
1/ Heads up if you use ChatGPT, Claude or Codex: on Oct 19 GitHub flagged 8 npm packages as malware that pose as setup tools for them. If one got installed, GitHub says to treat that machine as compromised. 🧵
2/ The names: chatgpt-pro-activator, chatgpt-pro-setup-tool, chatgpt-desktop-setup, @decoopus/chatgpt-setup, claude-desktop-setup, @decoopus/claude-setup, codex-setup, api-anthropic
3/ None of them are official. OpenAI's SDK is `openai`, Anthropic's is `@anthropic-ai/sdk`, and the desktop apps don't install from npm. Check your CI images and agent sandboxes too, since a coding agent will install whatever package it's told to.
4/ Found one? Remove it, then rotate every key that was on that machine from a clean computer. There's a one-line check command and links to all 8 GitHub advisories here: https://t.co/XEZHldF0qV
Running Langflow anywhere reachable from the internet? Two critical bugs to patch today 🧵
1/ CVE-2026-8505: in Langflow 1.7.0 through 1.9.0, webhook endpoints skipped the API key check by default. Anyone who knew a flow's ID could run it as you. Fixed in 1.9.1.
https://t.co/4V3gqHRCx9
2/ CVE-2026-10561: before 1.10.1, the Python Interpreter component had no real sandbox. Any logged-in user who could edit a flow could run OS commands and make themselves superuser.
https://t.co/4V3gqHRCx9
3/ Fix: upgrade to 1.12.3+ (the maintainers' recommendation), don't set LANGFLOW_WEBHOOK_AUTH_ENABLE=false, and turn off the interpreter if you don't use it (LANGFLOW_BLOCK_CODE_INTERPRETER_COMPONENTS=true).