A new CVE is announced. Are you affected and is there a patch? Are your security defenses already blocking exploits? Get answers with Atomicorp CVE Research Tools. Explore vulnerability research, attack patterns, and real-world results #CVE#ModSecurity https://t.co/e4OSE89CP5
A WAF can be running, correctly configured, and blocking known attacks while leaving significant gaps in application security. Gain greater visibility into application behavior and advanced threats. https://t.co/nDzmoOUyUO
#WAF#WebApplicationSecurity
Security tools generate mountains of data. SIEM helps make sense of it.
Connect the dots and detect threats, investigate suspicious activity, and monitor compliance—all from one central view. Paired with EDR, SIEM can turn security data into action. https://t.co/MyIJ4ZPmc5
#SIEM
Got a long-running production environment where monitoring and detection aren't possible due to end-of-life and unsupported technology? Atomicorp provides a noninvasive endpoint detection and response (EDR) solution with #endoflifesupport. #OSSEC https://t.co/qYLxRw54ug
Unpatchable software systems are an unfortunate reality for many organizations. Compensating security controls and a defense-in-depth strategy can reduce exposure while keeping critical systems running. #ITSecurity#OTSecurity#VulnerabilityManagement https://t.co/3AwlVgP4Ed
In a world where the web and cloud provide so much of today's infrastructure, computing endpoints and hosts remain a target in IT and OT environments. Find out how #EndpointProtection, #OTSecurity, and #OTVisibility can be noninvasive and affordable. https://t.co/2Iuibjy9aR
Legacy and unsupported web applications can be targets for CVE and KEV exploits. When you can't patch, shield with Atomic ModSecurity Rules and Atomic WAF. Visit the web application security page. #webapplicationsecurity#LegacyApplications#WAF https://t.co/gHZdpEZap9
Knowing that a change took place in your IT or OT environment is not enough. Detect the who, what, where, and when with Atomic OSSEC continuous file integrity monitoring. #fileintegritymonitoring#OSSEC#EndpointSecurity#ChangeDetection https://t.co/QXl5PPNTuj
The OpenAI and Hugging Face incident shows what happens when an autonomous attacker can probe, adapt, and execute thousands of actions at machine speed—and why defense in depth matters more than ever. #AICybersecurity#AutonomousAI#DefenseInDepth https://t.co/zQ2weNdhG2
New in Atomic OSSEC: graphical application allowlisting and blocklisting for Linux and Windows. Define what software can run, block unauthorized apps, inspect executables, and manage application control rules from a GUI.
https://t.co/pTrbGa5aIx #LinuxSecurity#WindowsSecurity
AI accelerates vulnerability analysis, exploit development and attack execution, turning days of response time into only hours. Give yourself more time to fight back with layers of affordable EDR security. #AIAttacks#DefenseInDepth#continuousmonitoring https://t.co/QmRrixACS2
Buy one Atomic ModSecurity Rules license and get a second license FREE thru Aug. 31.
Protect Apache, nginx, IIS, APIs, WordPress, legacy web apps with advanced, continuously updated commercial WAF rules and virtual patching. #ModSecurity#AppSec#WAF https://t.co/U3ip5mCslF
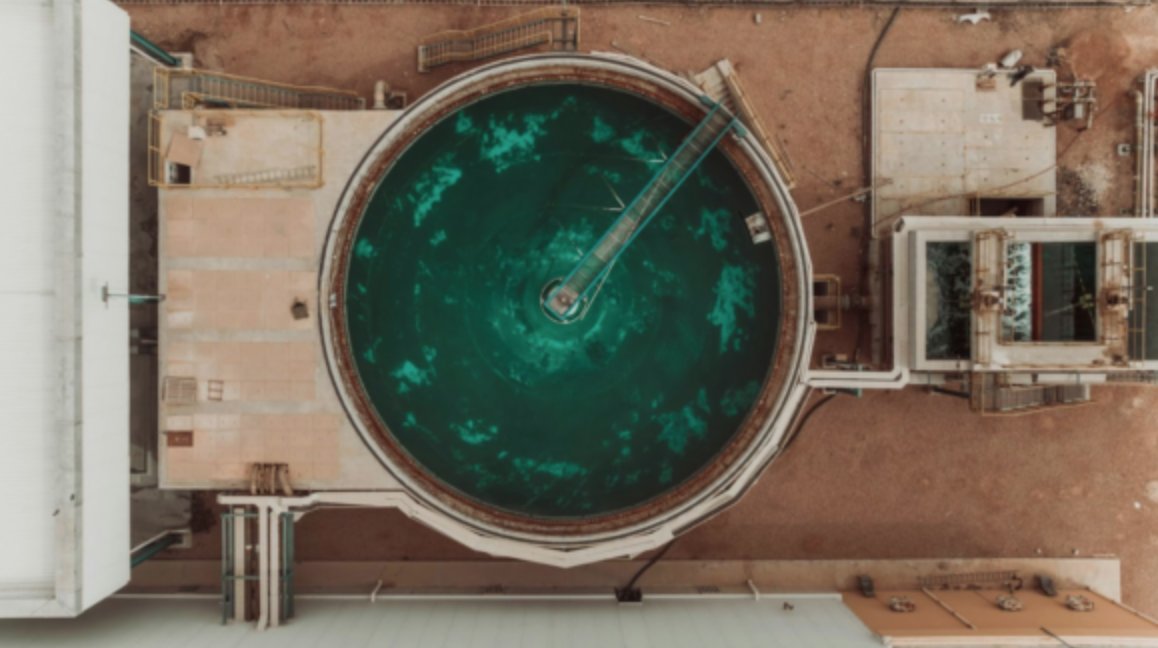
The attacks on U.S. water utilities are a reminder that OT security requires a different approach than IT.
Key steps:
• Disconnect internet-exposed PLCs
• Secure remote OT access
• Continuously monitor engineering workstations & IT/OT convergence . . . https://t.co/YDTuJj5AzJ
Facing compliance uncertainty? Atomicorp can help with your NIST 800-171 compliance and FedRAMP and CMMC readiness. #NIST800171#compliance#OSSEC#CMMC#CUI https://t.co/3sTEI3xYBU
The #wp2shell exploit shows why protecting against underlying software weaknesses matters. Atomicorp blocked every tested exploit class while allowing legitimate application traffic to continue—without waiting for a CVE-specific rule. #CWE#cybersecurity https://t.co/v3pXaCya5S
AI is accelerating cyber attacks faster than many can patch their environments. Continuous compliance monitoring helps identify security and compliance gaps as they emerge—not months later during an audit.
#ContinuousCompliance#OSSEC#ITSecurity https://t.co/ha119VaRjb