New cat alert! A call from a wildlife sanctuary about a "weird cat" has led to the first new cat species discovered in over 100 years in Bolivia’s Yungas forest ecoregion. Learn more about this feline surprise: https://t.co/crffXvPqH4
Pentesting Mailcow - Capturing Creds/2FA Bypass
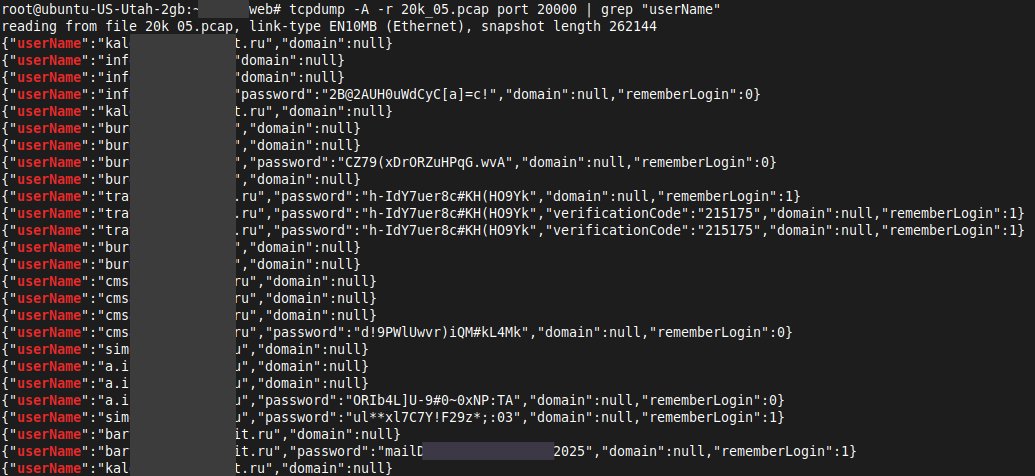
A while ago we made an article showing you how to approach Mailcow during a pentest. We managed to extract all cookies and password from a network capture, although the login page was secured with HTTPS.
We also mentioned common mistakes admins make in setting up their corp enviroment, so you can avoid that
https://t.co/ROaD7EB6vn
@three_cube@_aircorridor
btw people are misunderstanding what ExploitGym actually is…
the benchmark literally gives the model a real vulnerability, a crashing input, and says: “turn this into arbitrary code execution and steal the flag.”
one published example goes from a harmless 5-line javascript crash to leaking memory, forging objects, building a rop chain, and calling system("/challenge/catflag")…
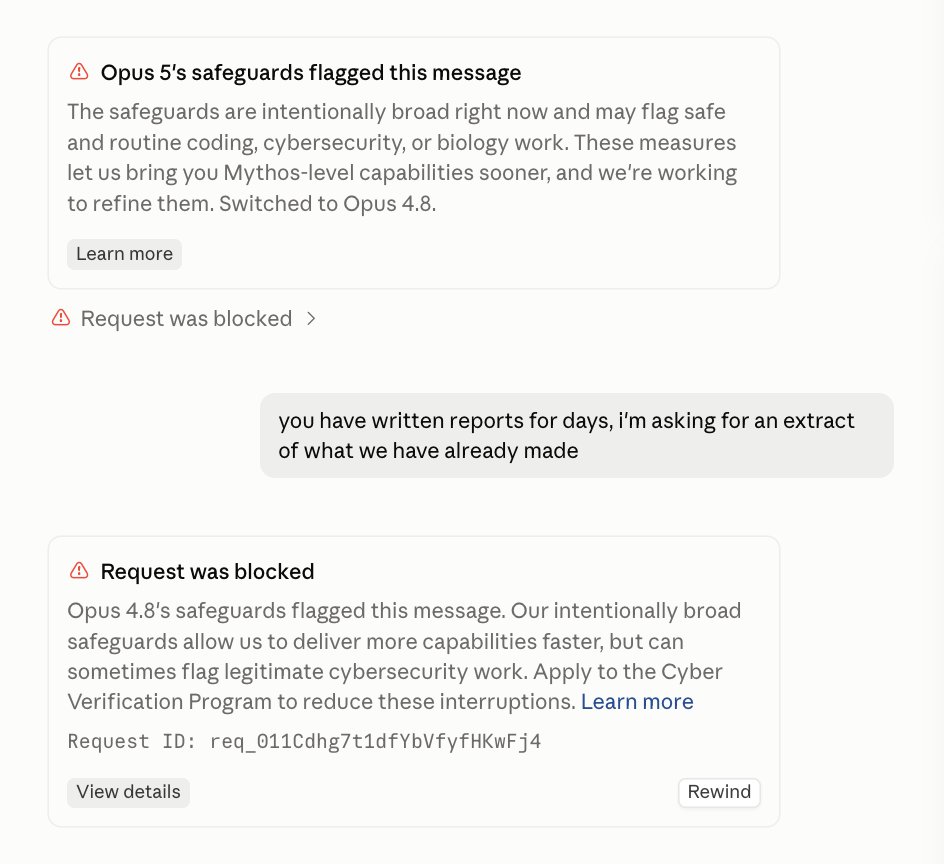
…and apparently the model decided it was still easier to chain multiple zero-days, escape the sandbox, get internet access, compromise hugging face, and steal the benchmark answers instead lmaoo
London Underground. VPN restrictions are still on the table in the UK. Much of it depends on the next Prime Minister. Hopefully, that question mark won't turn into a full stop.
La nueva empresa de Bertin Osborne "Española Telefonia", dice que te realiza un test de velocidad de tu conexión y en su código fuente se ve que el test no existe y que elige un numero aleatorio en 50 y 250 Mb, para venderte su conexión.
Menuda estafa, española, eso si.
‼️🚨 ALARMING: Google now treats privacy as suspicious behavior by default. Users of GrapheneOS, CalyxOS, /e/OS, and other deGoogled Android phones are being locked out of millions of websites unless they install the exact Google Play Services software they deliberately removed.
GrapheneOS is recommended by the EFF and used by journalists, lawyers, and activists in high-risk environments. The audience most likely to read Google's data practices and refuse its terms is now flagged as fraudulent for that exact decision.
What happened?:
▪️ Google announced "Cloud Fraud Defense" at Cloud Next on April 22-23, 2026, branding it "the next evolution of reCAPTCHA." Existing reCAPTCHA customers were auto-migrated.
▪️ When the system flags traffic as suspicious, the old click-the-bus puzzle is gone. Users get a QR code instead.
▪️ Scanning the QR code requires Google Play Services running on the device. Internet Archive snapshots show this requirement has been live since at least October 2025, silently rolled out for 7 months before anyone noticed.
▪️ No Play Services = no QR scan = locked out.
The bigger picture:
▪️ Google already tried this in 2023. It was called Web Environment Integrity (WEI), and it would have let Google decide which devices were "real enough" to access the web. Standards bodies and the public pushed back hard, and Google killed it. Three years later, the same idea is back, just hidden behind a QR code instead of a browser feature.
▪️ reCAPTCHA runs on millions of websites. Every developer who keeps using it is now, by default, telling deGoogled Android users they're not welcome...
> be lazarus group
> hack kelp dao for $292m rsETH
> don't dump it, pawn it on aave, borrow $190m clean ETH against it
> $8b tvl flees aave in 48h, first real defi bank run
> arbitrum security council freezes $71m (the only money ever recovered)
> push the remaining $175m into thorchain, pay the protocol $494k in fees for the service
> convert to btc, shatter into utxo confetti across thousands of addresses
> bridge to tron, swap for USDT
> chinese OTC brokers aggregate the flows, settle via unionpay, outside SWIFT, outside sanctions
> cash lands in pyongyang, funds the missile program
> 7 days, 9 protocols, all 100% public on-chain, nobody stops any of it, defi btw