Imagine after a loooong week you get a well-deserved day off. You decide to go to #Starbucks for your favorite drink. Five baristas but not one can make your order right. And they want a tip. Here's a tip... get the fuck out of here .#FFS
Today Instagram had this massive exploit where hackers were just stealing rare handles left and right. Hundreds of accounts gone.
People losing handles they’ve owned since 2010, some worth hundreds of thousands.
I own a few rare ones so I was actually stressed watching this happen in real time, which I haven’t been in years.
Obama White House account got hit.
These aren’t some random new accounts, these are verified, locked down accounts and they still got compromised.
The thing is the exploit is so simple it’s almost funny. Attacker goes to Forgot Password, says their account is hacked, turns on a VPN to match the target’s location (which now you can find on the about section of the page).
Instagram’s AI support flow asks them to verify with a selfie.
They grab a photo from the target’s profile, run it through an AI video generator to make an animation of the person’s face moving around, upload that to Meta’s AI as proof.
And Meta’s AI just accepts it because it can’t tell the difference between a real selfie and an AI-generated video of someone’s face
.
Once verified they change the email to theirs. Password reset link goes to their email. They own it now. 2FA gets bypassed somehow in the process but honestly I don’t know exactly how, just that it did.
Point is even locked down accounts went down.
Then you try to recover your account and you’re talking to a chatbot that has zero ability to help.
You can’t escalate to a human. You’re just stuck. Your asset is gone and there’s no one to call.
The whole thing just highlighted how stupid it is to automate account security without any human in the loop.
One AI fooling another AI while there’s literally no person anywhere to catch it.
Meta took hours to even acknowledge it while accounts were getting stolen every minute.
Now thankfully it’s patched but I don’t think it will be the last one. Stay safe!
@Costco, making people scan just to enter the warehouse creates an unnecessary bottleneck. Esp when members have to scan their membership to pay. Figure out a different solution if you're try to control who is entering.
China's biggest cybersecurity company apparently just shipped an AI assistant with its own SSL private key sitting inside the installer. Qihoo 360, think Norton or McAfee, but dominant across the entire Chinese market
It appears that their new AI product, 360安全龙虾 (Security Claw) bundles a wrapper on @OpenClaw. Inside the installer package - accessible to anyone who downloaded it - was a private SSL certificate key for the domain *.myclaw.360.cn. An SSL private key is essentially the master password to a website's encrypted connection. With it, an attacker can impersonate 360's servers, silently intercept user traffic, forge a login page that looks completely legitimate, or possibly take over the AI agent altogether. The cert is valid until April 2027 and covers every subdomain on the platform. It's now public. The founder launched the product with a promise it would "never leak passwords". It did that during release? 461 million users, a $10B valuation, and nobody checked the zip file before shipping. The cert expires April 2027.
Last weekend marked the 5th year in a row that @ARosenmund and I have presented a workshop at DefCon!
Our DC33 Workshop is entitled "Putting EDRs in Their Place: Killing and Silencing EDR Agents Like an Adversary." Not only do we have step-by-step instructions on GitHub, but our PluralSight Labs environment will be up and available for free for a while. Weeks, months even!
If you're interested in learning about how to EDR killers and silencing methods work, check out the workshop!
https://t.co/68HSDwsSTO
🦜⚓️ New to the village? Come aboard!
Get the lay of the land at MHV: unmanned craft, port systems, crane controls, and real cyber-physical gear. No other @DEFCON village goes this deep into the deep.
🏴☠️ Get briefed. Get oriented. Get hacking.
🕒 10:00 | MHV Booth (W2-504) Workshop Area
#DEFCON33 #MaritimeHackingVillage #OTsecurity
With DEFCON 33 fast approaching, the Rare Circuits team is excited to finally unveil our 2025 SAO in collaboration with @SecureAerospace Village!
* Receiving and listening to Air-Band VHF audio
* Jamming out to FM radio, in *stereo*!
* …and more @defcon
@defcon crew!!! Under 150 hours! FIND US at DefCon and hack a real STS/ship-to-shore crane control system donated by our partners at @yuseninc and rigged up by @portoflongbeach. AND we have our very own magic box (container challenge) on the other side of it. SEE WHAT'S INSIDE!!! #DEFCON #DC33 #DEFCONVillages @DC_BHV@ICS_Village
Mcafee refund scam going around
Number used (863) 393-7965
@_JohnHammond@ScammerPayback
Made me discover this site https://t.co/mXUtVyUHA1 which is very cool 🤙🏻
Some thoughts on edge devices, especially after reading Rapid7’s write-up on Ivanti:
1. The more features these boxes have, the more attack surface they expose.
2. A locked-down OS and restricted shell make compromise assessment nearly impossible.
3. Foreign actors have the time and resources to reverse-engineer patches and identify bugs that were fixed without realizing their full impact — like in this case, where a minor bug turned out to be an RCE.
4. When a 0-day was exploited in the wild, patching is not enough. Vendors must publish IOCs.
5. If IOCs are missing, that’s not “responsible disclosure” — it’s hiding evidence from defenders.
A patch doesn’t undo a compromise. Everyone needs to be clear about that.
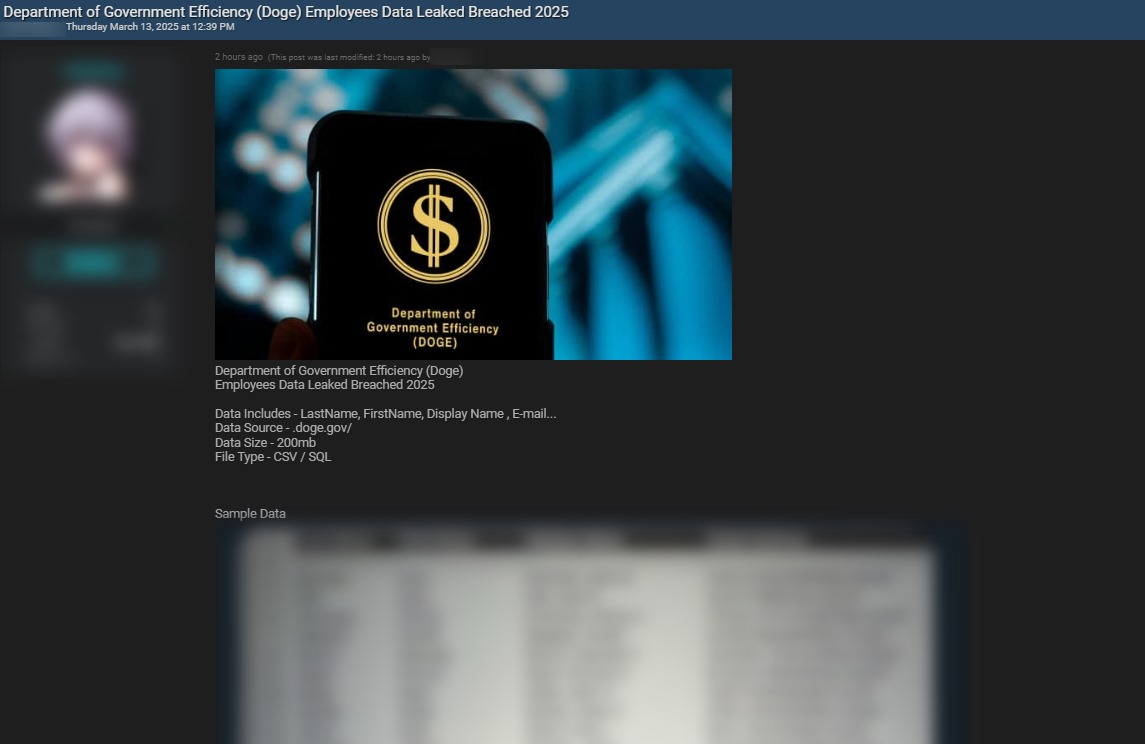
🚨 Data Breach Alert: Department of Government Efficiency (DOGE) 🇺🇸
📢 A member of BreachForums has posted about a significant data breach involving Department of Government Efficiency (DOGE), USA.
The compromised data reportedly includes 200 MB of information containing first names, last names, display names, email addresses, and other details.
EXCLUSIVE: Defense Secretary Pete Hegseth last week ordered U.S. Cyber Command to stand down from all planning against Russia, including offensive digital actions.
https://t.co/fsFQzOt17y
@CactusCon 🌵#cacuscon2025
it's really a cool badge, but I can't wait for the update looping issue to get resolved. would be cool to if we could change the wifi ap too. 🙏