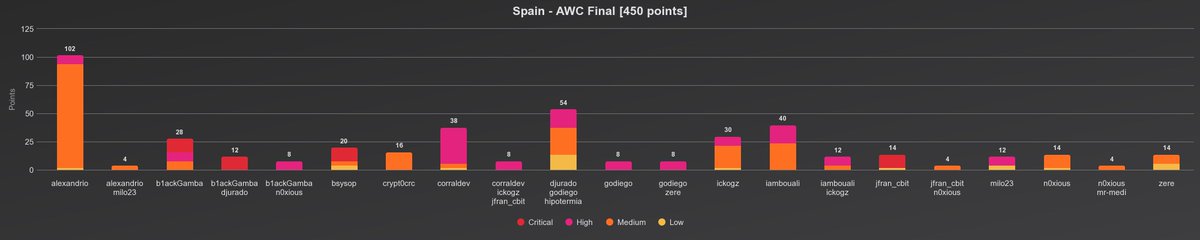
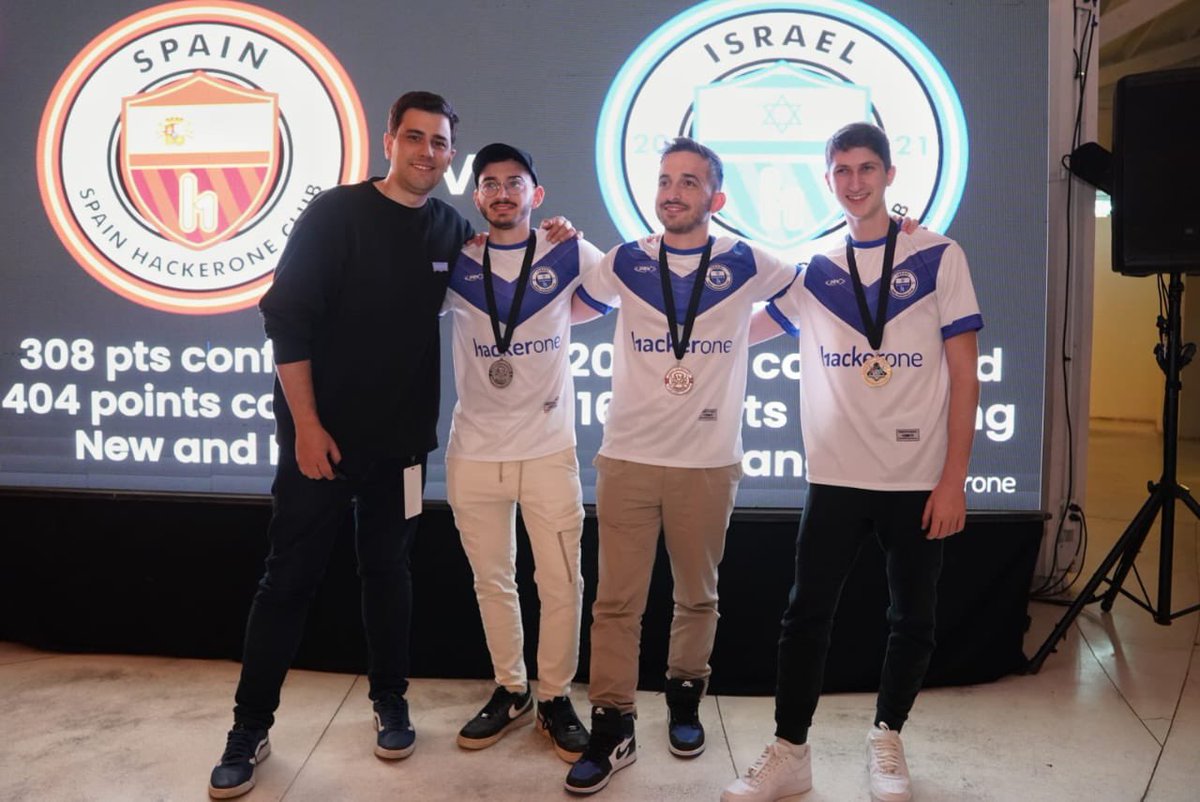
We won the HackerOne Ambassador World Cup for the second year in a row! 🇪🇸🏆
Thanks to every member of the team, none of this would have been possible without them.
Thrilled to release my latest research on Apache HTTP Server, revealing several architectural issues! https://t.co/7ygwWXY0pd
Highlights include:
⚡ Escaping from DocumentRoot to System Root
⚡ Bypassing built-in ACL/Auth with just a '?'
⚡ Turning XSS into RCE with legacy code from 1996
🔥 XSS on any website with missing charset information? 😳
Attackers may leverage the ISO-2022-JP character encoding to inject arbitrary JavaScript code into a website. Read more in our latest blog post:
https://t.co/Ji3V0fK5b6
#appsec#security#vulnerability
As someone involved in the AWS offsec space, I want to share why I strongly do NOT recommend the HackTricks AWS Red Team Expert course. The author of it is a plagiarist, stealing content from other creators and is directly profiting off of it through sponsorships. A 🧵
Dear Fell(owl)ship, we are experiencing a miracle. Two posts in our blog in the same month! This time @TheXC3LL's homily is about a product he pwned last xmas.
A christmas tale: pwning GTB Central Console (CVE-2024-22107 & CVE-2024-22108)
https://t.co/YNvEU8tg9a
There's still a load of potential for further research and discoveries in HTTP request smuggling. This massive-impact finding from @deadvolvo exploiting Akamai/F5 is a great example:
https://t.co/YHkP4fHoo8
Team Israel 🇮🇱 finished 2nd on @Hacker0x01’s 2023 Ambassador World-cup beating 🇮🇳🇺🇸🇹🇷🇸🇬🇫🇷 along the way!
Circumstances were tough but we gave a proper fight - kudos to the team for all the hard work, looking forward to the next one and for better times ahead 🙏
#BugBounty
Vamos ESPAÑA! 🇪🇸
Much love to everyone in the team participating, especially those that were virtual and well played to Israel, they put up a very good fight!
And the winner is #TeamSpain!! 🇪🇸Congratulations to every hacker and team who participated in the #ambassadorworldcup this year! Your committment to #hackforgood inspires us to keep the HackerOne mission going. Way to go!!
Just popped another crazy XSS. Check this one out 👀
So a CRLF was passed to me by a podcast listener. The CRLF was in the path, so it couldn't contain a /.
We could do response splitting, but couldnt change the content-type to text/html because we couldn't use a /.
So we...
A detailed two part video showing how we found a DNS parsing vulnerability and wrote a remote root exploit for it🤌
Part 1: Finding the vulnerability via "fuzzing" and reverse engineering with Ghidra 👾
https://t.co/08ghgyiphS
Part 2: Understanding vulnerability constraints and work around them to build a surprisingly complex exploit 💣
https://t.co/F3o4JTEkGP
This was an excellent find: https://t.co/Ndl4trxCbq
I love the logic flaw found within the nginx rules leadigng to the auth bypass needed to get to the RCE.
A $1,000,000 bounty?
How @kucoincom leaked user information via a simple vulnerability
And why you shouldn't hack on @HackenProof.
https://t.co/aczH4Oeqki