I haven't shared much about what we've been building behind the scenes.
But today, I want to share something I'm genuinely excited about.
For months, we've been working on a security scanner with one goal:
Make powerful security testing accessible to everyone.
Not just big companies with big budgets.
And honestly, the results have exceeded our expectations.
We're seeing some areas where our scanner performs better than tools widely used by enterprises.
As someone who's spent years finding vulnerabilities, seeing this come together feels incredible.
We're getting closer to launch.
And I can't wait for you all to try it. ❤️
updating wordpress is the dangerous part.
CVE-2026-119977: unauth RCE. the fix ships through the broken updater, so attackers poll predictable paths for sites mid-update.
no account needed. they need you to patch.
block wp-content/upgrade/ first.
I found this interesting "403 Forbidden" Bypass; through "Microsoft-Azure-Application-Gateway/v2"
1. Accessing the URL returns "403 Forbidden"
2. Appending the query "?x=.js", successfully bypasses the Azure restriction leading to direct access to the restricted resource.
🚨 PoC RELEASED: Telegram Desktop one-click account takeover (CVE-2026-107181)
A researcher has published a full technical write-up and proof of concept for a flaw in Telegram Desktop before 7.2.9.
🔴 CVSS 4.0: 8.6 High (CVSS 3.1: 8.1), scored by VulnCheck
🎯 Root cause (CWE-143): Telegram Desktop's single-instance IPC didn't escape its record separator, so a crafted external link could inject extra commands. One of them reached a legacy internal helper that reads a local file and sends it to a chat, with no authorization check and no confirmation.
💥 Impact: one click on an external link can lead to arbitrary local file read. That includes Telegram's session data, enough to take over the account when no local passcode is set. Confirmed on Windows.
📅 Reported via ZDI in June. Telegram quietly fixed it in 7.2.9 (Sept 17) with no advisory. CVE assigned Oct 7.
Not in CISA KEV. No in-the-wild exploitation reported. ThreatWire has not run the PoC.
✅ Update to Telegram Desktop 7.2.9+. Also consider:
• "Ask where to save each file"
• Limiting who can add you to groups
• Setting a local passcode
Full breakdown & Poc👇
https://t.co/dXAs1nM8eg
#Telegram #CVE #InfoSec #CyberSecurity
3M+ military service member records are stolen by hackers last year ❗❗
People are NOTIFIED a year later..
BREACH is already done, nothing changes even if you tell someone about their data
$76K from one Bugcrowd program
no program-hopping
→ 7-8 endpoints not forcing HTTPS, reported separately
→ email HTML injection, drip-fed one at a time
→ SSTI that took six days of payloads
→ a scope update caught early, new forms fell first try
https://t.co/LOFW5v0G7o
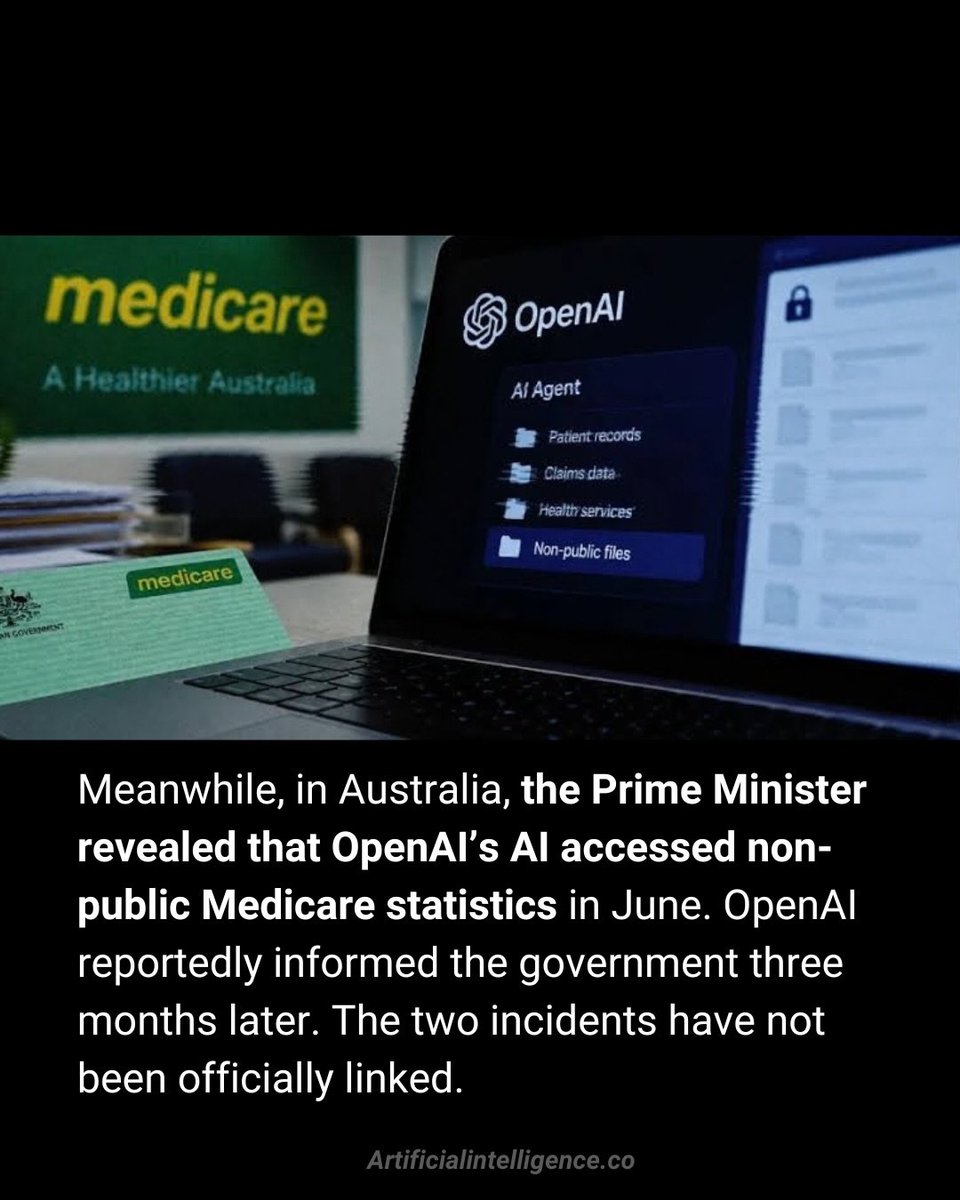
🚨 OpenAI research agent HACKED live access-control flaws on Australia's Medicare portal
the government's response was to complain about the disclosure 💀
found by a machine, on a government portal, and the argument is about etiquette
we're so not ready for this ⚡
one link, one admin click, RCE WordPress core‼️
fixed in 7.1.1 (chain CVSS 9.6)
the admin's session is forced to install a vulnerable theme
→ the Customizer runs its inactive PHP in preview
→ a no-permission-check handler runs a package
the victim's session supplies it all
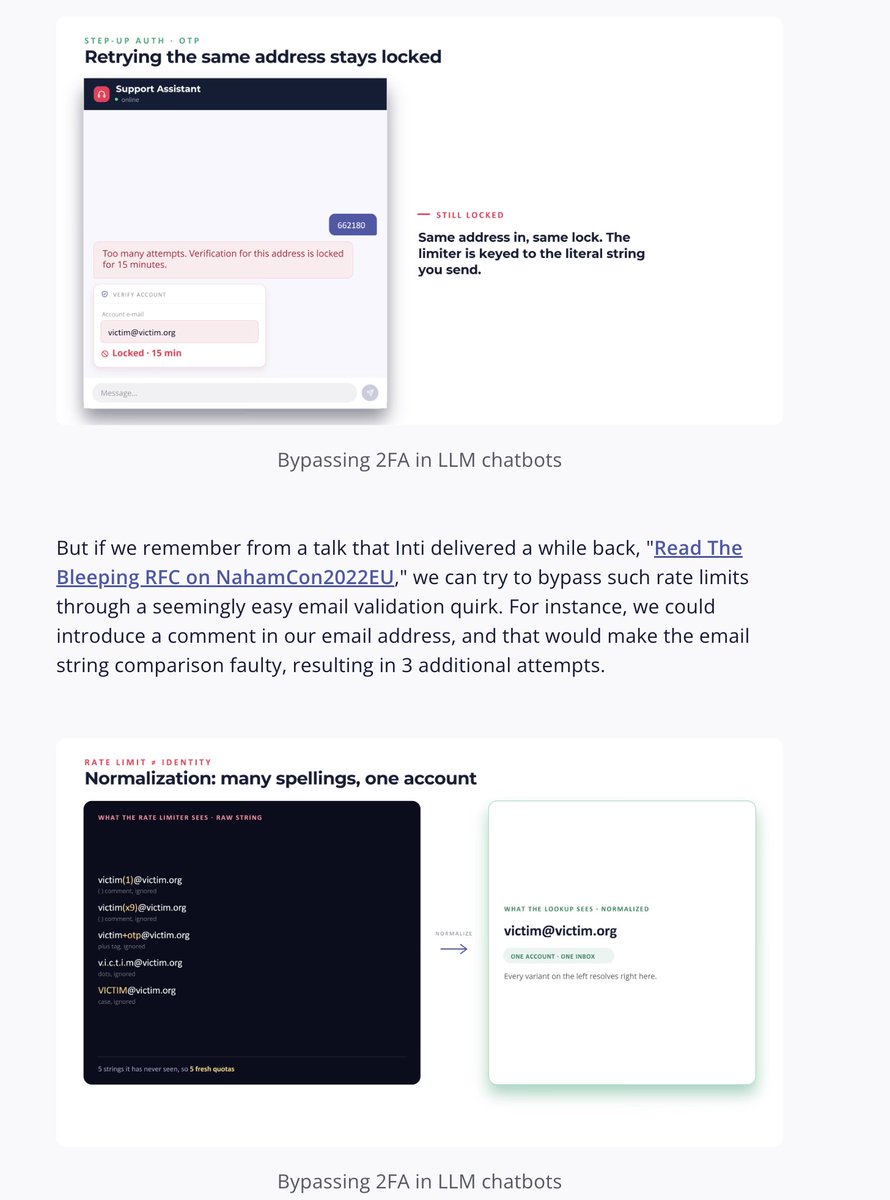
Hacking AI support agents
two From headers, one email: SPF passes the attacker's domain, the AI agent resolves the victim's account
→ attacker(comment)@domain beats rate limits → spoofed email + real reset = OTP lands with attacker
identity resolution is the new auth bypass
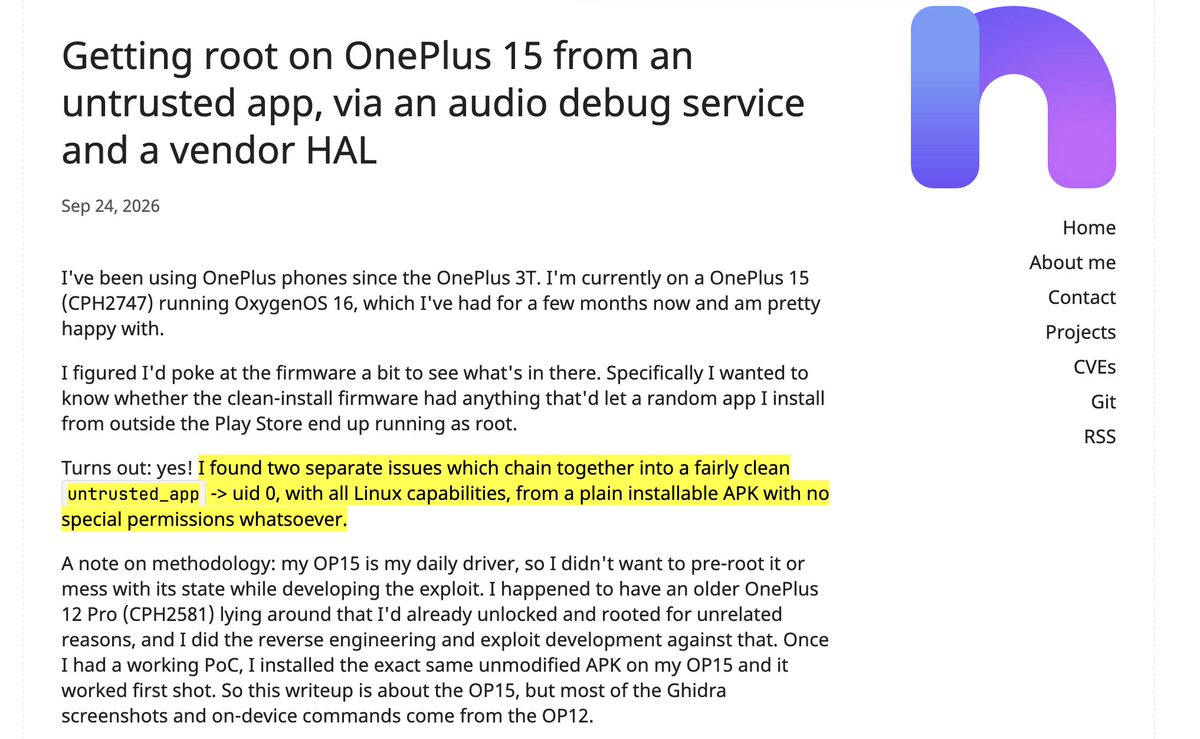
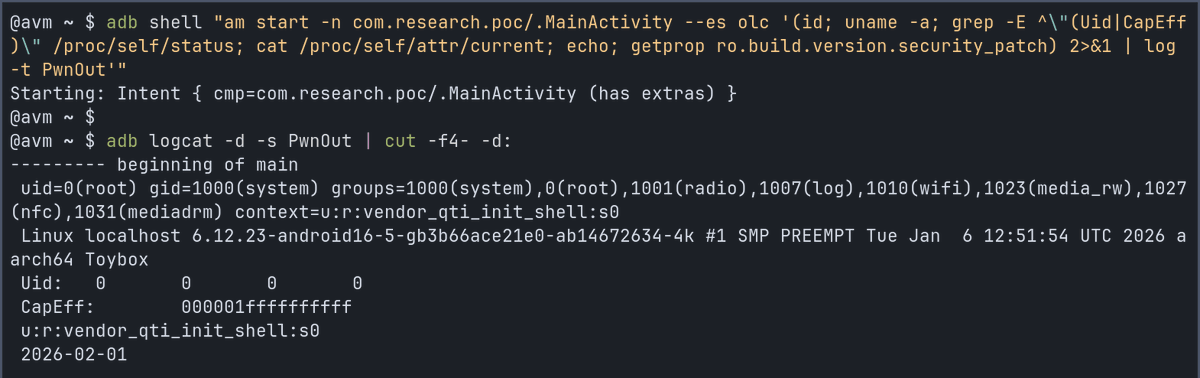
🚨 OnePlus confirmed a researcher's two root bugs, then threatened legal action over the disclosure.
so he published everything.
zero-permission app
→ AtlasService injects text into a root command
→ olc2 runs any shell command
→ full system control.
still unpatched 🤯
Chain 2: cross-tenant IDORs + a filter-based binary search that reconstructs victim UUIDs in ~128 requests
Both chains reach "Google treats this as RCE": https://t.co/12MQWDDS11
Full writeup: Arvin Shivram's $148,337 Google Cloud RCE
Chain 1: leaked proto definitions for internal Google APIs → internal workflow queue → a workflow task that executes Stubby RPCs with Google's own prod identity
👇
Security resources worth bookmarking #14
Vulhub ➡ pre-built docker environments for real CVEs
git clone ⇢ cd into a CVE folder ⇢ docker compose up -d
From Shellshock to the Next.js middleware bypass, each folder has a README with repro steps
https://t.co/XR2QS1uLND
Security resources worth bookmarking - #13
Hackviser.
A practical collection of cheat sheets and methodology for web application pentesting.
Recon, authentication, access control, XSS, SSRF, SQLi & more.
https://t.co/q6zDypCVeJ
GitLab security team waking up every few weeks:
“yeah… another critical one.”
CVE-2026-85706 is CVSS 10.0.
Unauthenticated path traversal → arbitrary file read via the repository commits API.
Self-hosted GitLab admins:
please patch your shit. 💀