Further enhance phishing investigations with @MISPProject playbooks! 'URL Remediation' streamlines finding abuse contacts via AbuseFinder, @lookyloo_app , @FIRSTdotOrg , and RDAP, while reporting malicious sites to MSRC, Google Safe Browsing and Netcraft. https://t.co/MvPKpI524Z
SkillAegis version 1.2.0 released
SkillAegis is a platform to design, run, and monitor exercise scenarios, enhancing skills in applications like MISP.
https://t.co/NVveh97hRh
#threatintel#training#cybersecurity#opensource
MISP 2.4.200 and 2.5.2 released - Post https://t.co/zqk97AAaLz release with many new features.
New feature such as Ad-Hoc Workflows, Private Custom Galaxies, Tags on Event Report, new features in event report & improved PDF export.
https://t.co/F9klUMJZSz
#ThreatIntel#cti
MISP 2.4.195 released with new features and performance boosts!
Introducing correlation rule systems to reduce data noise, enhanced OpenAPI specs for seamless integrations, and major search API improvements for faster queries.
https://t.co/Jtn7CyxDh8
#ThreatIntel#opensource
The MISP galaxy evolved into a complete set of knowledge base freely accessible to many projects including MISP. At the EU ATT&CK community workshop, we presented the recommendations for models creator:
Slides: https://t.co/XoaZ4K04JZ
#threatintelligence@cvandeplas@adulau
MISP - Elastic Stack - Docker
This lab explains how to connect MISP to the Elastic Stack in order to leverage IOCs from MISP and trigger alerts based on user defined rules.
https://t.co/Wj3PxJM77L
@elastic#elastic#misp#opensource#threatintel
We transformed the MISP modules into a standalone project featuring a unique user interface. Now, it's easier to utilise all the expansion modules for enhanced open-source intelligence, threat intelligence efforts and keep a track of all your pivoting.
https://t.co/zyESo9xXQ9
A @MISPProject tip of the week: When you set a 'Remote MISP server' as internal instance it transfers local tags when syncing events. Set 'https://t.co/OQA6n4mM4E_org_id' and check 'Internal instance'. Ideal for organisations running multiple MISPs. https://t.co/yrc0Dz3YNS
“Sharing Communities: The Good, the Bad, and the Ugly.” Interesting paper to understand working methods, goals, benefits, and challenges of sharing communities. #cti https://t.co/AFSEkRMEmy
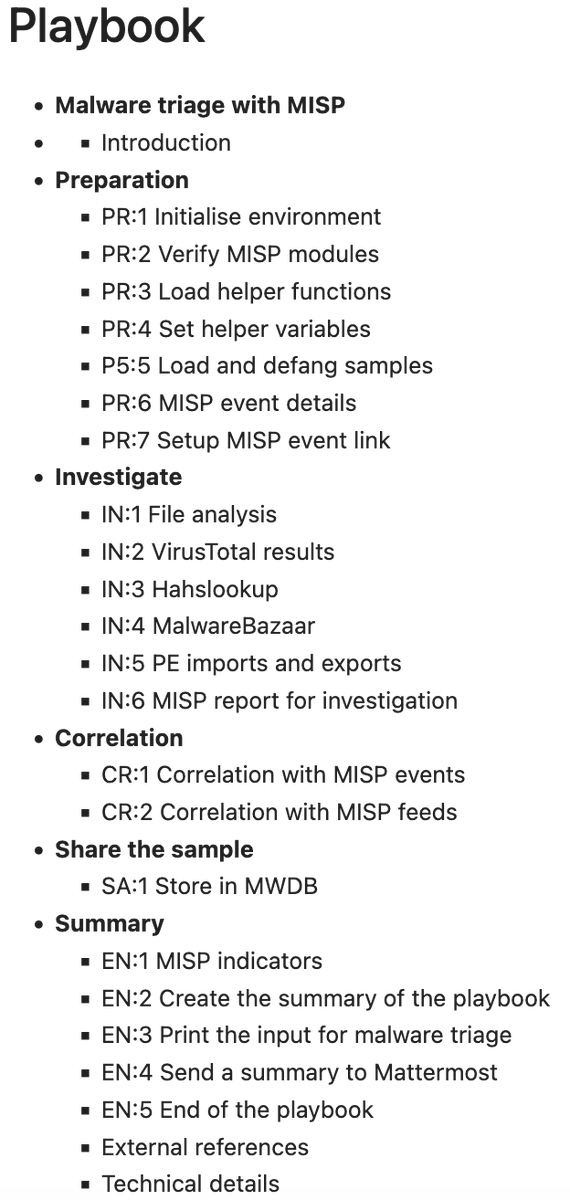
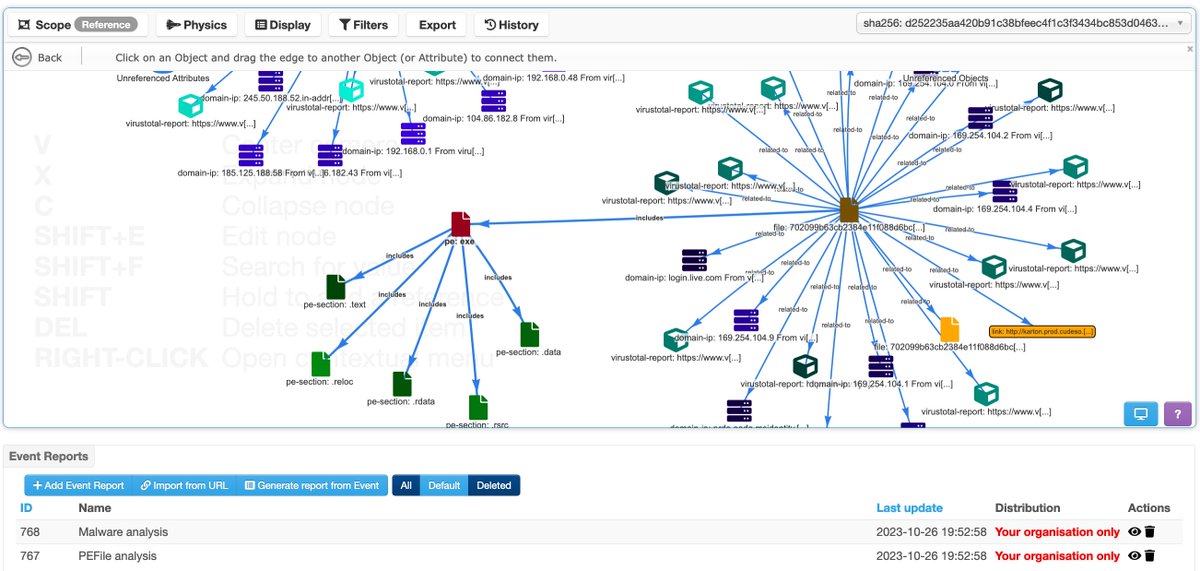
I shared the @MISPProject playbook for malware triage that I regularly use for a first assessment on new samples. It uses MISP, @virustotal , MalwareBazaar, Hashlookup and pefile, uploads to MWDB and alerts to Mattermost. #csirt#ir#dfir https://t.co/tgOmnJtsZ4
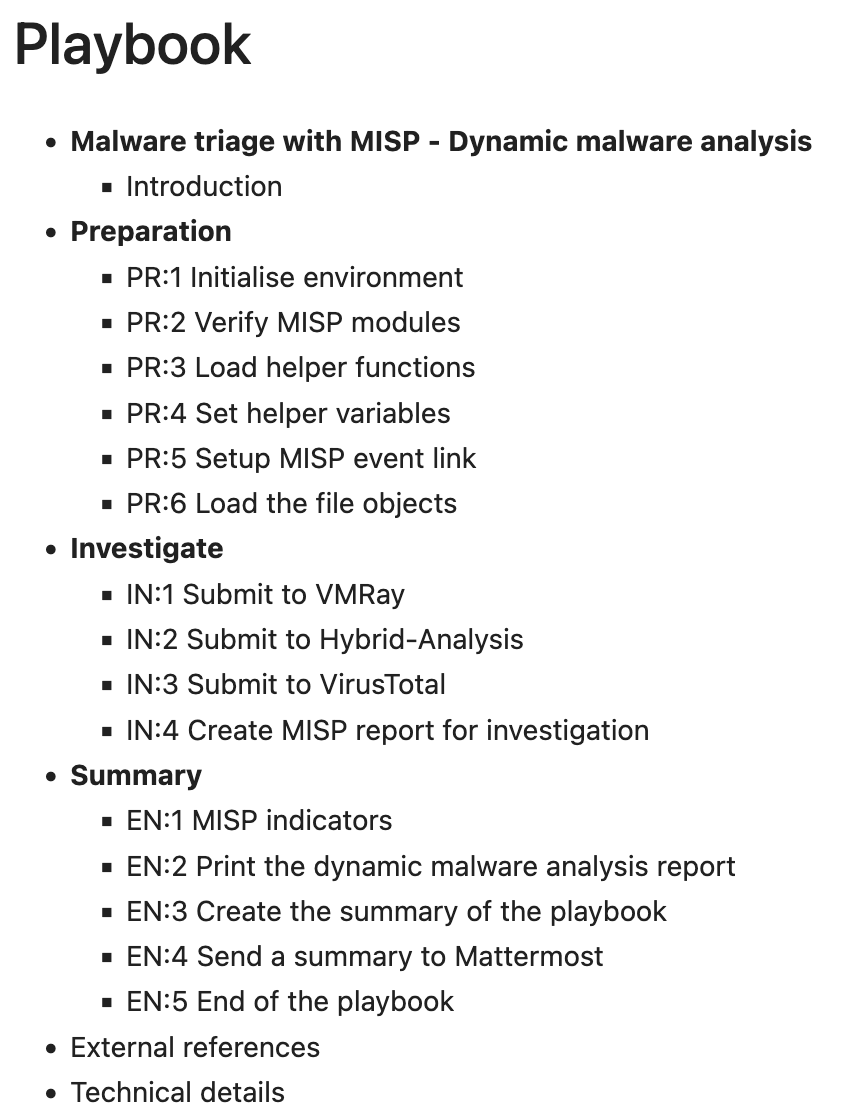
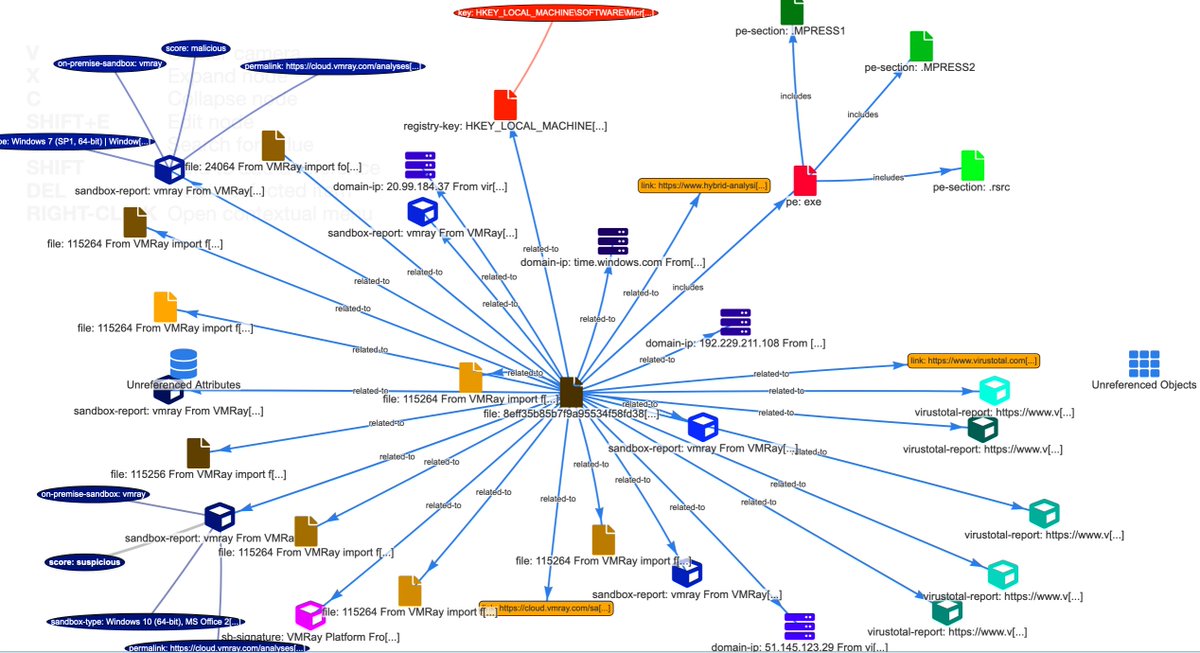
If you liked the previous @MISPProject playbook for static malware analysis then you're certainly going to like this one. This playbook extends the results with dynamic malware analysis by the sandboxes from @vmray , @HybridAnalysis and @virustotal https://t.co/MKvVB0nNbn
Over recent months, the MISP project has undergone significant enhancements and advancements. These developments extend beyond software, encompassing enrichments in the community-managed MISP standard base (galaxy, objects).
#ThreatIntelligence
https://t.co/pSqysyCnPq
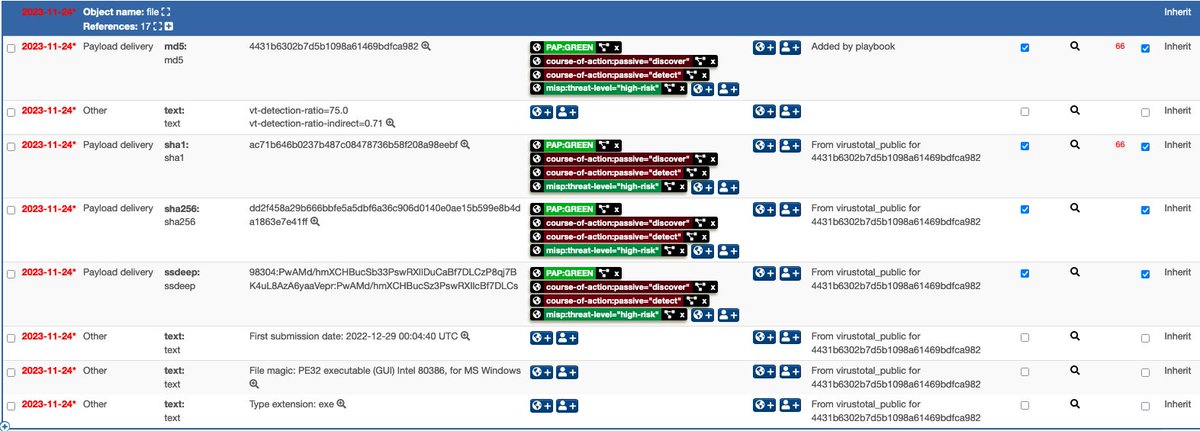
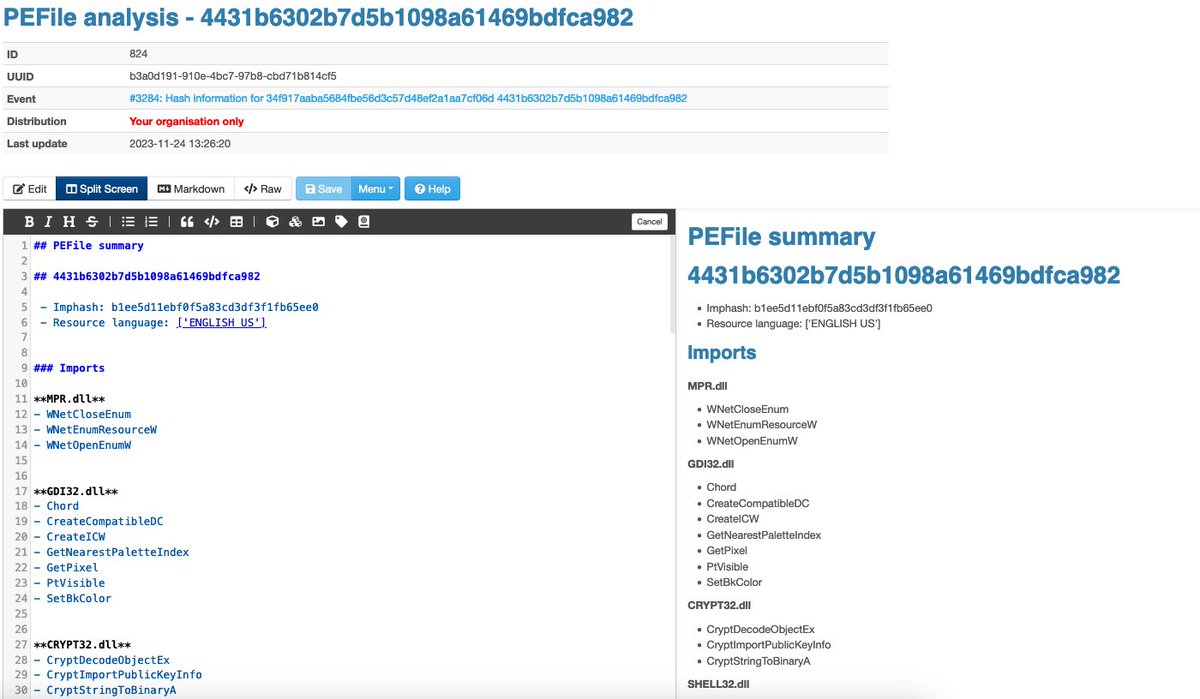
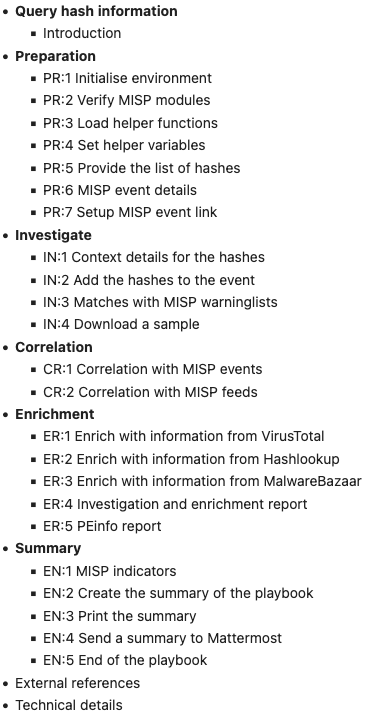
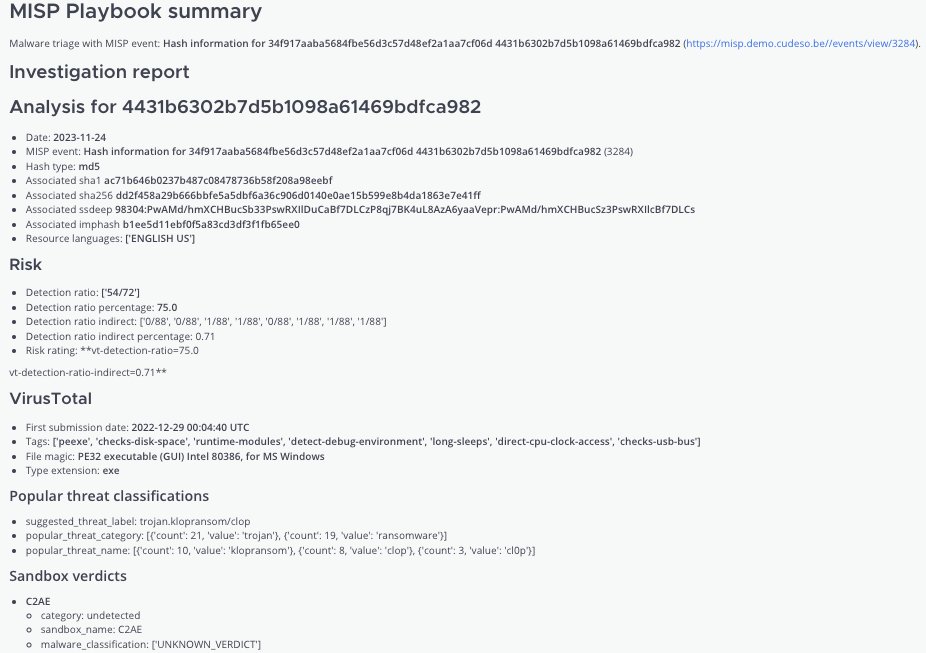
Concluding the series of @MISPProject playbooks for malware analysis, "Query hash information" helps discovering which malware is associated with a hash. You get a MISP report on the hash investigation, peinfo details and a summary is sent to Mattermost. https://t.co/MkOShnl3px
misp-wireshark v1.1 released including support for tshark.
misp-wireshark is a Lua plugin intended to help analysts extract data from Wireshark and convert it into the MISP Core format
#opensource#dfir#misp@WiresharkNews#wireshark#threatintel
https://t.co/LQdQkS3mZ4