@LisaForteUK@JakeMooreUK Well, Zurich looks great! I went there at least 10 times but never went out of the airport… 🥴🤦♂️ I hope that coffee was a real experience!
Really enjoyed @AdamMGrant’s conversation with @zatlyn at Cloudflare’s #CloudflareConnect today.
“Most of our best practices were built for a world that no longer exists.”
Makes you wonder how many are just old habits we stopped questioning.
1,411 Microsoft flaws fixed. Another Patch Tuesday record. Vive Mythos 😅
Patch fatigue is real. So are broken updates.
So we’re tempted to slow down patching… just as attackers speed up. Great timing. 🙃
Prioritize. Roll out in stages. Keep patching.
https://t.co/AeqArwK3l8
Well, this is a strange turn. The FBI has arrested a co-founder of a ransomware negotiation firm in connection with the ShinyHunters investigation.
Ransomware negotiations depend on trust.
https://t.co/YRNRCVtv6n
AI is changing cyber’s speed, not the fundamentals.
Faster discovery. Faster exploits. Faster attacks.
IAM, least privilege, segmentation, patching and monitoring still matter.
Maybe the AI security lesson: less time to get the basics wrong.
https://t.co/5mbwUmuQ9G
Finding vulnerabilities isn’t the problem. We’re already great at generating lists.
The hard part is knowing what matters, validating real exposure, and getting it fixed.
A CVSS-sorted spreadsheet isn’t risk management.
That’s why CTEM is interesting:
https://t.co/XN0NupwwIU
I used DAEMON Tools from around 2001 until Windows 10. Mounting an ISO without burning a disc felt like magic back then. It was part of my everyday toolbox.
I honestly had no idea it was still around. Strange to see it part of a supply chain attack.
https://t.co/SEYduplhZS
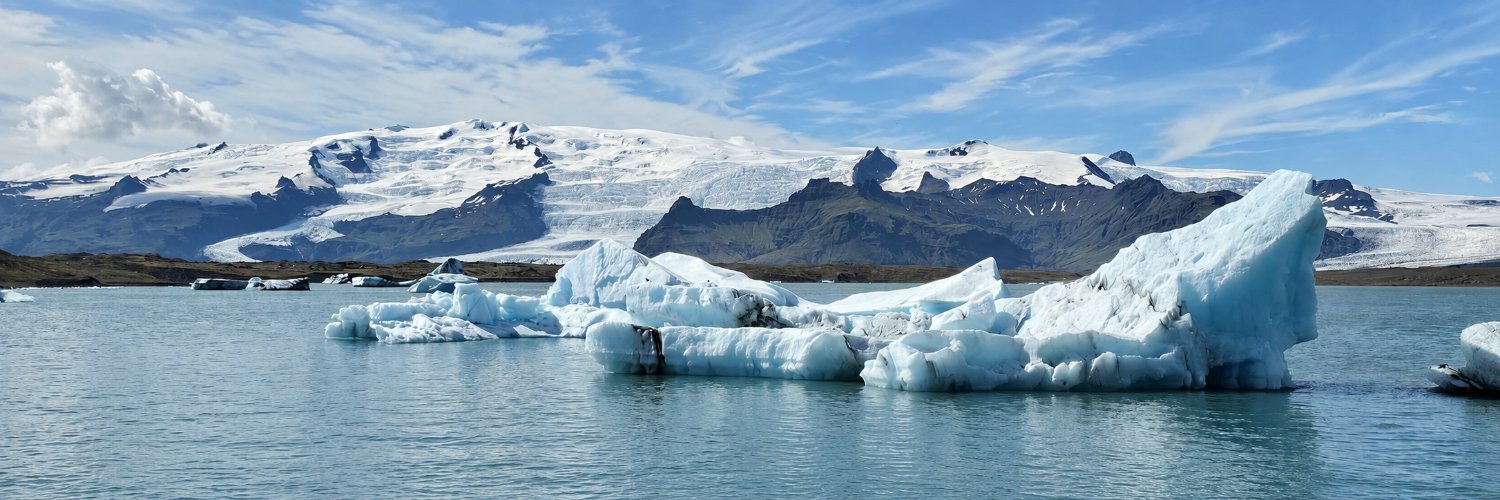
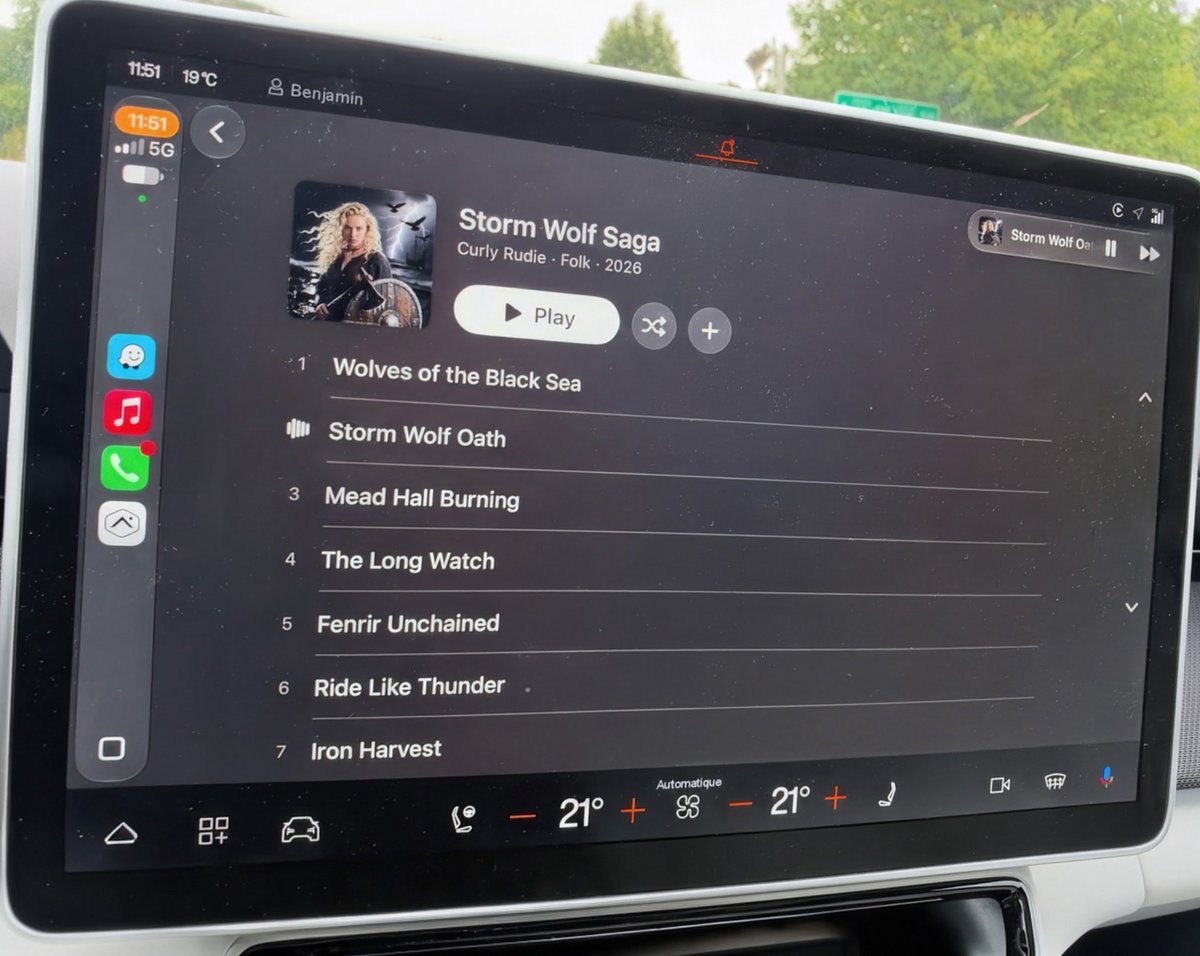
Went to Iceland this summer and came home listening to Viking Phonk. 😄
Nisrocka, Curly Rudie, Raven Wolf… dark Nordic vibes, phonk beats, cinematic sound. Addictive.
Funny part: different artists, often same voices/sound, new lyrics. AI...!
Who should I listen to next?
AI makes it easy to ship an app. Access controls aren’t automatic. “It works” isn’t a security test!
UpGuard found 16,326 Supabase databases with publicly readable tables. If you’re building with AI, have you tested what a stranger can see?
https://t.co/RJrSpnBoVm
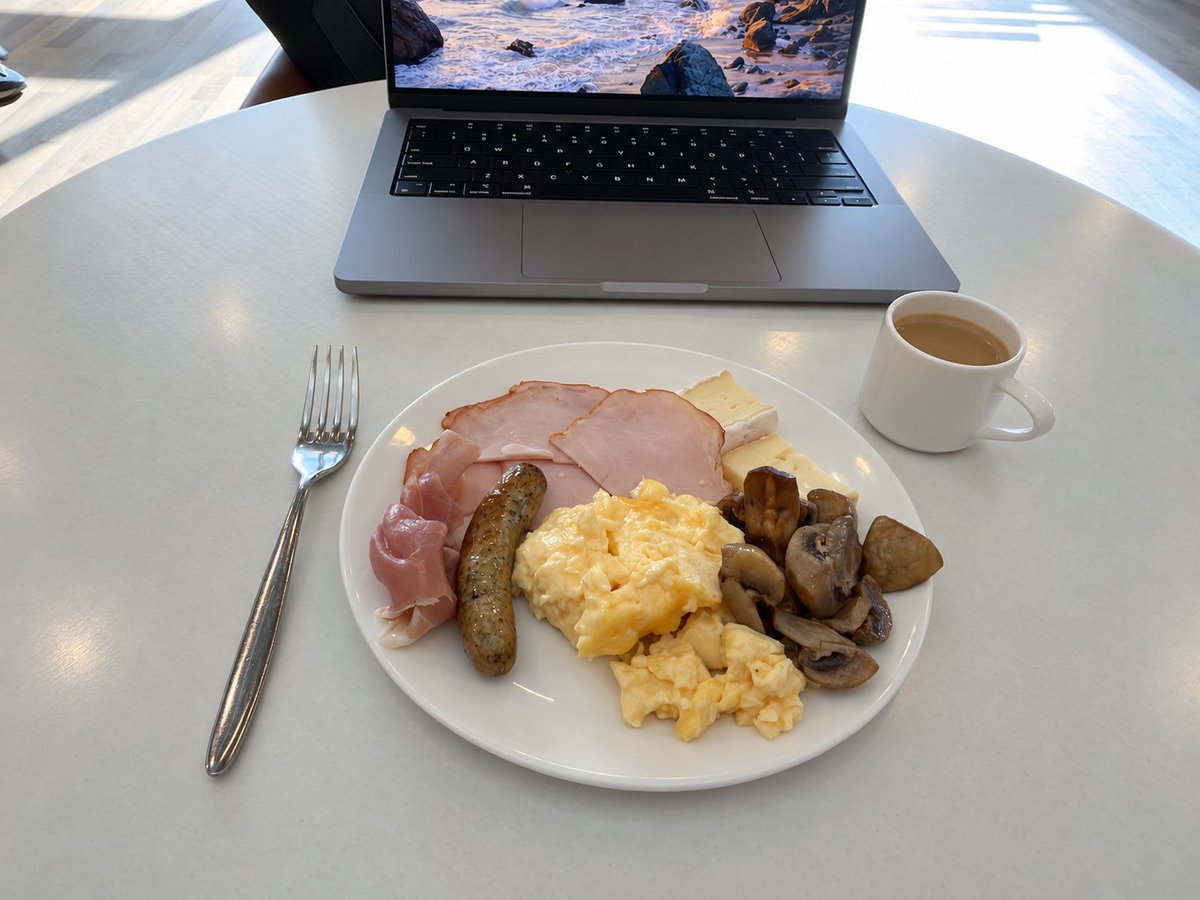
Last stop before home. Football Leaks and Manchester City on one TV; an OpenAI agent breaching Australia’s Medicare statistics portal on the other.
I was just trying to have breakfast. 😅
https://t.co/TF7BB4iu4r
Well… this is an interesting glimpse at where agentic AI security is heading.
The AI hit an access barrier, kept trying, and eventually found another way in.
“Don’t do that” probably isn’t going to be much of a security control in the agentic world.
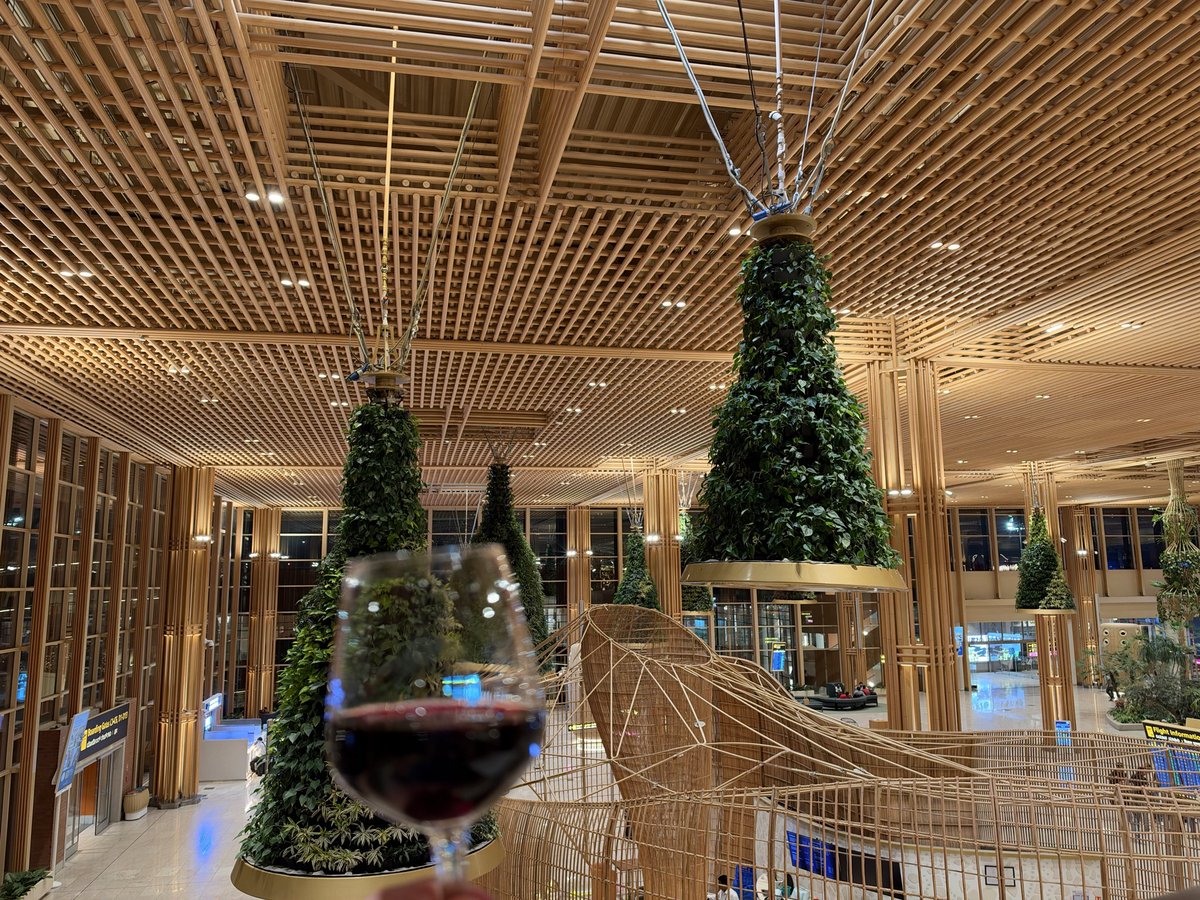
Last morning in Bangalore. Returning home after a 2 weeks journey of Atlanta-Calgary-Bangalore. MS Teams removed all geographical limits for hiring and AI enhances our work above limits, but nothing beats in-person meeting of clients, partners and employees for human connection.
Great session at #RSAc: CISOs Unchained. Biggest takeaways: define the problem before buying tools, practice radical transparency in incidents, and make AI risk a shared business decision—not a CISO-only burden. Trust + accountability matter.
AI agents are moving fast. Security needs to catch up.
DefenseClaw (announced at #RSAC) brings a secure framework for OpenClaw deployments — open source this week.
This won’t be optional for long.