We just received a $250,000 Chrome Full Chain bonus! 🎉
We've claimed the second Full Chain bonus of 2026. Only two remain!
Under the rules, every vulnerability had to be a non-duplicate 0-day, and the entire exploit chain had to be completed before any of them were patched.
Huge thanks to @nebusecurity for discovering a V8 vulnerability in just a single day! Also, a big thank you to @_deayzl for collaborating with me on the V8 Heap Sandbox research.
P.S. KVM escapes have been getting a lot of attention. I actually captured the Full VM Escape flag in KVMCTF about three months ago. Hopefully, I'll be able to share that research soon, too!
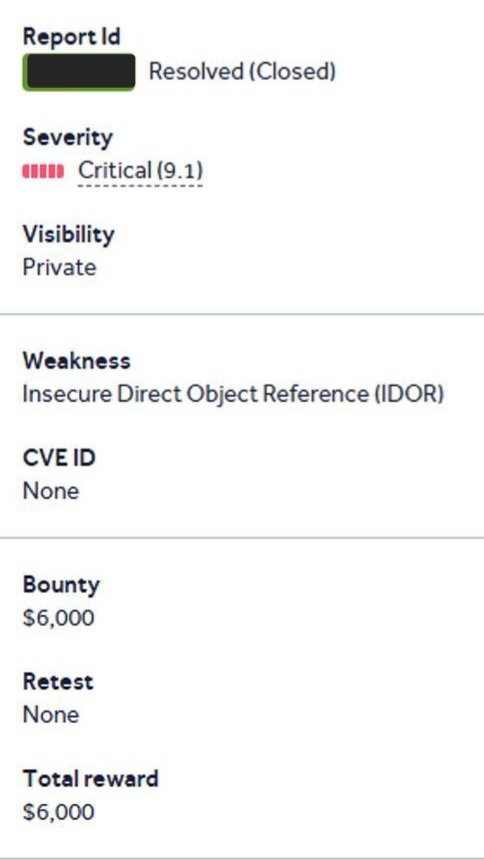
Opus 4.6 found an IDOR with low impact and said it wasn't worth reporting since, with the victim's email, it could only change their first name. But I was able to combine it with Mass Assignment and an inconsistency between two parts of the app to escalate it to a zero-click ATO.
$6,000 Mozilla VPN Clients: RCE via file write and path traversal 🤯💥
👨💻 Rein Daelman (x/ReinDaelman)
🔗 https://t.co/3A19wTRnZh
🔗 https://t.co/cADA5DUdp5
XSS using "xss.pdf" 👀
I’ve seen a lot of people successfully find XSS by uploading a malicious PDF that gets rendered inside a PDF viewer.
But there’s another angle people often miss: data exfiltration doesn’t always require JavaScript execution.
Depending on how the PDF viewer handles interactive PDF features, an attacker may be able to trick users into submitting sensitive information through a malicious prompt or form.
I put together the PDF PoC here:
https://t.co/9MgYEL0tE1
For more technical details on portable data exfiltration:
https://t.co/UlhWc07N8J
Only test this on systems you own or have explicit authorization to assess.
#bugbounty #bugbountytips
$10,000 Google Bug Bounty: AppSheet RCE
BugTraceAI found deserialization RCE in AppSheet automation. Malicious .NET payload → PowerShell execution on Google's backend.
🔗 https://t.co/XiBqxr8dLi
---
More writeups like this? 👇
🔗 Want to perfect?👉https://t.co/pJWHoCMDix
OAuth Bypass Testbed
https://t.co/8WHf78YqCz
Test your skills against a LOGIN (randomly vulnerable) and/or 17 AUTHENTICATION SERVER endpoints.
Like with JWT, a fully automated OAuth tool with complete FFF (Find, Forge, Fire) PoCs is on the way, exclusively for Brute One.