@briantashman You don’t like the idea they may find something? Why wouldn’t that be news? You and you anonymous sources are not journalists but hit men. This is why nobody trusts legacy media. If the fact stand in your way, your kind bury it or distract or become indignant at the accusations.
JESSE ARM: "6,600 noncitizens made it onto the [New Jersey] voter rolls. That, to me, is widespread voter fraud."
ABBY PHILLIP: "That's widespread?!"
ARM: "Yeah."
PHILLIP: "Where's the proof that it's widespread?"
ARM: "6,600 noncitizens on the voter rolls..."
PHILLIP: "That is .006% of registered voters in the state. Is it widespread, or is it something that is relatively rare?"
JENNINGS: "You're pounding him over the word widespread. I just would ask you, what is your tolerance for any fraud at all?"
PHILLIP: "Is it widespread?"
JENNINGS: "Absolutely. Over 6,000 people."
PHILLIP: "What is your bar for widespread?"
JENNINGS: "My bar is I want NO tolerance. I have ZERO tolerance for this."
PHILLIP: "What is your tolerance for American citizens whose valid voter registrations are invalidated by incorrect databases? What's your tolerance for that?"
JENNINGS: "I don't have tolerance for ANY mistakes in the electoral system, including putting noncitizens on the rolls."
Dive into the latest episode of Distilling Cyber Policy! @alexbotting and Jen Ellis chat with John Banghart and @bitwatcher about the National Vulnerability Database. Tune in to learn about the NVD's history, challenges, and future: https://t.co/9I3Vp2IJ8E
Now is a pivotal time for the NIST Cybersecurity Framework. Share your feedback on our 2.0 draft version by Nov. 4: https://t.co/UK1Qc6Y9aT
#CybersecurityAwarenessMonth
“Diversity leads to better #cybersecurity outcomes, and better cybersecurity outcomes lead to better business outcomes," says @corybullock. #Diversity in the cyber #workforce is more than a moral imperative, it’s key to biz continuity. #CyberNextDC
Cybersecurity Framework 2.0 Draft just released. Public Comment open until November 4, 2023! Participate and help shape the future of cyber risk management.
https://t.co/Kjw8Ixdi9j
If you are not staying current with what is occurring in the wild, you are at a disadvantage. Take a few minutes with the June 2023 Trellix CyberThreat Report. Great insights! https://t.co/Oc0MXW6bjc
NIST in 2022 “also celebrated 50 years of work in the cybersecurity space and [the National Cybersecurity Center of Excellence] celebrated a 10-year anniversary since inception.” @NISTcyber
Head of Threat Intelligence @John_Fokker shares our observations on cybercriminal behavior from over a year virtually staked out in the Genesis Marketplace — these insights ultimately assisted law enforcement in the market’s takedown. Hear more. https://t.co/dh2rqYzYjl
From the official swearing in, to discussing today’s most pressing national security issues, it was an honor to visit the White House last week for the May 2023 NSTAC member meeting.
While investigating vulns in the ICS & SCADA space, we uncovered 2 CVEs in Triangle MicroWorks’ SCADA Data Gateway — CVE-2023-2186 & CVE-2023-2187. @CGMcFarland shares insights from the manufacturing industry threat landscape exemplified by this discovery. https://t.co/sV0iCrX47c
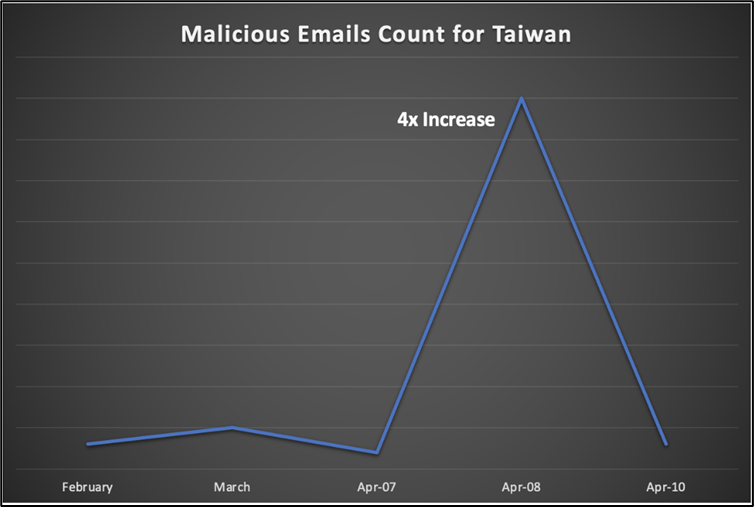
For several months, we saw increased cyberattacks against Taiwanese organizations. In April 2023, we observed a surge over the course of four days — 4x the average at its peak.
Researchers Daksh Kapur and @LeandroNVelasco explain our findings on the blog. https://t.co/G6msUq6S8K
As always, @John_Fokker does a fantastic job explaining the “what” and “why” behind a cyber threat. Read his explanation of the global rise in hacktivism in @secinfowatch. https://t.co/S2ypJqsoyI
Curious about the Genesis Market takedown? The @TrellixARC blog collaboration between @John_Fokker, @l3cr0f, and myself provides a complete overview, along with an analysis of the used malware: https://t.co/5wSoxX52Ta
Really enjoyed the in-person NIST Cybersecurity Framework Workshop last week. Great discussions on how to improve the CSF. Afterwards, discussed impressions with Inside Cybersecurity.
https://t.co/f1dH5CAnfh