Blokiments is entering a new chapter.
Over the last few years, we built tools for crypto users to filter new tokens, analyze launches, track wallets, and detect scam signals. That work gave us a deep understanding of how risky on-chain activity actually looks in practice.
Today, we’re officially shifting Blokiments toward what has become most valuable: crypto investigations, due diligence, and custom blockchain intelligence.
The new site is now live and reflects that transition.
What this means:
- a new landing page focused on investigations, due diligence, and custom data work
- a growing set of practical tools
- more public research, guides, and investigation workflows
- a stronger focus on helping funds, investigators, legal teams, and builders turn on-chain activity into usable answers
If you need help with wallet tracing, token reviews, suspicious flow analysis, or custom blockchain data workflows, take a look.
More updates soon.
New Blokiments tool: Wallet Risk Analyzer.
Paste an EVM wallet and get a structured view of its identity, activity, counterparties, and risk signals.
It checks:
• wallet & entity labels
• multichain activity
• sanctions & official watchlists
• stablecoin issuer restrictions
• exploit associations
• privacy protocol interactions
• scam / malicious-address signals
• on-chain behavioral patterns.
The report combines these signals into an AI-assisted risk assessment while showing the underlying evidence and coverage.
More networks and intelligence sources are coming.
➡️ Try it: https://t.co/xcCu6uW2P9
@osint_based Based on the fund flows, it looks more like the whale is using a mixer for privacy. Most of the funds were withdrawn from Tornado Cash to this wallet: 0x3e38f44bc521f05f739ceb7d5e938ee989a5651d.
BITGET EXPLOIT
There are reports of a major security incident involving Bitget, with estimated losses exceeding $170 million.
Several wallets that currently appear to hold or have received funds linked to the incident:
- 0xa6dd3f218b65e32ccc37be30f74884133c655545
- 0xA6dD3F218B65E32Ccc37BE30f74884133c655545
- 0xd2c2f029eff5cacc686f24377cfddcfc82d9f899
- 0x600cfedc6bd65fa79b604dc44964f419e45784b2
- 0x770b10b273fc44fe9197d6bf20f145c2e98463ee
We are continuing to trace the movement of the funds and will publish a more detailed investigation as additional information becomes available.
UPDATE: After the exploit, the funds were swapped for approximately 940,000 BSC-USD. Then, 40,000 USD was deposited to Binance. The remaining stolen funds were moved to four wallets via the Across Bridge:
~400,000 USD to Ethereum: 0x0e4052edf0a35ecddf2998db21a331a4ebede799
~300,000 USD to Base: 0xbbb248f74bd4671768926586f2f3a46bc2b72d1f
101,000 USD to Robinhood Chain: 0x1397c6115ff92574df231933201aba7ed9f89295
100,000 USD to BSC: 0xb714ebf48060c9b15e3e39ebd3944cc14291c5bf
EXPLOIT: MOKE Spot-Price and Stale LP Accounting Exploit
Network: BNB Smart Chain (BSC)
Exploit timestamp: 2026-08-02 20:50:11.000
Amount lost: 907,700 USD
Project: Moke
Attacker: https://t.co/dW01OHXNdS
TxHash: https://t.co/aPbhx1DrZq
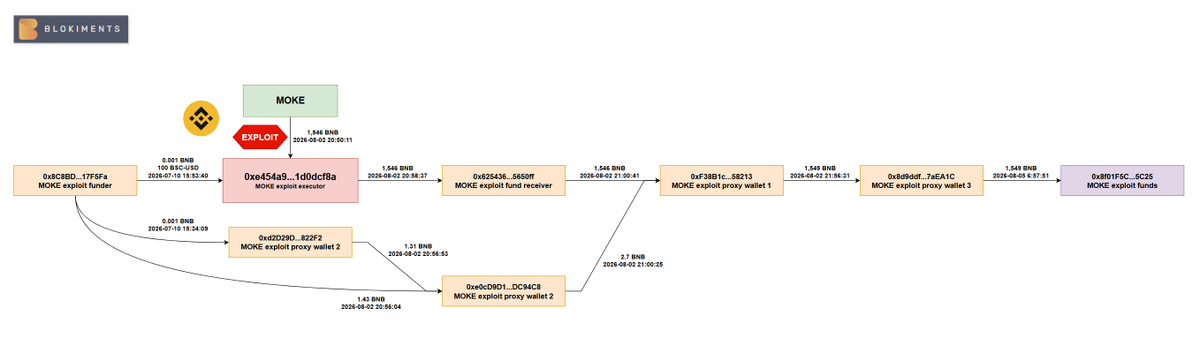
Summary: An attacker manipulated MOKE's same-transaction spot-price settlement and exploited stale LP dividend records to release tens of millions of MOKE, convert them into BNB, and realize approximately $907.7K.
Sources:
- https://t.co/d8Iz2PCzkW
- https://t.co/mdJs3Pe7II
TRACING the funds:
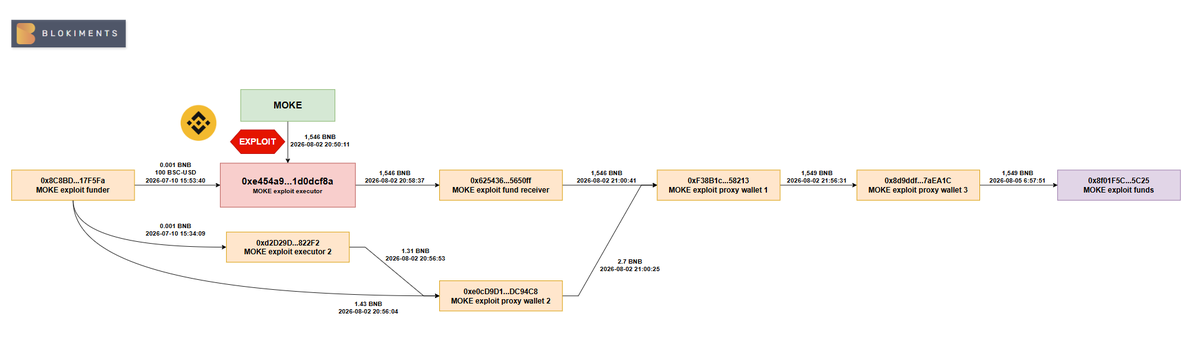
The MOKE exploiter funds were transferred to 0x6254365dD2E179055AFE9E68e90D0EAb305650ff.
The malicious actor then made two additional PancakeSwap swaps and transferred the funds through:
- 0xF38B1cab69C7DDDF11DBb17b7EbcE8098DF58213 and 0x8d9ddf0ab2e3e3Ff450aac7773dEEBc27c7aEA1C.
On 2026-08-05, the stolen funds were transferred to 0x8f01F5C9827909Ab819cD6622588eBa2c1445C25.
The funds are still currently held in this wallet. The attacker has started converting the BNB to Binance-Peg BSC-USD. @binance
For now, the funds remain in this wallet. We will continue to monitor and update on any future movements.
🚨TenArmor Security Alert🚨
Our system has detected a suspicious attack involving #MOKE on #BSC, resulting in an approximately loss of $907.7K.
Attack transaction: https://t.co/6fxhdOtkEn
With TenArmor’s TenMonitor, you get early detection and automated response to on-chain attacks.
Need protection? Reach out anytime!
#TenArmorAlert #TenArmor
0x784aab4a45505c256f258845ad41b47671dbd8e68f3cdf461396b0f70b79d594 -> funding from https://t.co/Xgaz1Qcv8C
TXhash for Deposits to https://t.co/vU6QyIDIdH:
0xefba951de4891031c1429e8ad0d68239773fe476cb98ed533799ec42315047a7
0x67535e38e735810023fbe01f66eaae5414c40180c1171d1fe222c3feb9be8314
0x87f5ed4d05667dbbd920fb4530a586bf3c2d9c9e83e5a7f1b043817988b21034
0x1020cf1a34e4b395d7da469197ec81d82326d6373bf388fd9ec4257034b6a87d
NEW EXPLOIT: USM/FUM Split Redemption Pricing Exploit
Network: Ethereum
Exploit timestamp: 2026-08-09 8:12:47
Amount lost: 136,123 USD
Project: USM Stablecoin
Attacker: https://t.co/cWU6yJVZIj
TxHash: https://t.co/G4NP2W06jL
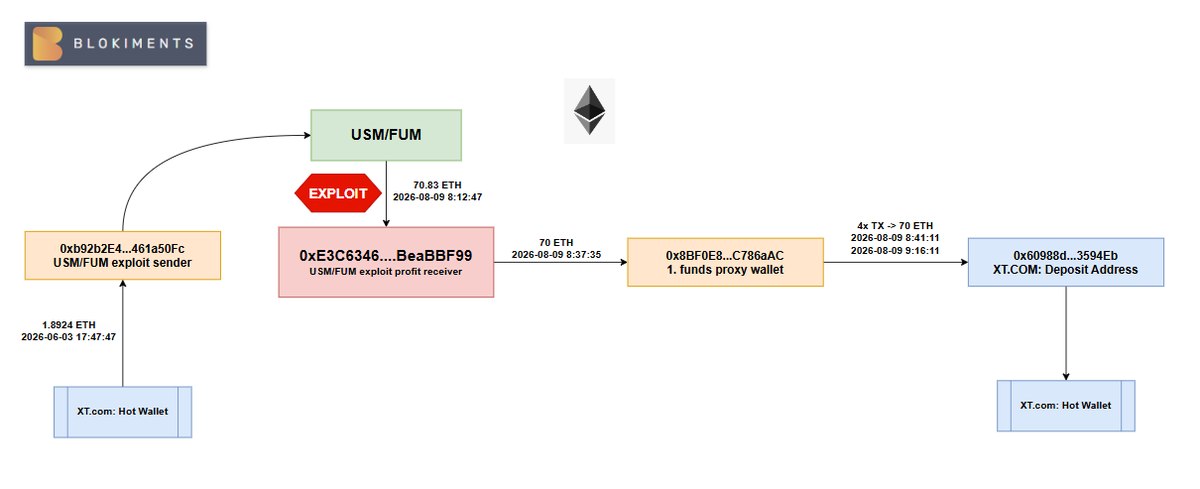
Summary: An attacker exploited path-dependent pricing between USM's fund() and defund() functions by flash-funding the ETH pool and splitting the resulting FUM redemption across 64 calls, extracting approximately 70.83 ETH.
Sources:
- https://t.co/a3LMRGNahe
-https://t.co/EOJOkfmHrV
TRACING THE FUNDS:
The 70.83 ETH from the USM exploit was sent to 0xE3C6346b6F282029312d2CAf4677EF39BeaBBF99.
After the exploit, 70 ETH of the stolen funds were transferred to 0x8BF0E85c2655D4b6051024a7c47B20190C786aAC.
This wallet then made four deposit transactions to the https://t.co/Xgaz1Qcv8C exchange deposit wallet 0x60988d3B4D3DfFe2C9A5277945968E61993594Eb. @XTexchange
The exploiter wallet 0xb92b2E47680c89DA8f951B8963ef469f461a50Fc also received ETH funds from the same https://t.co/Xgaz1Qcv8C exchange.
🚨 @usmfum - Loss $136K (2026-08-09)
Token: $FUM / $USM
Network: Ethereum
Type: Oracle / Price Manipulation (Flash Loan)
Attacker flash-loaned 11,580 WETH from Balancer and repeatedly called USM.defund() (65 iterations) to burn its ~62M FUM position against the ETH pool. Each defund tweaks the internal bidAskAdjustment / sliding price (USM.sol _defundFum, ls.bidAskAdjustment.wadMulDown), and chunking the exit inflated the effective FUM sell price far above the oracle mark (PriceChanged pushed to ~$7.1M vs oracle ~$1,921), letting each burn drain more ETH than fair value. The extracted ETH was re-wrapped to repay the loan, netting ~70.83 ETH profit drained from the USM ETH pool.
TX: https://t.co/gg5duRj0RO
Attacker: https://t.co/WRrrr6i1qe
Victim: https://t.co/5l1v8Z66pW
⏱️ Real-time alerts: https://t.co/X9cKWDVOJz
NEW EXPLOIT: https://t.co/UlfZhiUtlF Spot Price Manipulation Exploit
Network: Arbitrum
Exploit timestamp: 2026-08-07 04:18:12.000
Amount lost: 29,984 USD
Project: Atomic (@atomic__green)
Attacker: https://t.co/ns6xxWJJXl
TxHash: https://t.co/hRqkvh0Sqg
Summary: An attacker replayed an insufficiently scoped manager signature across 21 https://t.co/UlfZhiUtlF position IDs, enabling unauthorized full LP burns. Flash-loan manipulation of the underlying spot price amplified the withdrawals, resulting in approximately 29,984 USDC in losses.
TRACING THE FUNDS:
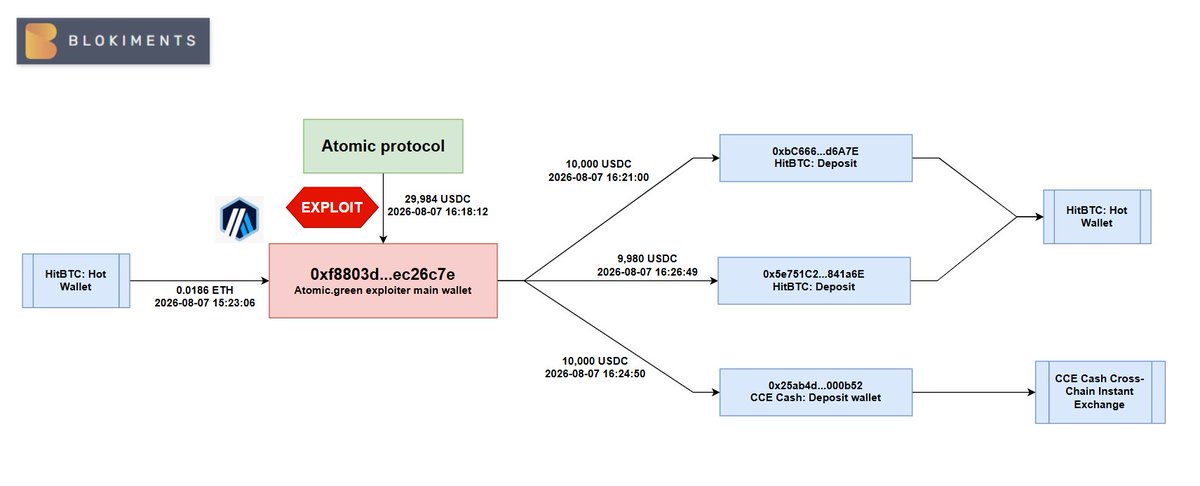
The attacker, 0xf8803dae13a6757e53711214769b5fb52ec26c7e, sent 19,980 USDC to two @hitbtc deposit wallets, while another 10,000 USDC was transferred to a @Cce_Cash Cross-Chain Instant Exchange deposit wallet.
The attacker was also funded with 0.0186 ETH from the HitBTC exchange an hour before the exploit.
@SlowMist_Team@atomic__green The attacker, 0xf8803dae13a6757e53711214769b5fb52ec26c7e, sent 19,980 USDC to two HitBTC
deposit wallets, while another 10,000 USDC was transferred to a CCE Cash
Cross-Chain Instant Exchange deposit wallet.
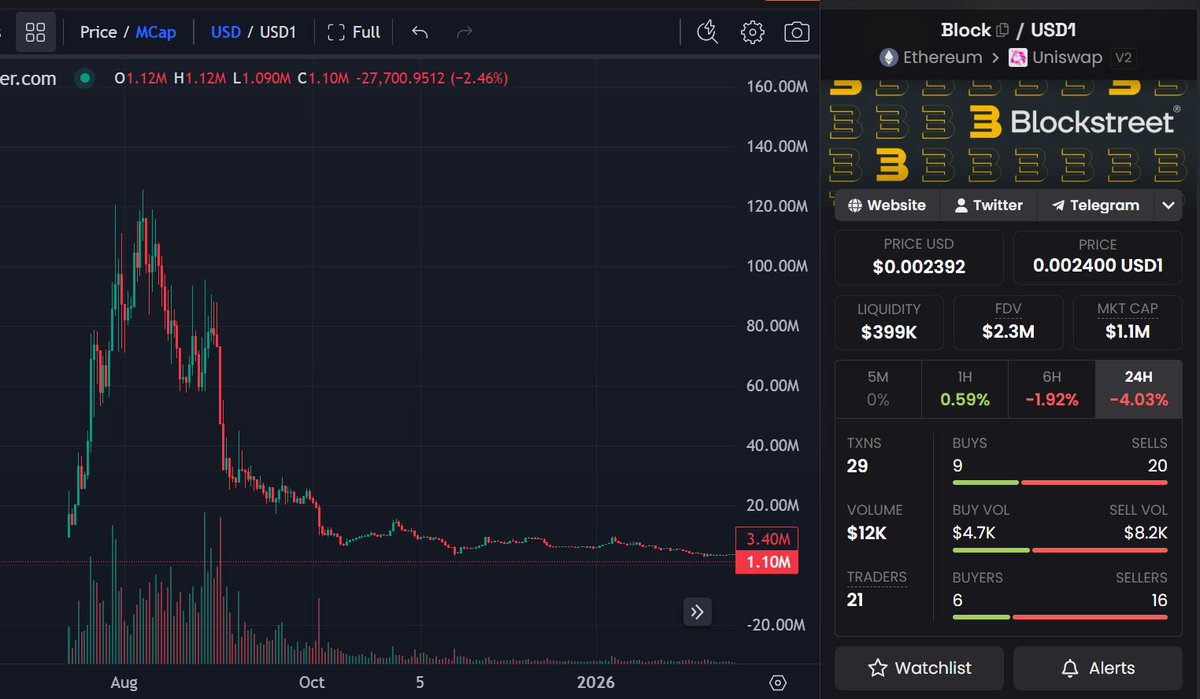
We investigated Blockstreet, the ethereum:0xcab84bc21f9092167fcfe0ea60f5ce053ab39a1e token, its links to MIXIE, the team, and the on-chain flows.
Our findings point to coordinated trading, major profit extraction, and serious questions about insider activity.
Read the full report: https://t.co/PUyLiNsxvp
@taziqx_@AiFiCorp Oh wow, I see it now. We took the screenshot and checked the page a few days ago, and he was still there. Do you know when the change happened?
We investigated Blockstreet, the ethereum:0xcab84bc21f9092167fcfe0ea60f5ce053ab39a1e token, its links to MIXIE, the team, and the on-chain flows.
Our findings point to coordinated trading, major profit extraction, and serious questions about insider activity.
Read the full report: https://t.co/PUyLiNsxvp