⚠️There is a massive bias I see in InfoSec I must highlight:
The Uninnovative Attacker Hypothesis
You think you are protected because attacker capabilities are driven by skill instead of tooling. That you can do something, and stop. It’s proven wrong. Here’s why. With proof. 🧵
JA4 is now in GA on @Cloudflare! Use it for bot prevention, security analytics, and WAF rules.
If you would like to see the rest of JA4+ on Cloudflare, submit a feature request! The more they get, the higher it will move up on their backlog.
https://t.co/q6AGz47MVS
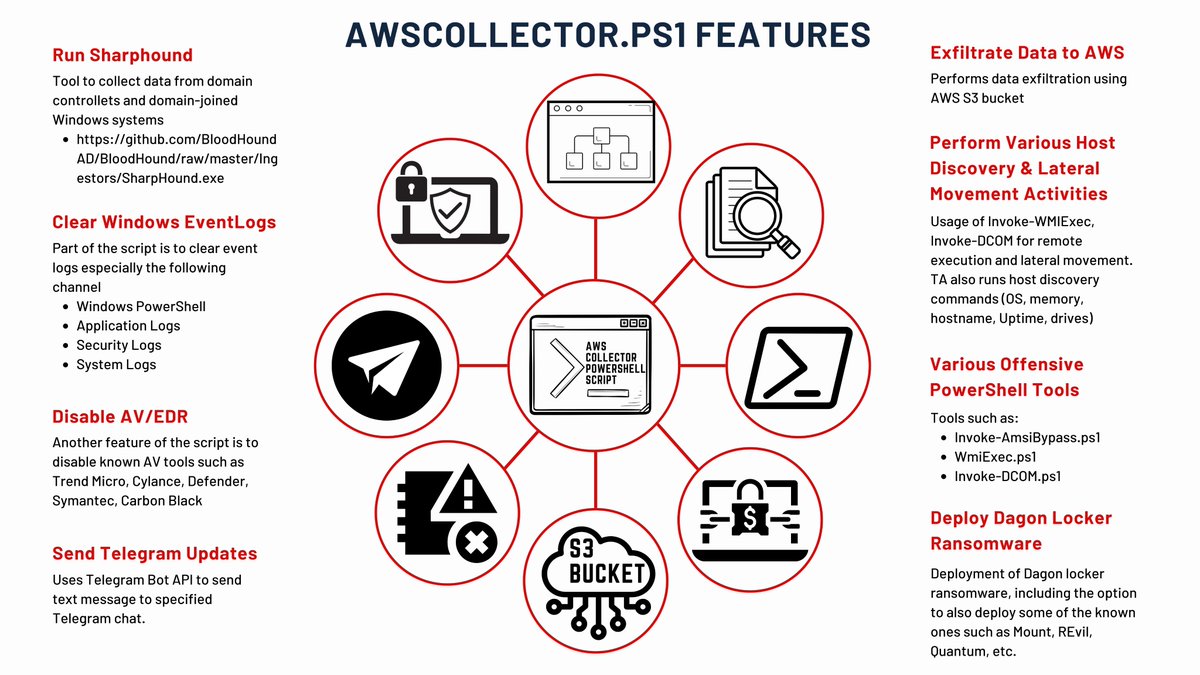
I had the opportunity to co-author this blog. This case started from IcedID to Cobalt Strike to deploying Dagon Locker RW. This case had a TTR (time to ransomware) of 29 days. It's a long report with lots of graphics. Hope you like it @TheDFIRReport#DFIR
https://t.co/hZTUmnrYOz
Our team at @Volexity has identified a new 0day exploited in the wild. This time we caught a threat actor using an unauthenticated RCE in Palo Alto Networks GlobalProtect. It has been assigned CVE-2024-3400 and is covered in this @PaloAltoNtwks advisory https://t.co/JZIOPnavnX
The xz backdoor was the final part of a campaign that spanned two years of operations. These operations were predominantly HUMINT style agent operations. There was an approach that lasted months before the Jia Tan persona was well positioned to be given a trusted role.
How do we demonstrate the value of cyber threat intelligence in the corporate world? In the latest episode of Unspoken Security with @AJNIntel, Freddy Murre dives into the challenge of adapting military intelligence expertise to the finance sector. https://t.co/MrU613HJh5
ICYMI: @Europol released their Cybercrime Training Competency Framework — and we’re taking notes for #FOR589#Cybercrime#Intelligence
— The Competency Matrix is broken down between roles, skill-sets, and skill levels
Read the 10-page paper here:
https://t.co/I8hdNcGHcY
In this blog post:
● My analysis of the Midnight Blizzard breach affecting Microsoft
● Step-by-step explanation of the attack path the adversary took
● Practical, free steps ANY Azure admin can take to protect themselves
https://t.co/2YbcvyK9el
Hewlett Packard Enterprise (HPE) disclosed today that suspected Russian hackers known as Midnight Blizzard gained access to the company's Microsoft Office 365 email environment to steal data from its cybersecurity team and other departments.
https://t.co/VJQKtA12Xr
🚨Active Exploitation🚨
➡️CVE-2023-22527 - Confluence template injection
➡️Executed whoami
➡️Source IP: 45.61.137[.]90
➡️UA: Opera/9.89.(Windows 95; sv-FI) Presto/2.9.181 Version/12.00
➡️PCAP, full POST URI and more available in our AllIntel service https://t.co/RXnF6Mx8fB
I tweeted recently about how an attacker used a misconfiguration in ADCS (Active Directory Certificate Services) to gain Domain Admin rights within the network.
@JimSycurity made me aware of Locksmith [1]: A small tool built to detect and fix common misconfigurations in Active Directory Certificate Services.
Locksmith will find common issues and attack paths, and for many of them, give you cmdlets you can run to resolve the issues yourself, or you can allow Locksmith to make fixes for you.
@NaderZaveri from Mandiant informed me of the "Modern Attack Paths, Mitigations, and Hardening" guide, detailing the various attack paths against ADCS and how to mitigate them.
So folks, check out Locksmith and the guide from Mandiant to secure your ADCS environment.
Good luck ☘️
[1] https://t.co/daQobA91Hx
[2] https://t.co/gVB4AFmbco
@AlexVanopslagh Virkelig dårlig dag for LA. Har stemt på LA siden i blev stiftet, men må indrømme at det nu nok bliver sidste gang med hende på holdet med det politiske menneskesyn.