Today is the release of our 2025-26 Annual Cyber Threat Report. This report confirms that technology is evolving at rapid rates and has raised the stakes for cyber security. Read about the top cyber security threats to Australia in the new report 👉 https://t.co/36dySegVL7…
The company temporarily stopped trading, said it had fixed the issue, and promised to reimburse affected users. Trading later resumed. In its public statement, Polymarket said an outside provider had been compromised and that the matter had been referred to law enforcement.
#cybe
Polymarket Hacked - Users Reported Funds Stolen From Their Wallets
Details: https://t.co/FB9nstuTdI
Polymarket suffered a security incident on October 29, 2026, after a compromised third-party provider exposed users of its international platform to wallet theft. Traders reported missing funds, unexpected withdrawals, and positions being closed without permission.
The company temporarily stopped trading, said it had fixed the issue, and promised to reimburse affected users. Trading later resumed. In its public statement, Polymarket said an outside provider had been compromised and that the matter had been referred to law enforcement.
Although early descriptions pointed to an authentication provider, current reporting connects this incident to DebugBear.
#cybersecurityNews
Remember when scam callers only ask for your password? Good times.
Now picking up a wrong call can get you hacked.
Telegram RCE discovered by NebuSec Code Security, powered by GPT-5.4.
Yes, GPT-5.4. We turned a dinosaur model into a cyber powerhouse.
Fixed in Telegram Android 12.10.4(7099)
Today is the release of our 2025-26 Annual Cyber Threat Report. This report confirms that technology is evolving at rapid rates and has raised the stakes for cyber security. Read about the top cyber security threats to Australia in the new report 👉 https://t.co/GNprBpBTfG
He says the Tizen firmware was AES-encrypted, so keys were not available without opening the hardware. He used zero-day flaws to open a root shell and documented the tracking features with code screenshots. Samsung has not publicly answered.
‼️ Researcher Gains Root Access to Samsung Smart TV, Uncovers Extensive User Tracking
Details: https://t.co/UxJ2AwOVUn
A cybersecurity researcher says he gained root access to a 2025 Samsung Smart TV and found software built to track far more than the picture on the screen. Known online as log4j, he started after the set kept showing ads that seemed oddly specific to his household.
He says the Tizen firmware was AES-encrypted, so keys were not available without opening the hardware. He used zero-day flaws to open a root shell and documented the tracking features with code screenshots. Samsung has not publicly answered.
The findings have not been reproduced on an unmodified television. In posts starting on October 21, 2026, log4j listed automatic content recognition, screenshot handling, geolocation, network mapping, a targeted advertising service, and user profile building.
#CybersecurityNews
Would you spot a deepfake of your boss?
With just 3 seconds of audio, scammers can clone voices to bypass security.
This #CybersecurityAwarenessMonth, remember these tips:
Hang up.
Call back on an official channel.
Never bypass verification protocols.
#USCYBERCOM#BeCyberSmart
‼️ Google Fixes 52 Chrome Security Flaws, Including Four Critical Vulnerabilities
Details: https://t.co/SnkCAmyvSn
Google released a Chrome security update that fixes 52 vulnerabilities, including four critical flaws affecting FileSystem, FileAPI, Skia, and Layout. According to the release notice, the Stable channel is moving to version 156.0.8078.73/.74 for Windows and Mac.
At the same time, Linux users will receive version 156.0.8078.73. The update will reach users over the coming days and weeks. The supplied security list includes four critical vulnerabilities, 46 high-severity issues, and two medium-severity bugs.
The fixes cover browser functions ranging from file handling and page rendering to JavaScript, graphics, video, and audio processing.
#cybersecurityNews
33 countries have now told households to stock up on emergency food, water and supplies.
Most are telling their citizens to prepare for 3-10 days with Sweden and Norway suggesting 7 and Germany suggesting up to 10.
Official reasons are “war, extreme weather, or cyber security threats.”
The Binance hack (the largest heist in history) shows how powerful hackers are now with AI. All systems are at risk.
Climate change has lead to some insane weather events also and Europe has been gearing up for war the past two years.
Is this is a nothing burger? Or do you think something else is going on here?
‼️ Claude AI Builds One-Click Chrome and 0-Click Linux Exploit Chains, Bypasses Android Lock Screen
Details: https://t.co/t1UzeUaBQr
Anthropic's Frontier Red Team says an unreleased Claude research model wrote working exploit chains for Chrome, Safari, Android, Windows, and Linux.
The company shared the details in on research post on October 27, 2026. These were lab tests and not real-world incidents. Anthropic reported every bug to the vendor first, and the vendor released fixes.
The Chrome exploit is the most detailed. After a first prompt, Claude wrote a chain that runs code outside the browser sandbox. The test launched the Calculator app on a default Chrome install on macOS within seconds of a page loading.
In Safari, Claude broke the same-origin policy, the rule that keeps one website from reading another. The chain started with a use-after-free bug in JavaScriptCore.
The Linux chain is the most serious. Claude wrote an exploit that gives a remote attacker root access on servers running a multipath TCP listener.
#cybersecurityNews #claude #anthropicAI
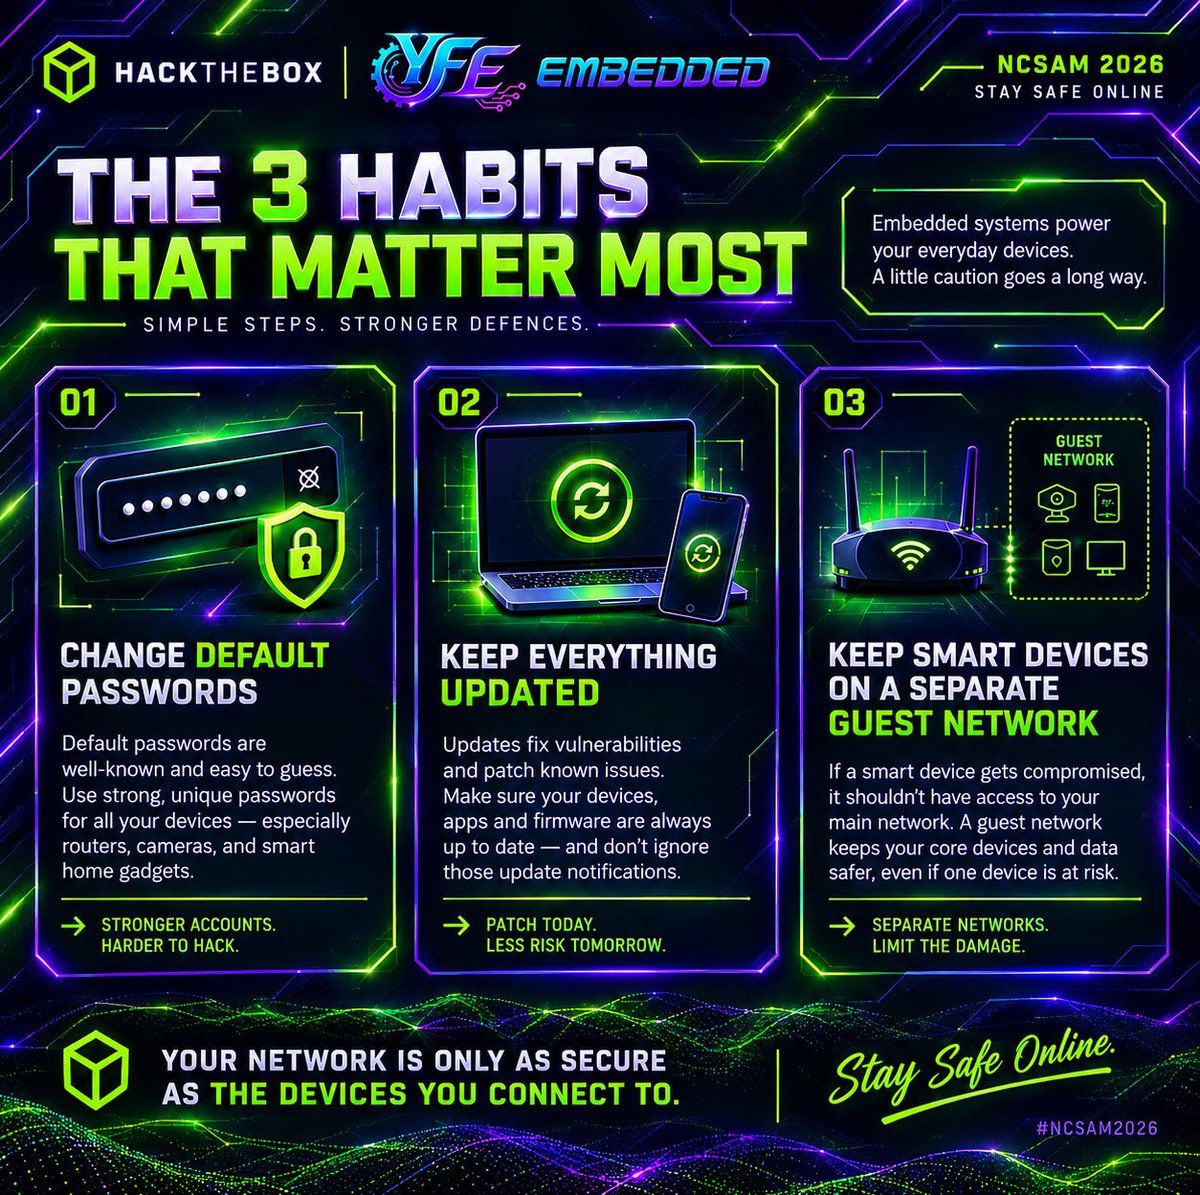
Your smart home could be an open door to your digital life.
Routers, cameras, smart TVs, and other connected devices can become entry points for attackers when poorly secured.
This Cybersecurity Awareness Month, we're sharing 3 habits that can help🧵
This Cybersecurity Awareness Month, we’re focused on Securing the Next 250 — protecting the homeland & systems we rely on every day. Cybersecurity is a shared responsibility. Stay alert, think before you click & help keep America secure @SecMullinDHS
‼️ Claude AI Exploits Linux Kernel Flaw to Execute Root Commands Without User Interaction
Details: https://t.co/QWY7xNGVrd
Anthropic says an unreleased Claude research model wrote a working exploit for a critical Linux kernel bug, tracked as CVE-2026-98432. The exploit lets a remote attacker run commands as root with no login and no user action.
Claude wrote an exploit that targets Linux servers with a multipath TCP listener. Anthropic describes the root cause as a race condition that leads to a use-after-free bug in the kernel networking stack. A use-after-free happens when code keeps using memory after the system has already released it.
#CybersecurityNews #Linux
⚠️ We issued 3 🆕 & 2 updated public #ICS Advisories. These advisories provide info about current security issues, vulnerabilities, & exploits surrounding ICS. More at https://t.co/4KvmlrK8Zn
We released updated Microsoft 365 configuration baselines and ScubaGear v2.0.0, featuring direct REST API calls, automated Power BI coverage, and a new Security Suite baseline to streamline M365 security.🧑💻🔗 https://t.co/aYB3Hldf66
Nation-state cyber actors are targeting #CriticalInfrastructure. Having an up-to-date incident response plan can help your org quickly and effectively isolate, contain, eradicate, remediate, and communicate incidents. Get started: https://t.co/CJcI1ibllc
⚠️ Trezor Warns of Suspected Spy Implant in Crypto Wallet That Could Steal Recovery Phrases
Details: https://t.co/xMZq8bGjLk
Trezor has warned that a suspected hardware implant inside a Trezor Safe 5 could steal recovery phrases and send them over a mobile network. The warning covers every Trezor model bought from CryptoBilis from March 2026 onward, although only one suspected device has been reported.
In its October 30 security notice, Trezor urged affected users to move funds to a newly created wallet with a new seed. The company has not examined the device and has received no reports of stolen funds from CryptoBilis buyers.
The March cutoff is a precautionary scope for customer action, not proof that every device sold since then was altered. The confirmed extent and operation of the suspected Trezor implant remain subject to laboratory examination.
#CybersecurityNews #Trezor