🚨 BREAKING: CRITICAL 9.5/10 VULNERABILITY THREATENS SERVERS WORLDWIDE. HACKERS COULD EXECUTE CODE BEFORE THE OPERATING SYSTEM EVEN LOADS.
Security researchers have uncovered a 16-year-old firmware vulnerability in technology used across the global server and data center ecosystem.
CVE-2026-97631 affects TianoCore EDK II, a foundational component used by major UEFI firmware vendors.
And the implications are serious.
🔴 Here's what we know:
➜ Pre-boot code execution: Attackers could execute malicious code at Ring 0, the CPU's highest privilege level, before operating system security controls are active.
➜ Widespread exposure: EDK II code is used extensively by firmware vendors including AMI, Insyde, and Phoenix, potentially exposing numerous enterprise servers.
➜ Security bypass potential: Successful exploitation could undermine the boot chain of trust and potentially enable persistent malware or compromise sensitive information.
➜ 16 YEARS UNDISCOVERED: The underlying buffer overflow has existed for approximately 16 years.
➜ Disclosure went wrong: Researchers from Anthropic and Google discovered the vulnerability, but a publicly released code fix exposed the issue months before its planned coordinated disclosure.
⚠️ THE BIG PROBLEM:
A source-code fix has been merged, but affected servers still require firmware updates from their manufacturers. Distributing those updates across enterprise infrastructure could take considerable time.
Important: Exploitation requires vulnerable firmware, PXE network boot, network access during the boot process, and target-specific knowledge. This is not an unrestricted remote exploit against every server.
Organizations should immediately review their firmware exposure, disable unnecessary network boot functionality, and check for vendor updates.
🔐 Lucid Security is offering FREE initial security reviews to help businesses identify potential vulnerabilities and reduce their attack surface.
🌐 https://t.co/RGeLnslnlj
CVE-2026-97631 | CVSS 9.5 CRITICAL
Source: Ars Technica / TianoCore Security Advisory
Get up to $50,000 with the HFM 100% Supercharged Bonus. Boost your trading potential. Download the app and get started today �Get up to $50,000 with the HFM 100% Supercharged Bonus. Boost your trading potential. Download the app and get started today 👇
BREAKING: 🇺🇸 GOOGLE JUST ANNOUNCED THEY ARE DEVELOPING A #BITCOIN AND CRYPTO CUSTODY SERVICE FOR INSTITUTIONS
BIG TECH IS ADOPTING BTC
THIS IS ABSOLUTELY MASSIVE 🔥
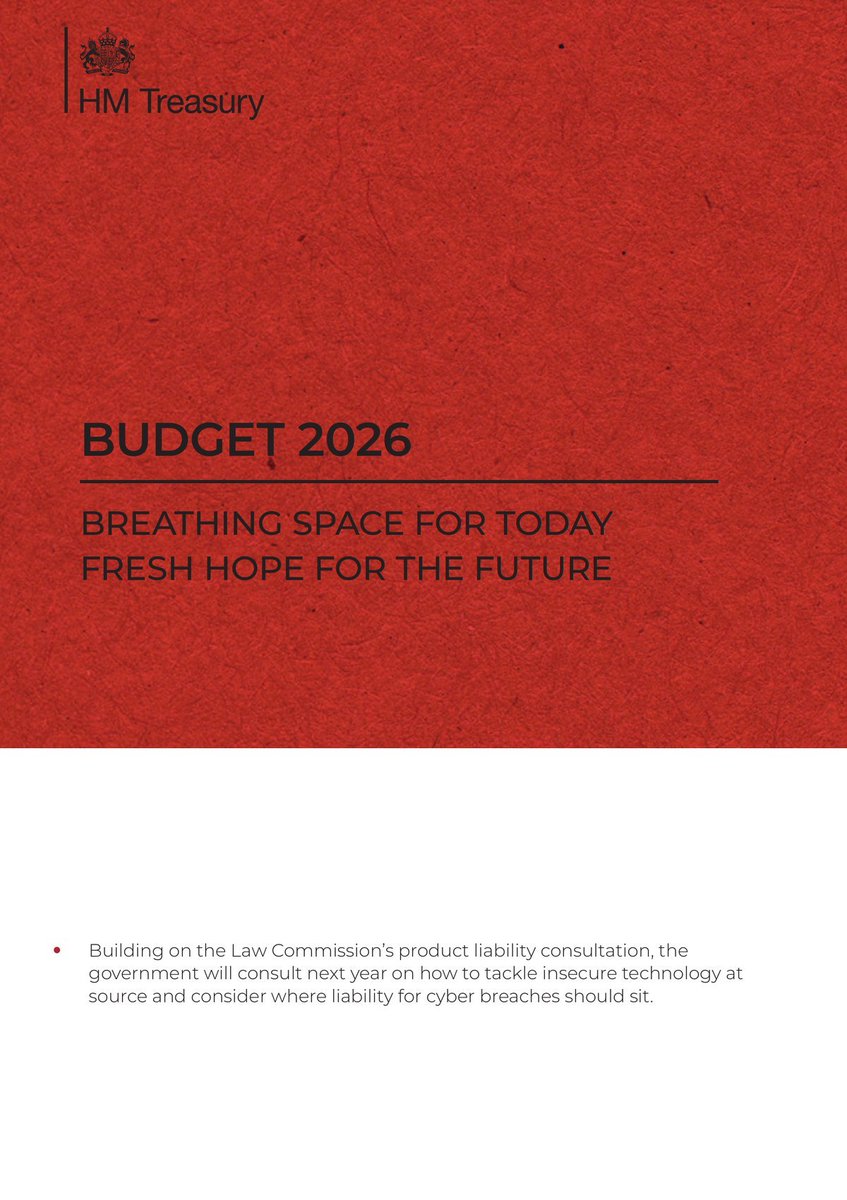
Britain will consult next year on where liability for cyber breaches should sit, its new budget says.
It could make software companies liable for insecure products, after years of relying on voluntary codes.
#koker#dannykoker
PwC Data Breach Claim – Everest Ransomware Group Claims to Have Stolen 590 GB of Data
Details: https://t.co/PSfMIt4saI
The Everest ransomware group claims to have stolen 590.69 GB of data from PwC, the global professional services firm. This alleged data theft includes human resources records, training materials, and internal documents. However, the claims are unverified, and PwC has not yet responded.
The supplied leak-site screenshot names a directory, pwc-stg.]csod.]com, and describes Cornerstone OnDemand platform materials, regional HR exports, e-learning courses, and integration testing documents. It lists 494 directories, alongside 1,333 original archive containers and 53 nested containers. The screenshot alone does not establish how these materials were obtained.
#CybersecurityNews
⚠️ We issued 2 🆕 & 1 updated public #ICS Advisories. This advisory provides info about current security issues, vulnerabilities, & exploits surrounding ICS. More at https://t.co/4KvmlrK8Zn
Cyber risks belong on the board's agenda. A Risk Operations Center (ROC) links technical vulnerabilities with financial business risks.
https://t.co/5i4y6ZujtL…
#Cybersecurity#KI@qualys
‼️ BREAKING: Oracle Issues Emergency Java Update for Critical 9.1 HTTPS Trust Vulnerability
Details: https://t.co/XZV8KY0rPW
Oracle has released an emergency Java security update to address CVE-2026-91403, a critical vulnerability affecting how Java applications trust digital certificates. Published on October 21, 2026, the alert assigns the flaw a CVSS 3.1 score of 9.1 and covers Oracle Java SE and GraalVM.
The update blocks affected intermediate certificate authority certificates linked to eMudhra. According to Oracle’s security advisory, the issue affects the Java Secure Socket Extension, or JSSE, component.
Oracle rates exploitation as low complexity, with no authentication or user interaction required. Successful attacks can expose or change sensitive data, although the risk matrix lists no availability impact.
#cybersecuritynews #vulnerability
‼️ Critical UEFI Firmware Flaw Could Expose Millions of Servers to Pre-Boot Code Execution
Details: https://t.co/3c3Bhee8Du
A critical bug in open-source EDK II firmware lets a remote attacker run code on a machine before the operating system starts. The flaw is tracked as CVE-2026-97631.
It sits in the network boot (PXE) driver and received a CVSS v4 score of 9.5. The advisory lists the NetworkPkg package in EDK II master as of September 14, 2026. EDK II is the reference code that many firmware makers use to build UEFI firmware, so the bug can reach servers, desktops, and laptops that boot over a network.
The advisory page still says “Not patched currently,” yet a fix has already been merged into the public code. Vendors must now ship that fix in their own firmware updates, which usually takes much longer.
#cybersecuritynews
AI is redefining cyber security best practice. That's why we have added a new chapter to our NCSC research problem book: 'AI in cyber security problems’.
To learn more and contribute to the discussion⬇️
https://t.co/nwkHCmUDnS
AI's cyber skills have taken a huge leap in about two years
In a test that simulates a 32-step cyberattack on a company network, tracking how far each model gets as it uses more tokens:
- GPT-4o, a 2024 model, stalled at step 2 and never improved with more tokens
- Today's top models kept improving all the way to 100M tokens, getting about three-quarters of the way through on average
- The best attempts finished all 32 steps and took over the entire network
From a16z's @OwenColby and @steph_zhang on The New Security Agenda: https://t.co/C814PJ4wGg
During #CyberStormX, CISA united thousands of public & private sector partners to strengthen cyber preparedness & critical infrastructure resilience. This #CybersecurityAwarenessMonth, we’re reinforcing the partnerships that secure our future. Read more: https://t.co/e7SlaLSq3B
Check out Muse, your personal AI agent. Redeem my code in Settings within 48 hours of joining and we'll both get 1 billion Muse tokens.
Code: 9AUGRN
https://t.co/TSPJwfNj4g
@EDietrich65070@DannyCountKoker Hello! Hope you're doing well.
I followed you😊 I was wondering if you can follow my favorite account too @silasjuliusHQ 🤗




![The_Cyber_News's tweet photo. PwC Data Breach Claim – Everest Ransomware Group Claims to Have Stolen 590 GB of Data
Details: https://t.co/PSfMIt4saI
The Everest ransomware group claims to have stolen 590.69 GB of data from PwC, the global professional services firm. This alleged data theft includes human resources records, training materials, and internal documents. However, the claims are unverified, and PwC has not yet responded.
The supplied leak-site screenshot names a directory, pwc-stg.]csod.]com, and describes Cornerstone OnDemand platform materials, regional HR exports, e-learning courses, and integration testing documents. It lists 494 directories, alongside 1,333 original archive containers and 53 nested containers. The screenshot alone does not establish how these materials were obtained.
#CybersecurityNews](https://pbs.twimg.com/media/HVSrAkvaMAAtl7D.jpg)