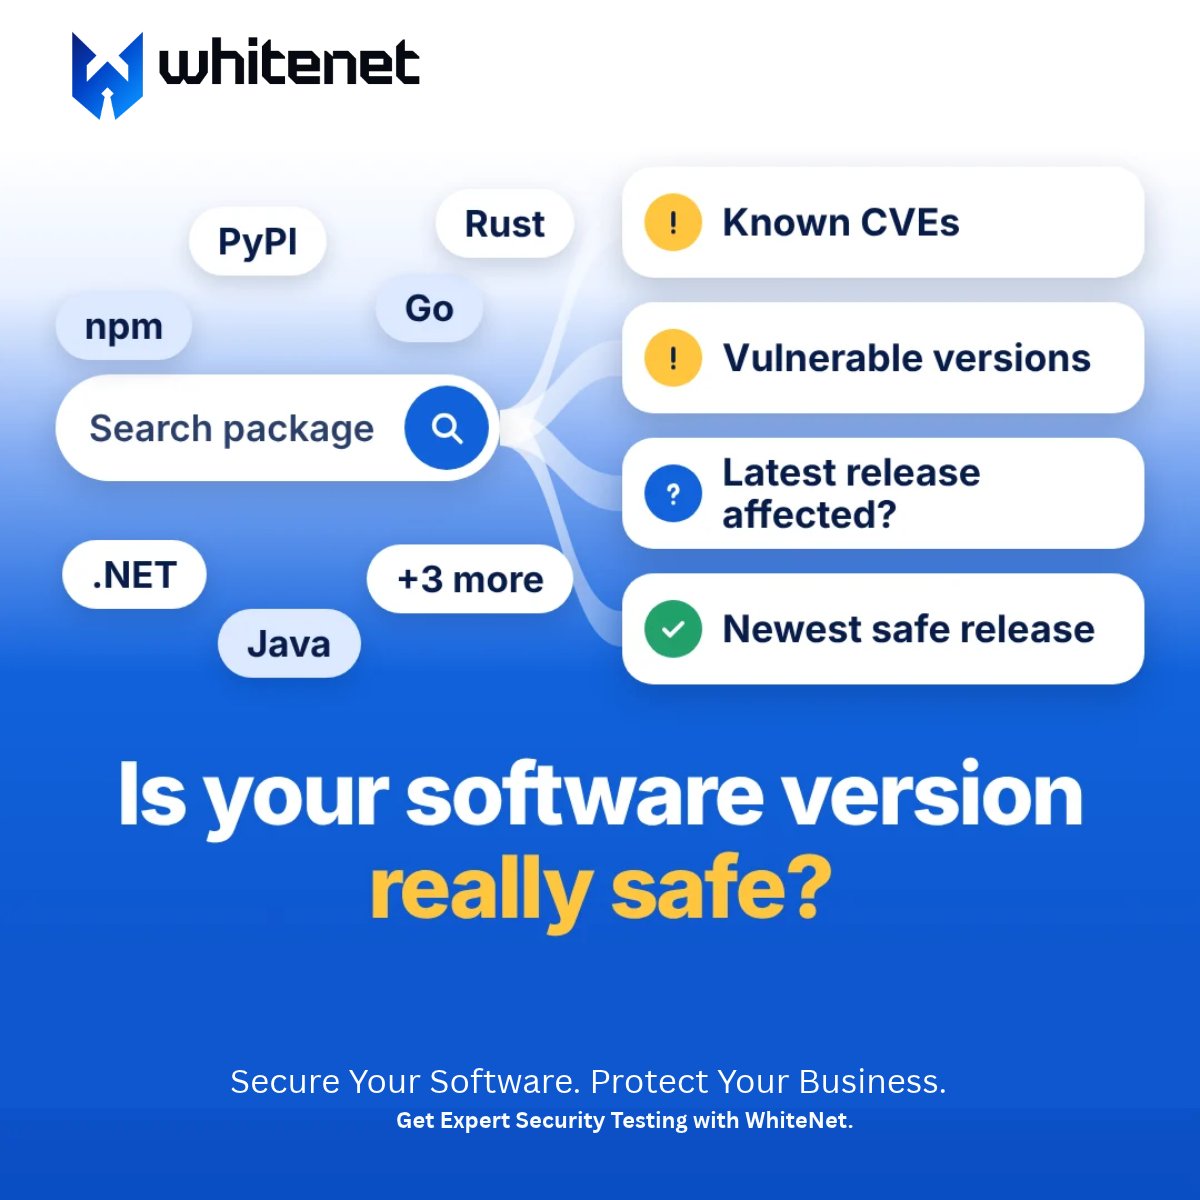
Is your software version really safe?
Outdated or vulnerable dependencies can put your applications at risk.
🔹 Check known CVEs.
🔹 Review affected versions.
🔹 Keep dependencies updated.
🔹 Strengthen application security.
Secure your software with WhiteNet.
#whitenet
🪔✨ Let the light of Diwali bring new beginnings, happiness, and prosperity.
May your celebrations be filled with joy, positivity, and countless bright moments.
WhiteNet wishes you and your loved ones a Safe & Happy Diwali! 💙
#HappyDiwali#Diwali2026#WhiteNet
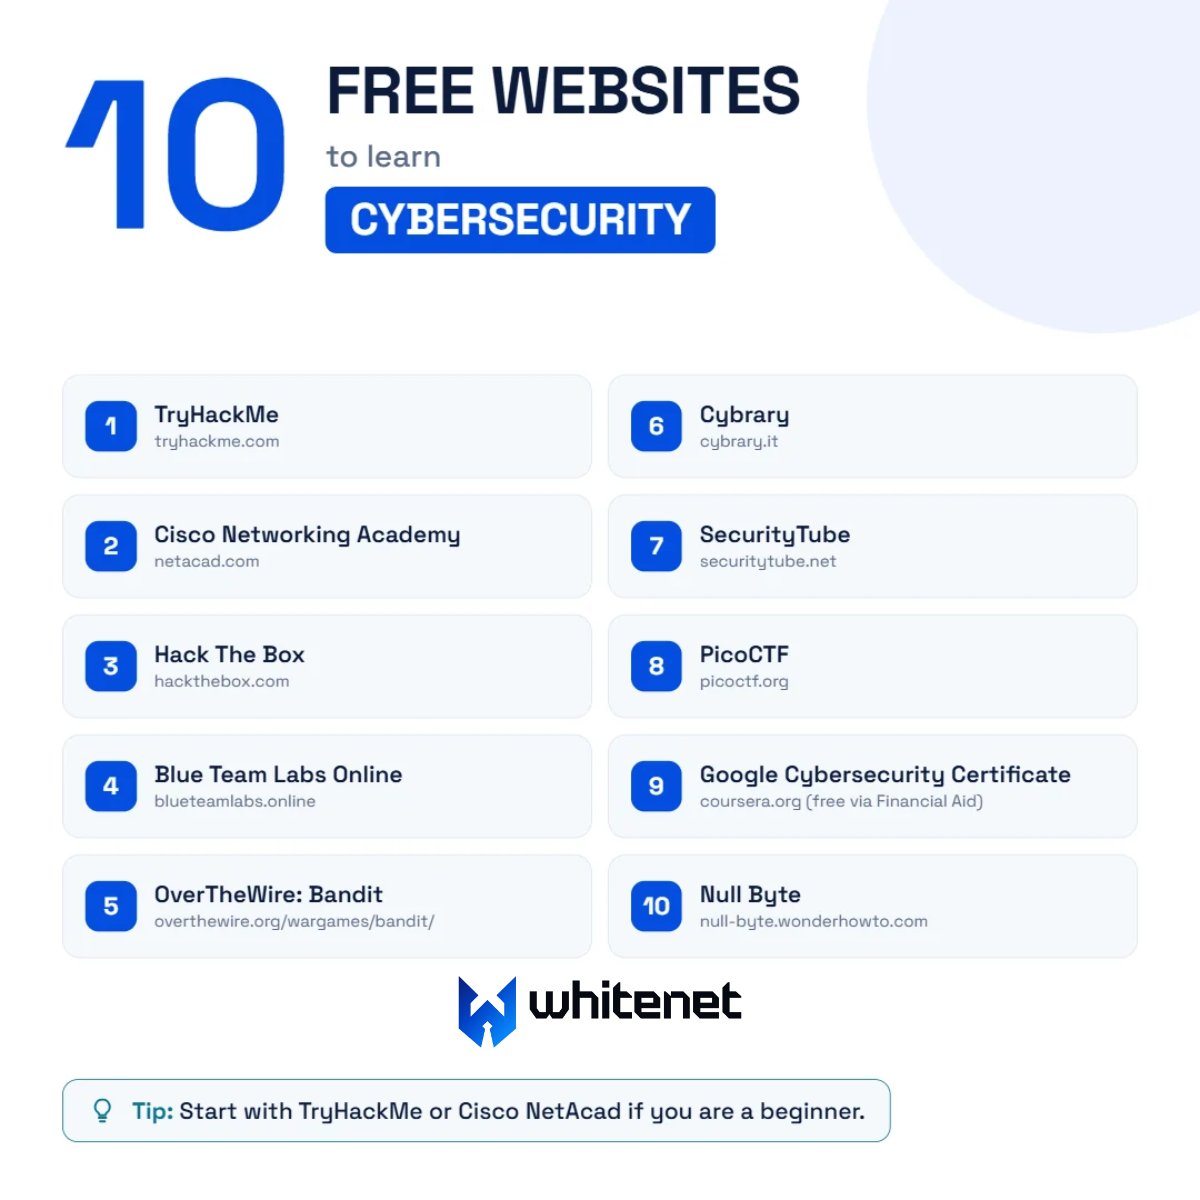
Want to build your cybersecurity skills? 🔐
Start with the right learning resources. From networking basics to hands-on security labs, these 10 platforms can help you learn and practise.
Which platform would you recommend to a beginner? 👇
#CyberSecurity#InfoSecApp
𝗖𝗿𝗶𝘁𝗶𝗰𝗮𝗹 𝗣𝗛𝗣 𝗩𝘂𝗹𝗻𝗲𝗿𝗮𝗯𝗶𝗹𝗶𝘁𝗶𝗲𝘀: 𝗔𝗰𝘁 𝗡𝗼𝘄!
CVE-2026-109618 & CVE-2026-109619 carry a CVSS v4.0 score of 9.2/10 and could enable unauthenticated remote code execution on affected servers.
Patch promptly. Verify your PHP environment.
#PHP#AppSec
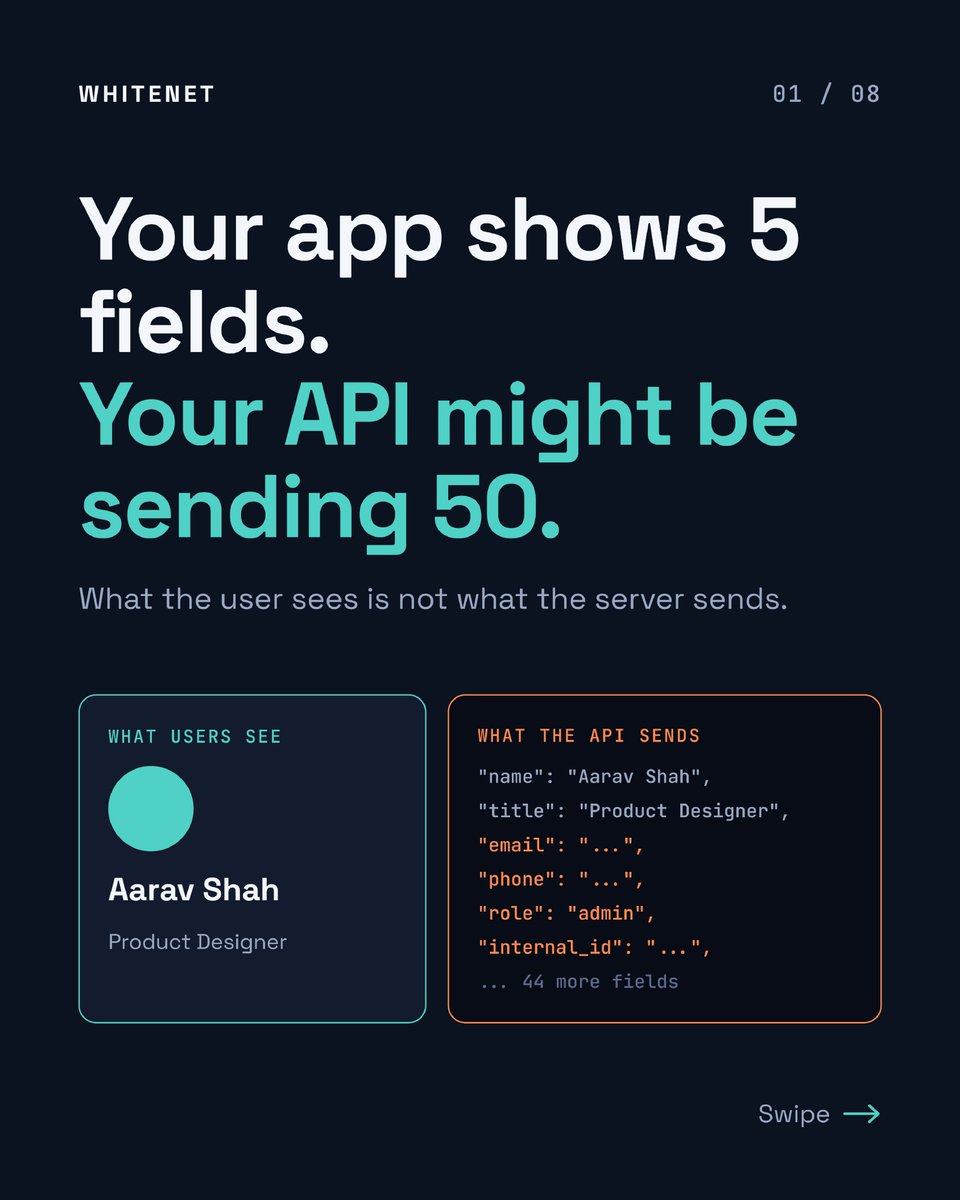
Your app shows 5 fields. Your API might be sending 50.
What users can’t see isn’t necessarily protected.
Read more on LinkedIn: https://t.co/EJI2SiPKqN
#APISecurity#AppSec
Dear Prime Minister Ambani,
Please accept my humble apologies for not realizing that you are the real boss of India.
Naturally, you would prefer to maintain your monopolistic exploitation of the great people of India, but would you nonetheless consider allowing Starlink to compete?
There are many areas of India, as there are in all countries, with no Internet access, which denies children the opportunity for education and for small businesses the opportunity to sell their goods to a global market. Starlink would change their lives for the better.
Thank you 🙏
I found a critical auth bypass that resulted in a $10K bounty due to mass PII exfiltration. Here’s the technique:
The endpoint had 3 checks:
1. JWT auth at the gateway
2. Backend path validation
3. A trusted-client header check
The bypass came from defeating each one differently.
1. JWT check
Normal request:
`GET /api/employee/12345`
→ `401`
But paths ending in `.json` were treated as static resources and skipped JWT auth:
`GET /api/employee/12345.json`
→ Auth check bypassed
2. Path validation
Problem: The backend still needed a clean employee ID.
Payload:
`GET /api/employee/12345%23.json`
The gateway saw a `.json` path.
After decoding:
`12345#.json`
The downstream parser truncated at `#`, leaving:
`12345`
Same request, but different interpretation at each layer.
3. Trusted-client check
The endpoint also expected a client header:
`X-CLIENT-ID: WEBAPP`
Without it:
→ `400`
With it:
→ Request accepted
So the final chain was:
`.json` → bypass gateway auth
`%23` → preserve a valid backend ID
Client header → satisfy the final gate
#BugBounty tip:
When multiple layers handle the same request, map every security check and test whether the gateway, proxy, and backend interpret the URL differently.
I found a critical auth bypass that resulted in a $10K bounty due to mass PII exfiltration. Here’s the technique:
The endpoint had 3 checks:
1. JWT auth at the gateway
2. Backend path validation
3. A trusted-client header check
The bypass came from defeating each one differently.
1. JWT check
Normal request:
`GET /api/employee/12345`
→ `401`
But paths ending in `.json` were treated as static resources and skipped JWT auth:
`GET /api/employee/12345.json`
→ Auth check bypassed
2. Path validation
Problem: The backend still needed a clean employee ID.
Payload:
`GET /api/employee/12345%23.json`
The gateway saw a `.json` path.
After decoding:
`12345#.json`
The downstream parser truncated at `#`, leaving:
`12345`
Same request, but different interpretation at each layer.
3. Trusted-client check
The endpoint also expected a client header:
`X-CLIENT-ID: WEBAPP`
Without it:
→ `400`
With it:
→ Request accepted
So the final chain was:
`.json` → bypass gateway auth
`%23` → preserve a valid backend ID
Client header → satisfy the final gate
#BugBounty tip:
When multiple layers handle the same request, map every security check and test whether the gateway, proxy, and backend interpret the URL differently.
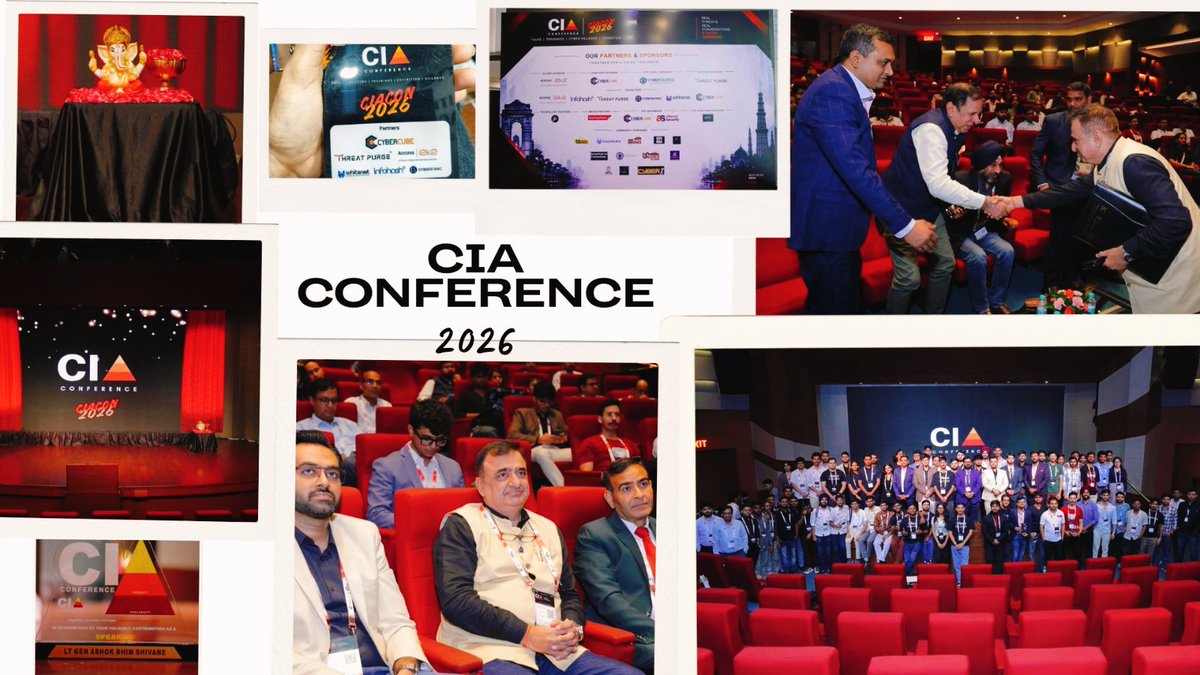
𝗠𝗼𝗺𝗲𝗻𝘁𝘀 𝗳𝗿𝗼𝗺 𝗖𝗜𝗔𝗖𝗢𝗡 𝟮𝟬𝟮𝟲!
Great conversations, valuable connections, and memorable moments with the cybersecurity community. 🤝
#CIACON2026#Cybersecurity#WhiteNet
𝗛𝗮𝗽𝗽𝘆 𝗚𝗮𝗻𝗱𝗵𝗶 𝗝𝗮𝘆𝗮𝗻𝘁𝗶 🇮🇳
On this Gandhi Jayanti, let’s remember the values of truth, integrity, and responsibility - values that can guide us towards a safer and better future.
Wishing everyone a peaceful and meaningful Gandhi Jayanti. 💙
#GandhiJayanti
𝗔𝗜 𝗜𝘀 𝗙𝗶𝗻𝗱𝗶𝗻𝗴 𝗩𝘂𝗹𝗻𝗲𝗿𝗮𝗯𝗶𝗹𝗶𝘁𝗶𝗲𝘀 𝗙𝗮𝘀𝘁𝗲𝗿.
AI is changing vulnerability discovery, but finding a flaw is only the first step. Testing, validation and human expertise still matter.
Is your application security ready for the AI era?
#Cybersecurity
What happens when an API lacks rate limiting?
Excessive requests, automated abuse, brute-force attempts, and service disruption can put an API at risk.
Rate limiting helps keep API access under control.
#APISecurity#CyberSecurity#ApplicationSecurity#RateLimiting
Techniques Attackers Use to Compromise Active Directory
Active Directory is a high-value target. Attackers can abuse credentials, privileges, Kerberos tickets, configurations, and identity trust to gain deeper access.
Read more: https://t.co/zCAqBOIxaT
#CyberSecurity#whitenet
Proud to see @whitenetio joining CIA Conference 2026 as an Exhibitor Partner.
Looking forward to meeting cybersecurity leaders, CISOs, founders, and fellow security professionals in New Delhi.
See you at CIA Conference –24 September.
#WhiteNet#CIAConference2026#CyberSecurity
We’re proud to have WhiteNet® join us at CIA Conference 2026, bringing its expertise in penetration testing, VAPT, red teaming, cloud security, application security, and advanced cybersecurity solutions.
As organizations face increasingly sophisticated cyber threats, proactive security testing and continuous validation are becoming critical to building resilient digital environments.
At CIA Conference 2026, WhiteNet will connect with cybersecurity leaders, CISOs, security practitioners, and technology decision-makers to exchange perspectives, explore emerging challenges, and contribute to conversations shaping the future of cybersecurity.
📅 23–24 September 2026
📍 PHD House, New Delhi
👥 300+ Cybersecurity Leaders & Decision Makers
🤝 Meet WhiteNet at CIA Conference 2026 and explore how proactive security can strengthen your organization’s cyber resilience.
Grab your passes now - https://t.co/73hpaZYWmr
🔗 Learn more about WhiteNet : https://t.co/4648PrO5md
Excited to be attending @CiaConference and representing @whitenetio as an Exhibitor. Looking forward to connecting with cybersecurity leaders, researchers, and fellow professionals in New Delhi. See you there! 🚀