Found a bug? A useful vulnerability report explains what happened, how to reproduce it and why it matters. Clear reports help teams fix issues faster and strengthen security.
🌐 https://t.co/7M7cXmiFbV
One cyberattack can disrupt an entire digital ecosystem.
Nepal’s NEPSE incident is a reminder that cybersecurity goes beyond protecting data, it’s about keeping critical systems running.
Read the blog to understand the risks and lessons.
https://t.co/4caa1Gg2x8
Your database shouldn’t trust everything.
Poorly handled database queries can expose sensitive information and create opportunities for unauthorized data access.
Learn more about web security and vulnerability prevention with Bugv Hacktober Fest!
It looks like text, but it can be more than that.
Cross-Site Scripting (XSS) happens when untrusted input is handled unsafely and gets interpreted by a browser, potentially putting users and their data at risk.
One input. Big risk.
Giveaway Alert!
Friday Quiz is here with Bugv Hacktober Fest.
October wasn’t always Cybersecurity Awareness Month. Can you guess when the story began?
Comment your answer (A, B, C or D) for a chance to win exciting giveaways.
Let’s see who gets it right!
#Bugv
Weak authentication can turn “My Account” into “Whose Account?”
From weak passwords to flawed login logic, authentication bugs can give attackers access to accounts and sensitive data.
Protect the login. Protect the user.
📞 01-4530730
🌐 https://t.co/7M7cXmiFbV
New to web security? Start with the fundamentals.
These are some of the key security issues beginners should know about when learning application security.
#OWASP#WebSecurity#BugBounty#Bugv#Hacktober
Companies have systems. Researchers have findings. Bugv brings them together.
Our platform connects businesses with security researchers to discover, report and address vulnerabilities responsibly.
🌐 https://t.co/7M7cXmiFbV
A bug isn’t always a vulnerability.
A vulnerability is a weakness that can create a security risk, potentially giving attackers a way to access, alter or disrupt something they shouldn’t.
Understanding the difference is where real security research begins.
#Bugv#HacktoberFest
Before you hit download, hit the reviews.
Not every app is what it claims to be. Check user reviews, verify the developer, and make sure you’re not installing something malicious or compromised.
Stay curious. Stay cautious. Stay secure.
#Bugv#HacktoberFest#CyberSecurity
Why do we have Cybersecurity Awareness Month?
It’s more than a yearly campaign. It’s a reminder that staying secure requires awareness, good habits and continuous action.
Read More:
https://t.co/GgicPRkfFu
Samparka is opening the door to responsible security research.
Samparka has launched its Vulnerability Disclosure Program on Bugv, giving security researchers a clear and responsible way to report potential vulnerabilities.
Read More:
https://t.co/vvjO9do80I
AI is making cyberattacks faster, smarter and harder to detect.
Is your business ready?
Read the full blog to understand how attackers are using AI and what businesses can do to stay ahead.
#Cybersecurity#AI#Bugv#CyberThreats#AIAttacks
https://t.co/Dl6z7axiqK
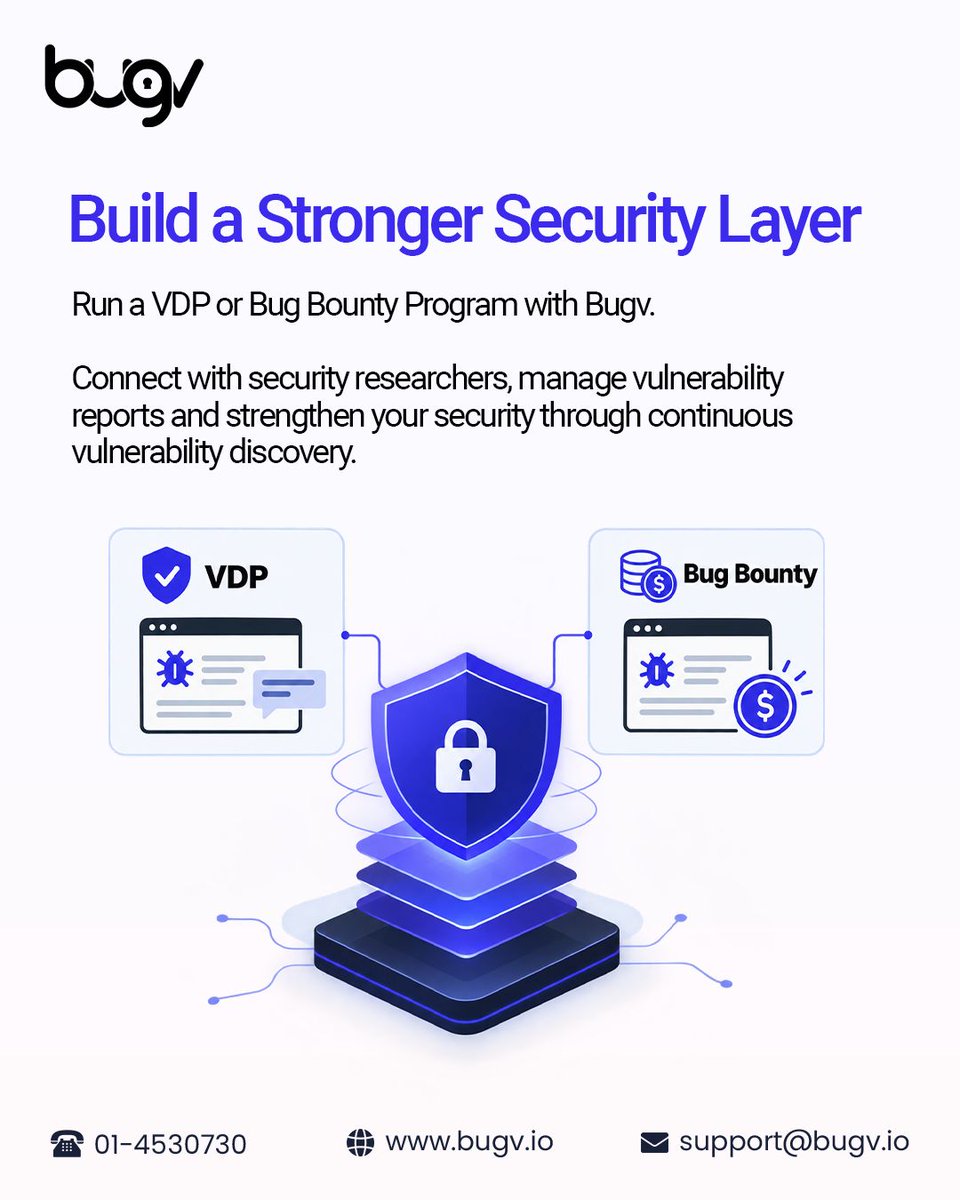
Bug Bounty or VDP? 🔐
A VDP gives researchers a clear way to report vulnerabilities. A Bug Bounty incentivizes them to find and report valid bugs, often with rewards.
Here’s how they differ.
#Bugv#Cybersecurity
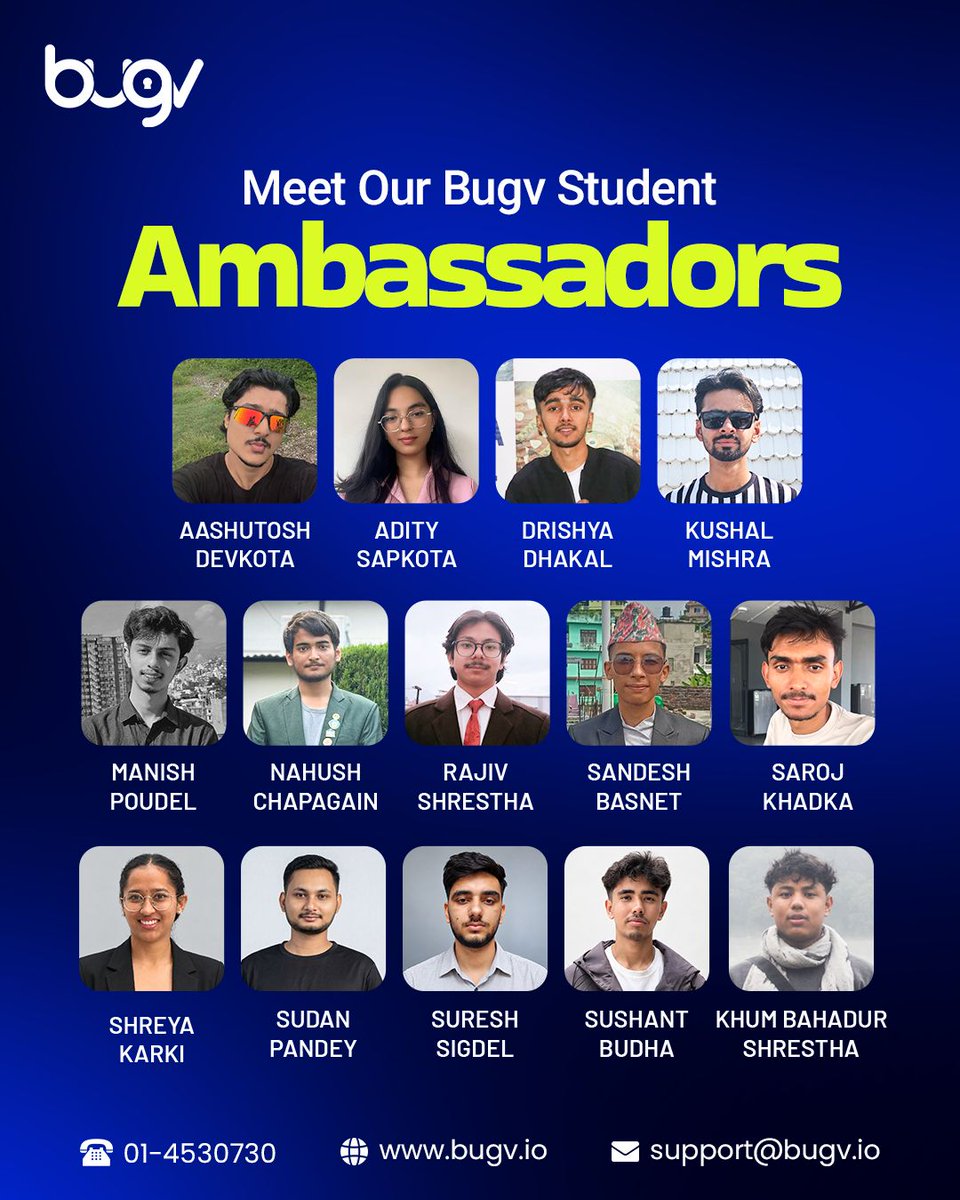
We’re excited to introduce our Bugv Student Ambassadors, a passionate group of students ready to learn, connect, create and contribute to the cybersecurity community.
Welcome to Bugv. Let’s learn, grow and secure together. 🔐
#Bugv#BugvStudentAmbassadors#Cybersecurity
Launch your Bug Bounty Program with Bugv. Define your scope, set rewards and let security researchers uncover vulnerabilities before attackers do.
📞 01-4530730 | 🌐 https://t.co/7M7cXmiFbV
#Bugv#BugBounty#Cybersecurity