Husband, Father, #DFIR @ Unit 42, Digital Forensics Discord Admin, AboutDFIR Contributor, Author, #USMC Veteran, Former LE, NHL Fan, Dark Mode, Animals, Music
A few months of behind-the-scenes work is now ready to share with the world! The official EZ Tools Manuals are now available to the public!
Grab the book - https://t.co/l86xmIjEii
Check out the source code for the book - https://t.co/XUuuwx2w8L
#eztoolsmanuals#dfir#eztools
1/ EZ Tools 2026.11: new options, most from reported issues/requests
🧾 EvtxECmd recovers records from cleared logs and slack
📂 MFTECmd takes folders of MFTs and finds Recycle Bin I files
🔧 RECmd batch files get 16 new conversions
Update with Get-ZimmermanTools 🧵 #DFIR
hashcat v8.0.0 released!
The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards.
Release notes: https://t.co/0ffrO586PJ
Download: https://t.co/Grn4jZmAWr
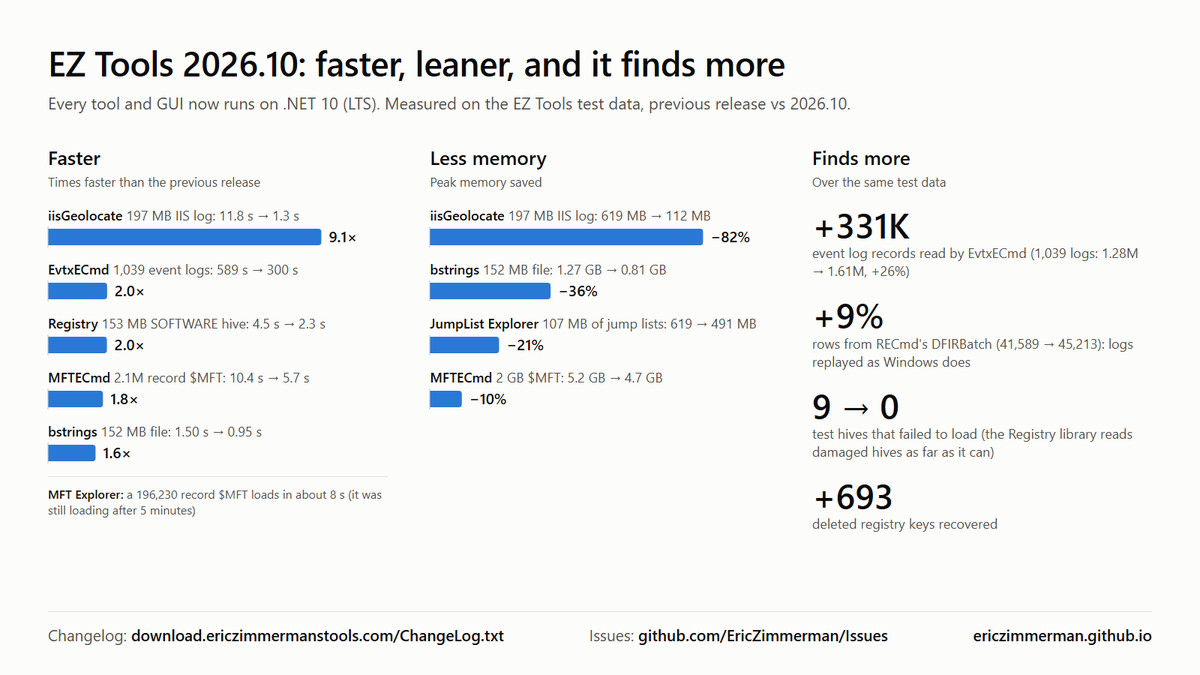
1/ EZ Tools 2026.10 is out, all on .NET 10 (LTS)
✅ More accurate: 331K more event log records, hive logs replayed as Windows does, every test hive loads
⚡ Faster: up to 9x; EvtxECmd and Registry 2x
📉 Less memory: up to 82% less
Update with Get-ZimmermanTools 🧵 #DFIR
1/ EZ Tools 2026.10 is out, all on .NET 10 (LTS)
✅ More accurate: 331K more event log records, hive logs replayed as Windows does, every test hive loads
⚡ Faster: up to 9x; EvtxECmd and Registry 2x
📉 Less memory: up to 82% less
Update with Get-ZimmermanTools 🧵 #DFIR
Paid opportunities for cybersecurity professionals of all specialties and experience levels, we have two great opportunities to introduce you to CyberStudio by SANS, a new training platform now in development. (Yes, I am writing a course for this!)
Beta testing: For professionals based anywhere in the United States, we invite you to test drive CyberStudio and participate in a follow-up interview (online) to share your thoughts.
When: 9/21 through 10/26
Register to be a beta tester at https://t.co/3SrFdKULS5
Focus group: For professionals in the Las Vegas area, we’d love for you to join us in-person at Caesars Palace to get an introduction to CyberStudio and share your thoughts.
When: Thursday, 9/24, evening (1–2 hours)
Where: Caesars Palace, Las Vegas
Register for the focus group at https://t.co/gNAswA0U2i
Focus group attendees and beta testers will be compensated! Thanks in advance.
🧟 Abeebus is back from the dead. v2.1 is out.
It pulls IPv4 addresses out of any file and gets GeoIP data for each one from https://t.co/diaa8HBDyk.
🔧 The big fix: it used to read the entire file into memory. Fine for email headers, not so great for a memory image. It streams now.
Also keeps your results if you hit the https://t.co/diaa8HBDyk rate limit.
If you prefer a native Windows binary, try SharpAbeebus.
https://t.co/tM4oI8EgNb
https://t.co/baPrO4D5kO
The first 13Cubed mini course, Architecting the Hunt, is now available! 🎉
An entry-level, hands-on introduction to threat hunting, learn a repeatable framework, then put it to work in a self-contained lab. No prior experience needed.
Watch the launch video 👉 https://t.co/pjP8EIAvOF
Enroll 👉 https://t.co/dRFzOp4eOD
#ThreatHunting #DFIR #BlueTeam
The very first 13Cubed mini course is coming, and we couldn't be more excited! 🔥
🎯 Architecting the Hunt takes you from zero to confident threat hunter with a repeatable framework, then drops you into a hands-on lab with 100 hosts and 9M+ events to hunt through. 🕵️
✅ Entry-level
✅ Hands-on lab (yours to keep!)
✅ No experience needed
The waitlist is OPEN 👇
https://t.co/dRFzOp4eOD
The Weather Channel has started letting you opt into a retro version of the forecast, and it's delightful. Includes the music and everything.
https://t.co/cfC6zibdNA
The Evidence Locker has been updated!
- 6 challenges from @RedHatPentester (Vehicle triages, network captures, Windows and more)
- Jimmy Wilson test image
https://t.co/WgjsPqC3ze
Do you have more that you want included? Check out the "New Submission" button on the page or send me a DM. #DFIR #MobileForensics
🎉 A new 13Cubed episode is up!
This time we're exploring the USN Journal on a live system. How can we view it while Windows is actively running, and does the reality match the common explanations? Let's find out!
https://t.co/XtCiJxPukW
#DFIR#DigitalForensics
Really enjoyed this interview by @elijahwoodward9 with @bunsofwrath12 on Team Cymru’s “Future of Threat Intelligence”
A lot of good DFIR points in there that often get ignored in enterprise envs:
- why default Win event log sizes are a forensic disaster
- why Sysmon deployments are often stale or incomplete
- the forensic value of Volume Shadow Copies and the $J USN Journal
- why EDR alone is not enough
- how true positives get buried in alert fatigue
- using AI as a force multiplier for parsing logs and writing one-off tooling, while still not treating it as forensic ground truth
Also liked the practical angle throughout the whole discussion. Felt very experience-driven, not theoretical.
Worth watching
https://t.co/SfgqjbR9Eu
@villanoflo@cyb3rops@ElijahWoodward9 It most definitely is not. I often find myself disappointed by what EDRs log, and much of the good stuff on a Windows endpoint has long since rolled over. There are simply too many high-fidelity things being logged to the Security event log channel. I hope you enjoyed the chat!
All EZ Tools have been updated! New version is 2026.5.0 across the board.
Nuget updates, control updates, bug fixes and general refreshing of everything.
Enjoy!!
#dfir