API keys leak every day: pushed to git, pasted into AI chats, stored on hosts that get hacked.
Burnkeys finds every key in your projects, tells you which ones are at risk, and replaces them everywhere in a minute. It never prints a secret.
Free for 3 projects → https://t.co/t9JfH6ExUS
The 5 stages of a leaked key:
1. "It's a private repo, it's fine"
2. "I'll rotate it tomorrow"
3. "Which projects even use this one?"
4. "Why is the new one failing?"
5. "Wait. Which one did I just revoke?"
Pasting an API key into an AI chat is the easiest leak there is.
The Burnkeys plugin for Claude Code blocks keys pasted into chat. It installs from the Mac app in one click, and it's on the free plan.
https://t.co/9COy08hkUT
Honest question for devs:
How old is the oldest API key that still works in your projects?
And could you name every place a copy of it lives right now?
Things that do NOT kill a leaked API key:
✗ force-pushing over the commit
✗ deleting the .env file
✗ deleting the key from a tool's settings
✗ making the repo private
Only revoking it at the provider does. Then check the old key actually fails a real request.
LiteLLM's write-up: a master key was committed to a public repo on May 27. They force-pushed over the commit. The key was never revoked.
Oct 10: an attacker used it. Oct 21: a malicious release shipped.
Force-push hides a key. Only revoking kills it.
https://t.co/QzyLbKMwts
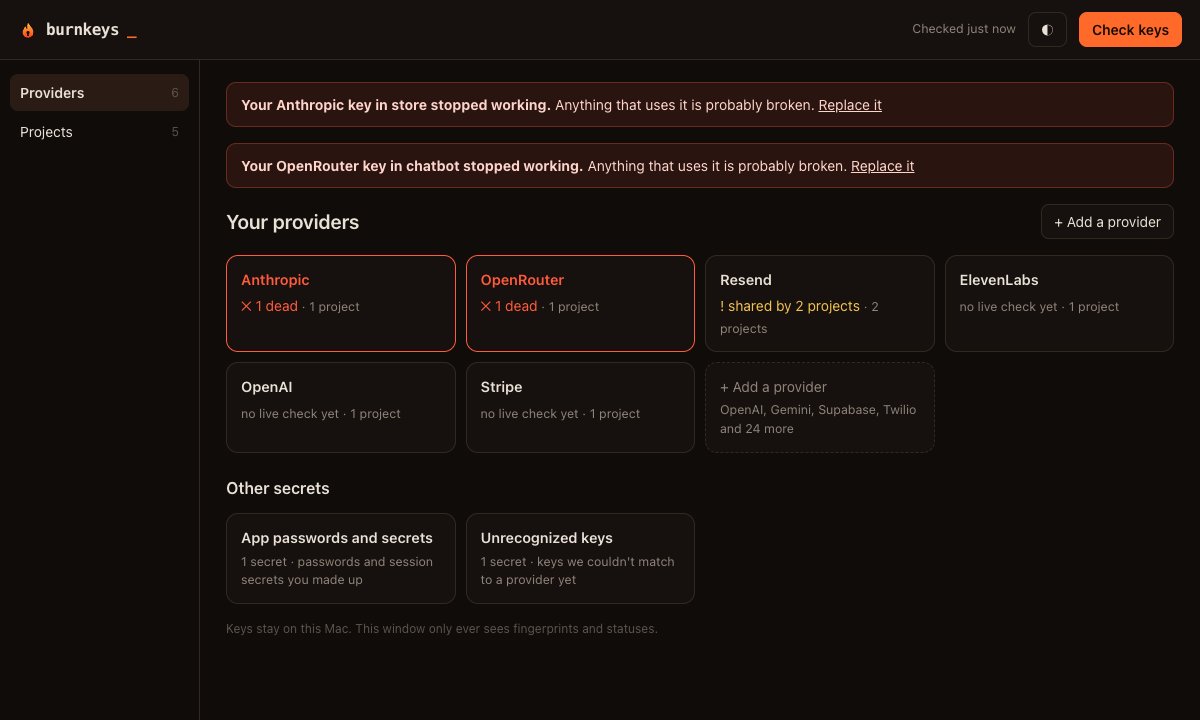
Rotating our keys after Railway, we found something worse: an Anthropic key in another project had been dead for weeks.
Nobody noticed, not even the AI assistant editing that code daily.
Burnkeys asks each provider one question: does this key still work?
https://t.co/TuCFtqYSGq
The cheapest leak to fix is the one that never gets committed.
`burnkeys hook install` blocks any git commit that contains an API key or an .env file. Or flip one toggle per project in the app.
Free. https://t.co/9COy08gN5l
A tool that reads your .env files should let you read its code.
Burnkeys is now open source. VERIFY.md lists every host a key is ever sent to, and how to check it yourself (Little Snitch, lsof, codesign).
https://t.co/Iw0xrRYy5X
Know which keys your team shares before one leaks.
Burnkeys Team: one view of every API key your projects use, who holds it, and whether it works. Slack alert when one dies or leaks into git.
Values never leave anyone's Mac.
https://t.co/I0ZXEADPgq
After Railway, rotating 10 keys took us 2 hours.
New in Burnkeys: Replace all. One pass through every affected key, updates Railway, Vercel, Netlify, https://t.co/DHESeBvz1f and Render, redeploys, and ends with one list of old keys to revoke.
~10 minutes.
https://t.co/TuCFtqYSGq
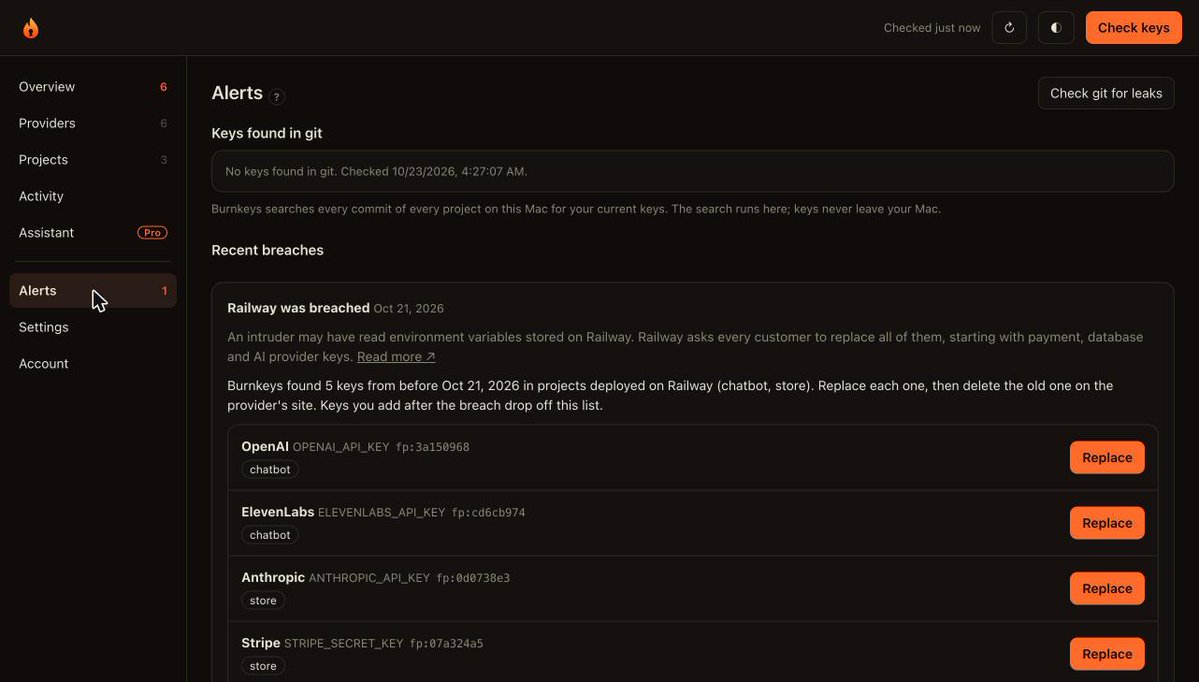
Railway was breached on Oct 21. If you ever stored env vars there, treat every one of them as leaked.
Here's how to replace all of them in about 10 minutes without missing one 🧵
So we built Burnkeys. On your Mac it:
✓ lists which of your keys were on Railway
✓ checks each one live
✓ "Replace all": one pass through every key, updates Railway, Vercel, Netlify, Fly, Render and redeploys
✓ ends with one list of old keys to revoke
Never prints a key.
It runs on your Mac. Your keys never leave it and never appear on screen.
Made for indie hackers, solo founders and small teams shipping with AI APIs, without a security team.
Mac app coming soon: https://t.co/9COy08hkUT
Last week our hosting provider got breached. Every API key we had stored there had to be rotated by hand.
10 keys. 2 hours. One new key deleted by mistake.
Then we found something worse. 🧵
So we built Burnkeys.
One window. Every project. Every API key.
✓ which keys still work
✕ which ones quietly died
! which ones are shared between projects
Click Replace, copy the new key on the provider's site. Burnkeys does the rest: every file, Vercel, redeploy.