@McPepiiVT@shadcn I’m not a frontend developer I just base my designs on other sites I see and try to reuse as much code as I can between them as to not need to reinvent the wheel basically, I can assure you there’s no need to worry about a database leak or emails/passwords being leaked.
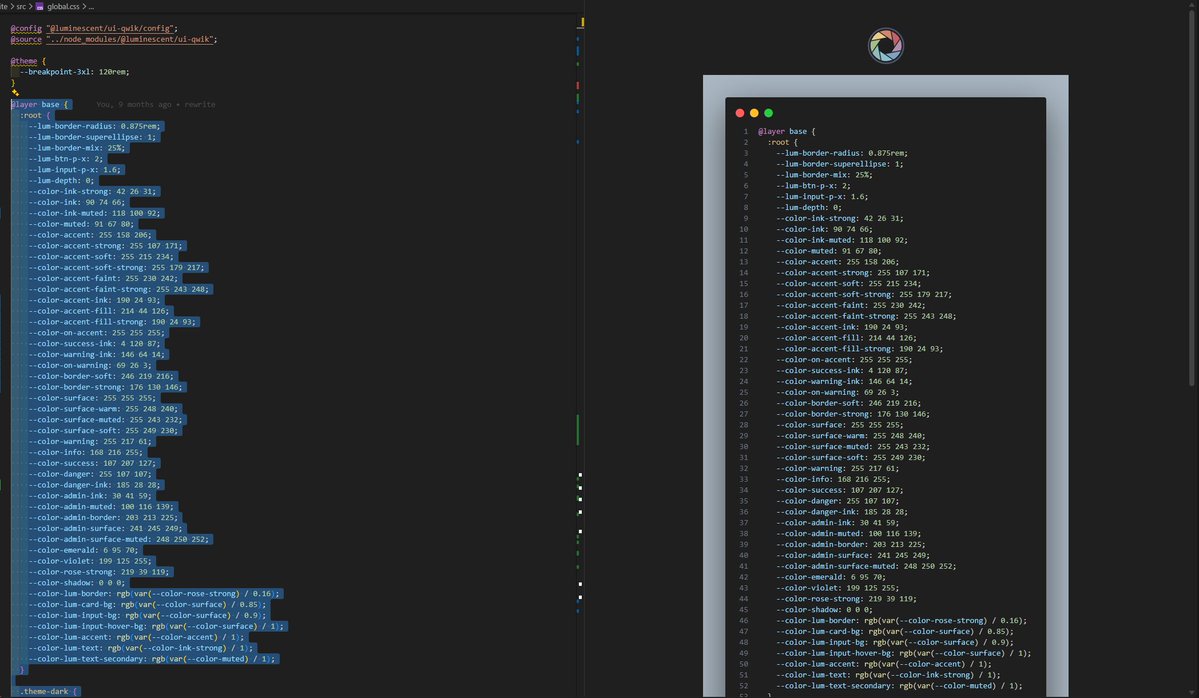
@McPepiiVT that screenshot is the style sheet nicely screenshotted using a vscode extension called codesnap
Luminescent UI isnt an ai tool its a UI library my friend and i made.
@McPepiiVT Actually its tailwind. It is like that for the theme system, --color-accent is a tailwind variable that changes when you change the theme from dark mode to light mode.
@McPepiiVT@selkiegyuu@vtubernook One last thing the ssl grade says nothing about data leaks or how the data is stored it is purely the connection between the browser and the server
@McPepiiVT@selkiegyuu@vtubernook since we dont store the passwords in plain text we hash them. a free ssl cert is no different from a paid one. I will still raise the minimum tls version to 1.2 and turn on HSTS so it will grade A/A+. Happy to look into any specific unsafe gaps you can point to!
@McPepiiVT@selkiegyuu@vtubernook The B is because we still provide the website over tls 1.0 for backwards compatability, no modern browser should be using tls 1.0 99% of people already go through tls 1.2/1.3 which WOULD make this get an A grade, the TLS version doesnt matter for the same of reused passwords 1/2
@fwosting@Yggr153@vtubernook This was me showing you the source code lol, the first one is the messed up version and the second one is what it should be i just messed up when writing it that is some pure human slop
Minecraft plugin developers what’s the most annoying part of testing and releasing an update?
I’m working on a project to help with testing and publishing and I’d love to hear what your current workflow looks like and what parts suck the most.