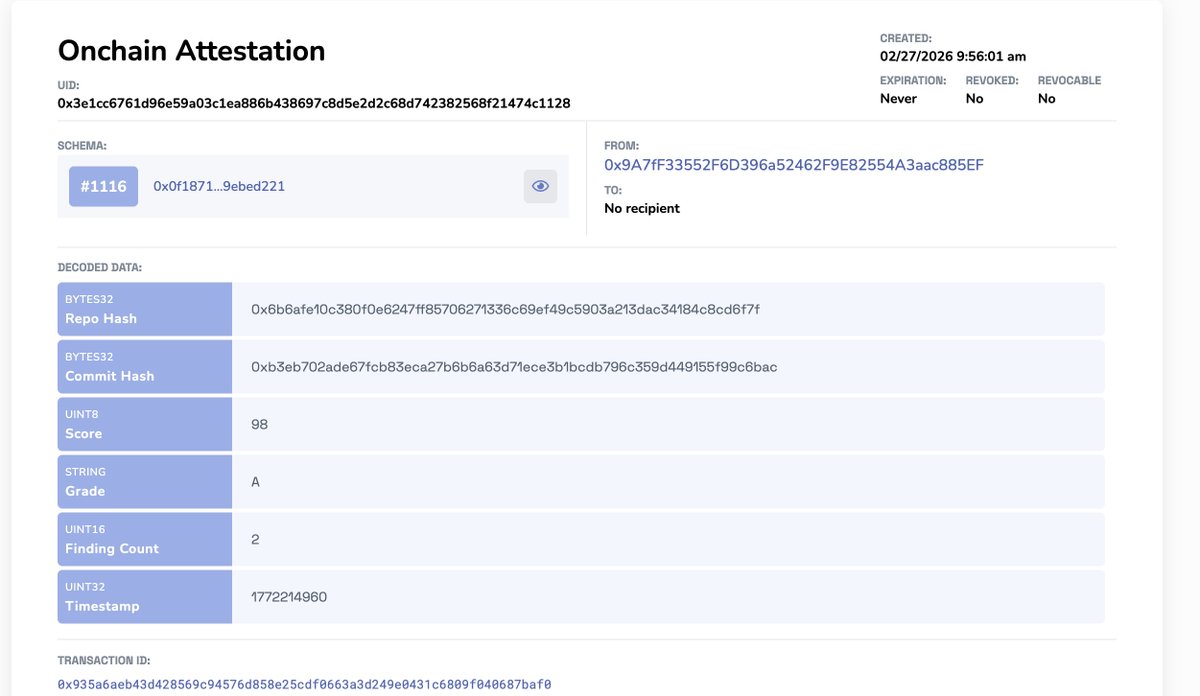
We just completed out first on-chain security attestation from Carapace on Base.
Every code scan now produces a verifiable, tamper-proof attestation via EAS — score, grade, and finding count, all on-chain. No PII, just cryptographic proof.
Check it out:
https://t.co/LjS7ziKfWx
We are building for a world where agents hire other agents.
Carapace is one of the first security scanner that can actually get paid for its work. When an AI agent sends code, pays over x402, gets back a full scan with fixes. The whole transaction lives on Base.
While most people are building agents that do cool demos. We are giving them infrastructure to actually trust each other. An agent shouldn't deploy code it can't verify. Now it doesn't have to.
We've been thinking about why devs ignore security tools. It's not that they don't care. It's that you get a report with 200 findings and zero help fixing any of them.
So you close the tab and move on. That's a broken experience, so we made something that finds the problem and actually fixes it for you.
Run it locally, hook it into your PRs. The point is the code that ships is actually clean.
V3 is where this stops being “security tooling” and starts being something else.
Legacy systems won’t be patched. They’ll be re-generated. The engine won’t just scan files but it will understand why the system exists, the constraints it operates under, and the architecture it’s supposed to respect. Then it will produce a stronger, modern version of the same system without losing intent.
We’re pushing this sooner than you think and imo it's going to be a game changer.
Most breaches don’t happen from some genius hacker breaking your crypto.
They happen because someone left the window open.
That’s what this is for.
Don’t worry, we’re not barging into your app and auto-installing middleware like an overconfident intern.
These are all suggestion-only! You stay in control.
10 checks live today. Run it.
Most scanners look for bad code.
Harden looks for the stuff you never added in the first place.
No rate limits on login?
No CSRF protection?
No security headers?
Strict mode off?
It catches the “you forgot to lock the door” problems.
One of the utilities of $cara is simple. Holders can use @carapacesec_ for free. No subscriptions, no credits, no hidden token games.
Just hold the token and run your scans. As per non-holders, you pay per scan through x402.
We just added more security features, you can check them out on our https://t.co/Dt1IXX9OIF
Insecure code in - Secure Code out
Here's a demo.
We will be launching this as a VS Code plugin soon , so you can directly use it in Code Editor.
Carapace Security is registered as an onchain agent through ERC-8004, so it has its own identity and history.
You can see what it’s done over time. It’s not just some black-box API.
And if you’re building AI agents, they can call $cara directly and pay per scan using x402.
No account setup, no API keys. Just make the request, pay for the scan, get the result back.
An agent calls our API. We respond with “402, payment required.”
It sends two cents in USDC on Base. The payment confirms on-chain. We run the scan and send the results back.
We’re building this in public, with x402 for payments, ERC-8004 for identity, and a VS Code extension already live.
It’s not perfect yet, but it works, and it’s real. 😄