This week let’s look at Active Directory domain permissions which are configured on the domain root and apply to the domain. There are many different type of concerning permissions, but let’s look at the most egregious.
Directory Changes & Directory Changes All – provides the ability to pull password hashes for users and computers (aka DCsync permissions).
Change Owner – provides the ability to set the owner on the domain root and the owner has the ability to set permissions.
Change Permission – provides the ability to set permissions on the domain root.
Full Control – provides the ability to control any type of object in the domain.
Full Control on Users and/or Computers – provides the ability to control the object type.
I wrote a PowerShell script leveraging the Active Directory PowerShell module that can help identify these permissions on the domain root: https://t.co/k1TS2GDgWv
For more on Active Directory permissions:
https://t.co/TgMpFORi6t
https://t.co/vLp3BunQjK
For more on DCSync: https://t.co/RQh4NnBq5c
Reference Article:
https://t.co/P4iSOwouoo
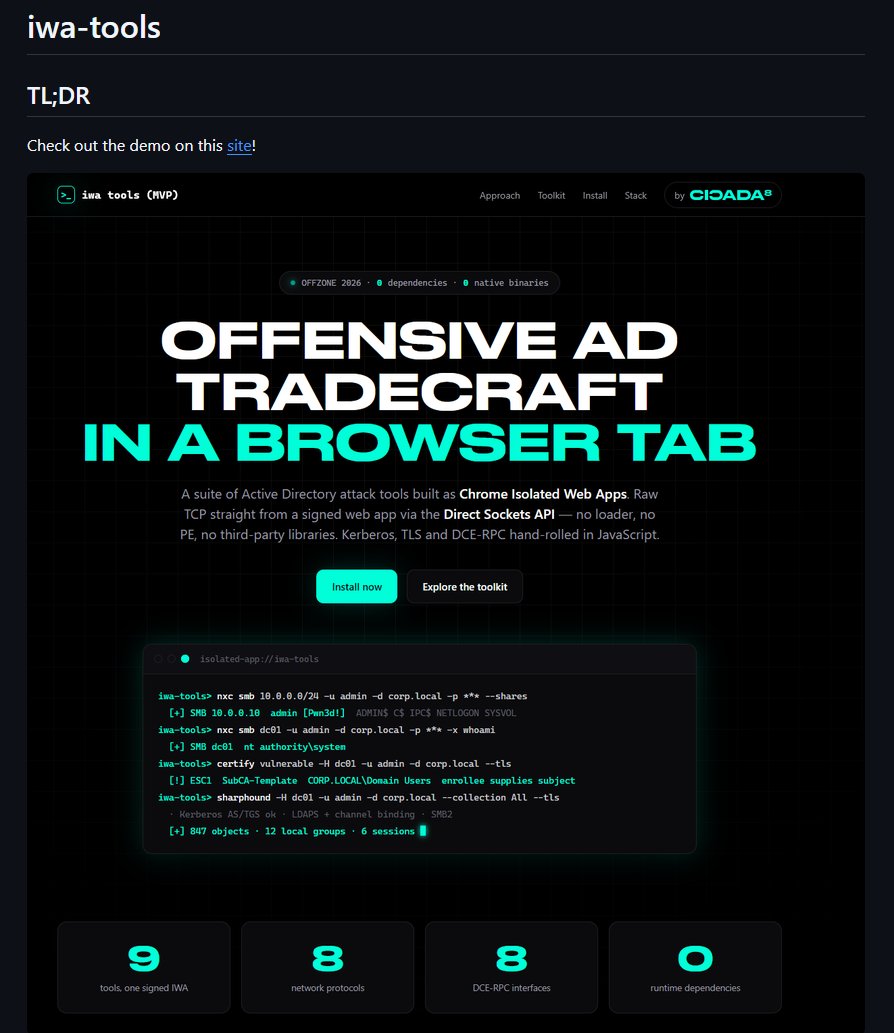
Hi everyone! I'd like to share with you the research of my colleague Vyacheslav Tsepennikov, who successfully ported numerous offensive tools into the browser! With iwa-tools, you can run all pentest tools from Chrome!
Check it out:
https://t.co/L8FodDuimP
https://t.co/qsXx0hiWUh
DutchOven - a deliberately small Windows red-team primitive that places explicit executable paths behind a deterministic network gate.
During each period, matching applications are blocked for a bounded interval and allowed to pass for the remainder
https://t.co/0OGOMlgPIC
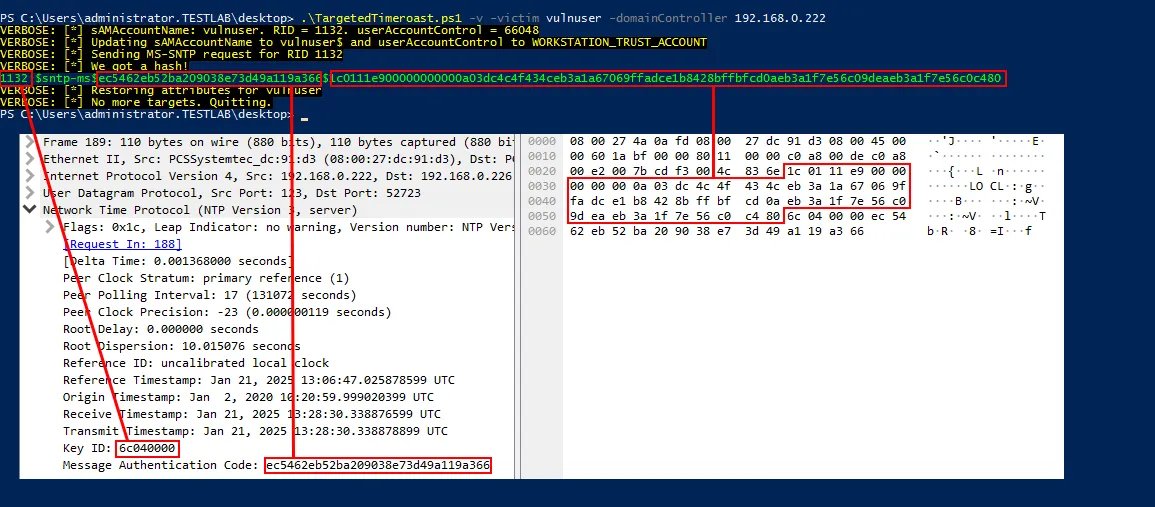
Timeroasting can be used to extract user hashes and it's stealtier than DCSync or NTDS shadow copies. Defenders should start monitoring this activity.
Learn how: https://t.co/JmjJnDvZc3
@three_cube@_aircorridor@DI0256#DFIR#BlueTeam#redteam
Antra is a desktop app that turns Spotify, Apple Music, and other streaming links into a local FLAC/ALAC/AAC/MP3 library with full tags, artwork, and lyrics.
Explore it here:
https://t.co/6FwMTZr4hc
Extracting and analyzing Windows service configurations and ACLs.
A tool by Panagiotis Chartas (@t3l3machus)
Source: https://t.co/V2hqVvVvat
#redteam#blueteam
Entra Connect v2.6.79.0 was just released and contains undisclosed security fixes and @Microsoft recommends to update fast. On the bright side, it will finally support FIDO2 based authentication!
The cat’s finally out of the bag! 🐈
Proud to announce that my book, The (Un)Natural History of Malware, is now available on the @nostarch website! 📖
https://t.co/AO7XL0jPBI
We've documented a new EDR-bypassing process injection technique from @z3ro2504 & Max Hirschberger on the @sensepost blog. Link to post and code in the replies.
LDAP Ping as a blind spot in AD discovery
Researchers from (@HuntressLabs, @4ndr3w6S) showed that using ".LDAP Ping" (also called ".cLDAP") to enumerate Active Directory usernames leaves no trace in Windows audit logs. Requests are handled by ".netlogon.dll" instead of ".ntdsa.dll", so ".Event 1644" is never triggered, making detections relying on traditional LDAP logging ineffective. However, the traffic is still visible on the network level ("UDP/389", WFP traces).
This pre‑authentication technique allows attackers with anonymous access to obtain a list of valid AD usernames, forming a base for further authenticated reconnaissance via tools like ".BloodHound" or ".PowerView". The attack requires no credentials and yields confirmed account names for subsequent brute‑force or privilege mapping stages.
Article: https://t.co/X7oxxUn1dG
#dbugs_attacks
MSF's Railgun was massively underrated but incredibly powerful. Resolve and call an API without needing to alloc and run a whole BOF or DLL. I hope to get this implemented nicely in CrystalC2 at some point.
Speeding up AD Pentests with ADScan and ADPulse
Active Directory pentesting often starts with the same repetitive checks, but ADScan and ADPulse can help you automate them.
The pentest does not always end with full domain compromise. Success is not measured by whether you obtain Domain Admin privileges, but by how well you identify and communicate risks that could impact the organization. Sometimes the most critical findings involve exposed data, weak configurations, or small mistakes that could later be chained into larger attacks.
https://t.co/r6qq1YRvOP
@three_cube@_aircorridor
#pentesting #redteam
Releasing DCOMIllusionist as part of our talk on DCOM at @x33fcon with @k3vinTell. It's a remote in memory fileless lateral movement technique based on some research of @tiraniddo
https://t.co/XLljazKmnH
EntraOps. personal research project to demonstrate capabilities for automated management of a Microsoft Entra ID tenant at scale using a DevOps approach, by @Thomas_Live
https://t.co/A6WfT6Lo4o
I asked Claude to build my daughter an app that plugs into our piano, can read live key strokes, can show her sheet notes and key view and ends with a Guitar Hero style game. All while giving progressively harder songs. Today she’s using It and crushing It.