We’re looking for a few early design partners.
If you’re building or deploying AI agents in production — or you’re a startup building agent-based products — I’d like to hear from you.
We’re building Cerbere-AG, a runtime security and observability layer for AI agents.
We’re looking for teams willing to:
→ integrate Cerbere-AG with an agent
→ test it in a real workflow
→ tell us what works and what doesn’t
→ challenge our security controls with real use cases
No polished sales demo. We’re looking for honest technical feedback that can shape the product.
If you’re deploying AI agents and want to participate, reply here or DM me.
An agent, a tool, a single execution limit.
Each call is verified, recorded and attributable.
No agent goes unnoticed.
We connected Cerbère-AG on a real AI agent in production.
The SDK is located between the agent and its tools - no modelling change is required.
(What we learned in prod: when the collector is unreachable, the default must be fail-closed, not fail-open.
A guardrail that lets everything through when it's down isn't a guardrail)
Github ⭐️: https://t.co/PJpYuMZPr3
Try cerbereag: https://t.co/H9PpnkOzjc
Your AI agent is in production. What happens after you give it access?
Files. Tools. APIs. Data. Tokens. Actions.
Cerbère-AG (@CerbereAg) is a runtime layer to observe, detect, enforce and audit what your agents do — before the tool call fires.
3 layers at the execution boundary:
1. Rules / Regex
2. ML classifier
3. LLM judge
→ ALLOW / BLOCK
No model changes required. No agent passes unseen.
🐕 https://t.co/H9PpnkOzjc
⭐️ https://t.co/PJpYuMZPr3
Your AI agent is in production. What happens after you give it access?
Files. Tools. APIs. Data. Tokens. Actions.
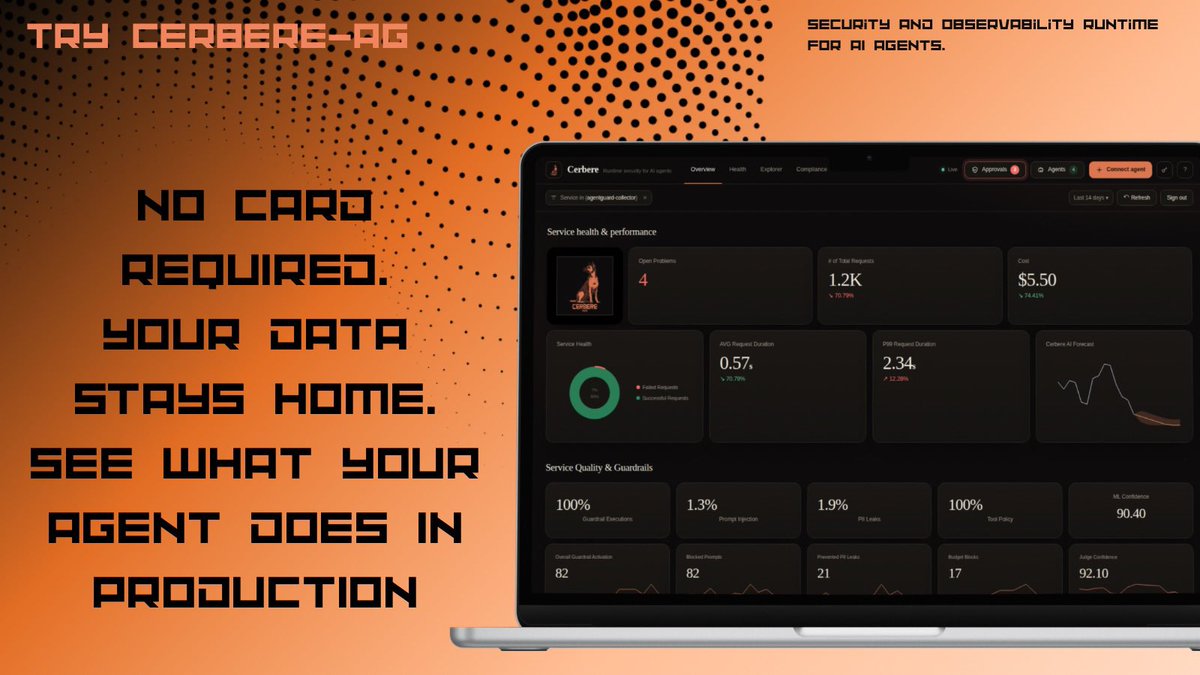
Cerbere-AG gives you a runtime layer to observe, detect, enforce and audit what your agents do in production.
No card required. Your data stays home.
Try it → https://t.co/H9PpnkO1tE
pip install cerbereag
Today, trying to exfiltrate a file through an AI agent by simply saying “ignore your instructions” is becoming less effective. Agents can have filters and regex rules that detect obvious attacks.
But the real problem is deeper: an agent may not be able to distinguish between a legitimate action and a dangerous one.
That’s why I created Cerbere-AG @CerbereAg.
Cerbere-AG is a security and observability runtime for companies deploying AI agents in production and sensitive environments.
If an agent tries to move a sensitive document from one folder or server to another, the action can be detected, evaluated, and require approval before execution.
No approval, no action.
The human remains in control.