Cerbos PDP v0.57.0 is out 🚀
Query plans now keep standalone has() checks, so your database applies the same test Cerbos does, and large policy stores keep serving requests during full reloads.
Details: https://t.co/vNiYeitGlg
#authorization
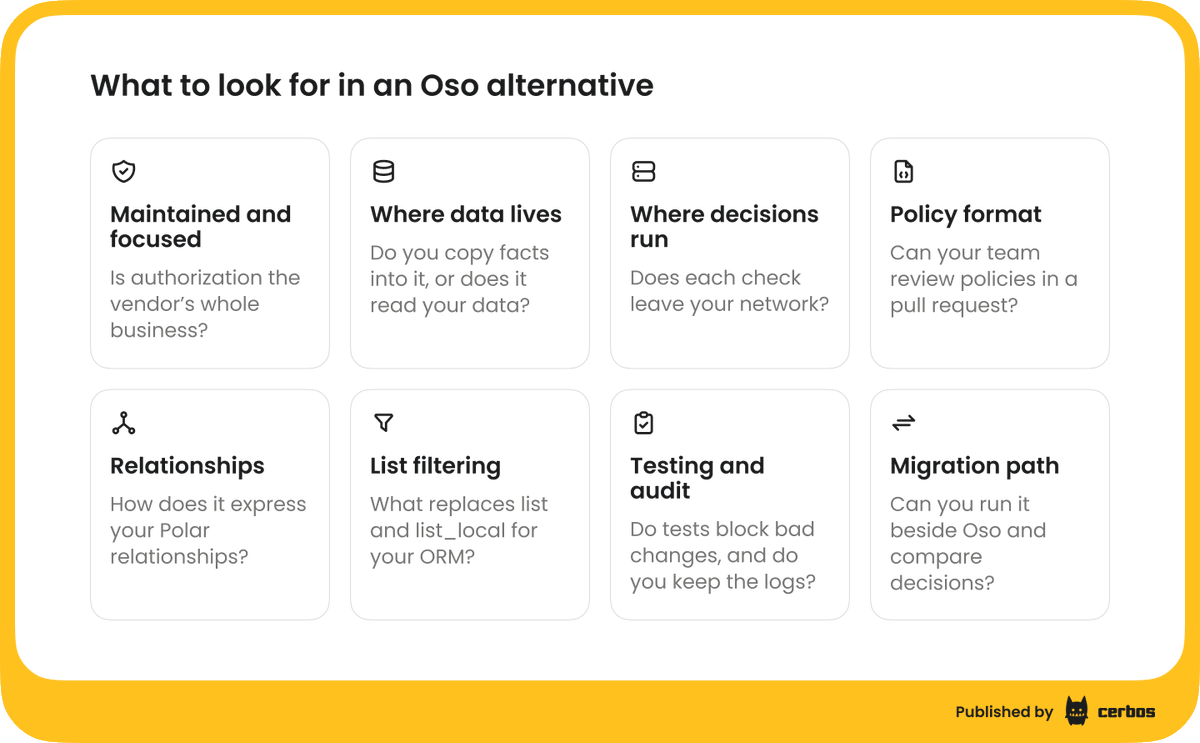
Weighing #Cerbos after Tiny acquired #Oso Cloud? We wrote up how the two compare.
Both handle roles, attributes and relationships, so most #Polar rules carry over. The real change is where your data lives and where decisions run.
👉 https://t.co/BX82hJ8zck
#authorization#abac
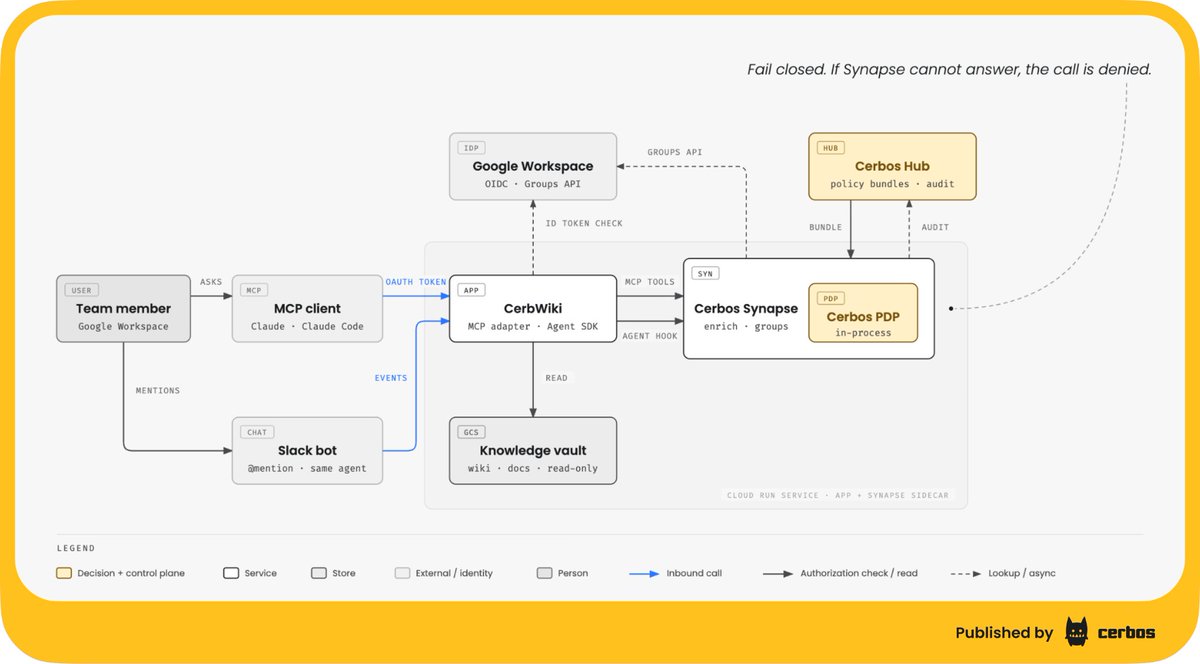
An internal AI agent can read files, search the web and query company data with nobody approving each step.
We wrote up how we check every step with #Cerbos, plus the policy and audit design to reuse on your own #MCP server.
🗒️ https://t.co/T2vuNHxYw0
#authorization
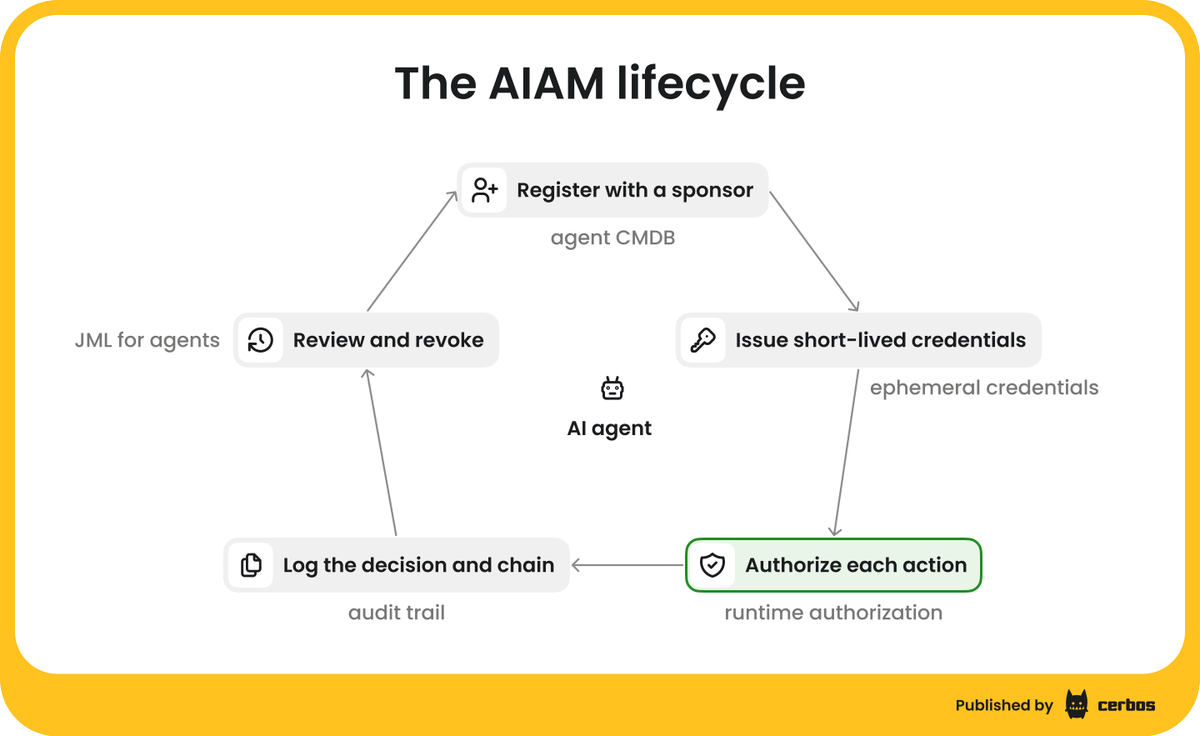
78% of organizations have no documented policy for creating or removing #AI identities.
We wrote up how to fix that: an owner for every agent, credentials that expire, and an #authorization check on every action it takes.
🛡️👉 https://t.co/IFMnc2kIOe
#IAM#AIAM
Cerbos Newsletter October 2026 📢 https://t.co/KWcJqgeF3K
✅Who owns #authorization in a large org
✅A #ZeroTrust stack, layer by layer
✅Why #audit trails break between #AIAgents
✅Cerbos PDP v0.56.0
Subscribe: https://t.co/C2oh2vXQk6
Enterprise #IAM is 5 domains. #SSO, #IGA, #PAM and machine identity get the budget. The 5th, #authorization, what an identity may do per request, is what most programs leave hardcoded in each app.
Guide to all 5, vendors in each, what to get first: https://t.co/grlO8VeE5h
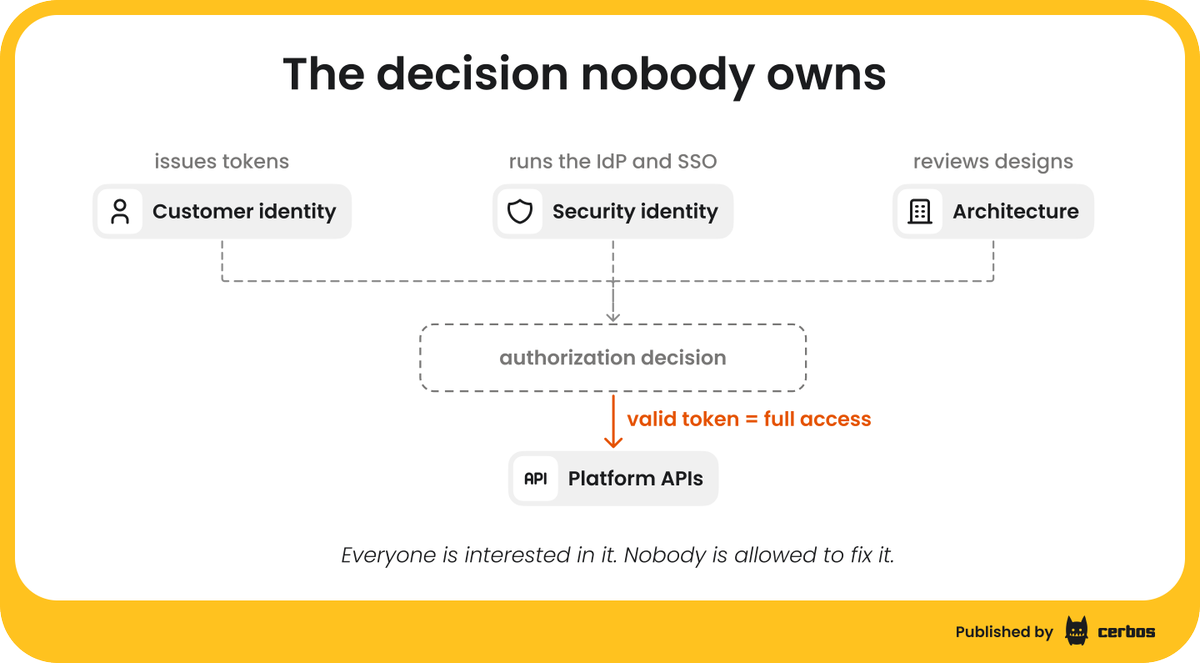
Ask who owns #authorization at a company with 500 engineers and you get 3 teams holding a piece each, and no owner.
We wrote up how to split ownership by layer, with a table to bring to the meeting where those teams argue about it.
✍️💡 https://t.co/PtZIvIZMhk
#IAM
Cerbos PDP v0.56.0 is out 🚀
Store reloads can now confirm new policies have compiled and are being served, and a new metric tracks the last successful rule table refresh.
We wrote up every change: https://t.co/0LMSh4PfiI
#authorization#CICD
@viragents We are! +1 to @karthiknish on the boundary sitting outside the model. The other half is what the rule sees: not only which agent is calling but who it's acting for, or every user reaches the tool looking identical. We're an authz platform (Cerbos), that per-call check is our job.
@Skuiggly@br11k_dev@justinstorre Hi! The math isn't the hard part. Getting the rules out of app code is. They start as if statements, then a customer wants custom roles, and Nikolay's 6 engineers x 6 months is the bill. Roles + ownership + repo membership is policy engine territory. We handle that here at Cerbos
@iKarthikNataraj Hi there! It feels repetitive because it's 3 problems not 1: authentication, multi-tenant authz, entitlements. Only the middle needs your object model, which is why only that one has no drop-in answer. We're that layer at Cerbos, policies in YAML outside your app 😊
@harleyfoote_@ellishlomo Hi there! Both, & the intersection is what decides. The agent's own principal caps what it can ever do, the user context caps what this task needed, so delegation can only narrow. We do that at Cerbos.
Our CPO @alexolivier will be at @WeAreDevs 🔊on why authorization spread across many services breaks at scale
Come if your permission checks live in more than one place. You'll leave with the warning signs and a checklist to fix them 🔒
https://t.co/UwEJhWTk9r
#WeAreDevelopers
The Cerbos PDP dashboard is now on @grafana 🎉
We rebuilt it on the #Prometheus metrics the PDP has always exposed.
Import ID 25769 and you get per-instance health, Hub connectivity, policy count, latency percentiles and restart annotations.
https://t.co/fsW59UamW5
ACES moved #authorization for ACES Meet onto Cerbos and wrote up how they did it step by step.
Dual writes, a shadow run against production traffic, then cutover. Useful if you're planning the same move off in-app permission checks. Thank you @nori_nori_8! #
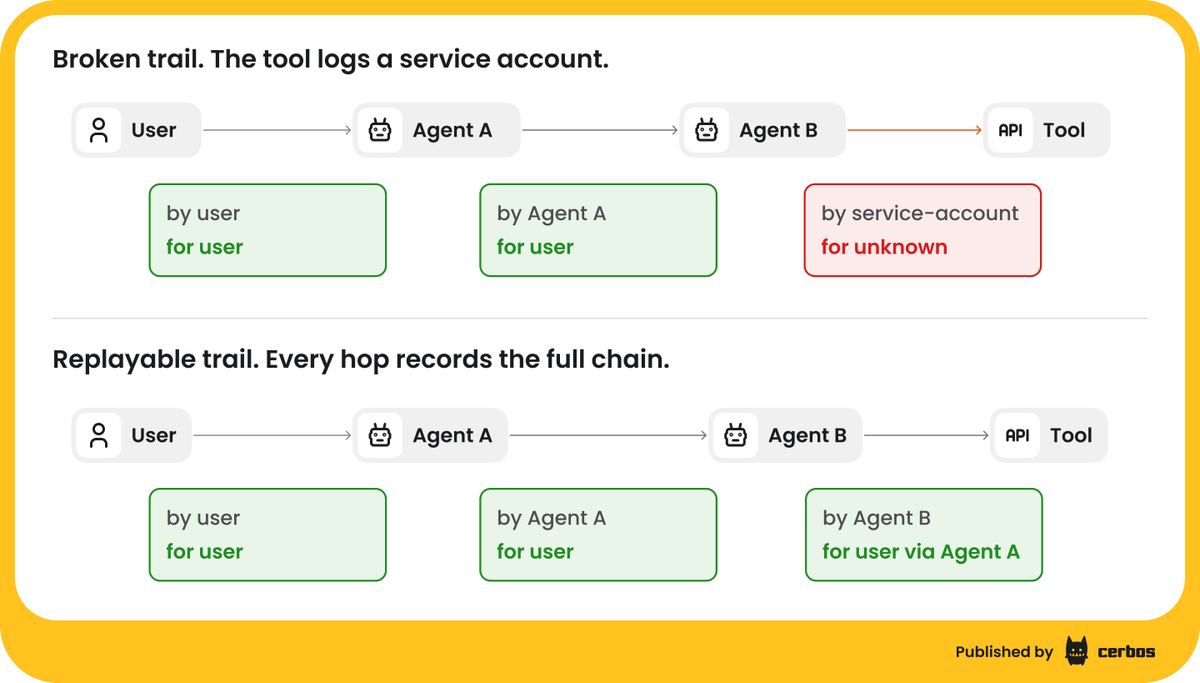
An #agent exports a record it shouldn't have.
The logs say a service account. Not the user, not the agent, not the sub-agent.
We wrote up why the trail goes dark at the handoff and the 4 things every hop has to log so it doesn't: 🛡️ https://t.co/VbOqX0gbiJ
#authorization#ai
Authorization bugs do more than leak data. At scale they become outages and stuck workflows.
Our CPO @alexolivier covers catching them early at #WeAreDevelopers World Congress, Sept 24. You'll leave with a checklist for making #authorization predictable.
https://t.co/UwEJhWTk9r
Same AI agent question at #IdentityWeekAmerica, whatever the badge said. Who's asking & what can it touch?
@alexolivier wrote up panel takeaways, who should own an agent, and which actions get a spend limit, a human in the loop, or a hard approval
🔗🤖 https://t.co/HZqj0a7XRC