Your End-To-End Security Partner.
Manual Audits, Formal Verification, and Protocol Design Review.
Trusted by Aave, Uniswap, Lido, EigenLayer, Solana and more.
Writing formal specifications has always been the bottleneck in formal verification.
Today we're launching AutoProver, an agentic formal verification system that reads your code, generates specifications, and verifies them. 🧵
Certora co-founder @SagivMooly is heading to @EFDevcon 8 to share insights from our work on @aave V4, exploring how AI agents and formal verification can help developers build safer smart contracts.
📅 Thu, Nov 5 | 12:30–12:55
📍 Lotus Stage 2
See you soon, Mumbai! 🇮🇳
❌🪲 @SagivMooly of @Certora is joining Devcon 8 for “Bug-Free Solidity Coding Agents,” digging into how verification and program analysis can help make AI-generated smart contracts safer.
Catch his talk on the Security stage.
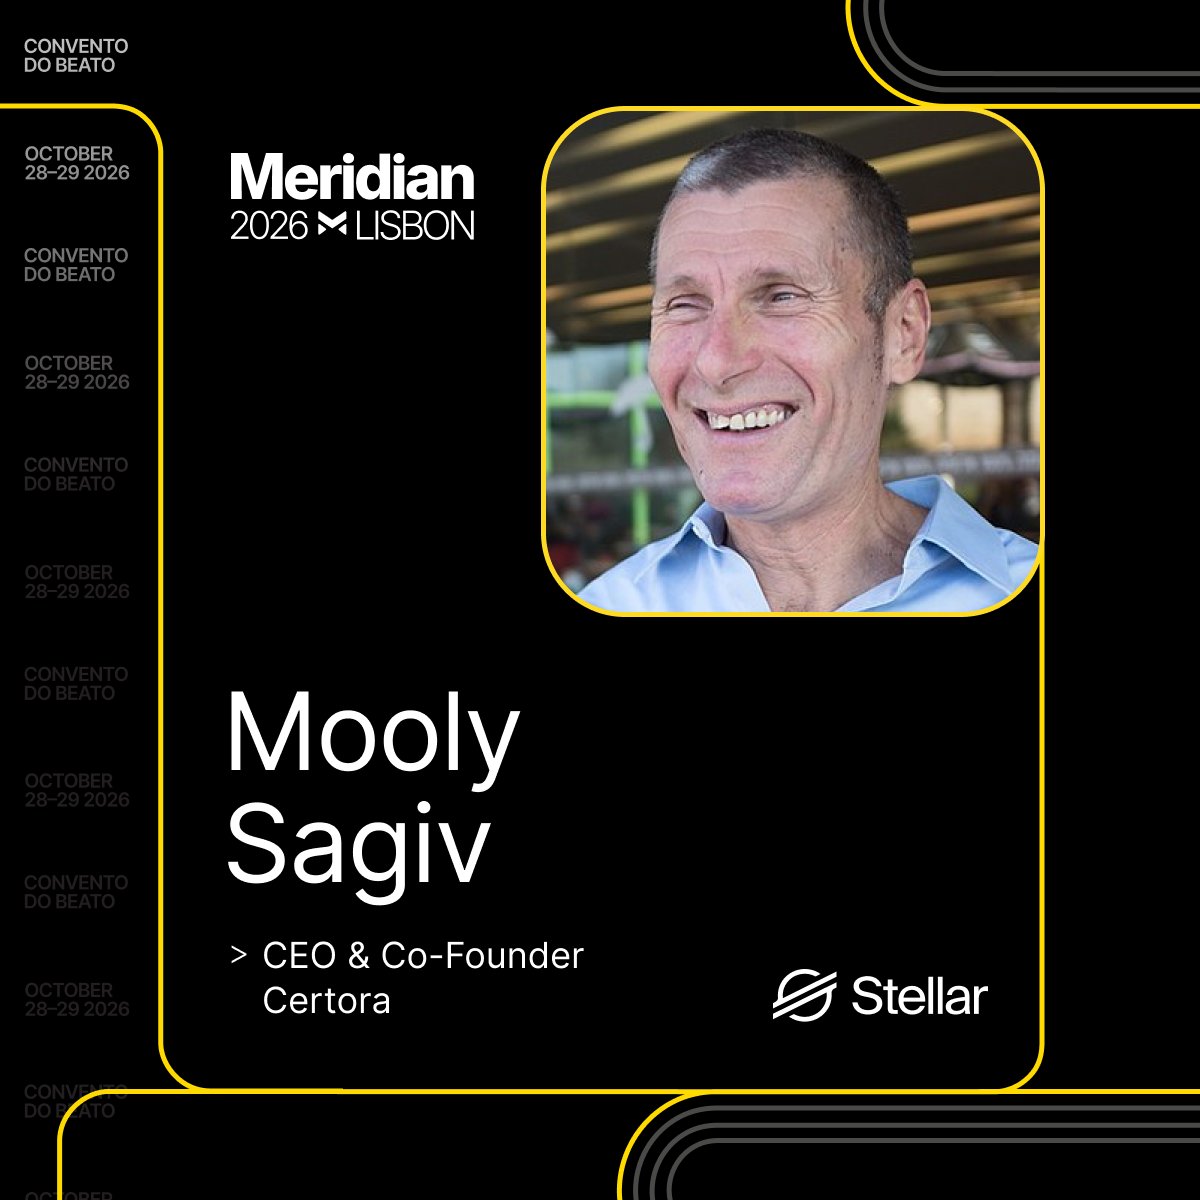
@SagivMooly is returning to @StellarOrg Meridian!
Join him on October 28 as he shares insights into how Certora's using agents to secure Stellar against agents.
We’d love to see you there ⬇️
https://t.co/o7Rfi31VcX
Going from seconds to milliseconds in finality is an impressive engineering achievement.
Congrats to the @anza_xyz and @solana teams on this major upgrade!
Alpenglow is now live on Solana mainnet. ⛰️
Finality just went from ~12.8 seconds to ~150ms.
The biggest consensus upgrade in Solana’s history, built by @anza_xyz.
excited to see more and more traditional finance companies moving to blockchain. @CantonNetwork is one of the networks getting a lot of interest
sharing some insights from our experience securing DAML smart contracts on Canton
Daml takes a different approach to smart contracts. What does that mean for security?
We share insights from our @CantonNetwork audits: authorization checks, contract references, and how locks and accounting can break across workflows.
🔗 Learn more:
https://t.co/19tge2nWkn
Can formally verified code still have bugs?
The answer is yes. A proof can pass, and the system can still be vulnerable.
Our latest article explores four ways formally verified code can still go wrong, with real-world examples and how to catch them before deployment.
https://t.co/bTwkeuE1JM
@aave V4 was built with a strong focus on security, with formal verification playing an important role in that process.
Proud of our team's work and excited to share some of it at @summit_defi in Mumbai 🫡
@AliceAndB0b · DSS 2026
“Proving the Spoke: Formal Verification of Aave V4’s Hub-and-Spoke Architecture”
Explore the talk and add it to your agenda:
https://t.co/QtoUJifMUK
Tickets: https://t.co/RTbPxGH7zF
Kudos to the @Certora team for the great research and responsible disclosure! The write-up is such an interesting read. It’s an honor to collaborate with such talented security researchers. Thanks @tpiliposian for sharing the behind-the-scenes story!
Fixed in gnark v0.16.4 (GHSA-7fx8-hmgc-82jp). Thanks to the gnark team at @Consensys and @_SEAL_Org for fast disclosure coordination.
Full write-up by Lior Oppenheim and Giuseppe Cocomazzi:
https://t.co/MQsBp71Ugc
In a ZK circuit, a hint is a value computed outside the circuit. It’s only as safe as the constraints placed on it. We found a case in gnark where one was missing, and it allowed ECDSA signature forgery. 🧵
Nothing asserted that R was on the curve. In ECDSA verification, that let a malicious prover steer the x-coordinate the signature is checked against, and pass verification under any public key. In-circuit EIP-7951 P-256 verification was affected.
On September 24, forged zero-knowledge proofs took ~$1.92M in USDC from Payy's bridge.
The fix for the Barretenberg verifier bug Payy blames had been in a public release for 73 days.
Find out why Payy was still exposed ⬇️
https://t.co/AH5HeGGsrk
Bringing Bitcoin into onchain financial markets requires strong security foundations, especially at this scale.
Proud to have formally verified Hashi’s smart contracts ahead of its mainnet launch. 🫡
Just in from the main stage at Sui Basecamp:
👉 Hashi mainnet starts rolling out this month, with $500M+ in capital already committed.
👉 @Anchorage joins as a launch partner, bringing qualified custody and stablecoin liquidity.
Learn more ⤵️
https://t.co/TJV8LEHEOf
Building on @StellarOrg comes with a different set of security assumptions.
Authorization, storage, cross-contract calls, native assets, cross-chain messaging. Soroban handles each differently from the EVM, and those differences matter when designing secure applications.
Based on our work across the Stellar ecosystem, we break down what builders should know about securing smart contracts on Soroban.
Read the full article by @tpiliposian:
https://t.co/2fFNsPUO2A