I've been watching the California vs. Washington AI debate closely, and I think it's becoming about much more than AI.
California wants to move aggressively on AI oversight. The federal government wants a national AI policy and not a patchwork of state laws.
Meanwhile, many of the same AI CEOs building these technologies are now publicly asking for more caution and stronger safeguards, which we'll be discussing in an upcoming MSP Zone episode.
It's one of the reasons we added AI governance controls to UCS 4.0. AI is already embedded in managed services operations. The question is no longer whether we adopt AI. It's whether we adopt it responsibly.
What interests me most is the federalism question underneath all of this:
How much authority should states have over technologies that operate nationally and globally?
I can appreciate both sides of the argument. But one thing seems certain: the outcome of this debate will influence far more than AI regulation.
It will influence how America governs innovation itself.
#AI #MSP #Cybersecurity #AIGovernance #UCS40 #TechnologyPolicy #Federalism #MSPAlliance
My situation at the moment:
“My mind is a raging torrent, flooded with rivulets of thought cascading into a waterfall of creative alternatives.”
Hedley Lamarr
AI is moving fast. Governance isn't.
What client data should never go into AI tools? Do you need an AI acceptable-use policy? How should MSPs govern AI without slowing innovation?
Join us for MSPAlliance Office Hours: AI Governance & Practical Adoption.
Register: https://t.co/iKXuHGSk5x
Bring your questions. We'll discuss real-world MSP use cases, governance, data protection, and practical adoption strategies.
#MSP #AI #AIGovernance #CyberVerify
In response to the Department of War's suspension of CMMC Phase 2, MSPAlliance has issued the following statement:
MSPAlliance supports strong cybersecurity requirements for organizations handling government information. Compliance programs, however, must be practical, scalable, operationally sustainable, and accessible to organizations of all sizes. The industry should favor continuous compliance, objective validation, and measurable operational maturity over costly, bureaucratic, point-in-time audit exercises that discourage participation and reduce innovation.
https://t.co/CxvYbh8qmr
More on this topic soon to follow...
Cyber insurance is getting harder—not easier—for MSPs and their clients.
Join MSPAlliance Office Hours this month as we break down:
• What coverage MSPs actually need
• Why claims get denied
• How MSP frameworks like Cyber Verify impact premiums
• Where liability really sits
And most importantly—how to get ahead of it.
We’ll share practical guidance MSPs can use right now to protect their business and their clients.
Register here: https://t.co/1qgCSCuPdr
🚀 Big win this week at MSPAlliance!
Three of our MSP members successfully issued SOC 2 reports this week using Cyber Verify — demonstrating once again how influential managed service providers are in compliance.
Think MSPs don’t have a significant role to play in compliance?
Think again.
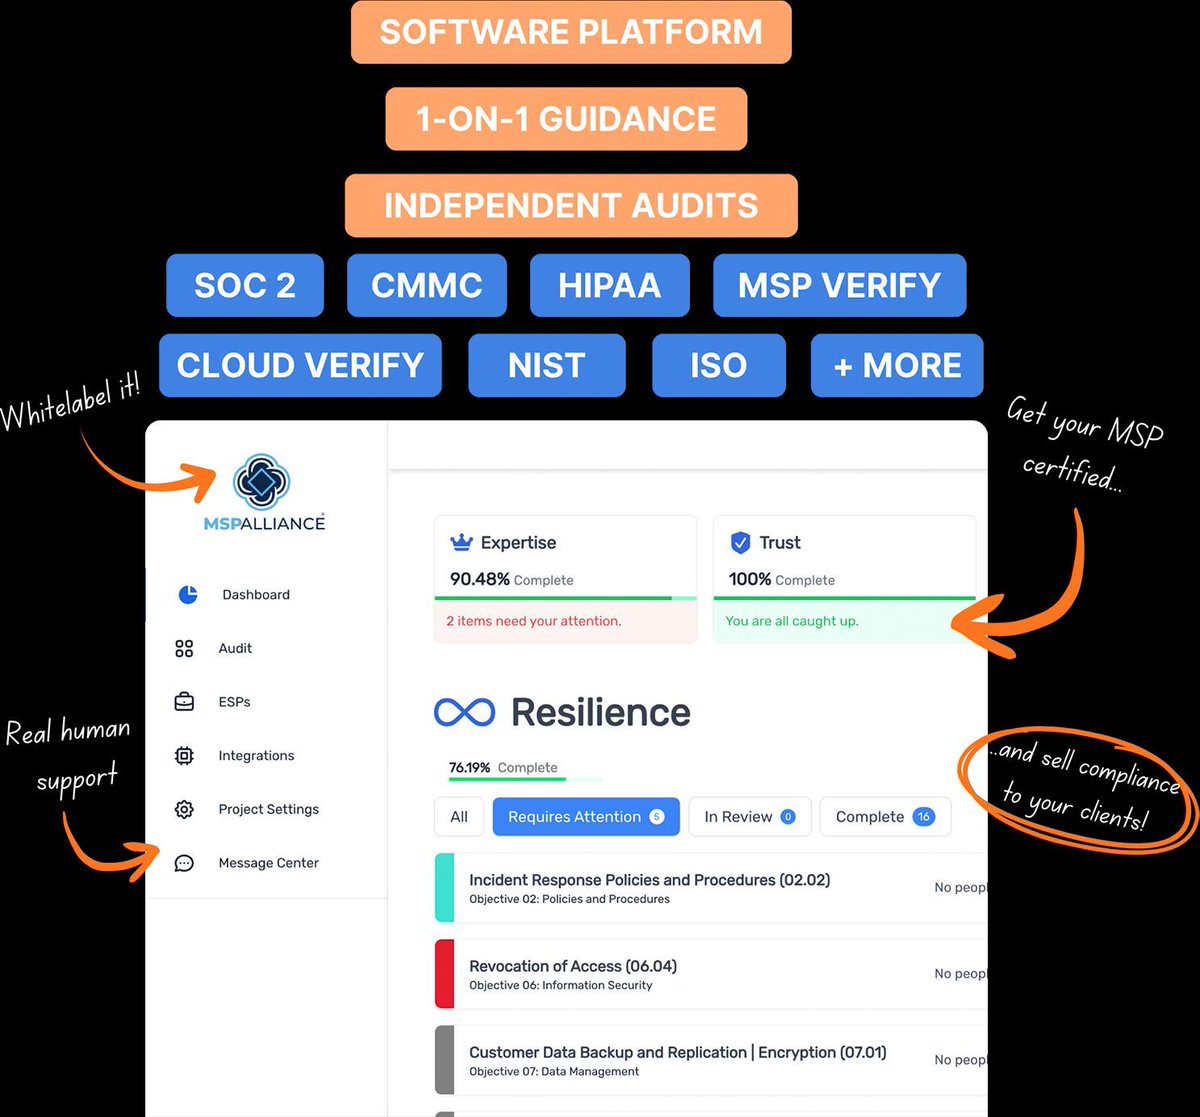
Whether you’re just starting your compliance journey or looking to level up your practice, MSPAlliance is here to help you become compliant, spin up your compliance offerings, build client trust, and supercharge your managed services business.
Ready to get compliant and grow faster?
📩 Contact https://t.co/BkeskyOLTd today and let’s make it happen!
#MSP #SOC2 #Compliance #ManagedServices #MSPAlliance
Friendly reminder for MSPs working through compliance:
MSPAlliance helps MSPs get to SOC 2, CMMC, and other certification goals—but the important part is how. We built this to be MSP-first, with an MSP-friendly experience (not generic enterprise templates).
If compliance feels like a square peg / round hole, there’s a better way.
https://t.co/RMZuexLFl7
Before you use AI in your MSP practice, pause for a second:
Imagine the AI is a person.
Would you feel comfortable giving them that data?
Would your instructions make sense to them?
Would you trust them to act on it?
If the answer is no, don’t use AI.
AI doesn’t remove responsibility—it amplifies it.
SOC 2 isn’t optional for MSPs anymore.
Not because of regulation—because of clients.
They’re not asking “Can you manage IT?”
They’re asking “Can you prove you’re secure?”
Problem is, SOC 2 was never built for MSPs:
❌ Expensive
❌ Time-consuming
❌ Enterprise-focused
Cyber Verify changes that.
✅ Built for MSP operations
✅ Continuous compliance (not audit panic)
✅ Maps SOC 2, ISO, CMMC
✅ Turns compliance into a revenue stream
SOC 2 = proof.
MSPs that prove it… win.
https://t.co/LFlM1wbTbN
“Most MSPs are stuck in reactive mode” is a catchy line, but it’s not entirely accurate.
MSPs, by definition, are proactive.
If you’re purely reacting, you’re not delivering managed services—you’re doing break/fix with a subscription.
That distinction matters. A lot.
Just picked up my brand new Model Y in Quicksilver. Spent 5 minutes customizing everything, entered my home address, pressed full self driving, and then the magic happened.
My car drove off the Tesla lot and went 80 miles to my home. What an amazing experience FSD is. Awesome job @elonmusk and the @Tesla team!