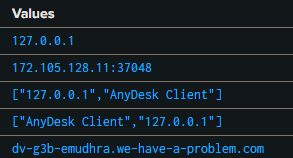
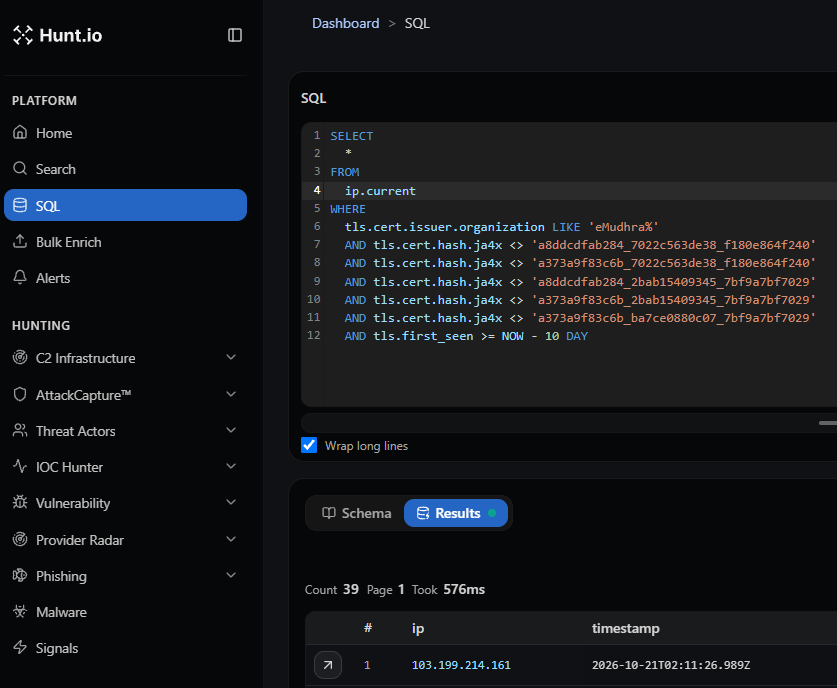
The private keys for the eMudhra CA were compromised yesterday. Here's all the IPs likely hosting fake eMudhra certificates. These were found using JA4X on https://t.co/opSKwMeCEM but you can do the same thing on Censys, Xpanse, Validin, or any other tool running JA4+
We're launching urlscan Labs to bring new and experimental features to our most advanced customers earlier. As part of the launch, we're making three new tools available:
* File uploads for malicious SMS / short messages.
* Multisearch
* Auto-Screenshots
https://t.co/kSorctdBRU
Introducing JA4Scan, the latest addition to JA4+
JA4Scan is available now and built into (or coming soon to) all of the tools you already use including Censys, Palo Alto Networks, Hunt, SecurityScorecard, Modat, Validin, and more.
https://t.co/OqYaV1CK0T
ok I'm genuinely proud of what we've built at https://t.co/N5XL7zFxWf, seriously.
A security team messaged me today to say thanks... They ran one of their domains through it this morning, and found an issue they didn't know was there. Honestly that made my day!! 🥳
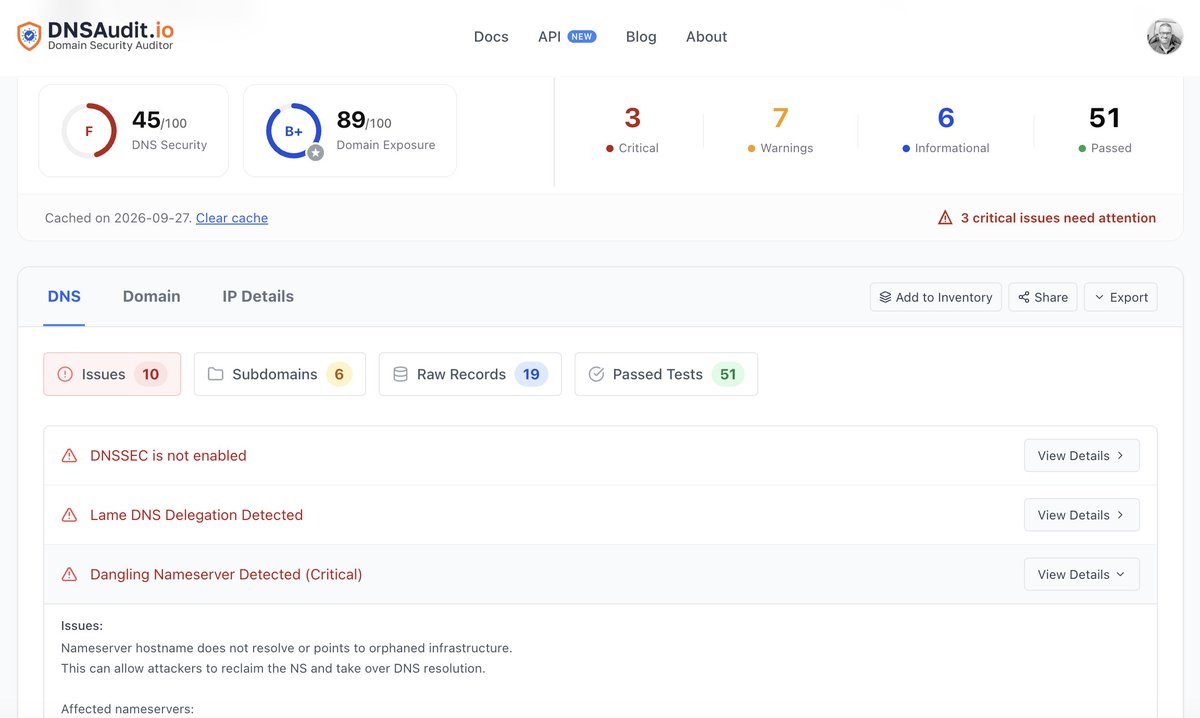
It started as a small tool I built for myself, and now it does what I always wanted: you put in a domain and in about 30 seconds you see what's wrong with its DNS. Dangling records, lame delegation, no DNSSEC, weak SPF/DMARC, missing registrar locks, old subdomains nobody remembers creating
You don't need to install anything or give it access to your zones... it just looks at your domain from the outside, like anyone on the internet can.
The screenshot is from a real scan. A nameserver that stopped answering but is still in the delegation. Nobody notices these until someone else does.
Try it on your own domain, and tell me what it finds: https://t.co/7i64HAHVEB
My blog post on the Iran-backed APT group MuddyWater is out. MuddyWater uses tools from TAG-150, a Malware-as-a-Service platform run by Russian-speaking cybercriminals. In this campaign, an MSI package is distributed through Amadey, installs the Deno-based DinDoor agent and runs it in memory. The agent collects browser passwords, cookies and crypto wallet data, and the final stage of the chain connects to a CastleRAT C2 server.
https://t.co/wtyOoeSRhV
Uh oh, a MikroTik ssh 0-day campaign in the wild - we're keeping an eye on the missing hashes from 82.192.72[.]4 and wil let you all known when they show up on @virustotal 972b474b896f9fac3cd6b5b8476b410b8f39fbedee8a3b0c745d6e3b328d7dcd
6e95f70fdbabb57881b3f5b2c8465d4b17ba901100704efb1278bb3386e6729d
6dca83338d60467b65b7789d4d59754e40a7aaa36f40ea2da57538367ac9b89e
hashes courtesy of @Huntio 🙏