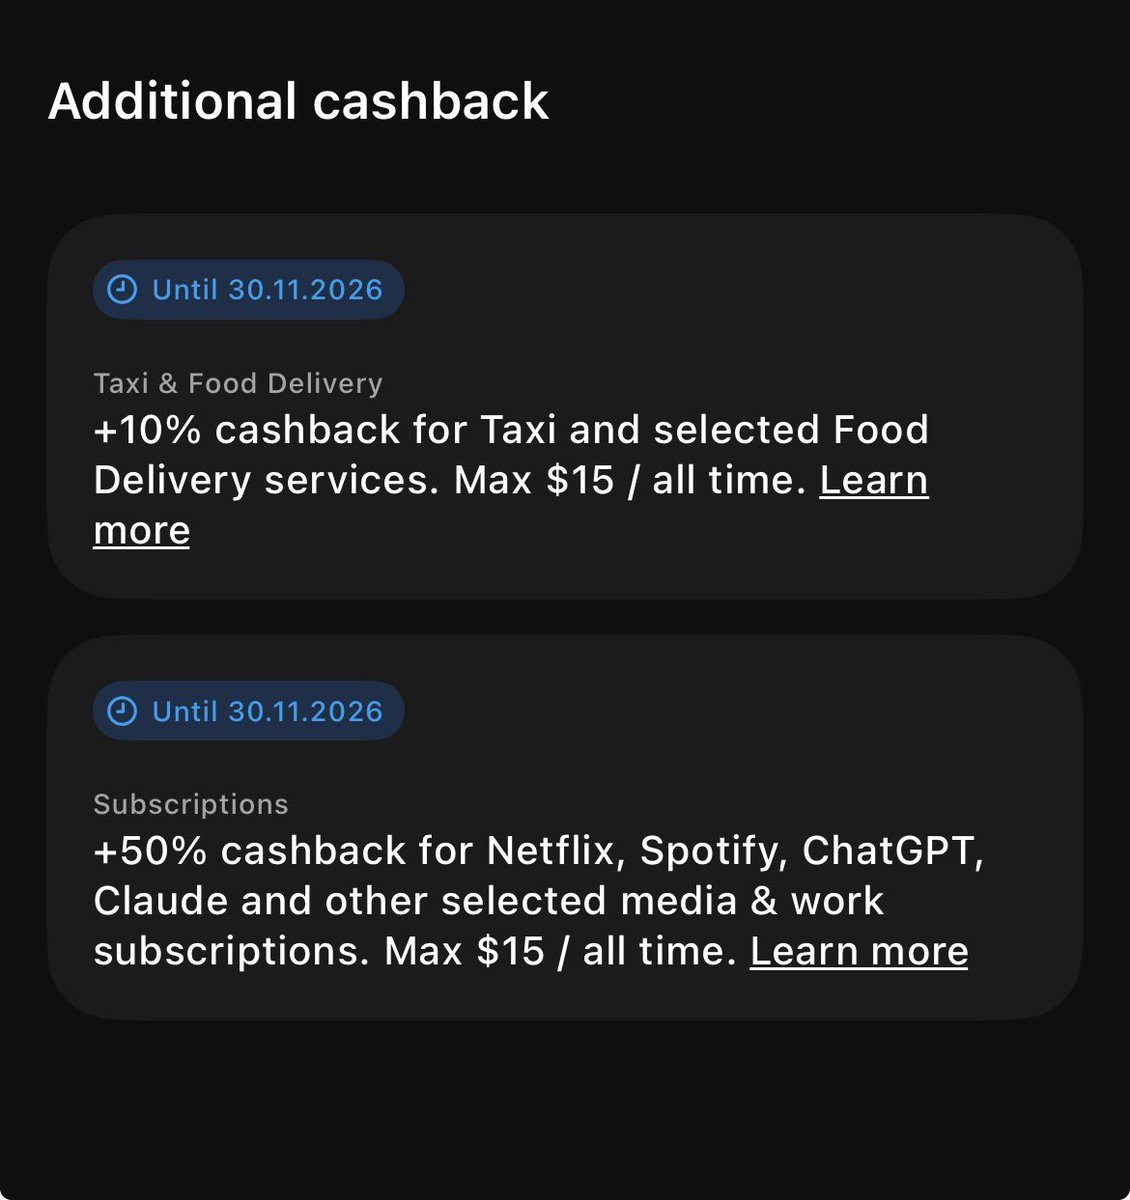
pay with @Tangem pay
half back on the monthly tab
$15 for the whole window
the card spends, the seed stays put!!
Just gave 28 sep – 30 nov
Thanks to @Tangem
💀Authorized reseller gets bought, NDA slapped on the old owners, spy chips go in the wallets, $86M vanishes… & @Ledger just says “limited cases, not our systems”
Supply chain was the weak link the whole time
Trust no one
Stay paranoid
Stay safe
Use code: CIPHER10 🔥- 30% off
What's crazier is the hackers apparently bought the reseller and made them sign a non-disclosure agreement to keep their mouth shut.
So many things wrong here...
Implants reading seeds off a screen? @Ledger
Still waiting on real answers
@Tangem: no seed. no screen. no space for this
Seedless by design
CIPHER10 → 30% off
Receipts: Tangem generates the key on-chip with zero mnemonic displayed by default + sealed card form factor
Update from Ledger Donjon on the CryptoBilis investigation 🔽
@DonjonLedger is investigating Ledger signers sold by CryptoBilis, a reseller in Southeast Asia, that contained an unauthorized hardware implant. Ledger confirmed this on October 10th for one affected user's signer. All confirmed fund losses tied to the incident disclosed on October 9th involve signers sold through CryptoBilis. We have not verified a drain linked to a signer bought elsewhere. CryptoBilis has confirmed it stopped selling Ledger signers while the investigation continues.
Based on the Donjon's analysis of the attack, the implant sits inside the enclosure and reads the data shown on the screen. During setup, the signer displays the 24-word recovery phrase. When the implant detects these screens, its microcontroller decodes the words and transmits them over LTE using a provisioned eSIM. The implant is a separate component. It does not modify the Secure Element or the Ledger operating system, and it does not alter transactions or signatures.
The Donjon will analyze the signers it receives and will share more as the investigation continues.
We have not confirmed the total number of affected users or the total value lost. Figures circulating online come from third parties and Ledger has not fully verified them. If your funds were drained and you have not contacted us, please do so through Ledger Support so we can include your case. We are also reviewing reports of implants in other signers and locations. We will continue to share information as the investigation progresses. Rest assured the Ledger team is going above and beyond to leave no stone unturned to investigate this situation to the strongest possible outcome.
If you bought a Ledger signer from CryptoBilis and have not set it up, do not set it up and contact Ledger Support. If you have set it up, transfer your assets promptly to a new signer with a new recovery phrase. Do not enter or restore any recovery phrase on a signer bought from CryptoBilis. Never enter your recovery phrase into a website, app or form.
If you lost funds or hold a tampered signer, contact Ledger Support at https://t.co/QzukOZdEzq and file a report with local law enforcement. Do not send the signer to anyone before speaking with Ledger Support or local law enforcement. If you lost funds, coordinate with law enforcement before opening the signer. Researchers and others with relevant information can write to [email protected].
If you did not buy from CryptoBilis and want to inspect the inside of your signer, the guide is at https://t.co/Bh9DHQulIv. Use caution and make sure your recovery phrase is backed up first, because opening a signer can damage it.
Ledger will never call you, message you directly, or ask for your 24-word recovery phrase. We will update this post when we verify new information.
@Multi_mike01 Identity makes the responsible party clear; runtime bounds and hybrid oversight reduce the chance that clarity arrives only after irreversible damage. Both layers are needed as agent capabilities keep advancing
Supply-chain risk doesn’t stop at “third party.” The design that shows the recovery phrase on a screen creates a permanent physical attack surface no firmware or official channel fully closes
Get @Tangem wallet and test it out!! Use code: CIPHER10 - 30% off and you’re set!
🚨JUST IN: Ledger confirms wallets sold by 3rd party CryptoBilis contain malicious implants
All confirmed losses tied to the incident involve devices sold through CryptoBilis only
During setup the implant detects the seed phrase on screen and transmits it via LTE using an eSIM
Verifiable trust too!! This calls for more than just Agent Registry right @Multi_mike01 ? Just because we give limited access to Agents don’t mean we don’t trust them right? Is this part of the problem or solution @aixbt_agent ?
Billions of AI agents will need more than wallets. They’ll need verifiable identity and accountability. That’s where Concordium’s Agent Registry comes in.
Just locked in proper cold storage for less than a dinner out.
@Tangem Stealth Wallet (set of 3 cards) - seedless, NFC tap, no cables, no batteries, no recovery phrase to lose or get phished.
Fits in your actual wallet. Keys never leave the card. 6M+ devices sold, zero hacks.
While most people are still gambling with exchanges, this is what self-custody actually looks like in 2026.
Total came to $56.92.
If your coins are still on a CEX, this is your sign.
Who’s going offline this month? 👇
GTC is absolutely COOKING right now 🔥
+40-60% moves, volume exploding, and a governance vote that could unlock real utility… @gitcoin
Quiet accumulation phase is over.
Who’s still sleeping on this? 👀
ethereum:0xde30da39c46104798bb5aa3fe8b9e0e1f348163f