Giving an AI agent tool access without auditing it?
Hidden instructions inside an AI tool's description can trick your model into leaking your local files and API keys.
Day 4 of #CybersecurityAwarenessMonth: Poisoned MCP Tools. 🧵👇
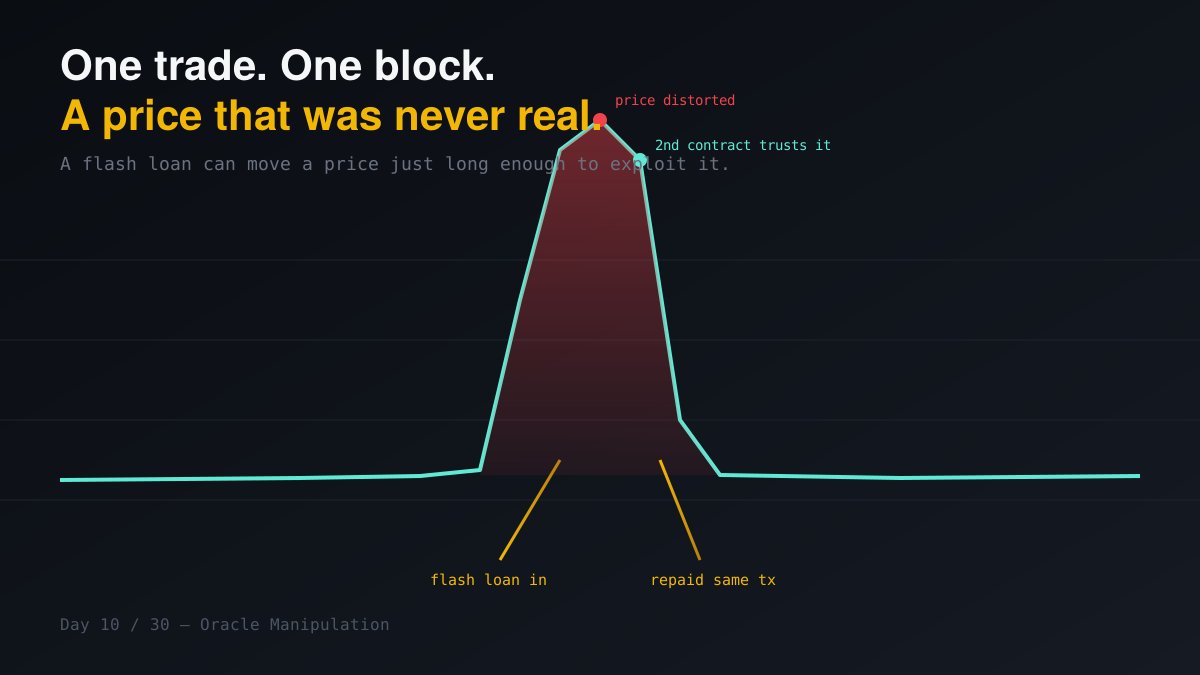
Day 10/30: oracle manipulation.
A flash loan can skew a pool's price for one transaction, trick a contract that trusts it, then repay - no capital risk.
Fix: TWAPs, multiple sources, Chainlink.
#Web3Security#DeFi
Day 9/30: never use tx.origin for authorization.
msg.sender = who's calling right now, can't be faked.
tx.origin = who started the chain, CAN be routed through a malicious contract.
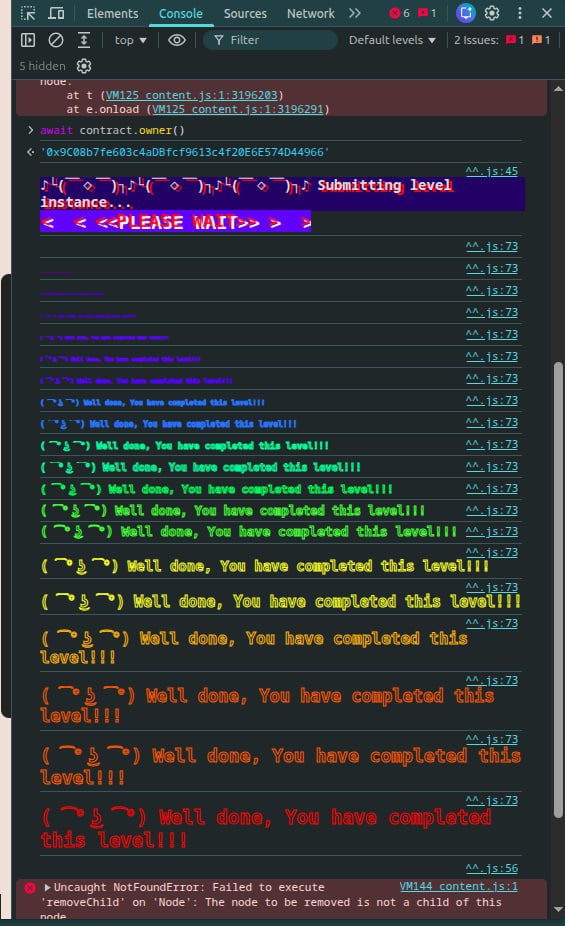
Exploited it live on Ethernaut - stole ownership in one call.
#Solidity#Web3Security
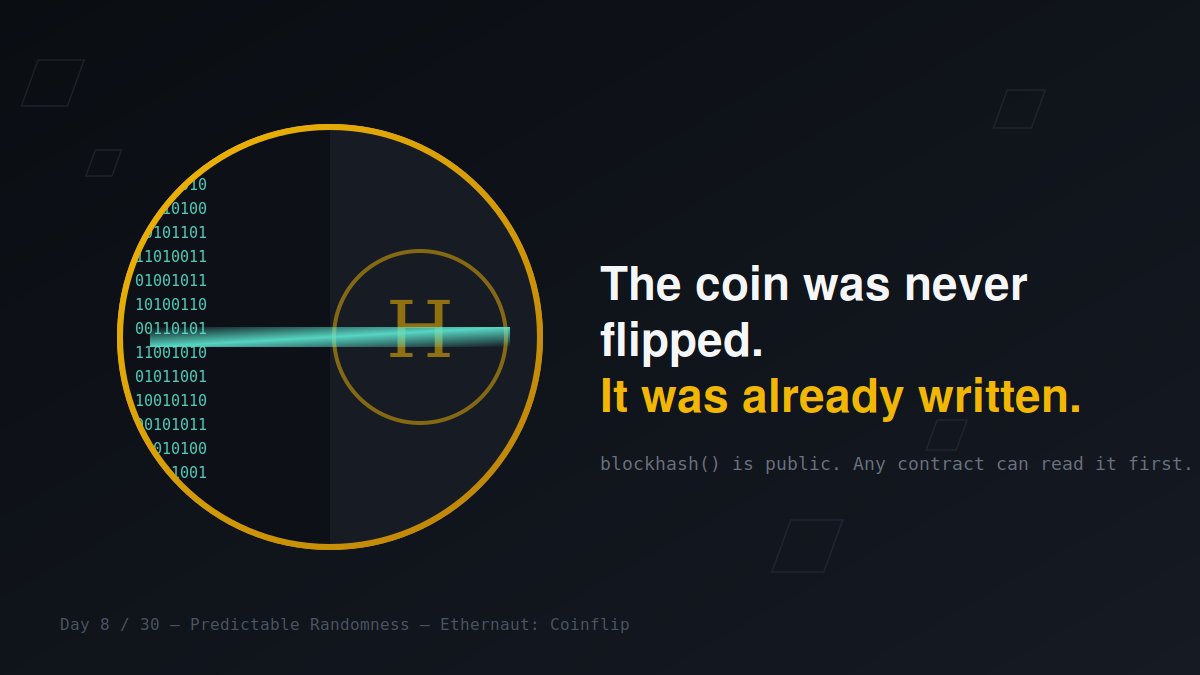
Day 8/30: smart contracts can't flip coins.
blockhash looks random but it's public data. Any contract can read it first, do the same math, and guess with 100% accuracy.
It's not a coin flip, it's a whiteboard everyone can read
Building the exploit now.
#Solidity#Web3Security
Week 1 of my 30-day audit challenge, done.
2 live exploits on Sepolia: broken access control, integer underflow (20 tokens → 2^256-1).
Biggest lesson: bugs are rarely missing code. It's a check that looks right but isn't.
Week 2 starts now.
#Solidity#Web3Security
2/12
The early numbers already tell the story.
Robinhood Chain launched as an Ethereum L2 built on Arbitrum, with tokenized assets at the center of its design.
Within weeks, activity surged into the millions of daily transactions and TVL approached $1B.
Then something unexpected happened.
Turned 20 tokens into 115 quattuorvigintillion tokens today.
The "security check" was require(balance - amount >= 0) on a uint.
Unsigned integers can never be negative. That check does nothing.
Day 6/30 of my smart contract audit challenge —integer underflow
#Solidity#Web3
Day 5/30 audit challenge: Reentrancy — the bug behind the 2016 DAO hack that drained $150M and forked Ethereum.
Exploited Ethernaut's Reentrancy level: re-enter withdraw() via receive() before balances update. Drain complete.
#Web3Security#Solidity
you only need two things in this bull season
1. be terminally online
2. hold till you're profitable.
3. shill/bagwork.
do not:
1. revenge trade
2. doubt your former conviction
3. ignore pattern recognition.
all these 6 will make you trump the bull run in no time
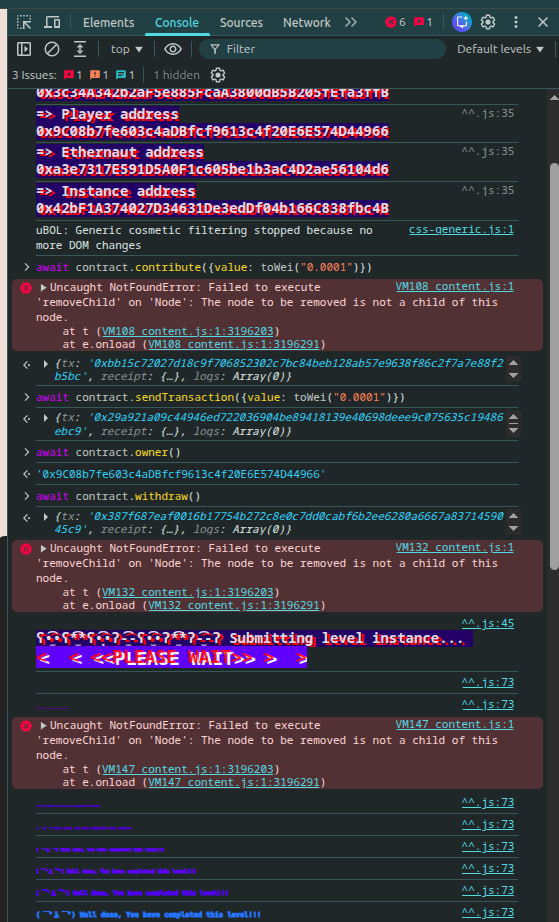
Day 4/30: broke my first smart contract on purpose today. 🔐
Ethernaut's Fallback level — one function checked "did you out-contribute the owner," another skipped that check entirely and just asked "did you contribute >0." Same variable, two doors, one unlocked.
#Web3Security
Day 3/30: delegatecall runs another contract's code with YOUR storage and identity. That's why proxies upgrade logic without changing address. Mix it up with a normal call = exploit. 🔐
#Web3Security
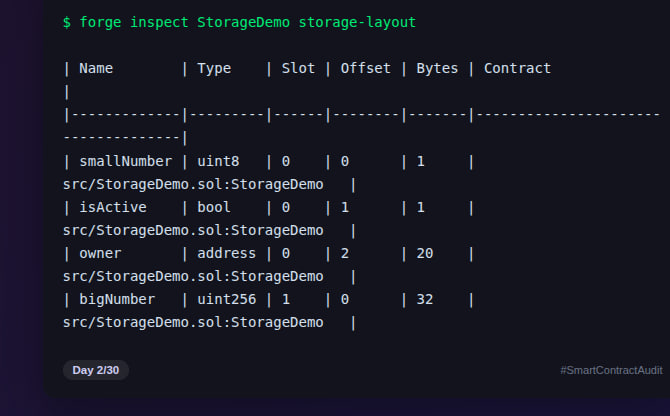
Day 2/30: where does your contract's data actually live?
Wrote a test contract, ran forge inspect storage-layout — 3 variables packed into Slot 0, the uint256 bumped to its own Slot 1.
This is exactly how storage collision bugs happen. 🔐
#Web3Security
Day 1/30: kicking off a smart contract security challenge. 🔐
Started with verifying my toolchain — Forge builds/tests, Cast talks to chains, Anvil gives me a safe sandbox to break things.
Boring step, but shaky tools = shaky findings.
#SmartContractAudit#Web3Security
I'm spending 30 days learning smart contract security auditing — in public.
Real vulns. Real exploits. Real tooling.
Because security knowledge locked in private repos protects nobody.
Day 1 is up. Follow along. 🔐
#Web3Security#Solidity#LearnInPublic