Vulnerabilities that get under your skin: join the talk of our researchers @frycos & Fabian Weber at @hardwear_io for a demonstrated attack chain targeting connected medical infusion pumps.
https://t.co/7GDNP0WZtS
Happy announcement: My colleague and me will present a talk at https://t.co/cveH1C7bhu NL 2026, "Vulnerabilities That Get Under Your Skin: Targeting the World’s Best-Selling Infusion Pumps". 100% human-brain VR 😛
incredibly excited to share that my research 'Playing with HTTP/2 CONNECT' made the final @PortSwigger Top 10 Web Hacking Techniques of 2025!
A huge thank you to everyone who voted. It’s a privilege to be featured alongside such talented researchers.
https://t.co/JNIq91CclQ
You like technical deep dives into binary exploitation and crazy heap wizardry? Then you'll like our blog post by @0xor_solo about unauth'ed RCE in NetSupport Manager aka CVE-2025-34164 & CVE-2025-34165 https://t.co/qTobSqOjrY
Our 2024 applicants challenge is officially #roasted: the full BeanBeat × Maultaschenfabrikle walkthrough is now online. Unwrap the write-up at https://t.co/FOspfgRmRc and revisit the hacks that escalated from cold brew to full breach.
Latest ≠ Greatest? A Retrospective Analysis of CVE-2025-59287 in Microsoft WSUS from our very own @mwulftange who loves converting n-days to 0-days https://t.co/2ev64hf2Ng
CODE WHITE proudly presents #ULMageddon which is our newest applicants challenge at https://t.co/25hlvHXiGW packaged as a metal festival. Have fun 🤘 and #applyIfYouCan
We've added a new demo to NewRemotingTricks that makes deploying a MarshalByRefObject (e.g., WebClient) even easier: System.Lazy<T> creates an instance of T on serialization, which is probably more likely to be allowed than a XAML gadget getting through. https://t.co/JhxnpXPDa5
To clarify: we did not discover these bugs - all credit goes to @_l0gg. We diffed the patches, quickly built a working exploit internally (and identified another auth bypass afterwards)
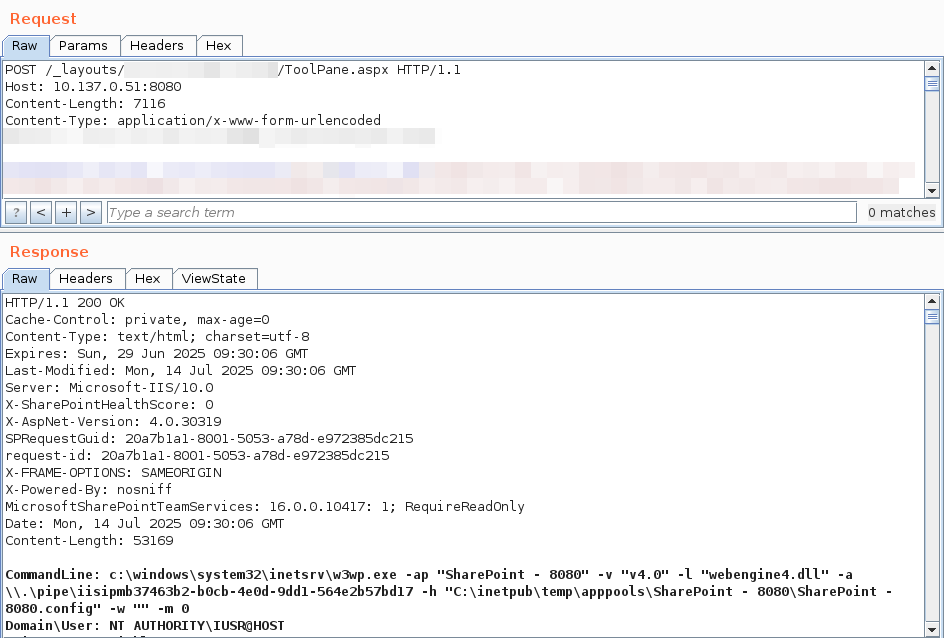
We have reproduced "ToolShell", the unauthenticated exploit chain for CVE-2025-49706 + CVE-2025-49704 used by @_l0gg to pop SharePoint at #Pwn2Own Berlin 2025, it's really just one request! Kudos to @mwulftange
Yes, we're beating a dead horse. But that horse still runs in corporate networks - and quietly gives attackers the keys to the kingdom. We're publishing what’s long been exploitable. Time to talk about it. #DSM#Ivanti https://t.co/weWtiB72Dv