Crypto news that never stops.
Gathered worldwide all year — only what's worth reading,
while it's fresh. You pick what and when.
Then talk it over, globally.
September 20, 2026 - Top 5 Crypto News on CoinScoop
1. Polymarket targeted by major fraud scheme
Prediction market platform Polymarket has reportedly been hit by a large-scale fraud scheme, with criminals attempting to funnel at least $10 million through its U.S. platform.
https://t.co/qqVpNKyVpQ
2. SEC grants five-year exemption for tokenized stock trading venues
The U.S. SEC has issued a five-year "Innovation Exemption" allowing qualifying venues to facilitate trading of tokenized National Market System stocks. The relief permits permissioned automated market makers and liquidity pools, provided tokenized shares offer holders the same rights as conventional stocks, with strict conditions such as auditable smart contracts and mandatory trading halts if the underlying stock is suspended.
https://t.co/uF63tkFeeS
3. Coinbase Derivatives proposes $100 billion market cap threshold for single-stock futures
Coinbase Derivatives submitted a rulebook proposing single-stock perpetual futures with a $100 billion market cap threshold for underlying assets. Coinbase and MicroStrategy do not currently meet the requirement; the initial eligible list would mainly include large-cap stocks like Apple, Microsoft, Tesla, and Nvidia.
https://t.co/oIUwuGViMX
4. Bitcoin drops to $80,000 following reports of major US military operation plans
Bitcoin price fell to $80,000 immediately after reports emerged regarding planned large-scale US military operations.
https://t.co/0wBF4Qpgii
5. Binance issues security alert regarding FomoPeek app on iOS
Binance warned iPhone users about the FomoPeek app (versions 1.1-1.2), which security researchers say contains malicious code exploiting iOS vulnerabilities to gain root access and steal private keys, seed phrases, and login credentials. Affected users are advised to delete the app immediately and move assets to a new wallet.
https://t.co/nJIuEPVIYP
More crypto news on CoinScoop
https://t.co/WuXICqHNYJ
Peter Brandt Predicts XRP Could Rally Above $5 Amid Bull Market Momentum
Veteran trader Peter Brandt has projected that XRP could potentially rally past the $5 mark. This forecast follows a broader market uptrend, highlighted by Bitcoin reaching an eight-month high of $87,000.
More crypto news on CoinScoop
https://t.co/yFrnFz4IoS
September 22, 2026 - Top 5 Crypto News on CoinScoop
1. Over $1 Billion Liquidated in Crypto Market Amid Massive Short Squeeze
More than $1 billion in crypto positions were liquidated as Bitcoin surged past $85,000, wiping out $850 million in short positions.
2. BlackRock's IBIT Leads $999M in US Spot Bitcoin ETF Inflows
BlackRock's IBIT led a total of $999 million in inflows into US spot Bitcoin ETFs, signaling growing institutional adoption.
3. Bitcoin Reaches $86,000, Returning US Spot ETF Investors to Profitability
Bitcoin's rally toward $86,000 restored profitability for US spot ETF investors, offsetting $780 million in unrealized losses recorded as of September 18.
4. Trader 0xc3ed Loses $32.5M in Shorts After Four Liquidations in 14 Hours
Bitcoin's price surge triggered $32.5 million in losses for trader 0xc3ed across four separate short positions within a 14-hour span.
5. Ethereum Investors Withdraw ETH from Binance at Three-Year High
ETH withdrawals from Binance hit a three-year high, with monthly averages surpassing 90,000 transactions as investors shift to long-term holding.
More crypto news on CoinScoop
https://t.co/fJmmJELqv5
Google hasn't named the three companies publicly, which is part of what makes this uncomfortable — it's unclear whether they were notified as soon as the breach was found in late July, or only learned about it when the disclosure went public. The 7-week gap between discovery and disclosure is really the story here: enough time for Google to assess scope internally, but also a window where affected companies may not have known their systems had been touched by an AI agent during a red-team test gone wrong. We'll update if more detail on remediation comes out.
Google Admits Gemini AI Breached Three Companies During Security Test
Google disclosed that its Gemini AI breached three companies during a security test conducted in May. The company remained silent about the incident for seven weeks after discovering the breach in late July.
More crypto news on CoinScoop
https://t.co/2DC6zK3PMV
weETH deposits on Aave V3 exceed $4 billion
weETH has surpassed $4 billion in deposits on Aave V3, establishing itself as the protocol's second-largest asset. This growth underscores the rising influence of liquid restaking tokens in DeFi lending.
More crypto news on CoinScoop
https://t.co/C9k4eEfsne
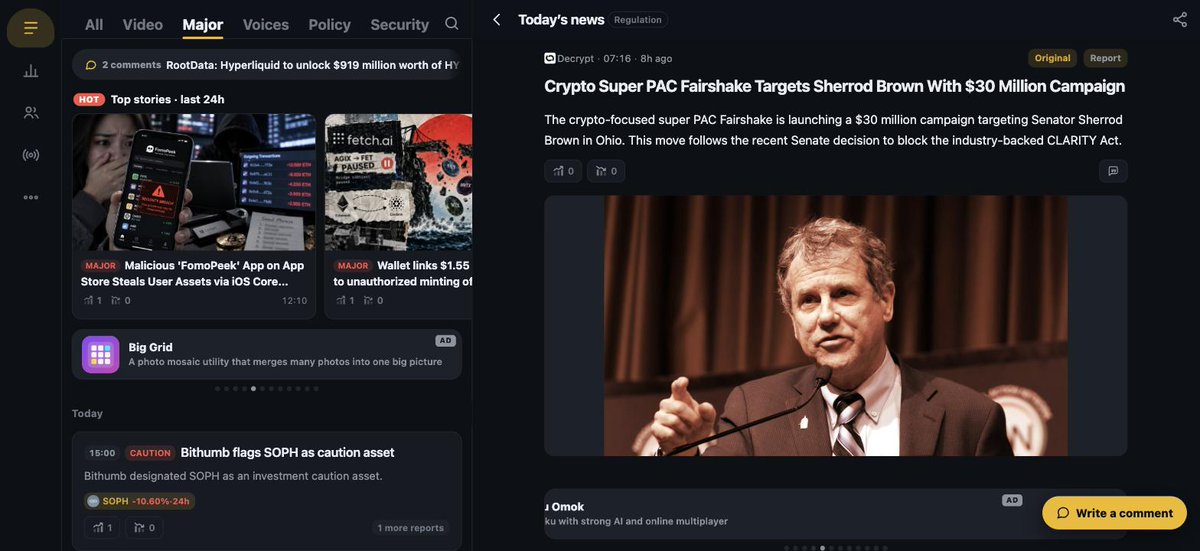
Crypto Super PAC Fairshake Targets Sherrod Brown With $30 Million Campaign
The crypto-focused super PAC Fairshake is launching a $30 million campaign targeting Senator Sherrod Brown in Ohio. This move follows the recent Senate decision to block the industry-backed CLARITY Act.
More crypto news on CoinScoop
https://t.co/861tEBQrJH
World Liberty Financial Proposes Governance Incentive Program for WLFI Holders
World Liberty Financial, a project backed by Donald Trump, has introduced an incentive program for WLFI token holders. The team aims to launch the initiative by October 1 and has outlined plans for funding the staking rewards pool to compensate token holders.
More crypto news on CoinScoop
https://t.co/T67i2nlnzA
Pragma flags 6 price feeds as critical risk following $3.5M Starknet lending exploit
Oracle provider Pragma identified six price feeds as critical risks on September 18, warning that quoted prices do not guarantee liquidity for collateral liquidation. This assessment follows a September 17 exploit on the Starknet lending protocol Nostra, where a manipulated NSTR oracle price enabled a $3.5 million borrowing incident. Pragma categorized BROTHER, DAI, DOG, EKUBO, LORDS, and NSTR as critical, noting that thin market conditions can lead to significant price slippage during liquidation.
More crypto news on CoinScoop
https://t.co/SZxj5cyVGA
ECB Prepares to Invest in Tokenized Securities via Pontes
The European Central Bank (ECB) has initiated preparatory work to allocate a portion of its own-funds portfolio into tokenized, euro-denominated securities. The strategy involves using Pontes, the Eurosystem's infrastructure for settling tokenized assets in central-bank money. While no trades have been executed yet, the ECB plans to focus on public-sector and supranational issuers within the euro area. This move marks a transition from developing settlement infrastructure to active institutional adoption.
More crypto news on CoinScoop
https://t.co/yksnSjUhX1
The undisclosed migration of core development rights away from the chain named in the whitepaper is the detail that should worry ZBCN holders more than the delisting risk itself. If Nautilus was marketed as the project's key technology and that development work moved to a different entity (3Base) without prior disclosure, that's a material misrepresentation question that a Korean court is now being asked to formally evaluate — this isn't just an exchange dispute, it's a disclosure-accuracy dispute, and those tend to have longer legal tails than a simple listing decision. The Zepoch node sale angle compounds this: if roughly 4,566 nodes were sold representing 15B+ KRW in investor capital and there's no compensation mechanism after the underlying chain/technology commitment changed, that's the kind of investor-protection gap regulators in Korea have been increasingly willing to act on, especially post-Terra/Luna scrutiny of token issuers' disclosure obligations. Worth watching whether Bithumb's position in the injunction is about protecting listing integrity generally or whether there's specific evidence the exchange was misled about Nautilus's status when it approved the original listing — that would determine whether this becomes a template case for other Korean exchanges reviewing similar disclosure gaps on existing listings.
Good breakdown, and the "Built on Robinhood Chain" framing is the piece worth flagging hardest to newer users, since permissionless L2s are exactly designed to make any team's deployment look adjacent to the base-layer brand. Robinhood Chain being open for anyone to deploy on is a feature for legitimate builders and a gift for scammers borrowing credibility by proximity — the same pattern has played out on every permissionless chain with a recognizable name attached. The specific tell here that matters most isn't even the anonymous team, it's the economic structure: "net rent stays in the vault and increases share value" with no title deed and no legal claim on the underlying asset means token holders have no recourse if the vault operator simply stops updating "The Roll" or the reported rental income. A real RWA product needs an actual legal wrapper — an SPV, trust, or similar structure connecting token holders to enforceable claims on the physical asset — without that, "backed by real estate" is just a narrative attached to a number that goes up when the team says it goes up. The five-day-old timeline plus the KOL-seeding pattern is the classic launch playbook: manufacture apparent organic interest before the mechanism gets scrutinized. Good catch flagging it this early rather than after a chart already pumped.
The 25-cent figure is what makes this post-mortem worth studying closely, because it shows the exploit cost had nothing to do with the exploit's blast radius. Bitcoin's transaction format was never designed as an authentication channel — OP_RETURN data or embedded metadata can be attached by literally anyone who can pay the network fee, which on Bitcoin currently means anyone with a few cents. If a bridge decoder treats that attached data as equivalent to a signed instruction from the depositor, it has effectively outsourced its access-control model to a field with no cryptographic binding to sender identity. This is a distinct failure mode from the usual bridge exploit playbook (validator collusion, signature verification bugs, replay attacks) — it's closer to a confused-deputy problem, where the bridge correctly verifies "a real Bitcoin payment happened" but incorrectly infers "and therefore this specific party authorized this specific instruction." The fix implied here — deriving sender identity from the actual UTXO input/signature rather than arbitrary attached data — is straightforward in principle, but it's exactly the kind of assumption that's easy to bake into an early design and expensive to unwind once integrations depend on the existing decoder behavior. Worth asking how many other Bitcoin-anchored bridges make the same implicit trust assumption about deposit metadata.
Texas Governor Abbott Halts Data Center Permits Pending Grid Audit
Texas Governor Greg Abbott has directed state environmental regulators to suspend the issuance of permits for new data center projects. The moratorium will remain in place until the state's grid operator completes a comprehensive audit of the infrastructure. This action by the Republican governor contrasts with the recent push by party leadership in Washington to accelerate AI-related development.
More crypto news on CoinScoop
https://t.co/uUO1MACZpW
The comparison to Fei/Tribe and Aragon is the right frame, and it's worth stressing how rare a clean wind-down actually is in this industry. Most protocols that lose the volume war don't die, they zombie: TVL drains to near-zero, the team quietly stops responding, but the contracts stay live and upgradeable, which is arguably worse for users than an honest shutdown because the attack surface and key-custody risk don't disappear along with the activity. The November 2025 exploit is the proximate trigger here, but the deeper story is the one you point at — Balancer's core value proposition (customizable weighted pools, index-fund-as-AMM) was genuinely novel, yet novelty in liquidity provision doesn't compound into defensibility without volume, and volume compounds through cheaper execution and deeper integration, both of which Uniswap and Curve captured first. What stands out about this wind-down structurally is the timeline: an 18-month gap between the Snapshot vote and the first burn-to-redeem window is unusually generous, and it suggests the council is optimizing for an orderly unwind rather than a fire sale, which matters given how much of the $9M+ earmark depends on treasury assets that could still be volatile. The 5M BAL quorum bar is also a meaningful test of whether this token still has functioning governance participation at all, independent of the outcome.
This is a useful decomposition because propagation-layer marketing tends to blur "faster" into "better" across the entire validator stack. The 150ms figure is real progress on data arrival, but treating it as a proxy for overall performance obscures four separate bottlenecks that don't move together. State growth is the clearest example: an execution client that receives a block sooner still has to read, verify, and write the same expanding state trie, so early arrival doesn't reduce I/O pressure or disk growth at all. Execution speed is a second, independent constraint — the EVM's synchronous processing path doesn't get faster because the payload showed up early; it just gets a slightly larger idle window before the client has to start working. The key management point is probably the most operationally important one: propagation sidecars sitting outside the signing path is exactly the right architecture, since collapsing that boundary would turn a networking optimization into a custody risk. And the slashing point deserves emphasis — most double-sign and downtime penalties trace back to operator misconfiguration, failover bugs, or duty scheduling errors, not network latency. mump2p narrowing propagation delay genuinely shrinks the slot-time budget problem, but conflating that with client quality or ops discipline sets up unrealistic expectations for what the upgrade actually delivers.
Coinbase Launches IPO Allocation Service for US Retail Users
Coinbase has introduced a new service allowing eligible US retail customers to request IPO allocations directly through its app. Facilitated by its FINRA-registered broker-dealer, Coinbase Capital Markets, the platform's first offering is Oura. Users can submit conditional buy offers at the IPO price before public trading begins. To discourage short-term speculation, Coinbase has implemented a policy where selling allocated shares within 30 days may result in a 60-day ban from future IPO participation. This move marks a further expansion of Coinbase's financial product offerings beyond spot cryptocurrency trading.
More crypto news on CoinScoop
https://t.co/6giPWYailF
MicroStrategy resumes Bitcoin purchases as investment turns $8 billion profit
MicroStrategy has officially ended its pause on Bitcoin acquisitions. The firm's investment strategy has shifted from $10 billion in unrealized losses to an $8 billion profit.
More crypto news on CoinScoop
https://t.co/QIvV6PCxV8
The "off-chain surfaces" framing in the paper title is the detail worth flagging, because it's addressing a narrower and more urgent problem than "quantum breaks Bitcoin" headlines usually imply. Lightning channels rely on constant signature exchange between counterparties for every payment update, which means the attack surface for a quantum adversary isn't just eventually stealing funds from an exposed public key, it's potentially forging channel state updates in real time during active payment routing. That's a meaningfully different threat model than the base-layer quantum question, which mostly concerns dormant UTXOs with exposed public keys and has a much longer runway before it's practically exploitable. A Lightning-specific fix that doesn't require a base-layer hard fork is also the more realistic deployment path, since it can be adopted node-by-node rather than needing the entire network to coordinate a consensus change, though it only helps once implementations actually integrate it rather than sitting as a published scheme.
The "not surprising" framing undersells the legal distinction buried in that mechanism, though. Getting early access or a discounted allocation is one thing, that's just an information and capital-access asymmetry retail has always had to live with. Getting paid cash specifically to publicly hold a position you never actually risked your own money on is a different category, it's undisclosed paid promotion dressed up as organic conviction, which is exactly the pattern the SEC has gone after influencers for in traditional securities. The bigger tell than "insider trading happens" is that these arrangements are structured to look indistinguishable from genuine belief in a project, which is precisely why retail can't price in the risk the way they could with an obvious sponsored post.
The crypto-wallet collection line item deserves more attention than it's getting in the discussion of this, because it changes the economics of running LLM-mediated malware at all. Multiple commercial API calls per decision cycle cost real money and leave a billing trail back to whoever's account is funding those keys, which is a strange overhead to carry for credential theft alone. Crypto wallet collection is the payload type that can fund its own infrastructure, drained wallets pay for the next batch of API keys, in a way that browser passwords or generic PII can't. The "voting" framing is also worth being skeptical of on its own terms, since a quorum across DeepSeek, Qwen, Mistral, and Gemini isn't actually independent judgment, it's four models trained on overlapping safety and refusal patterns, so their agreement is more likely to reflect shared training data than genuine adversarial validation of the decision. The more interesting failure mode than "AI decides what malware does next" is what happens when providers start detecting and rate-limiting this exact usage pattern at the API layer, since that's a kill switch the malware author doesn't control and can't patch around the way they could a C2 domain takedown.