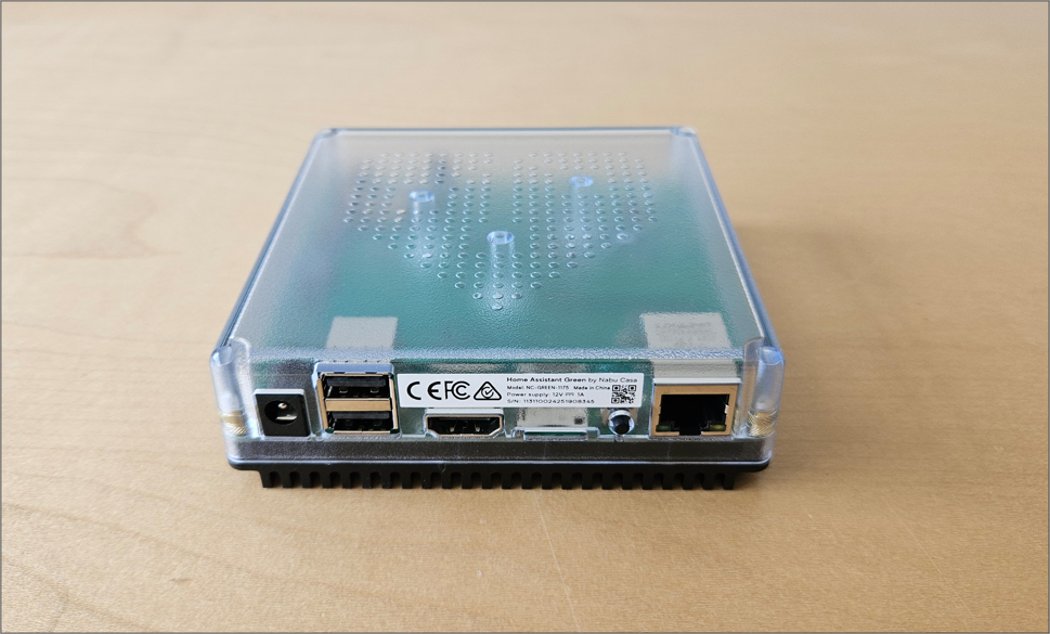
From an unauthenticated music add-on to root on the host. At #Pwn2Own Ireland 2025, our team chained their way through the Home Assistant Green and walked away with $20k. Emanuele shows the full chain, and how it nearly failed on stage. https://t.co/BlHCePNLAx
#IoTSecurity
Compass Security supports Graubündner Kantonalbank with a structured bug bounty program that enables responsible reporting of potential vulnerabilities within a defined framework.
https://t.co/xV1MRcaMar
#bugbounty#ethicalhacking#cybersecurity
What’s for dessert? Root. 😈
After lunch at #BruCON0x12: Emanuele and @yves_bieri present Pwn the Hub, Own the Home
One vulnerable add-on → RCE → container escape → full Home Assistant compromise.
From 11 September 2026, manufacturers selling digital products in the EU have 24 hours to report actively exploited vulnerabilities. ⏱️ Andreas Brombach explains what is reportable, and how to actually make those deadlines: https://t.co/uCBc0LifGT
#CRA#ProductSecurity
Pentesting passkeys? Security analyst @emanuelduss shows two JS snippets for tampering with the WebAuthn APIs. Handy for checking if you can login using a security key without knowing the PIN.
Check out the technical details and how he got there: https://t.co/yxTY6WaI5M
Pipeleek 1.0 is out 💧 Secret scanning across 7 CI/CD platforms, plus runner and Renovate bot exploitation.
Want to see one leaked job log turn into repo takeover? Try our deliberately vulnerable GitLab Attack Lab. Happy leeking!
https://t.co/dvyVsT1biO
#DevSecOps#CICD
Your team evaluated that automation platform as a productivity tool. Attackers see a jump host with SSH access, stored credentials, and a path around your network segmentation.
Read our latest blog post before deploying any automation platform: https://t.co/UDMxc3iie8
How do you translate the Cyber Resilience Act into technical testing? Part II of our #CRA series follows a cheap IP camera, from STRIDE threat modelling and firmware analysis to compliance with IEC 62443-4-2.
https://t.co/ezuDPCS1hm
#CyberSecurity#CyberResilienceAct#IEC62443
How do you prepare a product for the Cyber Resilience Act? Our latest article covers #CRA scope, product classification, threat modelling, technical security testing, and why we use IEC 62443 as an assessment framework. Part I of a two part series: https://t.co/u4aKX7MagQ
Attending @a41con in Dübendorf (CH)? 🎯 Swing by our booth and check out RAPTR: our open-source collab platform for Purple Team ops. Plan, attack, detect, report. All in one place.
See you there on Thursday/Friday!
#Area41#PurpleTeam
At @a41con next week?👋
Come to our booth to see EntraFalcon in action: our open-source tool for assessing Microsoft Entra ID security posture. Privileged objects, risky assignments, conditional access misconfigs: find what's hiding in your tenant.
AI agents in your Entra ID tenant? They come with new identities, permissions, fresh attack paths.
Chrigi @ZH938472 breaks down Entra Agent ID security, their capabilities, control paths, abuse scenarios, and how to review your exposure with EntraFalcon.
https://t.co/vtR3Wat3gc
The monkey is still curious 🐒 Teleboy has topped up its bug bounty program with another CHF 10'000 in rewards. Explore a platform serving 400'000+ users across TV, internet, and telephony. Ready for another hunt? #bugbounty#ethicalhacking#cybersecurity
https://t.co/oXuB0Xld85
SSH everywhere, misconfigurations somewhere. Our new SSH Labs let you get your hands dirty: slides, video, and a Docker-based lab. Created by our Security Analyst @emanuelduss, learn how SSH breaks and how to fix it: https://t.co/2jxuEK8N4i
#SSH#InfoSec#Security
✨ We’re excited to welcome @compasssecurity as a Platinum Sponsor for the AREA41 security conference 2026 🛸 👽
Thank you for supporting the infosec community‼️
➡️ Check them out at: https://t.co/jHGJDVrtlu
📅 June 18-19. 2026, Zürich - https://t.co/WTAd8rhP6q
Compass vulnerability research identified code execution paths affecting AI coding assistants including @claudeai , @cursor_ai and @OpenAI#Codex. The findings will be demonstrated live at @thezdi Initiative #Pwn2Own Berlin 2026, May 14 to 16. #AIsecurity#LLM
🦖 Meet RAPTR: our new open source platform for red and purple team collaboration. Plan engagements, document attacks and detections, evaluate results, and generate reports, all API-driven. Beta is live, feedback welcome! #PurpleTeam
https://t.co/GyXw40nN2p
Tabletop exercises show how incident response processes fall apart under pressure, far beyond what any plan suggests. Here we share key lessons from real TTX sessions: failures in communication, decision-making, structure, and human factors.
https://t.co/Kp0ryUL3Dv
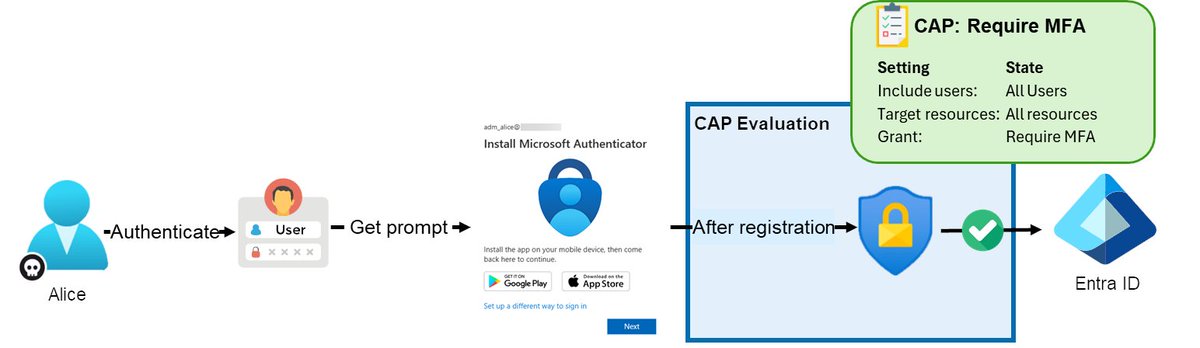
The final part of our Entra ID blog series looks at common Conditional Access weaknesses, practical attack scenarios, and how to identify such issues with EntraFalcon.
https://t.co/vx43hX6mDj