We are deeply sorry for the disruption this incident has caused our customers and partners. We know the trust they place in our services and take that responsibility extremely seriously. We are seeing broad recovery and stability across our services.
This was a technical issue not related to cyber or AI / agents. The incident was introduced by an issue during an earlier network capacity upgrade that surfaced following a recent network change. We have addressed the underlying issue and continue to restore service to remaining customers and regions.
Given the scale of demand, we restored services gradually, validating stability at each stage. While this took longer, it helped ensure a stable restoration.
We will provide a full post-incident report once our review is complete.
We don't know the root cause yet but it is interesting to breakdown the traffic by source data center. The recovery came in fits and starts and varied greatly by source, probably due to Microsoft's efforts to bring the service back online.
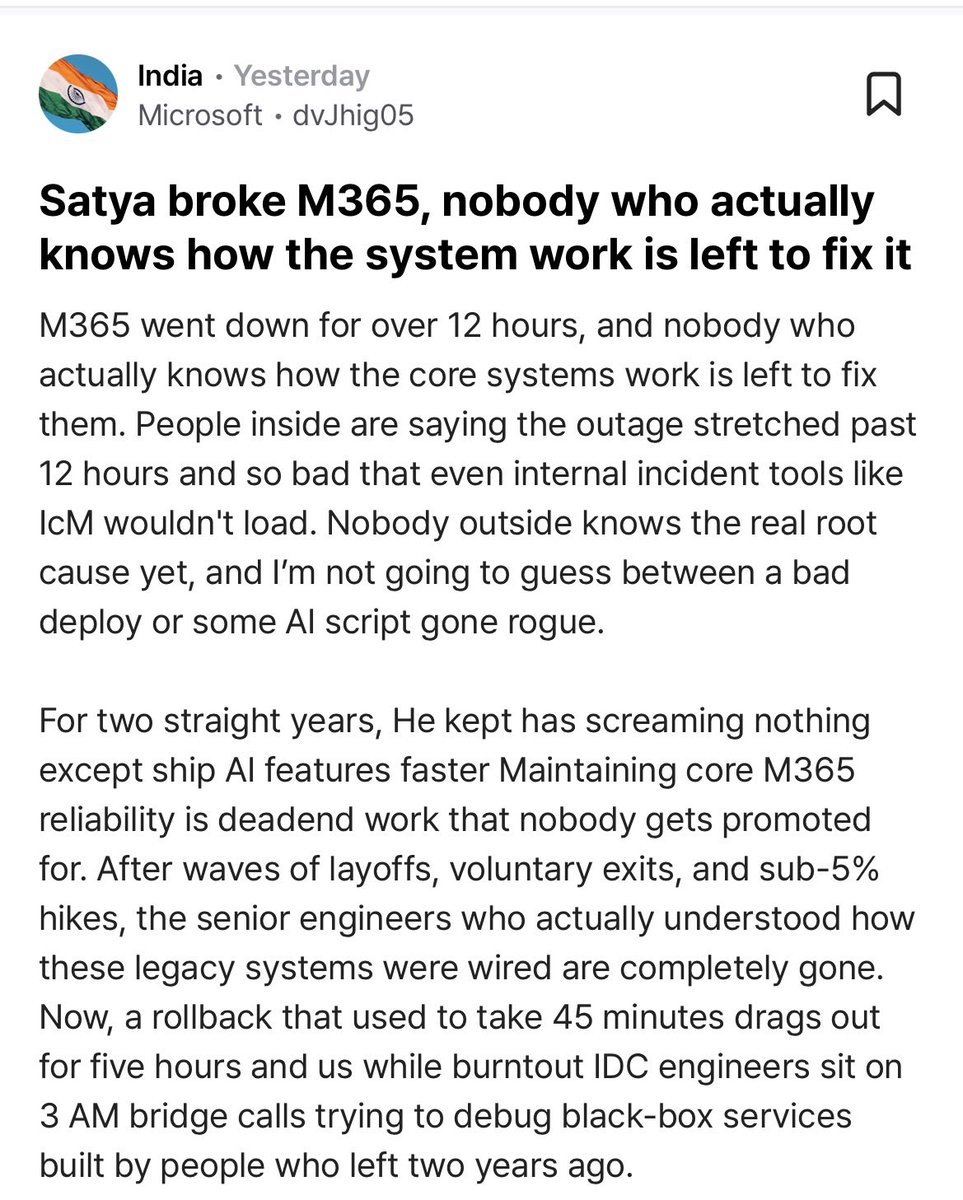
To translate this to normal speech, they fired a guy who past 20 years been manually deploying patches to prod and replaced him with AI. AI can't figure out the root password because it's written on sticky note below his desk. They're trying to locate the desk.
Exchange Online is finally climbing back. After ~18 hours running about 85% below expected levels, traffic to Microsoft’s email service began rising sharply at 6:20 AM ET (11:20 UTC), the biggest gain we’ve seen since the outage began.
This shows, a renowned company like this can anytime be struggling doing restoration.
I don’t trust China company, they are usually cheap quality support for sure. See now
We’re seeing encouraging recovery progress, with service availability and email delivery performance improving across a growing portion of affected Microsoft 365 infrastructure. Some users may still experience intermittent issues as recovery actions continue. We’re focused on recovery for the remaining affected environments while prioritizing email queue and backlog reduction. The extended 48-hour email timeout window remains in place to help protect delayed messages as delivery catches up. A more comprehensive update can be found at MO1550821 in the Microsoft 365 admin center, as well as https://t.co/bVoAAh3D2G if the admin center is not available to you.
To the Microsoft employees desperately trying to bring Outlook back online, please don’t push yourselves too hard. Your health matters more than any deadline. Take a long weekend, relax, and come back Monday feeling refreshed. You’ve worked hard enough this week, and I promise those 400 unread emails aren’t going anywhere.
Beginning around 17:30 UTC, ThousandEyes observed availability issues affecting Microsoft 365 services globally. Users attempting to access Microsoft Outlook and other Microsoft 365 services encountered connection resets, connection refusals, response timeouts, and HTTP server errors. Significant traffic loss in Microsoft’s network was also observed during the incident. The incident is still ongoing.
Explore the outage within the ThousandEyes platform (no login required): https://t.co/M23mpjcjqY
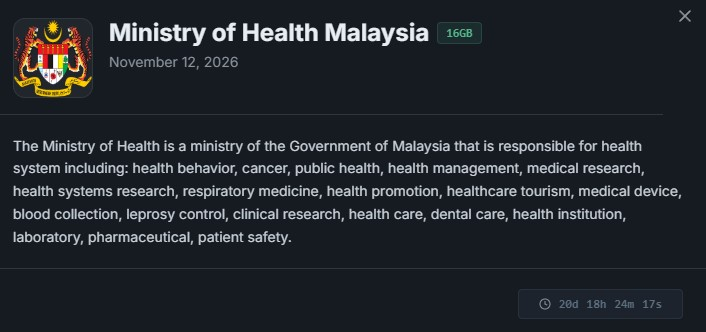
📢 Ransomware Alert: 🇲🇾
Ministry of Health, Malaysia (https://t.co/sr673hKGRp), a Malaysian government ministry healthcare system, has reportedly fallen victim to Panzer ransomware.
NB : The group intents to publish the data within 20-21 days.
🔍 Key Details:
🛡️ Threat Actor: Panzer
📅 Reported on: 12/11/2026
⚠️ Data Compromised: 16 GB
While we're working to mitigate impact, we've confirmed the issue may affect Microsoft 365 service connectivity for users in any region, more information will be provided in the Microsoft 365 admin center under EX1550543.
Microsoft's outage reports on November 12 reached 74 countries and territories in about an hour on Downdetector.
Microsoft says its Exchange Online incident began at 16:17 UTC. Reports to Downdetector about Outlook began climbing at about 17:25 UTC, 12:25 in New York. By 18:25, reports about five Microsoft services combined reached 19,650 a minute, against <15 a minute on an average Thursday.
Outlook reports alone peaked at more than 2,000 times their normal level.
Reports did not stay in the Americas. They jumped tenfold in the UK at 17:43, in India at 23:21 local time and in New Zealand at 06:55 local time. Between 17:00 and 18:55 UTC, nearly 3 in 10 reports came from outside the US. We count a country here once its reports reach ten times normal and at least 20 in five minutes.
Reports about Microsoft 365, Copilot, Teams and OneDrive each rose more than a hundredfold, and Azure about a hundredfold. Xbox, GitHub and LinkedIn, also Microsoft's, rose far less.
Microsoft said a portion of its infrastructure was experiencing elevated load across multiple regions. At 19:38 UTC, reports were still running at more than 11,000 a minute.
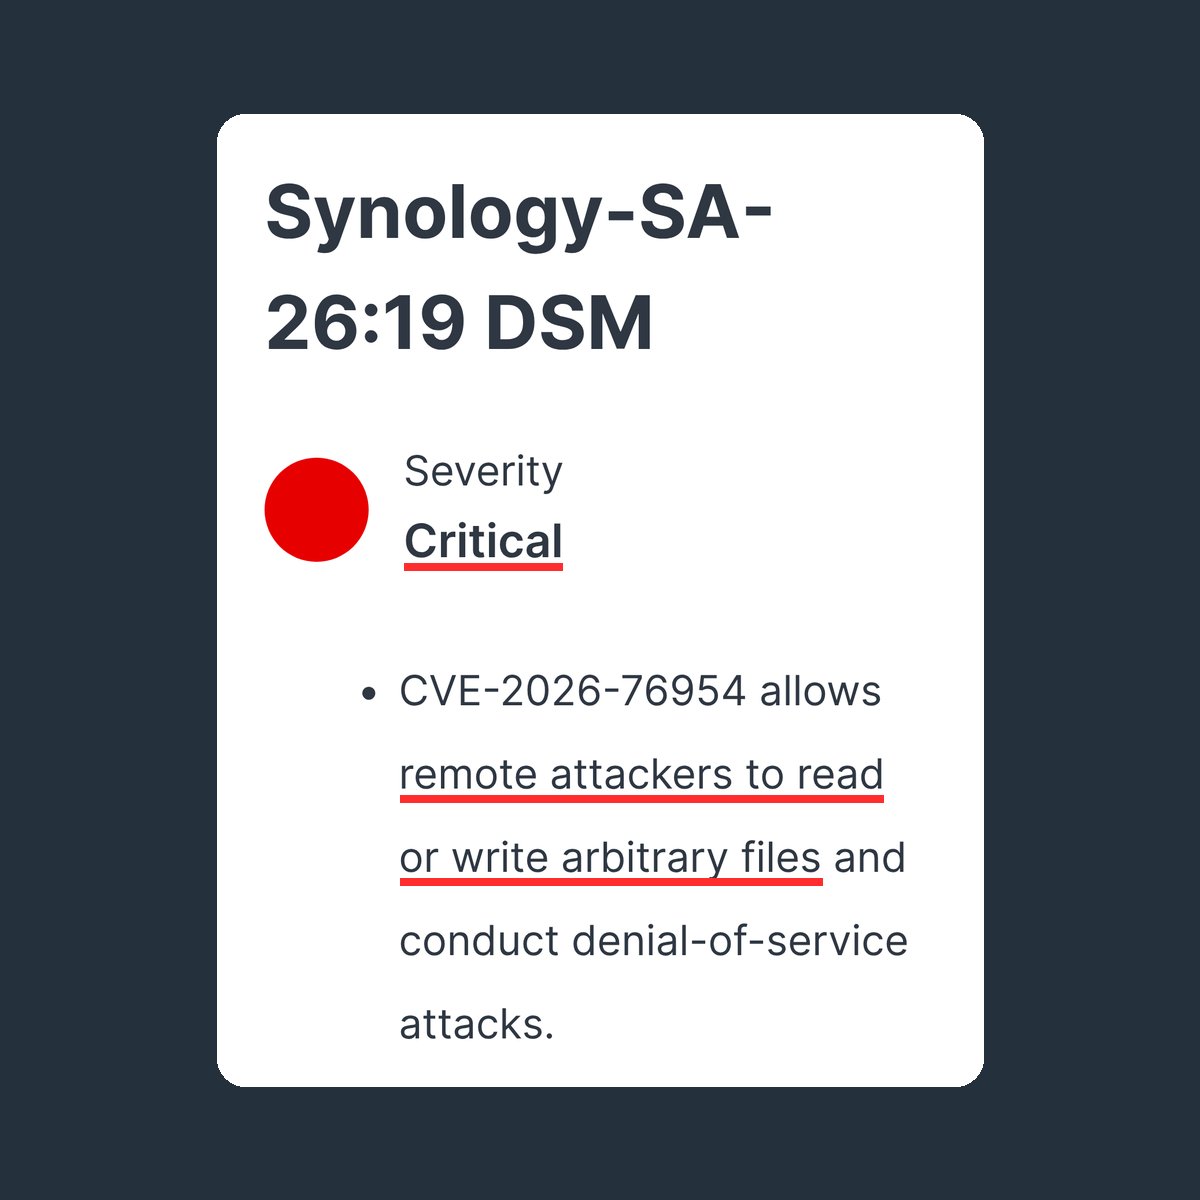
‼️BREAKING: A critical flaw in Synology NAS devices lets attackers read and write any file on them without logging in.
The SQL injection bug in their login system scores 9.8 out of 10. A second flaw, in rsync, skips the login too.
Synology patched both today. Update ASAP.
Free speech is great i know. It gives people the right to start a genuinely stupid podcast in a random kedai mamak and they act like the world (Malaysian) asked for their opinions.
Our security researchers built an autonomous cyber vulnerability discovery, exploitation, and patching pipeline.
In a single run with an upcoming cyber model, it validated and generated patches for 948 local privilege escalation vulnerabilities in the Linux kernel at a total API cost of $1.2 million.