Four days of Burp Suite with @Agarri_FR at Entrypoint.
> Mastering Burp Suite Pro, 100% hands-on
Session handling, API testing, Agentic workflow, Bambdas and authorization checks, make the most out of Burp Suite!
Course details: https://t.co/h6HFiyA5BD
"Site Unseen: Enumerating and Attacking Active Directory Sites"
https://t.co/wo556kJRX3
PR and article by @croco_byte.
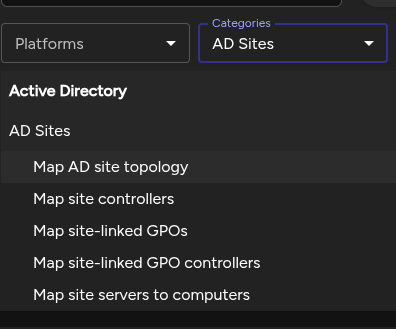
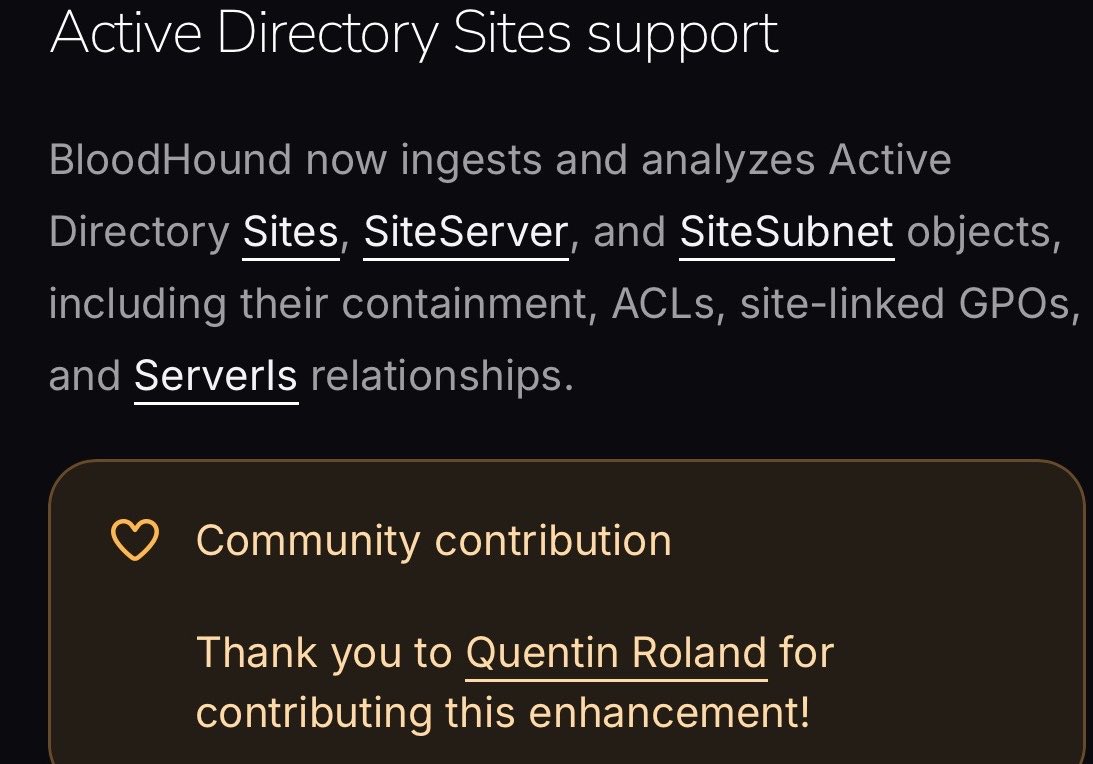
First image from article, it looks a little different in the final version that got implemented in BloodHound but you get the idea. Second is AD Sites queries.
Sharphound now ingests Sites, SiteServer and SiteSubnet.
You need at least bloodhound 9.8.0 otherwise it will complain that the site*.json files have ‘no valid metatag’.
https://t.co/IkpnsbNUur
In our latest article, @croco_byte presents new scripts allowing to simulate legitimate AD services in a flexible manner, and demonstrates their use through GPO exploitation ⬇️
https://t.co/qkgQsFltEa
Attacking heavy applications through named pipes: an attack surface often overlooked due to its complexity.
In this article, @TurboThonSec explains how we designed a tool abusing legitimate processes to attack higly privileged components of heavy clients.
Article⬇️
https://t.co/Y9tAU0xGAi
Hidden GPO-based attack paths are now in BloodHound.
@croco_byte breaks down new OU & AD Site abuse paths that can lead to privilege escalation or full domain compromise, and how to find, map, and weaponize them. #SOCON2026
https://t.co/rrK8yn7IFm: Exploiting SCCM Policies Distribution for Credentials Harvesting, Initial Access and Lateral Movement, by @croco_byte
https://t.co/KBnJFNSY1O
HID recently disclosed HID-PSA-2025-002, a critical flaw in the #ActivID Authentication Appliance 8.7.
In our new blog post, @us3r777 and @__pierreg break down exactly how they uncovered it, from methodology to exploitation 💡
Read it here ⬇️
https://t.co/wmXamNEqra
[Blogpost] @croco_byte presents how to exploit attack paths related to Active Directory sites' ACLs.
As the latter often constitute a blind spot for AD enumeration tools, the article also describes a pull request aiming to integrate them into the BloodHound project: https://t.co/s1qTnPvD2y
Afterwards, the great @croco_byte took the stage, also at #OrangeCon, to present the authentication relay techniques he discovered earlier this year.
As always, he illustrated his talk with a demo, showing that these techniques can be applied to real-world AD environments. 🔥
How safe is your browser?
Our ninja, Riadh Bouchahoua, uncovers how attackers can exploit Chromium extension loading to steal data, maintain persistent access, and breach confidentiality on Chromium-based browsers.
Read more here ⬇️ https://t.co/Q9c4CnL8qr
🧑🎓 Boost your offensive Active Directory skills with our Entry & Advanced trainings. Hands-on labs with dozens of machines + latest research from DEFCON, x33fcon & more! Seats are limited, don’t miss out!
🔗 Entry: https://t.co/7get5clXOg
🔗 Advanced: https://t.co/KEVNM9zdjF
🛠️ GroupPolicyBackdoor - a python utility for Group Policy Objects (GPOs) manipulation and exploitation.
✅ GPO attack vectors can very often lead to impactful privilege escalation scenarios in Active Directory environments. https://t.co/2bh2HsPORv
The GroupPolicyBackdoor tool, presented at #DEFCON 2025, is now available on Synacktiv's GitHub: https://t.co/CWLknch5RZ
This python utility offers a stable, modular and stealthy exploitation framework targeting Group Policy Objects in Active Directory!
My personal #defcon33 highlights:
Better tools for GPO exploitation: https://t.co/ZR1DT7LWOo
Critical vulns in Zscaler and Netskope: https://t.co/FaHFNdyPLL
Phishing on official Microsoft login: https://t.co/P0kwW8GFkD
SSH vulnerabilities: https://t.co/g3YOZfNKuo
🔥 A few hours ago our experts took the stage at #DEFCON33, sharing cutting-edge research on SCCM exploitation and modern GPO attacks in Active Directory. Proud of the team! 🙌 cc @kalimer0x00 @quent0x1 @wil_fri3d